DeviseInvitable: invitation tokens that never expire unless you set invite_for
An invitation strategy for devise
At a glance
- What is it?
- DeviseInvitable is a Devise module that sends email invitations and lets the recipient choose a password when they accept. It works on two ORMs, ships nine model options, and its out-of-the-box defaults leave invitations valid forever and sign the user in immediately after they set a password.
- Who is it for?
- Use DeviseInvitable when signups must be closed and access granted by email, and expect to change two defaults before it reaches production: set `invite_for` to a real period, because zero means the token stays valid indefinitely, and decide deliberately on `allow_insecure_sign_in_after_accept`, which signs the user in the moment the password is set.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 10 days ago.
- What is it written in?
- Mainly Ruby, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
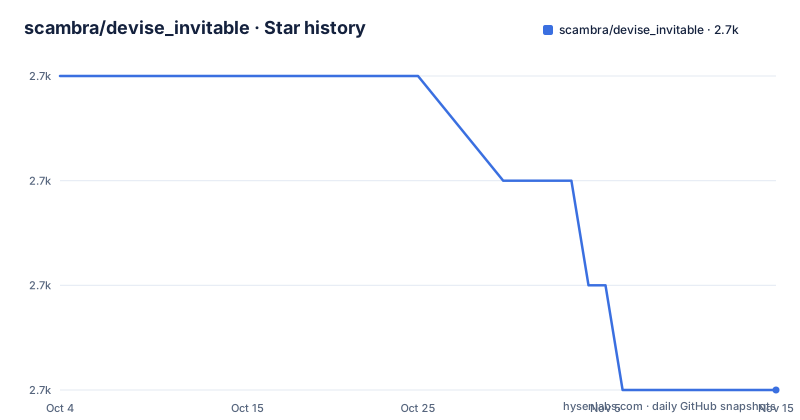
- scambra/devise_invitable2,671 ★ · -3
| Repository | 2026-10-04 | 2026-11-15 |
|---|---|---|
| scambra/devise_invitable | 2.7k | 2.7k |
-3 Stars in the last 42 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The default invitation never expires and the column that records it goes unread
The first configuration option decides how long an invitation stays usable. `invite_for` is the period during which a generated invitation token is valid, and once that period passes the invited resource can no longer accept the invitation. The default value is `0`, and the documentation for the option states plainly that at `0` the invitation will not expire. That is a quiet default: an invitation link sent today still works next year, and nothing in the schema or the code expires it for you. The column that would let you reason about age exists, `invitation_created_at` sits in the migration alongside the others, but the policy that decides whether it matters is entirely up to this setting. Two ways of setting it are given, either as a commented line in the Devise initializer:
# ==> Configuration for :invitable
# The period the generated invitation token is valid.
# After this period, the invited resource won't be able to accept the invitation.
# When invite_for is 0 (the default), the invitation won't expire.
# config.invite_for = 2.weeks
or as an argument on the `devise` call in the model itself, which keeps the setting next to the modules it applies to.
Four options decide who is allowed to send an invitation
The remaining options split into two groups, and the ones that decide who may send an invite are worth reading together. `invitation_limit` is a count with three distinct meanings: the default `nil` means users can send as many invites as they like and the `invitation_limit` column is not consulted at all, `0` means they cannot send invitations, and a value above zero means they can send exactly that many. The per-user column can be set to a different number for individual users, so a global `0` can still be overridden for specific records. `invite_key` controls which existing users count as matches when an invitation goes out, and it accepts a hash of keys whose values respond to the `===` operator, which includes procs and regexes, so several matching strategies can be combined; the default looks users up by email and validates with `Devise.email_regexp`. `validate_on_invite` forces a record to be valid before it is actually invited, and `resend_invitation`, enabled by default, controls whether inviting a user who is already in the invited state sends a fresh message. The last three options describe the inviter side: `invited_by_class_name`, `invited_by_foreign_key` and `invited_by_counter_cache`.
The Mongoid field list omits the inviter columns and its index names a field that does not exist
The ActiveRecord migration asks for seven columns: `invitation_token`, `invitation_created_at`, `invitation_sent_at`, `invitation_accepted_at`, `invitation_limit`, `invited_by_id` and `invited_by_type`, plus a unique index on the token. The Mongoid section asks for five, and the two it leaves out are exactly the pair that records who sent the invitation. In their place it defines the association itself, `belongs_to :invited_by, polymorphic: true`, on the grounds that no `belongs_to` needs declaring. The index list underneath then compounds the difference by indexing a field named `invitation_by_id`, which is not the column the migration uses, not the association name, and appears nowhere else in this gem's documentation. Both indexes are declared with the background option, so they are built asynchronously, which is the second reason the page closes with a reminder to create the indexes on the database after deploying:
rake db:mongoid:create_indexesAnyone following that section literally on Mongoid gets indexes on a field the model may not define, and no index on the one it does.
Two defaults decide whether a password is asked for and whether a session starts
The last two options are about what happens in the seconds after someone accepts. `require_password_on_accepting` is enabled by default, so an invitee is asked for a password while accepting; the documentation explains when to turn it off, namely when a password is already set at invitation time or will be set later, so that the acceptance step does not ask for something the user has already given. `allow_insecure_sign_in_after_accept` is also enabled by default, and it signs the user in automatically once they set that password. The option name is the warning: an automatic sign-in bypasses the credential check that would otherwise run, so a link that is forwarded, logged, or left in a shared mailbox becomes a completed session for whoever opens it last. Both switches are on out of the box, which means an application that only runs the install generator and adds `:invitable` to the model inherits a password prompt and an automatic login without having written a line of configuration.
Seven columns, one unique index, and a legacy column limit to undo
Adding the module to an existing model is a migration of seven columns and one index. The generator writes it for you when the ORM supports migrations, and the same thing can be written by hand:
def change
    add_column :users, :invitation_token, :string
    add_column :users, :invitation_created_at, :datetime
    add_column :users, :invitation_sent_at, :datetime
    add_column :users, :invitation_accepted_at, :datetime
    add_column :users, :invitation_limit, :integer
    add_column :users, :invited_by_id, :integer
    add_column :users, :invited_by_type, :string
    add_index :users, :invitation_token, unique: true
end
The token is the only indexed column and the index is unique, which is what stops two invitations sharing a value. One migration is offered for people who used this gem before: if an older install had put a `:limit` on `:invitation_token`, it has to be removed, because the unique index cannot be built on a column that caps its length below what a token needs. The supplied change is reversible, with the length restored to `60` on the way down, which is a reminder that this column once carried a hard limit. A new model skips all of this: `rails generate devise_invitable MODEL` adds the `:invitable` flag to the Devise modules and creates the migration file.
Two install paths, one version boundary, and a final sentence with no ending
There are two ways in. The automatic path installs the gem and runs `rails generate devise_invitable:install`, which writes the configuration into `config/initializers/devise.rb`, then `rails generate devise_invitable MODEL` for each model that needs it. The manual path is described as following the Devise walkthrough first and then this one, which means adding `:invitable` to the `devise` call yourself and writing the migration, as in `devise :database_authenticatable, :confirmable, :invitable`. Which Devise you are on decides which gem you need, and the boundary is drawn at 4.6: the current line works with Devise 4.6 and later, and anything from 4.0 up to but not including 4.6 needs version 1.7.5 of this gem. The Gemfile line that goes with the current line pins the minor series rather than a single version:
gem 'devise_invitable', '~> 2.0.0'The mail templates ship inside the gem, so customising them means copying them out with `rails generate devise_invitable:views`, or `rails generate devise_invitable:views users` for scoped templates, and then setting `config.scoped_views = true`. The final line of the page sends readers to Devise's own README for the rest, and stops there mid-clause.
CI on two platforms, a tracked tmp directory, and no releases
The repository root shows how the gem is maintained. There is a `.github/` directory and a `.gitlab-ci.yml` at the same time, so the same test suite is wired on two hosting platforms, and a `gemfiles/` directory alongside the `Gemfile` and `devise_invitable.gemspec` indicates the suite runs against several dependency sets rather than one. Two other entries are unusual for a published gem: a `tmp/` directory sits at the root, which in a Ruby project is scratch space for generated files, and a `.document` file records what the documentation generator is allowed to read. The default branch is `master`, and the Devise links throughout the page point at the `plataformatec/devise` account. Finally, the repository publishes no GitHub releases, even though the instructions ask you to pin `~> 2.0.0` and to fall back to a specific older release, 1.7.5, for older Devise. Those two numbers are the only version references a reader gets, and the last recorded push on the default branch is 2026-08-08.
Editorial conclusion
Use DeviseInvitable when signups must be closed and access granted by email, and expect to change two defaults before it reaches production: set `invite_for` to a real period, because zero means the token stays valid indefinitely, and decide deliberately on `allow_insecure_sign_in_after_accept`, which signs the user in the moment the password is set. Pick ActiveRecord or Mongoid with care rather than by habit, since the Mongoid field list covers five of the seven columns and its documented index names a field the rest of the gem never uses. Verify the Devise version on your side of the boundary as well, since 4.6 is the cut and older releases need the 1.7.5 line of this gem. Anyone customising the mail templates should run the views generator before editing, since the templates ship inside the gem.
Frequently asked questions
How does DeviseInvitable decide that an invited email already belongs to a user?
Through the invite_key option, whose default value looks for users by email and validates with Devise.email_regexp. You can replace it with a hash where each key is an invite key and each value responds to the === operator, so procs and regexes are both allowed, which is how several matching strategies get combined.
How many invitations can a user send with devise_invitable?
The invitation_limit option has three meanings. The default nil lets users send as many as they want and the invitation_limit column is not used at all, 0 stops them sending any, and a number above zero allows exactly that many. The column can also be set per user, so individual records get more or fewer invites even when the global setting is 0.
Do I have to create MongoDB indexes by hand for devise_invitable?
Yes, on Mongoid you do, and the page says to run rake db:mongoid:create_indexes after deploying your changes. The indexes are declared with the background option in the model, which only schedules the build.
Can I change the invitation email templates that ship with devise_invitable?
All the views are packaged inside the gem, so changing them means copying them into the application first with rails generate devise_invitable:views, or rails generate devise_invitable:views users for scoped templates, and then setting config.scoped_views to true in the Devise initializer.
Which Devise versions does devise_invitable support?
The latest version works with Devise 4.6 and later. For Devise releases from 4.0 up to but not including 4.6, the instructions say to use version 1.7.5 of the gem instead.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/scambra-devise-invitable)Star history chart for your README
[](https://hysenlabs.com/projects/scambra-devise-invitable)Was this useful?