scanopy: network diagrams rebuilt from every scan
Network diagrams that update themselves
At a glance
- What is it?
- Scanopy is a self-hosted daemon that scans a network on a schedule and turns each scan into L2, L3, workload and application views. The scanning is open source under AGPL-3.0, while Confluence export and air-gapped licences are sold separately.
- Who is it for?
- Use the Community Edition when you want documentation that follows the network and you can meet AGPL-3.0's obligations. Look at the commercial tiers when Confluence export or an offline licence key for an air-gapped network is a requirement rather than a preference.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
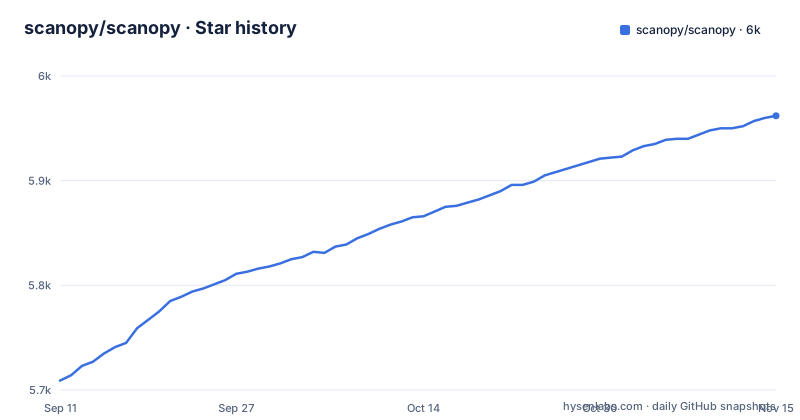
Star history
- scanopy/scanopy5,962 ★ · +253
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| scanopy/scanopy | 5.7k | 6k |
253 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One daemon, one scan, four views
Scanopy replaces hand drawn diagrams with a model built by scanning. A single daemon runs on a schedule, and every scan produces four views: L2 for the physical layer of switches, ports and links, L3 for subnets and how hosts connect across them, workloads from bare metal through hypervisors to containers, and applications, which group services with their dependencies. One scanner does all of it, with no agent installed on each device, and 410+ service definitions decide what a host is recognised as. Distributed scanning covers what one host cannot see: deploy daemons across segments to map multi-site and multi-VLAN topologies, with LLDP, CDP, switch forwarding tables and SNMP as sources. Containerized services are found natively too.
Each daemon scans the networks it can reach, on its own schedule, at the rate and subnet scope you set. Translations are handled through Weblate.
docker compose up -d brings up daemon, server and postgres
Self hosting starts with two commands. The compose file is fetched from the repository and started:
curl -O https://raw.githubusercontent.com/scanopy/scanopy/refs/heads/main/docker-compose.yml
docker compose up -d
Three services come up. The server publishes port 60072, postgres keeps its data in a named volume, and the daemon does the scanning. Then the browser step: open the UI at http://<your-server-ip>:60072, create your account, and the first discovery starts on its own. The account comes before any data because the UI is account based from the start, and the first scan is not instant.
For Portainer, the repository ships docker-compose.portainer.yml and portainer-template.json. Scanopy Cloud is the hosted option. The repository also ships install.sh and two systemd unit files, scanopy-daemon.service and [email protected], for installs that are not Docker based.
The daemon needs host networking, privileged mode and the socket
This is the part to read before deploying. The daemon service runs with host networking and privileged mode, and it is the piece that has to see the network it maps:
  daemon:
    image: ghcr.io/scanopy/scanopy/daemon:latest
    container_name: scanopy-daemon
    network_mode: host
    privileged: true
Privileged plus host networking is the combination that makes discovery reach the segments it documents, and it is also why this container belongs on infrastructure you control. The compose file points the daemon at the server through a fixed local URL:
      SCANOPY_SERVER_URL: http://127.0.0.1:60072
    healthcheck:
      test: ["CMD-SHELL", "curl -f http://localhost:60073/api/health || exit 1"]
      interval: 5s
      timeout: 3s
      retries: 15
Health is polled on port 60073, a port that never appears in the address you type. Five second intervals, a three second timeout, fifteen retries.
Container discovery rides on a read only mount of the docker socket, and a comment above it explains the off switch:
    volumes:
      - daemon-config:/root/.config/scanopy/daemon
      # Mounted for the Docker integration. Comment out the line below if you don't use it
      - /var/run/docker.sock:/var/run/docker.sock:ro
Comment out that one line and container findings go with it. Daemon configuration persists in the named volume daemon-config, mounted at /root/.config/scanopy/daemon.
Postgres 17-alpine starts with the password 'password'
State lives in Postgres, pinned to the alpine flavoured 17 image:
  postgres:
    image: postgres:17-alpine
    environment:
      POSTGRES_DB: scanopy
      POSTGRES_USER: postgres
      POSTGRES_PASSWORD: ${POSTGRES_PASSWORD:-password}
That last line is the default that costs people an afternoon. With no .env present, the compose file substitutes the literal word password, and the database sits on the compose network. The escape route is written into the file as a comment: replace the value with POSTGRES_PASSWORD_FILE pointing at a path, and uncomment the secrets block naming postgres_password. Readiness is polled with pg_isready every ten seconds, with five retries.
The server container takes its settings a second way, from a .env file beside the compose file:
  server:
    image: ghcr.io/scanopy/scanopy/server:latest
    ports:
      - "60072:60072"
A comment in the compose file says it passes a .env alongside it straight through to the server. Without one, the defaults apply: registration and password login are both on by default, and SCANOPY_DISABLE_REGISTRATION or SCANOPY_DISABLE_PASSWORD_LOGIN have to be set by hand wherever port 60072 is reachable by strangers.
Secrets can arrive from files, and a missing one stops startup
Every SCANOPY_ variable on both the server and the daemon can be read from a file instead of the environment. The convention is a companion variable: point SCANOPY_DATABASE_URL_FILE at a path and the database URL comes from that file, with trailing newlines trimmed. The same pattern covers secrets injected by Docker secrets, Kubernetes or Portainer.
The failure behaviour is defined, which is unusual enough to quote exactly. Setting both the plain variable and its _FILE form, or pointing _FILE at a file that is missing or unreadable, stops startup with an error that names the variable. A misconfigured secret therefore fails loudly at boot instead of turning into an empty password halfway through a scan.
One exception sits in the same file. The daemon's SCANOPY_LOG_FILE is a path to write logs to, not a secret to read, so its file form is SCANOPY_LOG_FILE_FILE. That is an awkward pair of names, and anyone generating configuration from a template has to know it.
The server defaults that matter most are three lines:
SCANOPY_DATABASE_URL=postgresql://postgres:password@localhost:5432/scanopy
SCANOPY_PUBLIC_URL=http://your-domain.com:60072
SCANOPY_LOG_LEVEL=info
SCANOPY_PUBLIC_URL ships with the example value http://your-domain.com:60072, so replace it with your server's address.
SMTP is encrypted or off, and .env has to be passed through
Email is optional, and the example file states its two failure modes plainly. Every SMTP connection is encrypted; there is no plaintext mode and no setting to turn encryption on. The port decides the scheme: 465 is the default when SCANOPY_SMTP_PORT is unset and uses implicit TLS, while any other port uses STARTTLS, which is what submission ports such as 587 and 25 expect. STARTTLS is required rather than opportunistic, so a failed upgrade aborts the send instead of continuing unencrypted.
The second failure mode is silent. All four of RELAY, USERNAME, PASSWORD and EMAIL must be set or email stays off, and EMAIL should match USERNAME unless that account has permission to send as another address, because most providers reject a mismatch. Password reset and notifications depend on this, so a wrong relay turns into a login problem rather than a warning.
Getting those variables into the container needs one more piece of the compose file. Compose otherwise reads .env only to interpolate values that already have a line below, so a variable with no matching environment entry would never reach the container. Passing .env straight through to the server, as the compose file comment describes, is what makes every SCANOPY_SMTP_ variable reachable at all.
Confluence export and offline keys are paid tiers
Scanopy is AGPL-3.0, and the licensing section is explicit about what that obliges you to do: source disclosure for network services and copyleft compliance. The Community Edition is the full scanning engine under that licence. The Commercial Edition is split into Self-Hosted Standard, Self-Hosted Plus and Enterprise for organizations that cannot meet AGPL-3.0's terms.
What the money buys is a specific list. Confluence export, invoice billing, procurement documents and support arrive with a commercial licence. Self-Hosted Plus adds multiple organizations. Plus and Enterprise add offline licence keys for air-gapped networks, which is the one thing the self-hosted tiers cannot otherwise deliver. Note where Confluence sits in that list: the open source install exports SVG and Mermaid, and Confluence is the gap between editions rather than a format the community build can be coaxed into.
Every edition runs on your own infrastructure, and the tree carries a second compose file, docker-compose.commercial.yml, beside the community one, plus COMMERCIAL-LICENSE.md. A third option is Scanopy Cloud, the hosted version.
Versions move quickly. v0.19.5 shipped on 2026-10-30, v0.19.4 on 2026-10-29 and v0.19.3 on 2026-10-27, with the last push to the repository on 2026-11-02. Both images in the compose file are tagged latest, so a restart can change what runs without a version bump on your side.
Editorial conclusion
Use the Community Edition when you want documentation that follows the network and you can meet AGPL-3.0's obligations. Look at the commercial tiers when Confluence export or an offline licence key for an air-gapped network is a requirement rather than a preference. Before deploying, replace the default POSTGRES_PASSWORD, decide whether registration stays open on port 60072, and pin the image tags, because both services are tagged latest and a restart can pull a different build.
Frequently asked questions
How do I use scanopy after installing it?
Open the UI at http://<your-server-ip>:60072, create your account, and the first discovery starts on its own. Every scan then produces the L2, L3, workloads and applications views, and the model can be exported as SVG, Mermaid or Confluence, embedded as a live map, or fed into an existing source of truth.
How do I set up scanopy for self hosting?
Fetch the compose file from the repository and run docker compose up -d, which starts the daemon, the server on port 60072 and postgres. The repository also ships docker-compose.portainer.yml and portainer-template.json for Portainer.
Is scanopy free, or does the Community Edition fall short?
The Community Edition is free and open source under AGPL-3.0, which requires source disclosure for network services and copyleft compliance. Confluence export, invoice billing, procurement documents and support are commercial, and Self-Hosted Plus and Enterprise add multiple organizations and offline licence keys for air-gapped networks.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/scanopy-scanopy)Star history chart for your README
[](https://hysenlabs.com/projects/scanopy-scanopy)Was this useful?