RootBeer: nine checks, two of them the same check, and one duplicate in native
Simple to use root checking Android library and sample app
At a glance
- What is it?
- An Android root-detection library whose readme opens by saying there is no guaranteed way to check for root, recommends a competitor's attestation API instead, links a public write-up showing how to defeat it, still lists a BusyBox check that another section says it removed, and carries a native layer that adds exactly one check the Java layer already performs.
- Who is it for?
- RootBeer is worth reading as an honest artifact rather than adopting as a security control, because its documentation tells you exactly how far it can be trusted and where it fails. Use it if you want a best-effort signal for telemetry or for a soft warning, and treat the answer as one input among several, which is what its own readme instructs.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 8 months ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
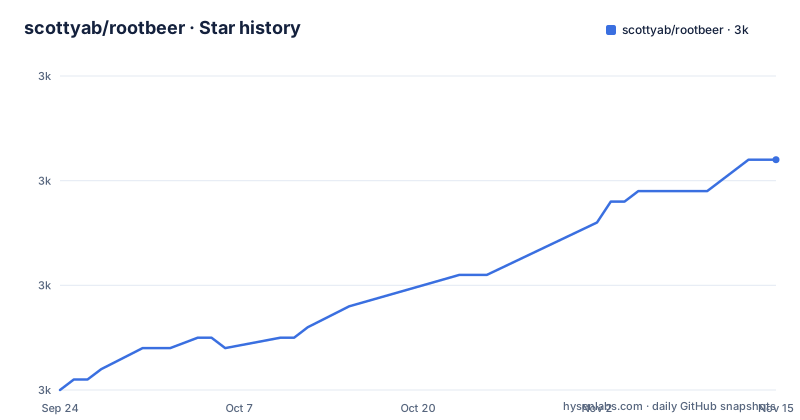
- scottyab/rootbeer2,972 ★ · +22
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| scottyab/rootbeer | 3k | 3k |
22 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
root equals god, and the docs point you at somebody else's API
The most useful section of the readme is the disclaimer, and it is unusually blunt. One way to think about root checking is that root equals god, so there is no guaranteed way to check for it. You are asked to treat the library's results as an indication of root together with other factors that vary by use case, rather than basing your whole security posture on the result.
Then comes the sentence that makes this page worth reading on its own: a more solid solution would be to use Google's Play Integrity API, which verifies that requests come from your unmodified app binary, installed by the store, running on a genuine device. That is a competing commercial attestation product, and the library's documentation recommends it instead of itself. For a security tool, naming the thing that does the job properly and telling its own users to go there is a level of candour that is easy to overlook and hard to replicate.
The page then adds that RootBeer can be bypassed, that several articles illustrate how, and links one of them, noting that it was found with a quick search. That is the maintainers publishing a pointer to a technique for defeating their own library.
Nine checks, and every row carries its own caveat
The checks are laid out as a table with three columns: a method name, what it does, and what it cannot do. The third column is the interesting one, because it is populated on every single row and it is where the real information sits.
The set covers apps for managing root access such as the well-known managers, a separate list of apps known to facilitate root, apps that cloak root from detection, firmware signed with Android's test keys, two dangerous system properties, the presence of a BusyBox binary, the presence of the privilege escalation binary by two different routes, and whether the system partition is mounted writable. Three of the caveats are worth pulling out. Cloaking apps evolve quickly and may bypass the detection mechanisms aimed at them. The properties check can be bypassed if the properties are reset or hidden. And the writable-partition check misses newer methods, because some rooting approaches deliberately do not require write access to that partition.
Two of the nine are the same check twice: one looks for the escalation binary as a file, the other asks the system to locate it. The limitations column says the same thing for both, which is at least honest about the redundancy.
The native layer adds one duplicate check
There is a native section, and it is two sentences plus a one-row table. The explanation is that the library calls through to its native checker to run some checks of its own, that native checks are typically harder to cloak, and that some cloaking apps respond by blocking the loading of native libraries whose filenames contain certain keywords.
The table then lists one method. It is the escalation-binary check again, and the limitations column refers back to the Java version of the same check. So the entire native layer, the part the documentation describes as harder to cloak and the part that ships compiled code into the app, adds a duplicate of a check the Java layer already performs. That is worth knowing before you take the dependency: the native path is not a second opinion, it is the same opinion asked in a different language, and it is defeated by a different and simpler trick, which is filename filtering at load time.
The BusyBox check is in the table and was removed from the aggregate
There is a contradiction between two sections that a reader will hit in the wrong order. The checks table lists a BusyBox binary check with a caveat explaining that not all rooted devices ship it and some manufacturers leave it on stock builds. Further down, a section on false positives explains that manufacturers do leave that binary in production builds, that this does not always mean the device is rooted, and that the check used to be included as standard inside the aggregate method has been removed to avoid those false positives.
So a reader who takes the table at face value will believe the aggregate result includes a BusyBox check, and a reader who reads on learns it does not. The opt-in is documented properly further down: one call detects the binary on its own, and another runs the full detection with the check reinstated. The false-positive list is also worth noting for its age, since it names a handset with an operating system version and a security patch from January 2018, and a whole manufacturer as a category.
rootBeer.isRootedWithBusyBoxCheck();A hackday project, tested in 2015, never retested
The background section says this started as a hackday project whose goal was to see whether the authors could beat the cloaking tools of the time, in 2015. It then states the position of the two creators, who both own rooted devices though not as daily drivers, and adds that when an app blocks rooted users, that is not the responsibility of this library: raise the concern with the app doing the blocking.
Then there is a section on cloakers, and it is the only place the readme records a test result. In 2015 the library was tested against two cloaking tools and flagged an indication of root against each one. It was defeated when a combination of those cloakers was active at the same time. Two cloakers, two frameworks they depend on, one test, dated eleven years before the last commit in the repository, and no statement that it was repeated.
So the honest summary is that the library was tested once, individually, against two tools, and lost when the tools were combined. Everything else on the page is the check list and its caveats.
Version 0.1.2, an eighteen-month gap, and a module file with the old name
The release record is three increments in five years. The first was published in May 2021, the second in September 2024, and the third in March 2026, which means an eighteen-month silence between the last two and a three-year gap before that. The version is still below one, and the last commit to the default branch is dated 2026-03-17, so read the current state of the repository rather than a summary of it.
The tree tells a similar story about names. There is a module file for an IntelliJ project that is called by the project's older name while everything else uses the newer one, which is the sort of residue that accumulates when a project is renamed and nobody opens the IDE configuration again. The build is a two-module Gradle project in the Kotlin dialect, one module for the library and one for the sample app, with the wrapper committed. The changelog file is not spelled the conventional way at the root. And the badge row has exactly one entry, pointing at a third-party statistics site for download numbers, with no build, coverage or licence badge anywhere.
The one usage note that matters for your app is that the aggregate call does disk input and output, so the readme advises calling it from a background thread.
Editorial conclusion
RootBeer is worth reading as an honest artifact rather than adopting as a security control, because its documentation tells you exactly how far it can be trusted and where it fails. Use it if you want a best-effort signal for telemetry or for a soft warning, and treat the answer as one input among several, which is what its own readme instructs. Do not gate anything valuable on it: the page says root cannot be checked with certainty, links material demonstrating bypasses, and points you at a platform attestation service instead. If you adopt it, call the aggregate check off the main thread, choose the BusyBox variant deliberately, and give each application sharing a code base its own prefix string rather than the default.
Frequently asked questions
What does RootBeer do on Android?
It gives an indication of whether a device is rooted. The library runs nine Java checks and calls a native checker, covering root management apps, apps that facilitate root, cloaking apps, test-key firmware, two dangerous system properties, a BusyBox binary, the privilege escalation binary by two routes, and whether the system partition is mounted writable.
Is RootBeer reliable at detecting root?
The readme says no. It states there is no guaranteed way to check for root, tells you to treat the result as an indication alongside other factors rather than a security decision, notes that the library can be bypassed and links an article showing how, and recommends a platform attestation API as the more solid approach.
Why did RootBeer drop the BusyBox check from its main check?
Because manufacturers sometimes leave that binary in production builds, which produced false positives. The readme says the check was removed as standard from the aggregate method, and documents an opt-in that runs full detection with the check reinstated, as well as a call that detects the binary on its own.
What does RootBeer say about the native checks?
That native checks are typically harder to cloak, so some cloaking apps respond by blocking the loading of native libraries whose filenames contain certain keywords. The native table lists one method, which duplicates the Java check for the privilege escalation binary.
How do I call RootBeer, and where do I get it?
Construct it with your context and call the aggregate method, which the readme advises doing from a background thread because it involves disk input and output, or call individual checks yourself. It is published on Maven Central, and the repository is a two-module Gradle project with a library module and a sample app.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/scottyab-rootbeer)Star history chart for your README
[](https://hysenlabs.com/projects/scottyab-rootbeer)Was this useful?