Scapy: packet defaults, root privileges, and a clone-based install
Scapy: the Python-based interactive packet manipulation program & library.
At a glance
- What is it?
- Scapy is a Python packet manipulation library and interactive shell that builds packets from working defaults, sends and captures them, and reads pcap files. It claims to cover hping, tcpdump, p0f and most of nmap at the packet layer, but the repository documents a git clone install, punts raw 802.11 specifics to the documentation, and warns that some tutorial examples have aged.
- Who is it for?
- Scapy is the right pick when the traffic you need to build or inspect does not fit what a scanner will emit, and when the surrounding team can already read Python well enough to keep small scripts around. It is the wrong pick as a drop-in GUI dissector, as an nmap replacement, or on a host where unprivileged raw sockets are not an option.
- Can I use it commercially?
- Yes, with conditions. GPL-2.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
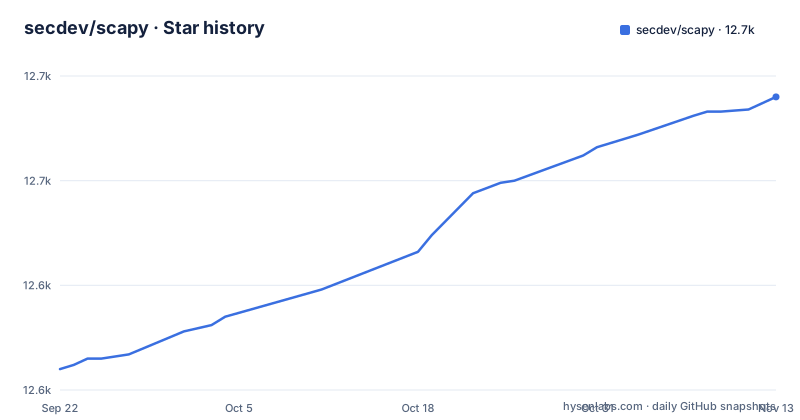
- secdev/scapy12,690 ★ · +130
| Repository | 2026-09-22 | 2026-11-13 |
|---|---|---|
| secdev/scapy | 12.6k | 12.7k |
130 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Defaults are the API: layer stacking and sr1
Scapy's design bet is that a packet should be writable from its defaults. You name the destination and the protocol family, let everything else fall into place, and then ask for the reply. The shell demo in the README is the whole idea in a few lines:
sudo ./run_scapy
Welcome to Scapy
>>> p = IP(dst="github.com")/ICMP()
>>> r = sr1(p)
Begin emission:
.Finished to send 1 packets.
*
Received 2 packets, got 1 answers, remaining 0 packets
>>> r[IP].src
'192.30.253.113'
IP(dst="github.com")/ICMP() builds an IPv4 packet carrying an ICMP body, sr1(p) sends it and waits for a single answer, and r[IP].src reaches into the reply layer for the source address. The output is worth reading closely: two packets came back for the one that was sent, and a dot interleaves with a star as progress and replies land. The stated goal is fast packet prototyping using default values that work, which is exactly why no checksum, length or source address is written out. The trade is that an implicit field stays invisible until the day you need it, so reading back what was actually built rather than assuming the defaults is the habit worth forming early.
The replacement claim is about packets, not about workflows
The project makes an explicit replacement claim, and the shape of that claim matters more than the number in it. The list runs to hping, 85% of nmap, arpspoof, arp-sk, arping, tcpdump, wireshark and p0f. Read that as a claim about how much packet-level reach one library has, not about how much of each tool you get back. It also does not mean Scapy automates scanning. The framing sentence puts scanning, tracerouting, probing, unit tests, attacks and network discovery in the same breath as packet handling, which is a different assertion from shipping a scanner with service detection and host classification. For a team weighing whether to retire tcpdump or p0f from a toolbox, the accurate reading is that a scriptable packet layer is on offer, and the higher-level tooling you would have to rebuild around it is not enumerated anywhere in the README.
Invalid frames and hand-built 802.11 are the reason it exists
The capability that sets it apart from the tools in that replacement list is sending invalid frames, injecting your own 802.11 frames, and combining techniques, with VLAN hopping plus ARP cache poisoning and VoIP decoding on a WEP protected channel offered as the examples. The combination is the point rather than any single trick, because each of those needs frames that a conforming emitter refuses to produce. The cost of that position is documentation. The README does not say which link layer Scapy drives on which adapter, does not list the platforms where raw 802.11 injection is available, and does not state the driver or permission requirements for it. So for an 802.11 research plan, this repository is a starting point and the documentation is where the platform specifics must be confirmed, because there is no capability matrix here to check a requirement against. The same gap shows up for the combination examples: the techniques are named in a sentence, with no sample script, no packet breakdown and no stated operating system attached to them.
The documented install is a git clone, and Windows is the exception
The install path on most systems is three lines, and each one has a consequence:
git clone https://github.com/secdev/scapy
cd scapy
./run_scapy
The shell needs root, which is why the demo opens with sudo ./run_scapy, and the repository root carries a parallel run_scapy.bat for Windows. On Linux and BSD style systems Scapy works with no external Python modules at all, while on Windows the documentation describes mandatory dependencies you install yourself, and optional capabilities are extra modules: plotting wants matplotlib, and cryptography covers the encrypted paths. Two things a reader hunting for a package install will not find here. There is no pip or PyPI command anywhere in this README, even though a PyPI project badge is linked at the top, and distribution coverage is reduced to a repology packaging status link. An environment with no git, or one where outbound clones are blocked, has to go to the installation documentation instead of this page. There is also no statement about pinning the clone to a tag, which matters the moment your build needs to be repeatable.
GPL v2 for the code, a non-commercial licence for the docs
The licensing is split, and the split is easy to read past. Scapy's code, tests and tools are licensed under GPL v2, pyproject.toml declares GPL-2.0-only, and the project authors are named as Philippe BIONDI and Gabriel POTTER. The documentation, meaning everything in doc/ unless marked otherwise and except the logo, is licensed under CC BY-NC-SA 2.5. That NonCommercial clause has teeth for one specific audience: if you are a vendor or a consultancy and you want to reuse the tutorial text, the reference pages or the notebooks in customer training or in your own manual, the documentation licence does not grant it and the restriction is not something the code licence overrides. The code side is the other half of the check. GPL v2 is copyleft, so pulling Scapy into a product you distribute gives your users obligations you have to plan for, and nothing here discusses relicensing, exceptions or a commercial grant. If either question is live for you, it needs answering before the clone, not after.
Python 2 died behind a build-time error, and versioning is hand rolled
Python 2 support ended with a guard in the build script rather than a line in a changelog. setup.py inspects the interpreter and raises an OSError telling you that Scapy no longer supports Python 2 and to use Scapy 2.5.0, and it raises a separate ImportError when setuptools is missing, so a broken environment fails at install rather than at first import. On the supported side, requires-python is set to >=3.9, <4, the README states Python 3.9+, and the classifiers enumerate 3.9 through 3.14. What those numbers do not tell you is which of those interpreters the suite currently exercises, because classifiers are a declaration rather than a test matrix, and tox.ini alongside a Travis configuration are where a real matrix would live. The versioning is deliberately unconventional. The setup script keeps its own scapy/VERSION file instead of using setuptools_scm, and the comment inside the file gives the reason: derived versioning sets the version into wheels but breaks source distributions, which carry no git metadata. The installed console entry point is therefore a plain scapy mapped to scapy.main:interact.
A master tarball link and an outdated-example warning
Activity is current and the release numbering explains very little. The last push to the master branch is dated 2026-11-01 and the repository is not archived. The recent tags are v2.8.0 on 2026-10-02, v2.7.0 on 2025-12-26 and v2.6.1 on 2024-11-05, leaving roughly a year between the 2.6.x and 2.7.x lines, and nothing in the README explains that gap or promises a schedule. Two details matter more than the dates for anyone building this. The Download URL in pyproject.toml points at the master branch tarball instead of a tagged archive, so following it literally hands you whatever sits on the branch tip rather than a release, and a build that copies that URL pins nothing at all. Second, the quick demo page in the documentation carries an explicit warning that some of its examples may be outdated, which tells you to treat older tutorial snippets as a starting point rather than reference material. The supporting files you would expect are all present, including SECURITY.md, CONTRIBUTING.md, AGENTS.md, MANIFEST.in and a .packit.yml for distribution packaging, plus the notebooks under doc/ for HTTP/2 and TLS work.
Editorial conclusion
Scapy is the right pick when the traffic you need to build or inspect does not fit what a scanner will emit, and when the surrounding team can already read Python well enough to keep small scripts around. It is the wrong pick as a drop-in GUI dissector, as an nmap replacement, or on a host where unprivileged raw sockets are not an option. Before you commit, read the installation documentation for the Windows dependency set, pin a git tag rather than the branch, and check the CC BY-NC-SA 2.5 terms on the documentation if any of it will end up in customer-facing material.
Frequently asked questions
What is Scapy used for?
Scapy forges or decodes packets across a wide number of protocols, sends them on the wire, captures them, stores or reads them from pcap files, and matches requests with replies. The README frames this as scanning, tracerouting, probing, unit tests, attacks and network discovery.
Is Scapy a Python module?
It is both, usable either as a shell or as a library, with requires-python set to >=3.9, <4. The installed entry point is a scapy console script mapped to scapy.main:interact, and optional extras include cli as ipython.
What are the limitations of scapy?
The shell needs root, so the demo runs sudo ./run_scapy. Windows requires mandatory dependencies from the installation documentation, plotting needs matplotlib, and the replacement claim covers 85% of nmap rather than all of it, leaving the rest of that tool to something else.
how to install scapy in python
The README documents a clone, cd and ./run_scapy sequence, and states that Scapy works with no external Python modules on Linux and BSD style systems. No pip command appears on that page, so the installation documentation is the place to check for other routes.
how to use scapy on windows
Windows is the documented exception: the README says you need to install some mandatory dependencies, described in the installation documentation. The repository ships run_scapy.bat next to run_scapy so the interactive shell has a Windows entry point.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/secdev-scapy)Star history chart for your README
[](https://hysenlabs.com/projects/secdev-scapy)Was this useful?