Securo puts bank credentials in a .env file, and refuses to start if you half-configure OIDC
Open-source personal finance manager. Self-hosted, privacy-first.
At a glance
- What is it?
- A look at a self-hosted finance manager: two install paths of very different risk, a compose file with a Podman workaround and development defaults in it, three bank sync providers with three different credential shapes, a free tier that silently returns nothing unless you pre-link your accounts, and a login configuration that fails loudly instead of locking you out.
- Who is it for?
- Securo fits someone who wants their financial data on their own machine, is comfortable with a compose file and an environment file, and can pick a bank sync provider for their region. It does not fit someone who wants someone else to run it, and it does not fit a European bank connection on the Enable Banking free plan without doing the pre-linking step first.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
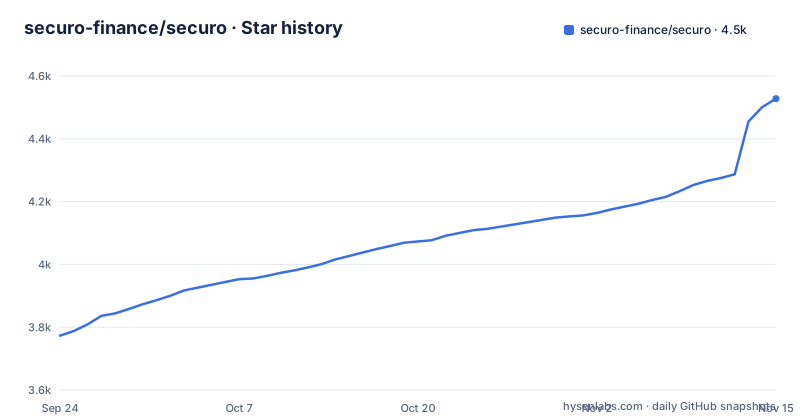
- securo-finance/securo4,528 ★ · +755
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| securo-finance/securo | 3.8k | 4.5k |
755 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One install path pipes a remote script into a shell, the other clones and builds
The quick start offers two routes and they are not equivalent in what they do to your machine.
On Linux and macOS the whole install is one line:
curl -fsSL https://usesecuro.com/install.sh | bashThat script is fetched from the project's own domain and executed immediately, and the documented behaviour is that it uses Docker or Podman and installs Docker if neither is present. So the shortest path also means installing a container runtime if you have not got one.
Windows takes the explicit route: install Docker Desktop, then clone and build.
git clone https://github.com/securo-finance/securo.git && cd securo
docker compose up --build
That path is auditable. You have the repository on disk, the compose file is in front of you, and nothing from the network is executed as a script.
Either way you end at http://localhost:3000 and create an account. Note the release numbers: v0.16.1 on 2026-09-22, v0.16.2 on 2026-09-25 and v0.16.3 on 2026-10-04. Three patch releases in twelve days, and the version is still 0.x, so treat the API and data model as moving.
The compose file carries a Podman workaround and development defaults side by side
docker-compose.yml is named, not default, and its first interesting content is a key that exists for a second runtime:
x-podman:
  in_pod: false
The comment above it explains the reason: podman-compose groups all services into a single pod by default, which interferes with per-service port mapping and networking, and disabling that makes it behave like Docker Compose. The note that Docker ignores unknown top-level x- keys is what makes the workaround safe, since the same file has to serve both runtimes.
The same file also hands you development defaults. The database URL points at a postgres service with postgres:postgres as the credentials, the secret key defaults to dev-secret-change-in-production, and DEBUG defaults to true. Those defaults are what make the clone-and-build path work with no configuration at all.
The one you must not keep is the secret key. The .env.example file names SECRET_KEY=change-me-in-production under a Required heading, and the compose default is the same idea in another form. Everything else in the file is a pass-through with an empty or sensible default, which is why the same compose file works for someone with no bank sync and for someone with all three providers configured.
Three bank providers, three completely different credential shapes
Bank sync is optional, configured entirely through .env, and enabled by presence rather than by a master switch: each provider auto-registers when its credentials are present, and the readme asks you to configure one or both and then restart with docker compose up.
Pluggy covers Brazilian banks and takes the conventional pair, PLUGGY_CLIENT_ID and PLUGGY_CLIENT_SECRET.
Enable Banking covers European PSD2 banks and takes three values, of which one is a file path. You create a Production application, download its PEM private key, save the PEM under ./secrets/ which is gitignored, then set ENABLE_BANKING_APP_ID, ENABLE_BANKING_PRIVATE_KEY_FILE and ENABLE_BANKING_OAUTH_REDIRECT_URI. That is a key pair on disk rather than a token in an environment variable, and the compose default path for the PEM is inside the container's /app/secrets.
SimpleFIN is the odd one out because it has no API key at all. It is described as a read-only open protocol where each connection brings its own credentials through a single-use Setup Token from the SimpleFIN Bridge, so all you configure is whether it is on and which bridge to talk to. In the interface you paste the token under Accounts, Connect Bank, SimpleFIN.
So the cost of a provider is not comparable across the three: credentials you sign up for, a key file plus an exact redirect URL match, or a one-time token.
The Enable Banking free plan returns no accounts unless you pre-link them first
One of the documented failure modes is specific enough to plan around. Enable Banking's free plan runs in what the readme calls a restricted mode: you have to pre-link the accounts you want to import inside the Enable Banking portal before connecting from Securo.
If you skip that step the connection returns no accounts. Securo does not leave you guessing, though: it surfaces a banner with a link to the provider's portal, so the empty list is explained rather than merely empty.
The HTTPS requirement is the other trap. Production Enable Banking requires HTTPS, and the redirect URI you register has to match exactly one of the allowed redirect URLs in the application. That combination means a local install cannot complete a production connection at all, so for local development the documented options are to expose your frontend through a tunnel such as ngrok or cloudflared, or to use the Enable Banking sandbox.
Practical consequence: if you are evaluating this on a laptop, expect to use a sandbox or a tunnel, and expect the sandbox to have different account coverage than a production connection. The pre-linking requirement applies to the free plan, so a paid production account does not behave this way.
SimpleFIN trades an API key for a single-use token and a bridge URL you can point at a sandbox
SimpleFIN is described as a read-only open protocol with no API key needed, where each connection brings its own credentials through a single-use Setup Token from the SimpleFIN Bridge. The configuration is therefore two lines:
SIMPLEFIN_ENABLED=true
SIMPLEFIN_API_URL=https://beta-bridge.simplefin.org   # sandbox; use bridge.simplefin.org for real banks
The comment is doing the real work there. The default URL in the compose file is the beta bridge, which is a sandbox, and the comment tells you to switch it to the non-beta host for real banks. The compose default and the .env default agree on the sandbox, which means a fresh install has no path to your actual bank until you change one value.
Read-only is the other constraint that belongs in your expectations rather than in a footnote. SimpleFIN gives you balances and transactions and nothing else, so it cannot drive the features that write: budgets, recurring transactions, goals or asset valuations all remain manual.
There is a way to try the whole path without a real bank. The SimpleFIN developer page issues free demo tokens, so you can exercise the connect-and-import flow against the sandbox bridge and confirm that your compose configuration works before you point it at a live account.
OIDC-only mode refuses to start unless three variables are set
Securo can delegate login to any standard OIDC provider, including Authentik and Pocket ID, by registering one redirect URI, the callback path under /api/auth/oidc/callback, and setting OIDC_ENABLED, the provider name, the discovery URL, a client id and a client secret. The redirect variable is optional and defaults to the frontend URL with that same callback path appended.
The interesting part is what happens when you want to require single sign-on and nothing else. Setting LOCAL_AUTH_ENABLED=false does that, and the validation rules are spelled out: the instance will start in this mode only when OIDC_ENABLED, OIDC_CLIENT_ID and OIDC_DISCOVERY_URL are all configured. Otherwise startup fails with a validation error, rather than coming up with no usable login method.
That is a deliberate choice and it is worth internalising before you try it. A configuration mistake produces a refusal to start, not a silently open instance.
There is one more asymmetry to know. If only the optional OIDC configuration request fails, the client keeps the local controls visible with a warning, but the backend stays authoritative and still rejects them in OIDC-only mode. The button you can still see is not a button that works.
On a fresh OIDC-only instance the first administrator has to arrive through OIDC
This is the failure mode that locks people out, and the readme addresses it head on.
On a fresh OIDC-only instance, the first account must be provisioned through OIDC, because there is no other path to creating one. The instruction is to keep OIDC_AUTO_REGISTER enabled, turn on OIDC_SYNC_ROLES, and make sure one of the values listed in OIDC_ADMIN_ROLES appears in that identity's configured roles claim, so that the first login becomes a Securo administrator rather than an ordinary user.
The order matters, and the readme says so: do not disable OIDC auto-registration before at least one matching account exists. Turn it off early and there is no way back in, because the account that would have been your administrator is the thing you have disabled.
Two other switches sit next to this one and control something different: OIDC_AUTO_REGISTER handles whether new OIDC identities get accounts, and OIDC_EXISTING_USER_LINK_MODE controls whether an OIDC login is linked to an existing account. Provisioning and linking are separate decisions, and confusing them is how an instance ends up with duplicate identities or with an existing account that never links.
Turning off local auth hides a long list of controls without deleting your data
The behaviour of LOCAL_AUTH_ENABLED=false is enumerated rather than summarised, and the list is long because it covers ceremonies rather than just a login form.
With local auth disabled, Securo rejects password and passkey login, public registration, first-admin password setup, the creation of password-backed users through an admin or workspace invite, forgot and reset password requests, password updates, new passkey registration or verification, and new TOTP setup or enablement. The local credential controls are hidden from the login, account, setup, registration and admin user-management screens.
What it does not do is delete anything. Existing users, password hashes, active sessions, passkeys and TOTP configuration all survive, and existing passkeys and TOTP can still be removed as cleanup paths. That distinction is the reason to be comfortable with the switch: disabling local authentication revokes the ceremonies, not the records.
Two features are worth noting alongside it. Two-factor authentication with TOTP comes with brute-force protection as a stated feature, and there is an optional AI Agents component described as self-hosted language model chat with tool use over your data plus a per-agent retrieval knowledge base. The optional label is doing real work: nothing in your data has to leave the machine unless you turn that on.
Editorial conclusion
Securo fits someone who wants their financial data on their own machine, is comfortable with a compose file and an environment file, and can pick a bank sync provider for their region. It does not fit someone who wants someone else to run it, and it does not fit a European bank connection on the Enable Banking free plan without doing the pre-linking step first. Before you expose it beyond localhost, replace the development SECRET_KEY default, work out which bank sync provider you can actually use, decide whether local authentication stays on, and read the OIDC-only section carefully, because turning local auth off changes what the instance will and will not let you do afterwards.
Frequently asked questions
What is Securo?
An open-source personal finance manager that runs on your own infrastructure, self-hosted and privacy-first, licensed AGPL-3.0. The repository's own framing is that finance apps want your data and this one does not. Once running, the web interface is at http://localhost:3000.
Is Securo a legitimate company, and who maintains it?
It is a self-hosted project rather than a hosted service. The repository links its own website, a demo instance, a roadmap, documentation, a Discord server, and a booking page described as talk to the maintainer. The licence is AGPL-3.0 and the most recent release is v0.16.3, published on 2026-10-04.
What are the practical limits of Securo's bank sync?
Each provider has its own shape. Pluggy covers Brazilian banks with a client id and secret, Enable Banking covers roughly 2500 European PSD2 banks but its free plan requires accounts to be pre-linked in the provider portal before you connect or no accounts are returned, and SimpleFIN is read-only with no API key, using a single-use setup token and a sandbox bridge URL by default.
How do I get help with Securo, or turn off local logins?
The readme links documentation, a Discord server and a booking link described as talk to the maintainer. Turning off local authentication is done with LOCAL_AUTH_ENABLED=false, which requires OIDC_ENABLED, OIDC_CLIENT_ID and OIDC_DISCOVERY_URL to be set, otherwise startup fails with a validation error.
Does Securo import statement files, or does it only connect to banks?
Both. File import covers OFX, QIF, CAMT and CSV, and bank sync runs through the three providers in parallel. Alongside that it has multi-currency with automatic FX conversion, budgets and recurring transactions, goals with progress tracking, asset valuation tracking, and net worth and income versus expenses reports.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/securo-finance-securo)Star history chart for your README
[](https://hysenlabs.com/projects/securo-finance-securo)Was this useful?