PcapPlusPlus: three layer libraries, one header per class, a conan line written for an older client, and date-shaped versions
PcapPlusPlus is a multiplatform C++ library for capturing, parsing and crafting of network packets. It is designed to be efficient, powerful and easy to use. It provides C++ wrappers for the most popular packet processing engines such as libpcap, Npcap, WinPcap, DPDK, AF_XDP and PF_RING.
At a glance
- What is it?
- seladb's PcapPlusPlus wraps seven packet capture engines behind one C++ interface and splits itself into Common++, Packet++ and Pcap++. The README documents package managers and release signing in detail, then stops before giving any build command, and its twenty-three example directories do not agree with each other on how to spell DPDK, PF_RING or DNS.
- Who is it for?
- Use it if you need one C++ interface across libpcap, Npcap, WinDivert, DPDK, AF_XDP or PF_RING, and read the feature list rather than the project description, since the description leaves two engines out. Plan around two gaps.
- Can I use it commercially?
- Yes. Unlicense is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
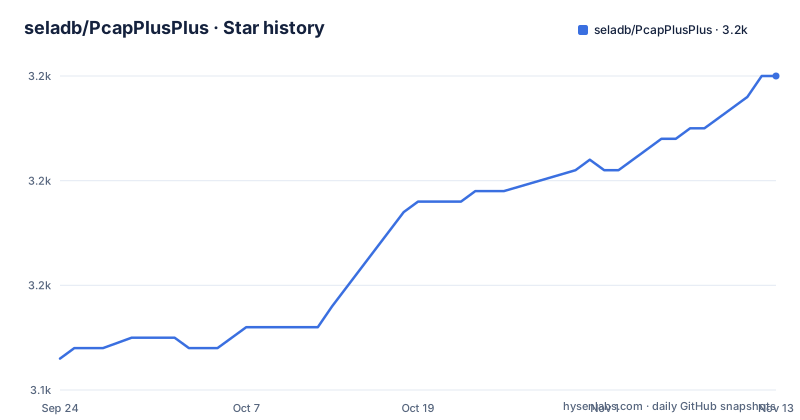
- seladb/PcapPlusPlus3,170 ★ · +27
| Repository | 2026-09-24 | 2026-11-13 |
|---|---|---|
| seladb/PcapPlusPlus | 3.1k | 3.2k |
27 Stars in the last 50 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Versions are shaped like dates, and the gaps are a year apart
The release names do not follow semantic versioning. They are v26.07, described as the July 2026 Release and tagged on 2026-07-23; v25.05, the May 2025 Release, tagged on 2025-05-15; and v24.09, the September 2024 Release, tagged on 2024-09-19.
So the number encodes year and month, with no patch component and no minor or major semantics to read into. The intervals are uneven as well: eight months between the September 2024 tag and the May 2025 one, then fourteen months to the July 2026 one.
That shape has one practical consequence worth planning for. A dependency declared as accepting any newer version is not expressing what this project means, so a consumer pinning a build has to decide whether it wants the newest release or the one it was tested against, and the tag names give no help in deciding that.
Three package recipes, and the conan line is written for an older client
The download section offers three routes before it offers to build from source, and each one gets its own command.
brew install pcapplusplusis the Homebrew recipe. Vcpkg is given in two variants, one for Windows with a leading path and one for MacOS and Linux:
vcpkg install pcapplusplusConan is a single line:
conan install "pcapplusplus/[>0]@" -uThat reference carries a bracketed version range and a trailing update flag, which is the older Conan client form, and the readme states no minimum client version for it. So a user on a current Conan is the one most likely to hit something in that line that needs translating.
The build-it-yourself route is where the README stops. It gives a clone command and nothing else, then sends the reader to the Build From Source page on the project website for platform instructions, even though a CMakeLists.txt sits at the root of the repository.
Package verification is the one place with a documented expected result
Most READMEs stop at installing. This one carries a section on checking what arrived.
Releases newer than v23.09 are signed with GitHub attestation, and every attestation is listed on the repository's own attestations page. The verification is a single GitHub CLI command:
gh attestation verify <path-to-package-file> --repository seladb/PcapPlusPlusWhat you should see afterwards is spelled out too: a check mark followed by the words Verification succeeded. It is the only place in the document where success output is given as literally as the command.
The cutoff date is the part that matters operationally. Everything released after v23.09 is inside the signed set, which covers all three releases listed in this repository's own history. Anything older, including copies a package manager has held for years, falls outside what this command can vouch for.
Three libraries, and every class arrives through its own header
The root of the repository is a three-library layout with supporting directories around it: Common++ for shared base types, Packet++ for parsing and crafting, and Pcap++ for capture, plus 3rdParty/ for vendored dependencies, Tests/, Examples/, ci/, and cmake/.
That split is visible in the getting started sample, which is also where the header convention shows:
#include <iostream>
#include "IPv4Layer.h"
#include "Packet.h"
#include "PcapFileDevice.h"
One include per class. There is no umbrella header in this example, so a file that touches a device, a packet and a protocol layer pulls three headers rather than one. That is a deliberate style, and it is also what makes the file-by-class API surface in Packet++ and Pcap++ visible in the first place.
The sample itself opens a reader on a file named 1_packet.pcap, checks the result of open(), and reports a failed open through the standard error stream before returning. The example ends there, before the packet is read or parsed.
Twenty-three example directories whose names disagree with each other
The Examples directory is the closest thing this project has to a test of its own API, and it is worth reading as a list.
Capture basics sit in ExampleApp, PcapPrinter, PcapSearch and PcapSplitter. Protocol and analysis work sits in DNSResolver, HttpAnalyzer, SSLAnalyzer, X509Toolkit, TLSFingerprinting, TcpReassembly, IPFragUtil, IPDefragUtil, IcmpFileTransfer and KniPong. Each hardware path has its own pair: DpdkBridge, DpdkExample-FilterTraffic, PfRingExample-FilterTraffic and XdpExample-FilterTraffic. Two directories are named for what they do to the network rather than for a protocol: ArpSpoofing and DnsSpoofing. PcapPlusPlus-benchmark is the performance harness and Tutorials holds the guided material.
The naming is inconsistent in three specific ways. The fragment and defragment tools differ by one letter in the same style, IPFragUtil and IPDefragUtil, with no other hint which does which. DNSResolver is in capitals while its neighbour DnsSpoofing is not. And the directories spell the engine names as Dpdk and PfRing while the prose spells them DPDK and PF_RING.
For a project whose pitch is portability, the naming is the part most likely to send someone to the wrong directory.
Eight hygiene files, one of them named for a migration
The repository carries more static-analysis configuration than most libraries of this size, and the file names say what each one is for.
There is .clang-format for formatting, .clang-tidy-new for static analysis, .gersemirc for commit message conventions, .codespellrc together with codespell-ignore-list.txt for one spell checker, typos-config.toml for a second one, cppcheckSuppressions.txt for suppressions, and .pre-commit-config.yaml to run the lot. A ninth file, .git-blame-ignore-revs, marks the commits a bulk reformat produced so blame skips them.
Two of those names are unusual. The tidy configuration carries a -new suffix rather than being named .clang-tidy, which reads as a configuration staged alongside an older one rather than a settled choice. And two separate spell checkers are configured, with an ignore list for one of them, so the same word can be argued about twice.
For contributors the practical effect is that a pre-commit hook may rewrite or block a commit for reasons that live in those files rather than in CONTRIBUTING.md.
The description lists six engines and the feature list names eight
The project's own one-line description names the capture engines it wraps: libpcap, Npcap, WinPcap, DPDK, AF_XDP and PF_RING. That is six.
The feature overview names eight. It adds WinDivert, and it adds raw sockets, which is not a third-party library at all but a platform primitive. It also splits the list across two claims, with the first describing packet capture through the engines and a fourth describing in-line-rate processing through DPDK, AF_XDP and PF_RING, so the same three engines appear twice in different roles.
The rest of that list is where the library's identity sits: reading and writing packets from and to files in both PCAP and PCAPNG formats, TCP reassembly covering retransmission, out-of-order packets and missing data, IP fragmentation and defragmentation for both IPv4 and IPv6, packet filtering that makes libpcap's BPF filters more user-friendly, and a JA3 and JA3S TLS fingerprinting implementation.
Platform support is stated as Linux, MacOS, Windows, Android and FreeBSD, which is broader than the three package managers the download section documents.
Editorial conclusion
Use it if you need one C++ interface across libpcap, Npcap, WinDivert, DPDK, AF_XDP or PF_RING, and read the feature list rather than the project description, since the description leaves two engines out. Plan around two gaps. There is no build command in the readme, so building from source means following the website page, and the Conan line is written in the older client form with no version stated. If you install from a package manager, verify provenance with the gh attestation command instead of trusting the copy, since only releases after v23.09 carry attestations.
Frequently asked questions
What is PCAP used for?
In this repository PCAP is a capture file format, handled alongside PCAPNG. The feature overview states that packets can be read from and written to files in both formats, and the getting started example opens one with a pcpp::PcapFileReaderDevice pointed at a file named 1_packet.pcap before checking whether it opened.
How can I read a pcap file with PcapPlusPlus?
The getting started sample includes IPv4Layer.h, Packet.h and PcapFileDevice.h, constructs a pcpp::PcapFileReaderDevice on 1_packet.pcap, and tests the result of open(), reporting a failure through the standard error stream. Each class comes from its own header in that example, with no umbrella include.
Which file format is better, PCAP or PCAPNG?
The readme takes no position. It says the library reads and writes packets from and to files in both formats and says nothing about when to prefer one, so the choice is left to the application using it.
Which packet capture engines does PcapPlusPlus wrap?
libpcap, WinPcap, Npcap, Intel DPDK, eBPF AF_XDP, WinDivert, ntop's PF_RING, and raw sockets, with in-line-rate processing through DPDK, AF_XDP and PF_RING. The project's short description names only the first six of those and leaves out WinDivert and raw sockets.
Which platforms does PcapPlusPlus support?
Linux, MacOS, Windows, Android and FreeBSD, stated as fully supported in the feature overview. Build instructions are not in the readme: it gives a clone command and then points to the Build From Source page on the project website for per-platform steps.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/seladb-pcapplusplus)Star history chart for your README
[](https://hysenlabs.com/projects/seladb-pcapplusplus)Was this useful?