xbackbone's homepage is plain HTTP and its release line has a 17-month gap
A lightweight file manager with full ShareX support and more
At a glance
- What is it?
- XBackBone is a self-hosted file and media sharing platform with ShareX integration, split into a published core package and a skeleton app so that an upgrade is a version bump. Its homepage is listed over plain HTTP, its release line has a seventeen-month gap, and it lets an admin upgrade the instance from a browser.
- Who is it for?
- XBackBone fits a self-hoster who wants ShareX-compatible uploads, per-user quotas and an admin surface without handing shell access to anybody, and the two-package split is a genuinely good reason to try it, because a downgrade is a version number. It is a poor fit if you cannot accept an application that upgrades itself over the network, or if you need FTP or plain HTTP anywhere in the path.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 27 days ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
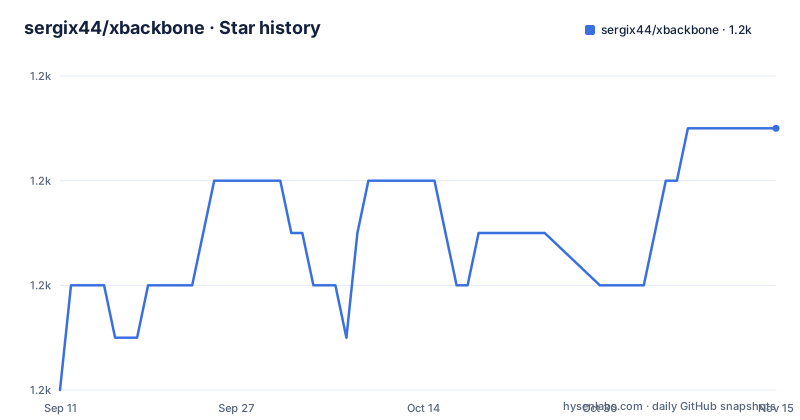
- sergix44/xbackbone1,171 ★ · +5
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| sergix44/xbackbone | 1.2k | 1.2k |
5 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The homepage the README publishes is plain HTTP
The project links its own site at a URL with no transport security on it. The scheme in the address is `http`, not `https`.
For most projects that would be a cosmetic slip. Here it is not, because the product is a file and media upload service with per-user tokens, per-resource passwords and expiration, and because one of the advertised features generates uploader configurations pre-filled with the instance URL and a personal token.
So a user who copies an uploader config out of this application and pastes it into a desktop screenshot tool is embedding an address that will carry a token over an unencrypted connection.
The other outbound links are not affected. The documentation is served from a GitHub Pages address over HTTPS, the ShareX project it integrates with is linked normally, and the licence and conduct files are relative paths inside the repository.
The point is narrow and worth stating precisely: the site the project advertises for itself does not use HTTPS, and a self-hoster who copies that URL into their client configuration inherits that.
Two releases eight days apart, then seventeen months
The three most recent releases are 3.8.2 dated 2026-06-27, 3.8.1 dated 2025-01-26 and 3.8.0 dated 2025-01-18.
So the two earlier releases landed eight days apart in the middle of January 2025, and the next one came seventeen months later. The last push to the default branch is dated 2026-09-18, roughly eleven weeks after the 3.8.2 tag, with no release following it.
That shape is consistent with a project that spent 2025 finishing a rewrite and shipped the result once. The README describes itself as the next generation of the product, rebuilt from the ground up on Laravel 13 and Livewire 4, and it includes a legacy import path for migrating users and uploads from an older instance with old links transparently redirected.
Two generations therefore share one release line and one version number space, which is why a patch release from January 2025 and one from June 2026 both sit at 3.8.x without anything in the numbering to distinguish the stacks underneath.
There is a `CHANGELOG.md` at the repository root. Whether it marks the boundary between the two architectures is the first thing to check.
The application is a package and the install is a skeleton
The repository is a monorepo with two directories, and the split is the most transferable idea in the project.
`core/` is the entire application, a Laravel and Livewire app holding all the logic, and it is published to Composer as `xbackbone/core`. `app/` is a minimal installation skeleton holding configuration, the bootstrap files and a public entrypoint, and its only job is to pull the core package in as a dependency.
The skeleton boots the core package and remaps its public, storage and environment paths to the skeleton root. That remapping is what makes the arrangement work: the core package assumes it owns the filesystem layout, and the skeleton corrects for that.
The stated payoff is version control of the application logic. Because the logic lives in a versioned package rather than in the deployment, an instance can be upgraded or downgraded by changing the required version of `xbackbone/core` and touching nothing else. For a self-hosted application that people are reluctant to touch, that is a real answer to the usual upgrade problem.
The trade is that the repository README is not an install guide. It says full installation, configuration and usage instructions live in the documentation, and points readers to a separate technical details document inside `core/`.
Upgrading from the browser means the instance fetches its own upgrades
One feature deserves its own reading: admins can check for new releases and upgrade the instance from the browser, with no shell access required.
Set that beside the guided web installer, which sets up the database, storage and the admin account from the browser, and the picture is a deliberate posture. This is an application designed to be installed and maintained by someone who never opens a terminal on the server.
The security surface follows from that. An upgrade triggered in the browser is a path by which new code enters a running instance, so the instance needs outbound network access to wherever that updater fetches from, and whoever holds the admin account can trigger it. The README describes the capability without describing the source of the artefact, the signature check, or whether a downgrade path is offered.
That silence is worth resolving before you rely on it, particularly given the release cadence. A seventeen-month gap between tags means an instance can sit on a version for a long time before there is anything to upgrade to, and there is a `CHANGELOG.md` in the repository that is the more predictable place to look.
Content addressing and per-resource visibility are not reconciled
Two of the storage features pull in opposite directions, and the documentation does not meet them.
One is content-addressed storage, described as uploads being de-duplicated by content fingerprint. The other is per-resource visibility, with an optional password and an expiration on each resource.
If two users upload identical bytes, content addressing means one stored object. What then happens when one of them sets a password, or makes the resource private, or expires it? The reference implementation has to pick: either the stored object carries the metadata, which makes it shared, or it does not, which means de-duplication was only ever at the storage layer and the visibility layer holds a second copy or a reference to the first.
The README does not say which, and it does not say whether the fingerprint is computed before or after any per-user transformation.
This matters for a hosted instance with per-user disk quotas, because a quota is a statement about bytes a user has caused to be stored, and a shared object with two owners makes that number ambiguous in one direction or the other.
It is a documentation gap rather than a demonstrated fault, and it is the kind of question to put to the project before you turn on quotas.
Generated uploader configs carry a personal token
The integration list is longer than ShareX, which is the first thing to notice. Ready-to-use uploader configurations are generated for ShareX, ScreenCloud, ishare, Spectacle on KDE, the macOS share sheet, Xerahs, and a command-line script.
The mechanism is described in one line: all of them come pre-filled with your instance URL and a personal token. That is what makes them one-click, and it is also what makes them a credential-handling decision rather than a convenience.
A generated configuration therefore contains a secret. Sharing a screenshot of a configured ShareX panel, pasting it into a forum post, or committing it to a dotfiles repository publishes a token that authenticates uploads as that user. The platform offers two-factor authentication with TOTP and passkeys for interactive logins, but a token embedded in a config file is not covered by either.
The activity log is the compensating control, and it is a good one: a searchable, filterable timeline of account and admin activity, showing your own actions and, for admins, the whole instance. So a leaked token is at least visible after the fact.
Per-user disk quotas and a feature flag that can disable sign-ups are in the same list, which tells you the intended deployment is a shared instance rather than a personal one.
The repository has no container file and no install commands
The repository root is short: a GitHub directory, a gitignore, a changelog, a code of conduct, a licence, the readme, a security file, and the `app/`, `core/` and `docs/` directories.
There is no container file and no compose file in that listing, and there is not one command in the readme. Installation is deferred entirely: the getting started section says full installation, configuration and usage instructions are available in the documentation, and links a documentation site hosted separately from the project site.
That is a coherent choice for a project whose installer is a web form, but it has a discoverability cost. Among the phrases people type for this project are several about running it in a container, about a hosted demo, and about an alternative to it. None of those can be answered from this repository.
Two smaller things sit alongside it. The security disclosure address in the readme is on a domain unrelated to the project name or the owner handle, and the readme asks that vulnerabilities be emailed there rather than filed on the public tracker, pointing to `SECURITY.md` for detail. The documentation is served from a GitHub Pages address while the project site is a separate domain, so there are three places this project lives and one place its readme points.
Editorial conclusion
XBackBone fits a self-hoster who wants ShareX-compatible uploads, per-user quotas and an admin surface without handing shell access to anybody, and the two-package split is a genuinely good reason to try it, because a downgrade is a version number. It is a poor fit if you cannot accept an application that upgrades itself over the network, or if you need FTP or plain HTTP anywhere in the path. Before you deploy it, settle three things. Put it behind TLS yourself, since the homepage the project publishes is plain HTTP. Read what the in-app updater fetches and from where, because an admin-triggered upgrade is a remote code path in your instance. And check the storage backend you intend to use, since FTP is on the list and is not encrypted. The last push was on 2026-09-18 and the newest release is 3.8.2 from 2026-06-27.
Frequently asked questions
What is XBackBone?
A self-hosted file and media sharing platform with first-class ShareX support, built as a Laravel 13 and Livewire 4 application. It handles images, GIFs, video, audio, PDFs, code and arbitrary files, and shares them through short links with social embeds, with per-user quotas and a versioned REST API.
How is the XBackBone repository laid out?
As two directories. `core/` holds the full application and is published as the `xbackbone/core` Composer package, and `app/` is a minimal skeleton with configuration, bootstrap and a public entrypoint that pulls core in as a dependency and remaps its public, storage and environment paths. Upgrading or downgrading is a matter of changing the required version of the core package.
Which storage backends does XBackBone support?
Local disk, Amazon S3 and S3-compatible services, FTP, and SFTP. Uploads are content-addressed and de-duplicated by content fingerprint, and each resource can be private or public, optionally password protected, and given an expiration.
How do I report a security problem in XBackBone?
By email to the address given in the README rather than through the public issue tracker, with further detail in `SECURITY.md`. The address is on a domain unrelated to the project name or the owner handle, so check it before sending anything sensitive.
Does XBackBone come with a container setup?
The repository root as listed contains no container file and no compose file, and the README gives no commands, deferring everything to hosted documentation. What it does provide is a guided web installer that sets up the database, storage and an admin account from the browser.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sergix44-xbackbone)Star history chart for your README
[](https://hysenlabs.com/projects/sergix44-xbackbone)Was this useful?