x64dbg-mcp exposes 79 debugger functions over HTTP and ships three write guards
MCP server plugin for x64dbg debugger - enables AI agents and external tools to control debugging via JSON-RPC 2.0 over HTTP/SSE
At a glance
- What is it?
- SetsunaYukiOvO/x64dbg-mcp is a native C++ plugin that puts an MCP server inside the x64dbg and x32dbg debuggers, letting an agent drive a live debugging session over JSON-RPC. It is built for authorised analysis of software you are allowed to inspect, and its safety story is a set of default-deny permission flags and allowlists rather than anything subtler.
- Who is it for?
- Use it if you own the binary or have written authorisation to analyse it, and you want an agent to drive a live debugging session rather than read a static disassembly.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 18 days ago.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
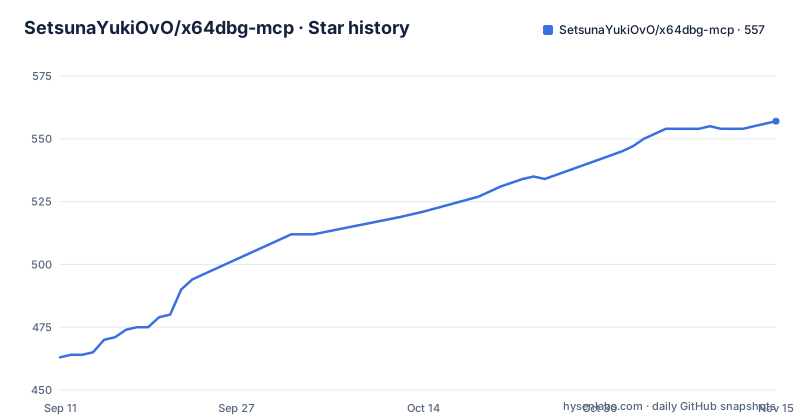
- SetsunaYukiOvO/x64dbg-mcp557 ★ · +94
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| SetsunaYukiOvO/x64dbg-mcp | 463 | 557 |
94 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One plugin exposes a live debugging session as 79 callable functions
The plugin sits inside x64dbg and its 32-bit sibling and turns the debugger into a server. An external program or an AI agent connects and drives the session programmatically instead of clicking through a user interface. The surface is large and organised by what a debugger actually does: execution control, so init, run, pause, single-step, run-to, restart and stop; memory reads, writes, search and allocation; register access across more than fifty registers including the general, SSE and AVX sets; breakpoint management in software, hardware, memory, conditional and logging flavours; disassembly and symbol resolution; thread listing, switching, suspension and resumption; stack trace and analysis; and context snapshots for capturing and comparing debugging state.
Two groups are called out in bold in the documentation because they reach further than the rest. A dump and analysis group handles module dumps, memory dumps, packer detection and original-entry-point detection. A script execution group runs commands inside the debugger and supports batch operations. Those two groups are the reason the permission model matters, and they are the reason this belongs to authorised analysis of your own or a client-owned binary rather than to anything else.
A normal debugging session is a loop of reading state, setting a breakpoint, stepping, and reading state again. What the plugin adds is that an automated client can drive that loop without a human at the keyboard, which is useful for triage and for reproducible investigation, and is exactly why the write operations are gated.
The permission block denies writes by default and lists the methods a client may call
The shipped configuration file is the clearest statement of the security posture, and it is a deny-by-default one. Three of the four capability flags are false in the example: memory writes are off, register writes are off, and script execution is off. Only breakpoint modification is on. Alongside those sits an allowlist of permitted method groups, and in the example it contains exactly two patterns covering the debugging and memory namespaces.
That combination is the part to understand. The boolean flags are coarse, tool-wide switches; the method allowlist is the fine-grained control, and it is what a caller cannot exceed even when a broad flag would allow the operation. So a deployment that wants an agent to read state and set breakpoints, but never write a byte of process memory or execute a debugger script, has a configuration that says so directly.
The security block beside it holds an origin allowlist, a host allowlist, an authentication toggle and a token field, all empty or off in the example. The two allowlists exist because a browser-based client can be pointed at a local server, and the origin and host entries are how you say which ones are welcome. Authentication being off by default is reasonable for a loopback-only debugging aid, and it is the setting to change first if the listener is ever anything other than loopback, which is what the in-application editor's confirmation prompt exists to catch.
The configuration editor treats unknown fields as data to preserve
Recent work added an in-application editor so the configuration does not have to be hand-edited as JSON. It is reached from the plugin menu alongside the server start command, and it presents pages for the server, security, permissions, runtime and logging groups.
The detail worth knowing is how it treats the file. The editor is described as covering every runtime setting in the shipped example, and as preserving the version field and any fields it does not recognise when it saves. That is a small design decision with real consequences: a configuration written by a newer build, or hand-extended by a user with their own keys, survives a round trip through the graphical editor instead of being flattened to the keys the editor knows about. For a tool whose config already has a version stamp, that is the right call.
The editor also handles the two security settings that are easy to get wrong by hand. Allowlists are entered one entry per line rather than as a JSON array, which is a better fit for the values they hold. The token field is masked, and it is required when bearer authentication is enabled, so you cannot save an authentication-required configuration with an empty token. Saving a non-loopback listener without authentication raises a confirmation, and the server has to be restarted for the server settings to take effect, which is stated rather than left to be discovered.
Three protocol generations are supported on two endpoints
The transport story is broader than a single endpoint, which matters because protocol clients have moved quickly. The primary transport is streamable HTTP, matching the March 2025 revision of the protocol, served on a path named for the protocol itself. Alongside it, a legacy mode combining HTTP with server-sent events is kept on a second path for older clients. The plugin also implements the full set of protocol building blocks: tools, resources and prompts, which it claims as complete rather than partial compliance.
The counts are specific enough to be checked against a running instance. There are seventy-nine tools, seven direct resources with eight more exposed as templates, and ten prompts. The resources are read-only and application-controlled, covering debugger state, registers, modules, threads, the memory map, breakpoints and the stack, with templates that can return memory content, disassembly, module information, symbol resolution and function analysis on request.
Carrying a legacy transport alongside a current one is normal for a protocol server that people deploy into environments they do not control. The cost is a second endpoint to reason about when you are writing an allowlist, and a second code path in the plugin. The benefit is that an older client is not locked out of a debugger session, which for a tool whose whole purpose is being driven by something else is worth a good deal.
It is built for both architectures, and you compile it twice
x64dbg ships as two debuggers, one for 64-bit targets and one for 32-bit, and this plugin builds for both. The build script takes architecture flags rather than making you run the toolchain by hand: a plain invocation builds both, a flag builds only 64-bit, another builds only 32-bit, a clean flag does a full rebuild, and a debug flag is present but marked as future support.
Under the script, the manual sequence is the one any CMake and Visual Studio project would use, starting from a clone and a build:
git clone https://github.com/SetsunaYukiOvO/x64dbg-mcp.git
cd x64dbg-mcp
A C++ package manager is bootstrapped into a fixed directory and its root recorded in an environment variable, then CMake is configured once per architecture with a generator and platform argument, the package manager's toolchain file, a target triplet that differs between the two builds, and a project-specific architecture flag that the build script reads. Compilation follows, then the two plugins land in a distribution directory with their architecture-specific extensions. Output sizes are given as roughly eight hundred kilobytes for each.
The prerequisites are a 64-bit Windows host, a recent CMake, a specific Visual Studio edition with the desktop C++ workload, the package manager, and Git. The manual path downloads one JSON library through the package manager. Nothing here depends on the model or on a hosted service; once built, the plugin is a local binary that loads into a local debugger.
The ten prompts are workflow templates, and several are for unpacking and patching
Prompts are the user-guided half of the protocol surface, and this plugin ships ten of them as workflow templates. They are grouped by the kind of investigation they scaffold: crash analysis, vulnerability hunting and function tracing on one side; binary unpacking, algorithm reversing and execution comparison on the other; string hunting, code patching and API monitoring as a third group; and session initialisation as the way you begin.
It is worth being plain about what several of these are for. Binary unpacking and original-entry-point detection are the tasks you perform on a packed executable to recover the code it hides. Code patching is modifying instructions in the running process. Vulnerability hunting and string hunting are the two prompts most directly associated with looking for weaknesses in a binary. These are ordinary capabilities of any debugger and plugin that exposes its command surface, and they are the reason the permission defaults and the method allowlist exist.
The framing that matters is authorisation. A debugger is a tool for understanding software, and the legitimate uses are vast: your own code, software you have licensed, malware analysis in a role where you are paid to analyse it, and compatibility work on binaries you are permitted to inspect. The same capabilities applied to software you have no right to examine are a different activity, and no prompt template changes that. If you are reaching for this plugin, the permission boundary is the question to answer first, and the default-deny configuration is there to keep a mistake small.
The examples are Python, so the plugin is driven from outside the debugger
The repository ships two examples and both are Python. One demonstrates dumping and analysis, and the other is a general HTTP client for talking to the server, which together tell you how the plugin is meant to be consumed: not through the debugger's own interface but from an external process that speaks the protocol over the network.
That framing is the point of the whole project. The agent, or the script, sits outside; the debugger sits inside, loaded with the target; the connection between them is a JSON-RPC conversation over HTTP. So the operational model is a local server on a port, a client that connects to it, and a set of permission flags deciding how much the client is allowed to do once connected.
Two practical notes follow from the configuration. The server listens on the loopback address by default on a port in the three thousand range, and it is started from the debugger's plugin menu rather than as a standalone process, so it comes up and goes down with the debugging session. Anything that binds beyond loopback is a deliberate choice with a confirmation attached, and a bearer token exists for the case where you make it. The rest of the repository is ordinary native-project furniture: a CMake file, a package manifest for the C++ dependencies, a header and source tree, a tests directory, a scripts directory with a PowerShell build alongside the batch file, documentation including a Chinese translation of this page, and an agent instruction file.
Editorial conclusion
Use it if you own the binary or have written authorisation to analyse it, and you want an agent to drive a live debugging session rather than read a static disassembly. The tool surface is broad, 79 functions including script execution and memory writes, so the guardrails are the thing to understand before you connect anything: writes to memory, registers and scripts are off by default, authentication is off by default, and the method allowlist is what actually limits a connected client. Before you start a server on anything but loopback, read the security block and turn bearer authentication on, because a non-loopback listener is what turns a local debugging aid into a remote control surface for the machine under test. And decide for yourself whether your use is authorised; this article describes the tool's mechanics, not a workflow for anyone whose engagement does not cover it.
Frequently asked questions
What does the x64dbg-mcp plugin do?
It loads into the x64dbg and x32dbg debuggers and exposes the debugging session over a JSON-RPC interface so an external program or AI agent can drive it. It provides 79 tools covering execution control, memory and register access, breakpoints, disassembly, threads, dumps, script execution and context snapshots, plus 7 resources and 10 workflow prompts.
Is x64dbg-mcp safe to connect an agent to?
It ships with memory writes, register writes and script execution all disabled by default, only breakpoint modification enabled, and a method allowlist restricting which tool groups a client may call, and its examples are external clients rather than an in-debugger automation surface. The authorisation question is separate from the tool: it is for software you own or are authorised to analyse.
Do I need to build x64dbg-mcp from source?
Yes, the documentation builds it from source with a provided script. You need a 64-bit Windows host, CMake, Visual Studio 2022 with the C++ desktop workload, vcpkg and Git, and you compile once for 64-bit and once for 32-bit, producing two plugin files you copy into the two debugger directories.
What network security does x64dbg-mcp provide?
The shipped configuration has bearer authentication off, an empty origin allowlist and an empty host allowlist, and binds to loopback. A configuration editor in the plugin menu masks the token field, requires a token when authentication is enabled, and asks for confirmation when you save a non-loopback listener without authentication.
Which MCP transports does x64dbg-mcp speak?
Both a current and a legacy transport. The primary is streamable HTTP matching the March 2025 protocol revision, served on one path, with a legacy HTTP plus server-sent-events mode kept on a second path for older clients, and it implements tools, resources and prompts as the full set of protocol building blocks.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/setsunayukiovo-x64dbg-mcp)Star history chart for your README
[](https://hysenlabs.com/projects/setsunayukiovo-x64dbg-mcp)Was this useful?