fscan internals: computed port scopes, flush-as-you-go output, and one distro in the install docs
An intranet comprehensive scanning tool enabling one-click automated, all-round vulnerability scanning.
At a glance
- What is it?
- fscan is a Go intranet scanner that folds host discovery, port scanning, service identification, weak password testing, and exploit plugins into a single binary that can also be embedded as an SDK. The build and output plumbing are unusually careful, while the install documentation covers exactly one Linux distribution and the bundled lab is unfinished.
- Who is it for?
- Reach for fscan when you hold written authorization for an internal network and want discovery, identification, and weak password testing in one binary you can also embed. Hold off if you need a supported install path outside Arch Linux, a finished training lab, or confidence that proxy mode port states from an older build match today's.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 44 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
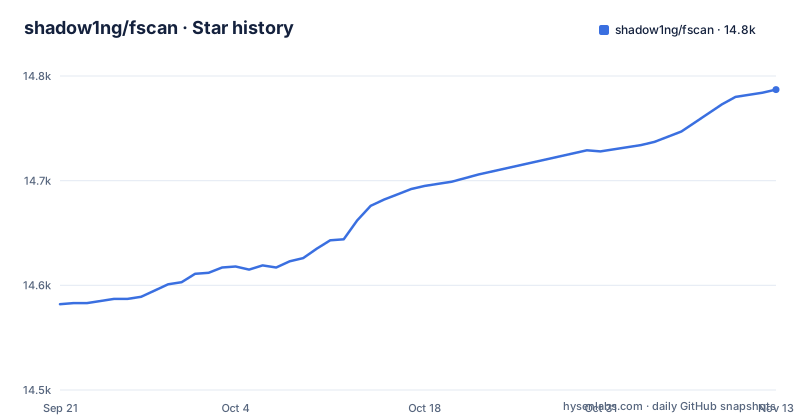
- shadow1ng/fscan14,787 ★ · +205
| Repository | 2026-09-21 | 2026-11-13 |
|---|---|---|
| shadow1ng/fscan | 14.6k | 14.8k |
205 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Host discovery runs on ICMP, and a token bucket throttles the sweep
Fscan starts with host discovery, and the mechanism is ICMP and ping liveness probing rather than a TCP sweep, paired with survival statistics for large B and C network segments. Two details matter more than the headline. An ICMP token bucket was added, with the stated reason being that fast scanning can crash the router sitting in front of the network, so a wide range is throttled rather than sprayed. The port scan stage also gained an automatic retry for failed attempts, and an ICMP race condition was fixed alongside it. Discovery runs on its own when you only want reachability, using the alive-only flag in the quick start, or as the first stage of a full run:
# 仅存活探测
./fscan -h 192.168.1.1/24 -ao
A whole address space with a single module named is `fscan.exe -h 192.0.0.0/8 -m icmp`.
Port scope is the union of the modules you name, not a fixed list
Port scope is computed rather than fixed, and this is the detail that catches people out. Name fixed-port modules with -m and pass neither -p nor -pf, and the range becomes the union of the default ports of the modules you selected, so reading targets from a file with `fscan -hf ip.txt -m netbios` sweeps `137,139` and nothing else. Pass -p to scan a non-standard port instead, with one exception: Web modules keep using the generic port range. Named port groups exist as well, web/db/service/all, over a built-in list that grew from 62 entries to 133 common ports, and full port range scanning was added in the same release. The consequence for anyone scripting this is that the same target reached with and without -m covers a different set of ports, and the narrower case silently inherits whatever ports those modules bind by default.
Fingerprints come in two layers, and redirects get matched twice
Identification is two fingerprint systems counted separately. Service identification matches 20+ service fingerprints, while web probing inspects page titles, CMS fingerprints, web middleware, and WAF or CDN products across 40+ fingerprints. The library behind them grew in the same release: FingerprintHub is integrated with 3139 fingerprints, favicon matching accepts both mmh3 and MD5 hashes, protocol detection decides HTTP versus HTTPS on its own, and a generic version extractor pulls service version strings. Two changes deal with awkward HTTP rather than adding breadth. Redirects are recognised twice, matching both the original response and the response after the jump, and results are sorted by fingerprint priority so the strongest match wins. That surface has its own failure history: the same release fixes dropped webtitle response data and a race between webtitle and webpoc, so a misidentified service is a known failure mode rather than a surprise.
Build tags fix the plugin set, and -list-plugins reports it
Plugin scope is settled at compile time, and the binary will tell you what it holds. `fscan -list-plugins` prints the module names, types, default ports, and invocation forms available in the current build, which is the only reliable answer to whether a service exists in the copy you are holding. The architecture keeps service plugins, web plugins, and local plugins separate, and a build tag system compiles each group independently, so a lean binary carries fewer modules and less surface. Embedding is the other route: pkg/fscan exposes a Go SDK for placing a scanner inside an agent or a security platform, with task control including Pause and Resume, real-time progress callbacks, and TaskID traceability, and the examples directory ships embed-basic, embed-stream, and embed-agent samples. A visual task manager sits behind the web build tag, and the interface switches language with -lang zh/en.
The password dictionary appends, and NTLM hashes are a separate path
Weak password work covers 28 services including SSH, RDP, SMB, FTP, MySQL, MSSQL, Oracle, and Redis. The dictionary is built in at 100+ common weak passwords and supports a {user} variable so one entry expands per account name. Dictionary flags come in two flavours with documented precedence: -pwda and -usera append to the default dictionary, and when combined with -pwd and -user, or with -pwdf and -userf, they append to the specified dictionary instead, which is how `fscan.exe -h 192.168.x.x -m ssh -user root -pwda pass1 pass2 pass3` adds three entries rather than replacing the list. Authentication is not limited to passwords. NTLM hash authentication covers SMB and WMI, as in `fscan -h 192.168.1.1 -m smb2 -user admin -hash xxxxx`, SSH private key login is supported, RDP goes through the grdp library for real system fingerprinting, and MySQL validation was moved to the information_schema database.
Output is flushed during the run, and Ctrl+C still writes results
Results are written while the scan runs, and the change log gives the reason: the output system was rebuilt with real-time flushing to disk plus a dual write mechanism to fix lost results and out-of-order records. Formats are TXT, JSON, and CSV, and a TXT run ends with a summary list of discovered web service URLs for batch testing. That rebuild also removed false vulnerability records from TXT output, unified the Target format for SERVICE results so JSON no longer loses fingerprints, and restored vulnerability details missing from TXT. Interrupting is handled on purpose: signal handling was added so Ctrl+C still writes results, and a separate fix stopped the elapsed time from displaying 0. A JSON performance report comes from -perf, silent mode drops the banner, progress bar, and colour, and the Makefile test target runs with the race detector while disabling vet, because the i18n call pattern clashes with the printf check.
Proxy mode is the part that produced the wrong answers
Every stage carries its own control, which is both the strength and the confusing part. Rate limiting and a maximum packet count sit next to separate timeouts for port, web, and global work, plus separate thread counts for port scanning and service scanning. Traversal can run through an HTTP or SOCKS5 proxy, the SOCKS5 dialer is reused globally to avoid repeated handshakes, and -iface selects a network interface for VPN scenarios. The release notes show where this subsystem has been wrong. Proxy mode could misjudge port state, SOCKS5 answered with a full echo and needed a connection verification step, service probing leaked connections that were never closed, and 22 places in the plugins were found to ignore context timeouts, the same class of bug that made POC scanning hang under high concurrency. The consequence for a reader comparing runs is that port state recorded through a proxy on an older build should be rechecked rather than trusted against a newer run.
One distro in the install section, and a lab marked unfinished
Installation covers exactly one distribution, and that is the whole of the install section:
# Arch Linux
yay -S fscan-git
Everything else is a source build, which means a Go toolchain, since the module declares go 1.25.0, and the build is one line:
# 标准编译
go build -ldflags="-s -w" -trimpath -o fscan .
The Web UI variant adds a build tag, and the Makefile notes that target builds the frontend first and needs Node.js and npm, starting on port 10240 by default. Two parts of the project are openly unfinished: the fscan-lab Docker range is labelled as not completed, and fscan-lite, a planned C rewrite for smaller size and fewer dependencies, sits on the roadmap rather than shipped. Releases are stated to be monthly, and the tags follow that with v2.2.0 on 2026-07-10, v2.2.1 on 2026-08-25, and v2.2.2 on 2026-10-01, though the detailed changelog stops at v2.1.0. An English version of the documentation lives in a separate README_EN.md file.
Editorial conclusion
Reach for fscan when you hold written authorization for an internal network and want discovery, identification, and weak password testing in one binary you can also embed. Hold off if you need a supported install path outside Arch Linux, a finished training lab, or confidence that proxy mode port states from an older build match today's. Before a run, check `fscan -list-plugins` for what your binary actually contains, pin the port range yourself because module defaults narrow it, and record the version you scanned with.
Frequently asked questions
What is an Fscan?
It is an intranet scanning tool for one-click automated vulnerability sweeps, written in Go. It does ICMP and ping host discovery, TCP full connect port scanning over 133 built-in ports, service identification, and web probing for titles, CMS fingerprints, middleware, and WAF or CDN products.
what is fscan exe
That is the Windows form of the binary used throughout the example invocations. The project also fixed cross-platform path and timeout problems in its Redis module, and a Windows compile warning was cleared.
fscan vs nmap
Rather than staying separate, fscan embeds nmap core for three things: probe strategy, the match engine, and version parsing. Service probing was also rebuilt around an Nmap style fallback mechanism.
fscan alternative
The project credits a set of related tools in its reference section: ServerScan, x-crack, Gscan, LadonGo, gopoc, gogo, FingerprintHub, and fscanx. FingerprintHub is also integrated directly, contributing 3139 fingerprints to the identification layer.
fscan vs fscanf
They are unrelated. fscanf is a C standard library input function, while this project is a Go program whose module path is github.com/shadow1ng/fscan and whose primary language is Go.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/shadow1ng-fscan)Star history chart for your README
[](https://hysenlabs.com/projects/shadow1ng-fscan)Was this useful?