Talos Linux: an API-only Kubernetes OS where go.mod carries patched forks
Talos Linux is a modern Linux distribution built for Kubernetes.
At a glance
- What is it?
- Talos replaces the shell with an authenticated API, so an operator cannot log in to fix a node by hand. The build is defined by a Makefile that derives its version from git describe, a Dockerfile that lists every bundled package as an ARG, and a go.mod that swaps several upstream dependencies for patched forks.
- Who is it for?
- Talos fits teams running Kubernetes at a scale where node configuration drift is already a real incident source and where every node is provisioned, not hand-maintained. It does not fit a cluster where engineers expect to ssh into a node, read a log file and fix something in place, because there is no shell and no interactive console to do that in.
- Can I use it commercially?
- Yes, with conditions. MPL-2.0 is a weak copyleft licence: you can use it inside commercial and closed-source software, but if you distribute changes to its own files, you must publish those changes under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
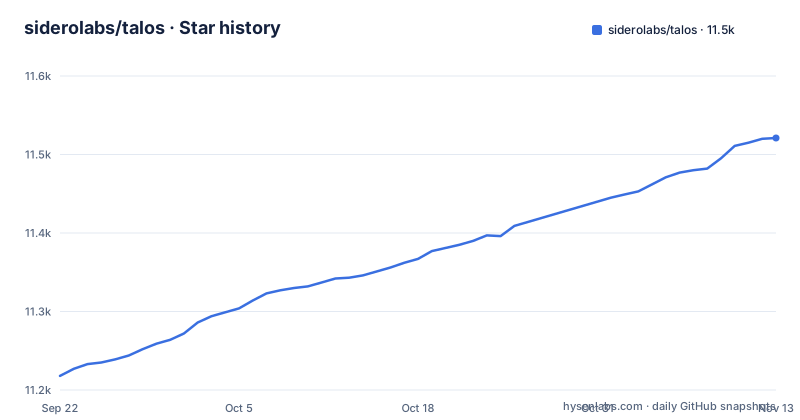
- siderolabs/talos11,521 ★ · +303
| Repository | 2026-09-22 | 2026-11-13 |
|---|---|---|
| siderolabs/talos | 11.2k | 11.5k |
303 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
There is no shell, so every diagnostic has to leave through the API
The defining constraint is stated in one line: all system management is done via an API, and there is no shell or interactive console. That sentence removes the reflex every Linux operator has, which is to ssh in and look.
The cost lands hardest during an incident. A pod will not schedule on a node, and the reflex is to read the kubelet log on that node. Under Talos there is no shell to read it from, so the same information has to come out through the API that manages the node. The security argument is the mirror image of that cost: a smaller attack surface, and an OS that is minimal, hardened and immutable. Every API call is authenticated with mutual TLS, so there is no password to guess and no session to steal.
The predictability argument follows from the same design. Configuration drift is eliminated, immutable infrastructure is the stated ideology, and updates are atomic, which means a node is either at the old version or the new one and not somewhere in between. What a team gives up in exchange is ad hoc improvisation on a running node.
go.mod downgrades gRPC and swaps four upstream dependencies for maintained forks
The dependency file is where this project stops being a repackaged Linux. Talos declares module github.com/siderolabs/talos on go 1.27.0, and it does not simply take upstream libraries as they are. Several of them are replaced with forks, each with a comment explaining why.
CorDNS is replaced with a Sidero Labs fork at v1.15.0-sidero.1 so the distribution does not carry Caddy and other dependencies it has no use for. ethtool is replaced with a fork that adds missing APIs. smart.go is replaced with a fork that sets O_CLOEXEC on device open and adds SataDevice.CheckPowerMode to skip standby disks, which is a hardware behaviour change rather than a build fix. wireguard's wgctrl is replaced with a fork that adds a Talos-specific userspace socket location, tracked back to issue 8514.
Two more replacements are forks too. kobject points at a fork by smira, referencing an upstream pull request, and siv-go points at a fork that disables the assembly implementation, referencing an upstream issue about it.
For an adopter this is the real maintenance bill. Six upstream projects now need tracking by someone, and two of the forks exist for reasons that are about Talos hardware and layout rather than about the libraries themselves.
pkg/machinery is a separate module, so the client and the node build on different terms
The module graph contains a nested module: github.com/siderolabs/talos/pkg/machinery points at ./pkg/machinery rather than at a version on the network. Everything else in the repository is one module.
A nested module is a versioning decision. Code under pkg/machinery, which is the part a management client needs to talk to a node, can be released and pinned independently of the operating system image, so a tool that only needs to speak the Talos API does not have to track the cadence of a full OS build.
The rest of the layout follows a conventional Go split. api/, cmd/, internal/ and pkg/ carry the code, hack/ and tools/ hold build and release tooling, and website/ holds documentation sources. Top-level policy files are unusually thorough for a kernel distribution: .disvulncheck.yaml and security-insights.yml for vulnerability scanning, .sops.yaml and .secrets.yaml for encrypted secrets, .conform.yaml for commit message enforcement, .golangci.yml for linting, and lefthook.yml for git hooks. ADOPTERS.md and RELEASE.md sit alongside them as written process, not just configuration.
The Dockerfile keeps its entire package inventory in ARG lines
The image build is not a shell script. It declares its contents as build arguments, and the list is the inventory of what Talos ships. From kernel, musl and sd-boot through containerd, runc, cni and flannel-cni, then the storage and filesystem tools: btrfsprogs, e2fsprogs, xfsprogs, dosfstools, libarchive, squashfs-tools, lvm2, mdadm, libburn, libisoburn and libisofs. Cryptography comes from openssl, cryptsetup, libcap and the SELinux libraries libselinux and libsepol.
Networking sits alongside: iptables, nftables, libnftnl, libmnl, and libpopt. Boot paths cover grub, ipxe, qemu-tools, open-vmdk and pigz, with libaio, libattr, pcre2, zlib, zstd, xz, igzip, lzma, glib, json-c, jansson, util-linux, tar, cpio, mtools and system-udevd closing the list.
Every one of these defaults to scratch in the Dockerfile; the Makefile supplies the real image references for each PKG_ variable.
The Makefile derives its own version from git describe, so a dirty tree changes the tag
There is no version constant to edit. The build derives identity from the repository's git history, and the defaults show exactly how:
REGISTRY ?= ghcr.io
FACTORY ?= factory.talos.dev
USERNAME ?= siderolabs
SHA ?= $(shell git describe --match=none --always --abbrev=8 --dirty)
ZSTD_COMPRESSION_LEVEL ?= 18
TAG and ABBREV_TAG are computed the same way from git describe with a version pattern, and the dirty flag means a tree with uncommitted changes labels its own image. SOURCE_DATE_EPOCH comes from the last commit timestamp, so two builds of the same commit produce the same value. Output lands in a directory named _out.
The interesting part is that the inputs are also pinned, and pinned to a 1.15 pre-release. The tools image defaults to v1.15.0-alpha.0-15-g2d70a26 and the packages image to v1.15.0-alpha.0-69-g5c111c8, both under ghcr.io/siderolabs. The build system therefore depends on a 1.15 alpha of the toolchain even though the stable releases listed are on 1.13 and 1.14. Support images come from ghcr.io/siderolabs/kres and ghcr.io/siderolabs/conform, and the image signer is pinned to release v0.3.2.
MPL-2.0 covers the repository, and the bundled GPL software has no source in the tree
The repository is MPL-2.0, which is a reasonable licence for an operating system image: modifications to MPL-covered files stay open, while a proprietary distribution can combine the result.
The licence section then draws a line that matters for anyone shipping Talos images to customers. Some of the software Talos distributes sits in the GNU General Public License family or under other licences that oblige the distributor to provide source. The project says as much and gives a route: request a copy of that source by email to the address published in the README.
So an image built from this Makefile is not a single-licence artifact. An organisation with a legal review step in its release process has to account for the GPL components separately, and the README gives them an email address rather than a document. Treat that as a compliance task to schedule during evaluation, not after the first production rollout.
Two release lines shipped patches three days apart, so the pin is a decision
The release list shows v1.15.0-alpha.2 on 2026-10-27, v1.14.5 on 2026-10-26 and v1.13.12 on 2026-10-21. The 1.13 line, which is a maintenance line rather than the newest feature line, received a patch five days before 1.14.5 shipped.
That is normal practice for a Kubernetes node OS, and it is also a decision an adopting team has to make rather than inherit. Pinning to the newest minor means taking 1.14.x patches and waiting for a planned 1.13 to 1.14 upgrade. Pinning to 1.13.x means staying on a line that still receives fixes without adopting the newer one on its schedule. Neither answer is wrong, but the choice belongs to whoever owns the cluster, and it has to be made before automation hard-codes a version string.
The repository is not archived and its last push was on 2026-11-02, so both lines are moving. Community support runs through GitHub Discussions, with a Slack channel that needs an invitation requested through a third-party invite service, office hours on the second Monday of each month at 16:30 UTC, and a monthly meeting open to anyone who shows up.
Editorial conclusion
Talos fits teams running Kubernetes at a scale where node configuration drift is already a real incident source and where every node is provisioned, not hand-maintained. It does not fit a cluster where engineers expect to ssh into a node, read a log file and fix something in place, because there is no shell and no interactive console to do that in. Before adopting it, read the deployment instructions at docs.siderolabs.com/talos for the platform you actually run, then check the release line you would pin: v1.13.12 and v1.14.5 shipped five days apart, so decide which line receives your patches before you build automation against a version.
Frequently asked questions
how to install talos linux
The README carries no installation procedure. It sends readers to the deployment documentation at docs.siderolabs.com/talos, and the repository itself is the source for building images, with a Dockerfile taking its package inventory from build arguments and a Makefile that derives tags from git describe.
how to access talos
There is no shell or interactive console on a Talos node. All system management goes through an API, and every API access is authenticated with mutual TLS.
how to install talos on bare metal
Nothing in the README covers bare metal installation specifically; it points to the deployment documentation at docs.siderolabs.com/talos. The repository root does hold the pieces a custom image needs, including a Dockerfile whose ARG list covers sd-boot, ipxe, grub, qemu-tools and open-vmdk.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/siderolabs-talos)Star history chart for your README
[](https://hysenlabs.com/projects/siderolabs-talos)Was this useful?