dufs: per-path auth rules that the global flags can veto, sha-512 hashes, and a FROM scratch container
A file server that supports static serving, uploading, searching, accessing control, webdav...
At a glance
- What is it?
- A single Rust binary that serves a directory over HTTP, WebDAV, and curl, with account based access control, resumable transfers, and search. The interesting parts are the places where the documented rules stop you: granted read-write is still capped by the global permission flags, hashed passwords must be sha-512, and digest auth does not survive them.
- Who is it for?
- Pick dufs when you need one static binary that serves a directory with optional uploads, WebDAV methods, and per-path accounts, and when you can live inside its rules: sha-512 for stored hashes, listing globs matched by name rather than by path, and permissions that no account rule can widen.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
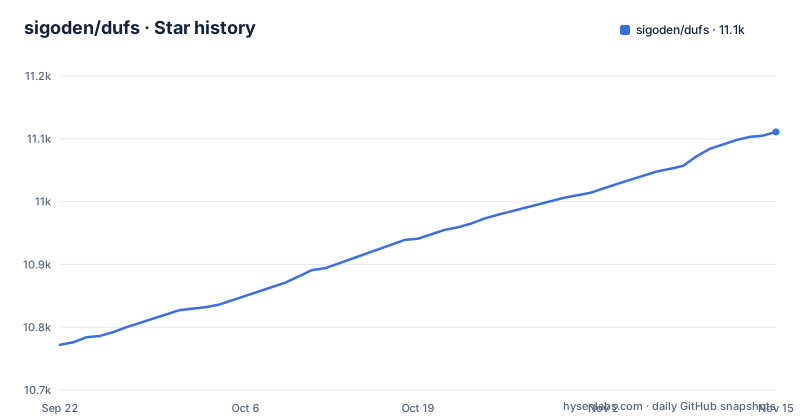
Star history
- sigoden/dufs11,111 ★ · +339
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| sigoden/dufs | 10.8k | 11.1k |
339 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
An account can be granted read-write and still not be able to upload
Access control is a per-path rule list, and the syntax packs four separators into one argument. In `-a admin:admin@/:rw -a guest:guest@/`, @ splits the account from the paths, : splits the username from the password, , separates multiple paths, and a :rw or :ro suffix sets the mode, with :ro being the default when the suffix is left off. The rule that catches people is the ceiling above all of it: auth permissions are restricted by the global permissions, so an account granted :rw gets no upload capability unless dufs itself was started with an upload flag such as --allow-upload. Consequence for an operator: a correct, generous rule set can still hand out read-only access, and the failure looks like a permissions bug in the rule rather than a missing flag. Verify both layers when you test an account, not just the role string.
Hashed passwords must start with $6$ and break digest authentication
Instead of a plaintext secret you can store a sha-512 hash, generated like this:
$ openssl passwd -6 123456 # or `mkpasswd -m sha-512 123456`
$6$tWMB51u6Kb2ui3wd$5gVHP92V9kZcMwQeKTjyTRgySsYJu471Jb1I6iHQ8iZ6s07GgCIO69KcPBRuwPE5tDq05xMAzye0NxVKuJdYs/
and passed like this:
dufs -a 'admin:$6$tWMB51u6Kb2ui3wd$5gVHP92V9kZcMwQeKTjyTRgySsYJu471Jb1I6iHQ8iZ6s07GgCIO69KcPBRuwPE5tDq05xMAzye0NxVKuJdYs/@/:rw'Two constraints come with it. Only sha-512 is accepted, so the stored string always has to begin with $6$, and digest authentication does not function properly with hashed passwords, while the same server handles both basic and digest against plaintext. Wrap the hash in single quotes, because $6 can expand as a variable in some shells and truncate the secret. If your clients need digest auth, you are back to plaintext passwords in the command line or in a config file.
The hidden globs match names, not paths, so they cannot hide a nested file
The hide option filters directory listings, and it works on individual names:
dufs --hidden '.*'                          # hidden dotfiles
dufs --hidden '*/'                          # hidden all folders
dufs --hidden '*.log,*.lock'                # hidden by exts
dufs --hidden '*.log' --hidden '*.lock'
The limitation is stated plainly: the glob only matches file and directory names, not paths, so `--hidden dir1/file` is invalid. There is no way to express a nested target here, and the matching is a listing filter rather than a documented denial. The README only describes the option as hiding paths from directory listings, so do not treat it as access control. Consequence: use the @ based role rules to enforce what must stay private, and use --hidden only to reduce noise in listings. A pattern like '*.log' also applies at every depth, so a name you meant to exclude from one folder disappears everywhere.
Resumable upload derives its own offset from a content-length header
Resumption is entirely a client side protocol here. The offset comes from a HEAD request, and the remaining bytes are streamed as a PATCH carrying a range header:
upload_offset=$(curl -I -s http://127.0.0.1:5000/file | tr -d '\r' | sed -n 's/content-length: //p')
dd skip=$upload_offset if=file status=none ibs=1 | \
  curl -X PATCH -H "X-Update-Range: append" --data-binary @- http://127.0.0.1:5000/file
Downloads have the simpler half, `curl -C- -o file http://127.0.0.1:5000/file`. Note what the upload path implies. The offset is read out of a header by the client, and the shell filter matches on the literal text content-length. Health checks have their own endpoint for monitoring: `curl http://127.0.0.1:5000/__dufs__/health`.
The container is FROM scratch, so there is no shell and no config file to edit
The image builds two static musl binaries and ships the result into an empty base:
FROM ${TARGETARCH} AS builder

FROM scratch
COPY --from=builder /bin/dufs /bin/dufs
STOPSIGNAL SIGINT
ENTRYPOINT ["/bin/dufs"]
Both architecture stages run `cargo install --path . --root /` on musl cross images, which is why the amd64 and arm64 builds exist as separate targets. What the scratch base removes is worth knowing before you deploy: no shell, no package manager, and no writable config path, so the configuration has to arrive as command arguments, a mounted config file passed with -c, or environment variables. The manifest enables the env feature on the argument parser, which is what makes that last route available. STOPSIGNAL SIGINT means a stopping container delivers an interrupt to the process rather than a kill, so shutdown timing is the server's to handle.
Two license files sit next to a manifest that offers either one
The manifest states `license = "MIT OR Apache-2.0"`, and the repository root carries both LICENSE-MIT and LICENSE-APACHE, so downstream compliance is a choice you make rather than a single obligation. The build is pinned as well: Cargo.lock is committed, the crate version reads 0.47.0 to match the newest tag, and the edition is 2021. The declared categories, command-line-utilities and web-programming::http-server, tell you how the author expects the crate to be indexed. The dependency set explains several behaviors at once, including async-deflate-zip for the ?zip download, alphanumeric-sort for listing order, and sha-crypt for the sha-512 password support.
Recent releases and activity on main
Recent releases are v0.45.0 on 2025-09-04, v0.46.0 on 2026-05-07, and v0.47.0 on 2026-10-17. The last push is dated 2026-10-30, about two weeks after the newest release, so the branch head may contain work that no tag covers. The repository is not archived, and a CHANGELOG.md sits at the root next to the manifests if you want the detail between tags. Two practical consequences. If you deploy from a tag, you are running code that predates the branch head, so decide deliberately between a release and a commit. And if you track main, there is no version string to pin against until a new tag appears, which makes your release process your own problem rather than the upstream one.
Editorial conclusion
Pick dufs when you need one static binary that serves a directory with optional uploads, WebDAV methods, and per-path accounts, and when you can live inside its rules: sha-512 for stored hashes, listing globs matched by name rather than by path, and permissions that no account rule can widen. Do not reach for it if your security review needs password hashes in another algorithm, if you need denial of a specific nested path through the hide option, or if you need releases on a predictable cadence, since the last tagged build is v0.47.0 from 2026-10-17 and the last push is dated 2026-10-30.
Frequently asked questions
How do I run dufs with a username and password?
Pass role rules with -a, for example `dufs -a admin:123@/:rw`. Use @ to separate the account from its paths, : between username and password, , between paths, and a :rw or :ro suffix for the mode. Rules such as `dufs -a user:pass@/:rw,/dir1` give read-write on the root and read-only on /dir1.
How do I install dufs on Ubuntu or with Docker?
Three routes are offered: `cargo install dufs`, `brew install dufs`, or binaries from the GitHub releases page for macOS, Linux, and Windows. For containers the quickstart line is `docker run -v `pwd`:/data -p 5000:5000 --rm sigoden/dufs /data -A`, which mounts the current directory as /data and publishes port 5000.
Does dufs support hidden files, HTTPS, and WebDAV clients?
All three are supported. Use --hidden with globs such as '.*' or '*.log,*.lock' to keep names out of directory listings, `dufs --tls-cert my.crt --tls-key my.key` for https, and the WebDAV verbs the API section exercises, including MKCOL, MOVE, PATCH, and DELETE. Note that hidden globs match names rather than paths.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sigoden-dufs)Star history chart for your README
[](https://hysenlabs.com/projects/sigoden-dufs)Was this useful?