got's own front page tells you to use a different library instead
🌐 Human-friendly and powerful HTTP request library for Node.js
At a glance
- What is it?
- Got is an HTTP client for Node.js with retries, pagination, standards-compliant caching, HTTP/2 and Unix socket support. Its author maintains it, its default branch was pushed to on 2026-10-30 and it is at version 16.2.0. Two things about it are unusual and both are stated plainly on the front page. The author opens by telling readers they probably want one of his other libraries instead, and the client retries failed requests by default, which is the wrong default for anything that is not idempotent.
- Who is it for?
- This is the right tool when you specifically need the features it has that the fetch-based alternatives do not: automatic pagination over a listing endpoint, response caching that follows the HTTP specification, streaming responses, or Unix domain sockets. If you do not need one of those, the author is telling you plainly that a smaller library will serve you better, and he is the person who knows.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 15 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
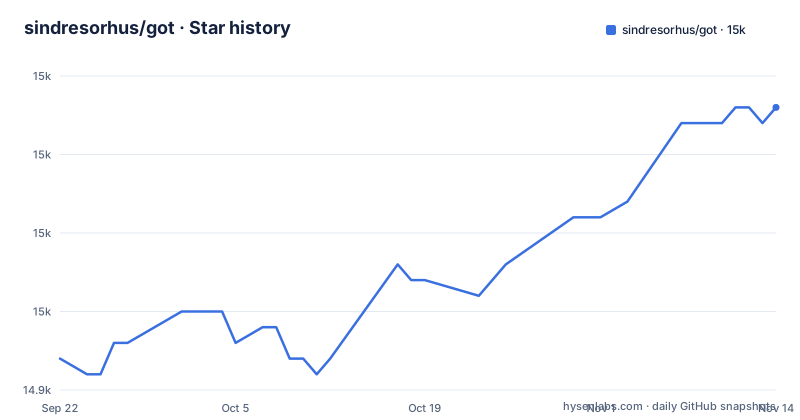
- sindresorhus/got14,963 ★ · +16
| Repository | 2026-09-22 | 2026-11-14 |
|---|---|---|
| sindresorhus/got | 14.9k | 15k |
16 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The front page opens by recommending a different library from the same author
This is the first substantive paragraph in the readme, and it is an argument against using the thing you just arrived at.
It says you probably want a different library, by the same people. The reasons given are that it is smaller, that it works in the browser too, and that it is more stable because it is built on the platform's own fetch interface. For simple needs it names a third option.
All three are by the same author, and one of the three is a direct competitor to this one. A maintainer telling you that a smaller sibling is more stable than their own larger project is an unusual thing to publish, and it tells you two useful things.
First, the comparison table further down the page is not advocacy. The same table marks this library as having no browser support while all four competitors have it, and marks pagination as something only this one does. Where the table favours competitors, it says so. That is a comparison you can trust.
Second, the advice is specific. Fetch-based libraries will be more stable on this author's own assessment, which for a library sitting on a platform interface rather than a Node-specific one is a reasonable claim rather than modesty.
So the consequence is to read the front page as doing triage. If your use needs pagination, caching or streaming, stay. If it does not, the author has told you which of his packages to install instead.
Failed requests are retried by default, and turning that off is a documented step
This is a default that surprises people, and the documentation leads with it rather than burying it.
The documentation section opens by stating that retries happen on failure by default, and that to disable this the retry limit option is set to zero. That sentence is the first thing in the documentation list, before the main API.
Why this matters is that retrying is only safe for requests where doing it twice changes nothing. A retrieval is fine. A submission may not be, and a payment or a created resource can be duplicated by the client's own retry logic rather than by anything the server did wrong.
The README names the option, options.retry.limit, and links to the retry documentation for the details of which requests are retried.
So the consequence is that adopting this library without reading that line can change the behaviour of your application in a way that only shows up under failure. Set it per call site on the first day rather than after your first duplicate.
There is no CommonJS entry point and the front page asks you not to ask about it
The install section carries a warning that is worth reading in full, because it includes an instruction about what not to do afterwards.
The package is native ES modules and no longer provides a CommonJS export. If your project uses CommonJS, the front page says you will have to convert to ESM, and links a guide for doing it.
Then the second half of the warning: do not open issues for questions regarding CommonJS or ES modules.
That is a maintainer drawing a line, and it is a reasonable one given how many such reports a package this widely used receives. It also tells you the migration cost is on you.
The Node version floor makes that harder. The manifest requires Node 22 or newer. So the choice is not between two module systems, it is between modernising your module setup and modernising your runtime at the same time.
The older major version is closed off too. The front page states that the eleventh major version is no longer maintained and that no backport requests will be accepted.
So there are three separate closures in this one section: no CommonJS, no issues about it, and no backports to the previous major line.
The consequence is that this library now requires a modern runtime and a modern module setup, and if you are on an older codebase it is a migration project rather than an install.
Server-side request forgery protection is a separate plugin, not a feature
Among the plugins listed on the front page there is one whose description is worth reading twice.
The others wrap this client for a specific service or purpose: signed AWS request handling, a GitHub convenience wrapper, a GitLab wrapper, a GraphQL query interface that parses queries rather than treating them as strings, a fetch-shaped interface, a scraper-oriented wrapper.
The seventh is described as a wrapper to protect server-side requests against server-side request forgery attacks.
The feature list shown on the front page does not include address filtering or allow-listing, and this plugin is offered as the way to add it.
This matters more here than in most libraries because one of the listed use cases for the scraper-oriented wrapper is fetching arbitrary pages on a server's behalf. That is exactly the pattern where a URL comes from user input and the server fetches it, which is the shape of the vulnerability.
So the consequence is that if you accept URLs from users and fetch them server-side with this library, you need that plugin or an equivalent allow-list, and the front page does not flag that as a default-on protection because it is not one.
Migration guides exist for three different starting points, one of them now unmaintained
The documentation includes guides for coming to this library from three places, and the framing tells you what the author considers the alternatives to be.
There is a guide for migrating from the older request library, one for Axios, and one for Node.js.
Three guides means three distinct populations this library wants to serve: people on the older community-maintained request package, people on the most popular promise-based client, and people who have no client at all beyond what the platform provides.
The note attached to the first guide is that the library being migrated from is unmaintained. That is stated as a fact with a link to its own tracker, which is both a reason to leave and a reason to be sceptical of a migration guide written partly to help people escape an abandoned dependency.
What none of the guides says is the reverse direction. There is no guidance here for someone deciding to leave this library, even though the opening paragraph recommends one of the alternatives. That asymmetry is honest and worth noticing: the author is actively helping people in, not out.
So the consequence is that the migration guides are a reasonable evaluation tool. Reading the Axios one tells you what this library thinks Axios users will miss, which is a compact statement of its own feature set.
The published package is one directory of compiled files with a single entry point
The manifest describes a deliberately narrow distribution, and it explains what you actually install.
There is a single entry point in the exports map, pointing at a type definition file and a compiled file in the same directory. There is no second entry point and no conditional export for a CommonJS consumer, which is the mechanical fact behind the warning in the install section.
The published files list is a single path, the compiled source directory. So the package is the build output and nothing else, with no sources and no test files in the tarball.
The package is also declared free of side effects, which lets a bundler drop it entirely if nothing is imported from it.
On the source side, the build is a single compiler invocation after deleting the output directory, and it runs automatically on install through the prepare script. Type checking is part of the test command rather than a separate step, running before the test runner alongside a linter.
So the consequence is that this is a compiled, single-entry, dependency-light package with no CommonJS path. That is a clean shape for a modern bundler and an awkward one for an older application.
The retry, pagination and caching features are the reason to be here at all
The comparison table is the clearest statement of what this library does that the alternatives do not, and it is a short list.
Streaming responses: this library and superagent have it, node-fetch has it only on Node, and ky and axios do not have it.
Pagination: this library has it, and none of the four competitors do.
Caching that follows the HTTP specification: this library lists RFC 7234 compliant caching among its features.
HTTP/2: this library and ky have it, node-fetch and axios do not, and superagent does with a caveat marker in the table.
Request aborting: all four have it.
Promise interface: all four have it.
So three features are genuinely differentiating and the rest is table stakes. If you are choosing between these libraries and you do not need pagination, caching, streaming, HTTP/2 or Unix sockets, the table says you are choosing on price, size and module format.
There is also a Unix domain socket option in the feature list, which matters if you are talking to a local service rather than a network one.
The JSON mode is the shape most people start from:
import got from 'got';

const {data} = await got.post('https://httpbin.org/anything', {
	json: {
		hello: 'world'
	}
}).json();
So the consequence is to identify which of those three you actually need before you start comparing. It is a much shorter conversation than a feature-by-feature one.
Editorial conclusion
This is the right tool when you specifically need the features it has that the fetch-based alternatives do not: automatic pagination over a listing endpoint, response caching that follows the HTTP specification, streaming responses, or Unix domain sockets. If you do not need one of those, the author is telling you plainly that a smaller library will serve you better, and he is the person who knows. Two things to check before you adopt it. Whether retries are acceptable in your request pattern, since they are on by default and you have to turn them off explicitly. And whether your application can be ES modules, because the package no longer ships a CommonJS entry point at all and the front page says not to open issues about it.
Frequently asked questions
what is sindresorhus got
Got is a human-friendly HTTP request library for Node.js, MIT licensed and written in TypeScript, currently at version 16.2.0. It runs on Node 22 or newer and is a native ES module with no CommonJS export. Its distinguishing features are a pagination interface, standards-compliant HTTP caching, streaming responses, HTTP/2 and Unix domain sockets.
How do I install got?
With `npm install got`. The install section carries a warning that the package is a native ES module and no longer provides a CommonJS export, so a project on CommonJS must convert to ES modules first. The manifest requires Node 22 or newer. The front page also states that the eleventh major version is no longer maintained and that no backport requests will be accepted.
Does got retry failed requests?
Yes, by default, and the documentation says so in its first line. To turn it off you set the retry limit option to zero. The retry documentation linked from the front page covers the details.
Which HTTP libraries does got compare against?
The front page compares it against node-fetch, the smaller fetch-based library by the same author, Axios, and superagent. The table marks this library as having no browser support while all four competitors have it, and marks pagination as a feature only it has. It also opens by saying you probably want the smaller fetch-based library instead unless you need the extra features.
Does got protect against server-side request forgery?
The front page does not list it as a built-in feature. It lists a separate third-party plugin whose described purpose is to protect server-side requests against server-side request forgery attacks. Other plugins wrap it for signed AWS requests, the GitHub and GitLab interfaces, a parsed GraphQL query interface, a fetch-shaped interface, and web scraping.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sindresorhus-got)Star history chart for your README
[](https://hysenlabs.com/projects/sindresorhus-got)Was this useful?