open: one function, three platform launchers, and a wait option that lies to you
Open stuff like URLs, files, executables. Cross-platform.
At a glance
- What is it?
- A small package that opens a URL, file or executable in the default or a named application. The published artefact is three files, the security note is blunt, and the documentation spends most of its length on the ways the wait option can mislead you.
- Who is it for?
- Use open in a command-line tool or script when you need to hand something to the user's desktop and get out of the way, because it is three files with two runtime detection helpers and nothing else. It is exactly the right size for the job and it does not want to be a framework.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 62 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
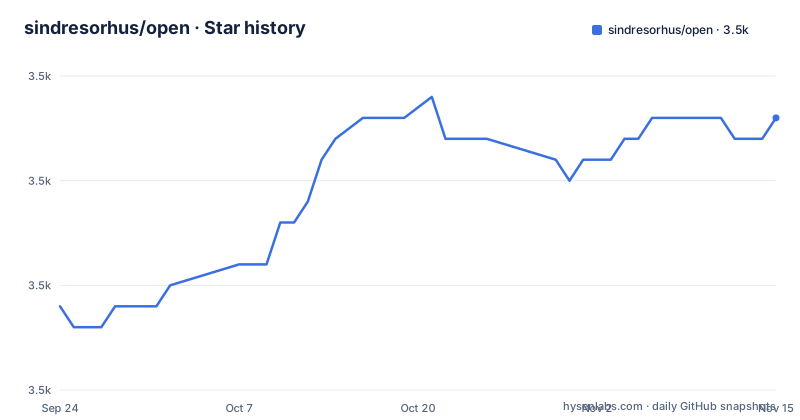
- sindresorhus/open3,523 ★ · +9
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| sindresorhus/open | 3.5k | 3.5k |
9 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
It spawns a launcher, it does not exec a shell
The whole design is in one sentence: it spawns rather than execs.
That distinction is the reason to prefer this over doing it yourself. Shelling out with a string means the platform command receives a command line that something has to parse, and parsing is where quoting bugs live. Spawning takes the program and its arguments separately, so a filename with a space in it is not an injection vector.
The launchers are the platform's own: a command that opens things with the default application on macOS, a different one on Windows, and the freedesktop opener everywhere else. That last one is vendored into the repository rather than assumed to exist on the machine, which is why the published files include the script itself.
The other reasons the documentation gives are worth separating from that one. It supports passing arguments to the application, which the original tool it grew out of did not handle well. It fixed most of the issues in that original package. And it handles paths that cross a subsystem boundary from Linux to Windows, which is a case that only appears once somebody has a Windows machine with a Linux environment on it.
The scope is stated just as plainly: this is for command-line tools and scripts, not for the browser, and the documentation points desktop application developers at their own platform's equivalent instead.
wait is the option with the caveats, and browsers break it
Most options here are ordinary. One is not, and it is the one you will reach for first.
The wait option tells the package to hold its promise open until the opened application exits. The default is false, in which case the promise fulfils as soon as the application has been launched. And the documentation is careful about what it waits for: the application exiting, not the window closing.
Two limitations follow. On Windows you have to name the application explicitly, otherwise it cannot wait at all.
Then there is the one flagged with a warning, and it is a genuine trap. If you open a URL in a browser that is already running, wait does not behave as expected. The reason given is architectural rather than a bug: browsers use a single-instance design, so the new URL is handed to the process that is already running, and the command that launched it exits immediately.
So your code awaits a promise, the promise resolves, and the browser is still open. Nothing warns you, because from the package's point of view the child process did exit.
The documented workarounds are honest about their limits. On macOS you can force a new instance of the application so the launched process is the one that owns the URL. Everywhere else the advice is to avoid combining wait with browsers, which is the same as saying do not use the option for the most common case.
App names differ per platform, which is why there is an apps object
The option that names an application is where cross-platform work actually happens.
It accepts a single application, or an array of applications to try in order, and the name itself can be an array of names to try. If every candidate fails, the last error is thrown rather than a generic failure, which is what you want when debugging a name that stopped matching.
The reason the documentation repeats the same warning twice, once for this option and once for the separate function that opens an application, is that application names are platform specific. The example given is one browser, which has three different names depending on the system: one on macOS, one on Linux, and a third on Windows.
The auto-detected object is used like this:
import open, {apps} from "open";

await open("https://google.com", {
	app: {
		name: apps.chrome
	}
});
So the guidance is not to hard code a name in a reusable module, and to use the auto-detection object where possible. That object carries detected binary names for four browsers, plus two entries for the user's default browser and for the default browser in private mode, the latter two served by a separate small package and limited to those same four browsers.
There is one more escape hatch, and it is the one you need under a subsystem. You can pass the full path to the executable, and the documented example is a Windows installation of a browser reached from a Linux subsystem through the mounted drive path, spaces and all.
Arguments to the launched application are passed the same way, with the same caveat that only that application's own documentation says what it accepts.
Two macOS-only options and one option the author asks you not to set
Two of the options exist only on macOS, and their behaviour elsewhere is stated rather than left blank.
One keeps the launched application out of the foreground. The other asks for a new instance even when the application is already running. That second one is the fix for the browser problem, and the documentation also notes that on other platforms a new instance is always opened anyway, which is why it is a macOS-only knob.
The third option is the interesting one, because the documentation recommends against it. It allows the launched application to exit with a nonzero status while waiting, on the grounds that the convention for success is an exit code of zero.
That is a reasonable position and it is worth understanding why. The wait option's whole job is to tell you whether opening succeeded, so allowing a failure code through removes the only signal you have and leaves you parsing the application name to guess. The author would rather you handle the rare case where an application exits nonzero on success yourself.
There is also a separate function for opening an application rather than a target. It takes the same options apart from the application one, and adds an arguments field that defaults to empty. So the two functions overlap almost entirely, and the split exists so that opening a named application does not require the awkward shape of the application option.
WSL is handled by trying PowerShell and falling back
The subsystem case gets its own section, which tells you it has caused problems.
The behaviour is a chain. When the package detects that Windows integration is available it uses it, through PowerShell. When PowerShell is not reachable, and the documentation gives the example of a sandboxed environment, it falls back to the freedesktop opener like any other Unix system.
That ordering makes sense. Under a subsystem you are on Linux but the desktop is Windows, so the Windows integration is the one that actually reaches the user's applications, while the freedesktop opener reaches the Linux side of the machine instead. Falling back is the correct behaviour rather than a failure, but it also means the two paths open different applications, which is worth knowing when something opens the wrong thing.
If you want the Linux behaviour deliberately, you can name the freedesktop opener as the application, and that is a documented one-line option rather than a trick.
The same environment detection shows up in the dependency list. Two of the runtime dependencies are small packages whose only job is answering whether you are in a remote shell session and whether you are inside a container. Both change how an application should be launched: there is no local display to bring to the foreground over a remote session, and a container may have neither the Windows integration nor a display server.
Detecting those two conditions is most of what this package does beyond spawning a launcher.
The published package is three files, and one of them is a shell script
Look at the file list in the manifest and the project's scope becomes concrete.
Three files are published: the implementation, its type declarations, and the vendored desktop opener script. Everything else in the repository is for development or is not shipped.
The module is native ES modules with a single export condition carrying the types, and the manifest declares no side effects, so a bundler can drop it if you import nothing from it. The runtime requirement is a current major version of Node.
There is a migration note, and it is written for people who upgraded rather than for new users. The package no longer provides a CommonJS export, so a CommonJS project has to convert or use dynamic import, and the documentation closes with a request not to file issues about that. It is a blunt instruction, and it exists because the same question arrives constantly.
The security position is in the second paragraph rather than at the end, where you would expect it. The package states that it makes no security guarantees and that if you pass untrusted input, sanitising it is your responsibility. Given that the package's whole advantage is avoiding shell parsing, that sentence is narrower than it sounds, but it is still there and it is still true: this opens things, and it opens whatever you hand it.
The manifest also carries a funding link and the author field, which in a package this small is one of the few non-code signals a user gets.
npm test lints and type checks, and the runtime tests sit beside it
The scripts section is one line, and it is not what you would guess.
The test script runs a linter and a type-definition test tool. It does not run the runtime tests.
Those exist separately: a test runner is a development dependency, and the repository has both a single test file and a test directory. So the package has runtime tests that are not wired to the default script.
That is worth knowing for a contributor, because the first thing you will do is run the test script and conclude the runtime tests pass when they never ran. It is also a defensible arrangement: the type definitions are the public contract of a package like this, so checking them on every run is the higher value check, and the linter is fast enough to always run.
The release picture is the other signal. This is major version eleven, with three patch releases across August and September 2026, and the last commit in this snapshot matches the newest patch. There are no changelog entries in the repository itself, so the commit log is the record.
Taken together: a mature, small, dependency-light package that changes when the platforms underneath it change, whose biggest documented risks are the browser single-instance behaviour and the absence of any sanitising on your behalf.
Editorial conclusion
Use open in a command-line tool or script when you need to hand something to the user's desktop and get out of the way, because it is three files with two runtime detection helpers and nothing else. It is exactly the right size for the job and it does not want to be a framework. Skip it in the browser, where the documentation says outright that it is not meant, and skip it in an Electron application, where the platform already has an equivalent. Before you use the wait option anywhere, read the warning about browsers, because the promise can resolve while the application is still open and there is no flag that fixes it outside macOS. And if you accept untrusted input, do the sanitising yourself: the package says in its second paragraph that it makes no security guarantees at all.
Frequently asked questions
What does the open package do?
It opens a URL, file or executable in the default application or a named one, using the platform's own launcher: a different command on macOS, another on Windows, and the freedesktop opener elsewhere. It returns a promise for the spawned child process.
Is open safe to use with untrusted input?
The package states that it makes no security guarantees and that sanitising untrusted input is your responsibility. Its design avoids shell string parsing by spawning the launcher with arguments separately, but that is not a substitute for validating what you pass.
How do I open a URL in a specific browser with open?
Pass an app option naming the application, or use one of the auto-detected names from the exported apps object, because application names differ per platform. You can pass an array of applications to try, and the last error is thrown if all of them fail.
Why does the wait option not work with browsers?
Browsers use a single-instance design, so a new URL is handed to the process that is already running and the launcher exits immediately, which resolves your promise while the browser is still open. On macOS a new instance option can be forced; elsewhere the advice is to avoid wait when opening URLs.
Does open support CommonJS?
No. The package is native ES modules and no longer provides a CommonJS export, so a CommonJS project has to convert or use dynamic import. The README asks that questions about that not be filed as issues.
How does open behave under the Windows Subsystem for Linux?
It uses the Windows integration through PowerShell when that is available, and falls back to the freedesktop opener when PowerShell cannot be reached, such as in sandboxed environments. Naming the freedesktop opener explicitly makes it use Linux applications instead.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sindresorhus-open)Star history chart for your README
[](https://hysenlabs.com/projects/sindresorhus-open)Was this useful?