Two defects in burp-ai-agent 0.9.x, and what the 1.0.0 release changed
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
At a glance
- What is it?
- Custom AI Agent is a Kotlin extension that puts MCP tooling, twelve AI backends and sixty-two vulnerability classes inside Burp Suite. Its whole 0.9.x line shipped two defects confirmed by running the shipped code, and both are fixed in the 1.0.0 release dated 2026-08-22.
- Who is it for?
- Custom AI Agent is worth loading from a release JAR if you test systems you hold written authorization for, and if you read SECURITY.md before you upgrade rather than after. Take 1.0.0, never a 0.9.x build: that line accepted unauthenticated MCP tool calls when external access was on, and it handed session cookies to AI backends unredacted under both STRICT and BALANCED, so rotating the MCP token and the affected cookies is part of the upgrade rather than an optional extra.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 25 days ago.
- What is it written in?
- Mainly Kotlin, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
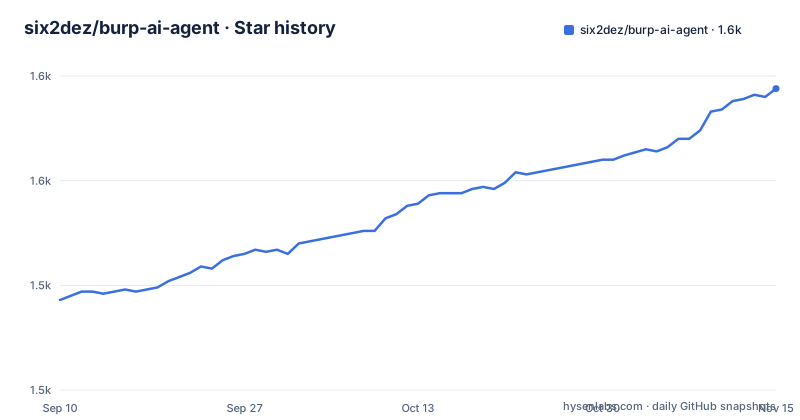
- six2dez/burp-ai-agent1,594 ★ · +101
| Repository | 2026-09-10 | 2026-11-15 |
|---|---|---|
| six2dez/burp-ai-agent | 1.5k | 1.6k |
101 Stars in the last 66 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Access control ran after routing, not ahead of it
Every published 0.9.x release carried SEC-04, rated critical, and the fix is a question of ordering. The MCP access-control decision did not run on resolved routes, which means the judgement was made at the wrong point in request handling. With external access enabled, the listener accepted unauthenticated tool calls, so any client that could reach the port could drive the fifty-nine tools the full build ships. In local mode the same ordering flaw left the Origin, Host and User-Agent checks inert on matched routes, together with the security response headers. 1.0.0 moves the decision ahead of routing, so a request is judged before a handler is picked.
The advisory is unusually specific about provenance. An external review of 0.9.2 on 2026-08-05 confirmed two exploitable defects by running the shipped code, and one of the two requires rotating credentials that may already have been disclosed to a third party. No CVE or GHSA identifier has been issued for either, so there is nothing to look up and nothing to search a bulletin for. The instruction attached to SEC-04 is to rotate your MCP token, which is the detail that turns this from a version bump into an incident response step.
STRICT and BALANCED both shipped session cookies in the clear
PRIV-05 is the second confirmed defect, and its shape is a lesson in what a privacy mode actually guarantees. The extension offers three modes, STRICT, BALANCED and OFF, and the two stricter ones failed. Session cookies reached AI backends unredacted under STRICT and again under BALANCED. The passive scanner emitted them as bare `name=value` pairs, which dropped the prefix redaction the rest of the pipeline keyed on, and the only cookie name the check caught was the literal string `session`. Any other name fell outside that check entirely.
The scanner behind this is the passive half of the sixty-two vulnerability classes the extension advertises, and it registers inside Burp as a `PassiveScanCheck`, which is a Burp Pro facility rather than a Community one. So the mode label was carrying more weight than the redaction logic underneath it, and a user who read the label rather than the advisory had no way to know which of their cookies were being forwarded to a hosted model endpoint.
The advisory response to PRIV-05 is to rotate the affected cookies. Because those values had already left Burp toward whichever backend you configured, rotating the cookie is the only way to establish which ones were exposed, and a model provider's own retention policy is not something this extension can speak for.
The store build and the full build are not the same extension
One Gradle property decides how much of the extension you get.
git clone https://github.com/six2dez/burp-ai-agent.git
cd burp-ai-agent

# Full build (default, GitHub releases) — all 59 MCP tools
JAVA_HOME=/path/to/jdk-21 ./gradlew clean shadowJar
# Output: build/libs/Custom-AI-Agent-full-<version>.jar

# Store build (BApp Store submission) — 8 extension-native AI tools only
JAVA_HOME=/path/to/jdk-21 ./gradlew clean shadowJar -PstoreBuild=true
# Output: build/libs/Custom-AI-Agent-<version>.jar
The default task produces the full JAR carrying all fifty-nine MCP tools, while `-PstoreBuild=true` cuts that down to the eight extension-native AI tools the BApp Store submission may carry. The two outputs have different filenames, so the name alone tells you which side of that split you are holding. Java 21 is the only prerequisite and it is pointed at through `JAVA_HOME`.
Either way the JAR registers in Burp as Custom AI Agent, added through Extensions, Installed, Add with the type set to Java, and it loads into Community as well as Professional. The twelve backends range from Burp's own built-in Burp AI through hosted providers, Ollama and LM Studio for local ones, the CLI front ends Gemini CLI, Claude CLI, Codex CLI, OpenCode CLI and Copilot CLI, and a generic OpenAI-compatible slot. Setup is laid out as a three column table of Backend, Type and Setup, and the row entries are not written out, so treat the Settings panel in the AI Agent tab rather than a guess as the source for the exact values.
Tool calls the model writes now stop for a decision
Before 1.0.0 a tool call could be parsed out of model output and reach Burp without anyone seeing it. SEC-06 closes that. A call arriving as text from the model does not execute until you decide, and the tiers fail closed rather than open: read-only bounded tools run silently, everything else raises an approval card in the chat, and a tool name the extension does not recognise asks every single time rather than running or being dropped. The failure direction is the point. An unrecognised name is exactly the case where a permissive guess would be cheapest, and a permissive guess is what turns a prompt injection into a tool invocation.
The same release moved three blocking operations off the Swing event dispatch thread, which is where tool execution, backend HTTP calls and the MCP `stop()` method used to sit. Recurring tasks are now guarded against death by exception, so a task that throws stops being scheduled silently instead of quietly disappearing. Together these change what a slow call looks like from the outside: the Burp window keeps responding while the request is in flight, and the approval card is the durable record of what you allowed.
The 1.0.0 notes also record the test suite growing from 660 to 1131 tests across 158 classes, project line coverage rising from 34% to 58%, and a detekt baseline that shrank from 1096 to 1040 entries rather than growing to absorb new findings. The last of those three is the one that suggests the defects were found by looking rather than by coverage arithmetic.
A local process squatting the port no longer walks away with the token
The MCP listener binds a local port, and a position another process on the same machine can take first. SEC-07 describes exactly that: a local process squatting the MCP port and echoing back the identity header could harvest a token granting full MCP tool access, which is the same reach an unauthenticated remote caller gets once external access is switched on. The takeover client now presents an HMAC proof of possession instead of the token itself, so a squatter that only listens learns nothing usable, and under TLS the client pins the server certificate to its own keystore rather than accepting whatever certificate answers on that port.
This sits directly beside the Scoped MCP Access feature, which confines each MCP tool to the hosts you have placed in scope so an external AI client cannot reach an out-of-scope target by way of Burp. Scoping is worth understanding before you enable external access, because it is the layer that decides which hosts a tool call can land on at all. The audit log is the layer that shows what happened afterwards: launches are stamped with `promptSource` and `contextKind` into JSONL with SHA-256 integrity hashing, which is aimed at compliance evidence rather than at debugging, and it records the decision context rather than the decision itself.
Notation decides whether SsrfGuard raises the private address warning
SSRF protection that recognises private and link-local ranges by string matching is sidestepped by writing the same address a different way. The example the release notes give is `http://2852039166/`, which is decimal notation for `169.254.169.254`, the cloud instance metadata address. Under the old classification, changing the notation alone was enough to fall outside the private and link-local warning. SsrfGuard now classifies alternate IP notations, and it does so with no name resolution at all, which is the part worth sitting with. If classification had to resolve a name in order to decide, the answer would depend on who controls name resolution at the moment of the request, and the check would be answering a different question from the one that decides whether a call is allowed.
The same release closes a shorter path. QUAL-06 is a route from importing a settings file to running a command, reachable with values that carry shell metacharacters but no whitespace at all, `foo;id` and `$(cmd)` being the two cases named. Shell arguments are now quoted by allowlist, so an imported value is handed to the process as an argument instead of being re-parsed by a shell. Both of these read like hardening notes and behave like boundaries, which is why they sit in the same SECURITY.md advisories entry as the token rotation rather than in the general changelog.
Custom AI Agent in the Extensions list, burp-ai-agent on disk
The published name and the project name differ, and the split is deliberate. The extension appears in the BApp Store listing, in the Extensions list and as the Suite tab as Custom AI Agent, renamed from Burp AI Agent to meet PortSwigger's naming requirements and to keep it distinct from the built-in Burp AI provider. The GitHub repository, the documentation site at burp-ai-agent.six2dez.com, and the configuration directory `~/.burp-ai-agent/` all keep the older identifier, so anything that matches on the package name will not match on the display name and the reverse holds too.
On first run the extension auto-installs its bundled agent profiles into `~/.burp-ai-agent/AGENTS/`, and dropping further `*.md` files into that directory adds custom profiles, which makes the profile set a plain file operation rather than a settings screen exercise. The repository root carries the same habit in the open: `AGENTS.md`, `CLAUDE.md`, `DECISIONS.md`, `SPEC.md`, `skills/`, `docs/`, `.planning/` and `screenshots/` sit beside `build.gradle.kts`, `detekt.yml` and the `detekt-baseline.xml` the release notes measure themselves against.
Distribution is still a JAR from the releases page. The store submission tracked as issue 231 in PortSwigger's extension portal has been open since January 2026. The three most recent tags are v1.0.0 on 2026-08-22 and v0.9.2 and v0.9.1 both on 2026-07-29, and the last push on record is dated 2026-09-02.
Editorial conclusion
Custom AI Agent is worth loading from a release JAR if you test systems you hold written authorization for, and if you read SECURITY.md before you upgrade rather than after. Take 1.0.0, never a 0.9.x build: that line accepted unauthenticated MCP tool calls when external access was on, and it handed session cookies to AI backends unredacted under both STRICT and BALANCED, so rotating the MCP token and the affected cookies is part of the upgrade rather than an optional extra. Before you load anything, confirm which of the two JARs you downloaded, because the store build exposes eight MCP tools and the full build exposes fifty-nine, and confirm the review scope you hold actually covers the hosts you point the scanners at. Scoped MCP Access narrows what a tool call can reach, but it is a constraint on your own configuration and not a permission.
Frequently asked questions
What does the Custom AI Agent extension add to Burp Suite?
It registers twelve AI backends, fifty-nine MCP tools in the full build, sixty-two vulnerability classes covered by passive and active scanners, three privacy modes, a custom prompt library per context, and JSONL audit logging with SHA-256 integrity hashing. The passive scanner runs as a Burp PassiveScanCheck, which needs Burp Pro.
Is burp-ai-agent on the PortSwigger BApp Store yet?
Not yet. The submission has been open as issue 231 in PortSwigger's extension portal since January 2026, so installation means downloading a JAR from the project's releases page or building one from source with Java 21.
How many MCP tools ship in the burp-ai-agent store build?
Eight extension-native AI tools. The full build produced by the default Gradle task carries all fifty-nine, and the two JARs are named differently, `Custom-AI-Agent-full-<version>.jar` against `Custom-AI-Agent-<version>.jar`.
Why do the burp-ai-agent 0.9.x releases carry a security advisory?
An external review of 0.9.2 on 2026-08-05 confirmed two exploitable defects by running the shipped code, and the advisory states both affect every published 0.9.x release. They are fixed in 1.0.0, no CVE or GHSA identifier has been issued, and the prescribed response is to rotate your MCP token and the affected cookies.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/six2dez-burp-ai-agent)Star history chart for your README
[](https://hysenlabs.com/projects/six2dez-burp-ai-agent)Was this useful?