A security skill whose own install advice is a URL
SlowMist Agent Security Skill: A comprehensive security review framework for AI agents operating in adversarial environments. Core principle: Every external input is untrusted until verified.
At a glance
- What is it?
- SlowMist's agent security skill is six review guides, a red-flag pattern file and a four-level risk scale that an agent applies to skills, repositories, documents, addresses and product recommendations. The irony is structural: the fastest documented install is to hand a repository URL to an agent, and the install step that claims to download the latest release points at a repository with no releases.
- Who is it for?
- slowmist-agent-security fits a team that has already decided an agent may install things and wants a written procedure for what to check first, with a rating scale that forces a decision and a human approval step at the top of the risk band. It does not enforce anything: the framework is followed by the same agent that could be manipulated.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 7 months ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
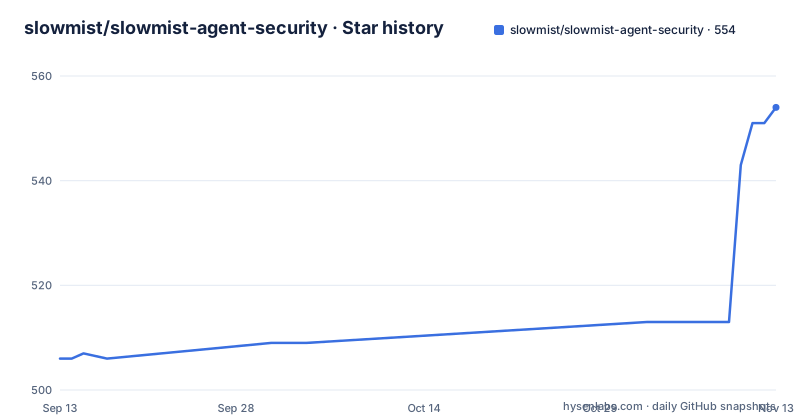
- slowmist/slowmist-agent-security554 ★ · +48
| Repository | 2026-09-13 | 2026-11-13 |
|---|---|---|
| slowmist/slowmist-agent-security | 506 | 554 |
48 Stars in the last 61 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The install section points at a release that does not exist
Option one tells you to download the latest release and extract it into your agent's skills workspace, then shows a `git clone` into `~/.openclaw/workspace/skills`, which is a clone rather than a release download. The repository publishes no GitHub releases, so there is no latest release to fetch and the two sentences describe different things.
cd ~/.openclaw/workspace/skills
git clone https://github.com/slowmist/slowmist-agent-security.git
Option two is a ClawHub install, marked as available when it is, which means the distribution channel you may prefer is also the one the document cannot promise. The framing sentence above both is the one to think about: you can hand the repository URL to your agent and let it install. For a framework whose stated principle is that every external input is untrusted until verified, that is the sharpest edge in the repository, since it asks for exactly the unreviewed fetch the framework exists to catch.
Six review guides, one pattern file, and a missing directory
The framework is organised as `SKILL.md` for the main documentation, `_meta.json` for ClawHub metadata, six guides under `reviews/` covering skill and MCP installation, repository review, URL and document analysis, on-chain addresses, product and service evaluation, and social shares, plus `patterns/red-flags.md`. The two worked examples end by writing a report from `templates/report-skill.md` and `templates/report-onchain.md`, and a `templates/` directory does exist in the repository, but the structure diagram in the README does not list it. A reader copying the layout from the document will miss the output half of the workflow and only discover the templates when a run fails to write its report.
Four levels, and only the bottom one is automatic
The risk scale is the part an agent can act on. LOW covers information-only items with no execution, no data collection and a trusted source, where the agent informs the user and proceeds if asked. MEDIUM is limited capability with clear scope and some risk, producing a full report with risk items and a recommendation to be careful. HIGH involves credentials, funds, system modification or an unknown source and requires human approval. REJECT means the item matches red-flag patterns or has an unacceptable design, and the agent refuses and explains. Three of the four therefore end in a human reading the output, which is the correct shape for this problem and also means the framework cannot be automated away.
Stars are treated as a reason to read the code
The trust hierarchy is five tiers and deliberately unpopular. An official project or exchange organisation sits at tier one with moderate scrutiny, a known security team or researcher at tier two also with moderate scrutiny, a ClawHub package with high downloads and multiple versions at tier three with moderate to high, a GitHub repository with many stars and active maintenance at tier four with high scrutiny and an instruction to verify the code, and an unknown source or new account at tier five with maximum scrutiny. The ordering puts an official vendor on the same footing as an independent researcher, and it puts popularity in the fourth tier rather than the first, which is the opposite of how most people triage a link a colleague sent.
What each review is actually for
The six areas cover different threat shapes. Skill and MCP installation is about malicious patterns arriving with a package. Repository review is a code audit. URL and document analysis looks for prompt injection and social engineering, which is the part aimed at content rather than code. On-chain address review is AML risk assessment and transaction analysis, with the example validating the address format, querying AML risk data through whatever tools are available, and writing a report. Product and service evaluation is architecture and permission analysis, and social share review validates tools recommended inside chats, which is the case where a recommendation arrives with no URL to inspect. An external MistTrack skills package is offered for the on-chain path. The patterns behind all of this are credited: the framework is inspired by a community skill called skill-vetter, its attack patterns are informed by SlowMist's own OpenClaw security practice guide, and the prompt injection patterns are described as based on real-world proof-of-concept research rather than on imagination.
Where this is the wrong tool
Three limits. It is guidance, not enforcement: nothing here stops an agent from installing a malicious skill, and the reviewer is the same agent being reviewed, which is the structural weakness of any prompt-level defence. It is also manual in the way a security review has to be, with no scanner, no hook in a CI pipeline and no automatic gate, so it only helps when a person remembers to invoke it. And the on-chain path depends on an external AML integration being present, while the ClawHub channel is described as available only when it is. The last push to the default branch was on 2026-04-17 with no releases published, so treat the pattern list as a starting set rather than a maintained corpus. The project is maintained by SlowMist under the MIT licence, and it invites contributions of new attack patterns, improved detection rules and additional review templates, which is the maintenance model that matches a document someone else has to keep current for you.
Editorial conclusion
slowmist-agent-security fits a team that has already decided an agent may install things and wants a written procedure for what to check first, with a rating scale that forces a decision and a human approval step at the top of the risk band. It does not enforce anything: the framework is followed by the same agent that could be manipulated. Verify two things before relying on it, that the skill is installed by a person who read it rather than by an agent handed a URL, and that the report templates its examples reference are present in your copy, since the structure diagram does not list the templates directory.
Frequently asked questions
What does the SlowMist Agent Security Skill cover?
Six areas: skill and MCP installation review, GitHub repository review, URL and document analysis for prompt injection and social engineering, on-chain address review for AML risk, product and service evaluation, and social share review for tools recommended in chats. Each has a guide under reviews/ with red-flag patterns in patterns/red-flags.md.
How do I install slowmist-agent-security?
Clone the repository into your agent's skills directory, which the example shows as ~/.openclaw/workspace/skills, or install it from ClawHub when that channel is available. The README also suggests handing the repository URL to your agent and letting it install, which is worth doing by hand given the framework's own premise.
What risk levels does slowmist-agent-security use?
Four. LOW is information-only with a trusted source, where the agent informs you and proceeds if asked. MEDIUM produces a full report and a recommendation for caution. HIGH covers credentials, funds, system modification or an unknown source and must have human approval. REJECT means the item matches red-flag patterns or has an unacceptable design, and the agent refuses.
Does a popular GitHub repository get trusted automatically?
No. The trust hierarchy puts GitHub repositories with many stars and active maintenance at tier four, with high scrutiny and an instruction to verify the code, while unknown sources and new accounts get maximum scrutiny and official vendor organisations sit only at tier one with moderate scrutiny.
Can slowmist-agent-security assess a blockchain address on its own?
It validates the address format and queries AML risk data through whatever tools are available, then writes a report. An external integration, MistTrack Skills, is offered for that step, so the assessment depends on a tool being present.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/slowmist-slowmist-agent-security)Star history chart for your README
[](https://hysenlabs.com/projects/slowmist-slowmist-agent-security)Was this useful?