driftctl: the drift scanner whose newest tag is older than its newest commit
Detect, track and alert on infrastructure drift
At a glance
- What is it?
- driftctl maps AWS, Azure, GCP and GitHub resources onto Terraform code to report drift, and its own build files say more about its current state than its release line does: a maintenance mode banner sitting above a beta warning, acceptance tests that create and destroy real cloud resources, and a Makefile that rewrites go.mod on every default run.
- Who is it for?
- driftctl still answers a question nothing else in that stack does: which parts of a live account never made it back into Terraform. Treat it as a fixed snapshot rather than a dependency that grows.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 8 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
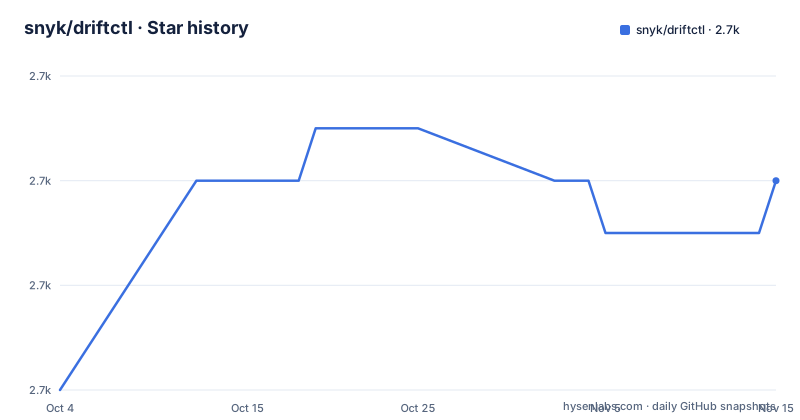
- snyk/driftctl2,666 ★ · +4
| Repository | 2026-10-04 | 2026-11-15 |
|---|---|---|
| snyk/driftctl | 2.7k | 2.7k |
4 Stars in the last 42 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two lifecycle statements sit in the same README
The file opens by declaring the project in maintenance mode, saying contributions will not be reviewed and inviting forks. Twenty lines further down, a warning block still announces that the tool is in beta state and will evolve with breaking changes. Neither statement has been reconciled with the other. The tags carry their own version of the story: v0.40.0 shipped on 2023-12-01, v0.39.0 on 2023-06-06 and v0.38.2 on 2023-01-09, while the default branch took a commit on 2026-09-21. A package manager install and a build from the branch are therefore not the same program, and nothing in the tree says which one you have. The centered header block and the Links section also carry two different Discord invite codes, discord.gg/NMCBxtD7Nd and discord.gg/7zHQ8r2PgP.
Acceptance tests create and destroy real cloud resources
The acceptance target sits one environment variable away from running against a live account:
ACC_PATTERN ?= TestAcc_
acc:
	DRIFTCTL_ACC=true $(GOTEST) --format standard-verbose --junitfile unit-tests-acc.xml -- -coverprofile=cover-acc.out -test.timeout 5h -coverpkg=./pkg/... -run=$(ACC_PATTERN) ./pkg/...
DRIFTCTL_ACC is the only thing standing between the suite and whatever provider credentials the shell exports, and the five hour timeout leaves plenty of room for waits against real APIs. The README's security notice confirms the intent: the Terraform state and Terraform files committed here exist for unit tests, and the one exception where running code touches those resources is the create and destroy that acceptance tests perform. There is no dry run flag and no per test confirmation, so the account you aim this at should be a disposable one.
make with no arguments rewrites go.mod before it builds
The default target is a chain that ends in the dependency files:
all: fmt lint test build go.mod

go.mod: FORCE
	$(GOMOD) tidy
	$(GOMOD) verify
go.sum: go.mod
Because FORCE is declared phony, make treats go.mod as permanently out of date. Every default invocation runs go mod tidy and go mod verify, and go.sum is rebuilt from the result. The unit tests in the same run use -mod=readonly, which means they execute against a module graph that the build was free to edit moments earlier. The README hands build work to two files it never spells out itself, .github/CONTRIBUTING.md for the process and docs/README.md for technical details, so a fork inherits the recipe rather than the reasoning behind it.
The linter is fetched by piping a script from a moving branch
lint:
	@which golangci-lint > /dev/null 2>&1 || (curl -sSfL https://raw.githubusercontent.com/golangci/golangci-lint/master/install.sh | bash -s -- -b $(GOBINPATH) v1.64.7)
	golangci-lint run -v --timeout=10m
The tool version is pinned to v1.64.7, but the installer is pulled from the master branch of the golangci-lint repository, so the script that decides what to download can change without any commit here. Elsewhere the same file pins by version: install-tools installs gotestsum at v1.10.0 and mockery at v2.36.1. The two build recipes work the same way, one passing SINGLE_TARGET=true and the other ENV=release to scripts/build.sh, which is also where the per target output directory used by the Dockerfile gets its name.
Coverage is filtered by grepping mock_ out of the profile
The test recipe measures coverage across the root package and everything under pkg/, writes it to cover.out.tmp, then rebuilds the profile by dropping every line whose file name contains mock_:
test:
	$(GOTEST) --format testname --junitfile unit-tests.xml -- -mod=readonly -coverprofile=cover.out.tmp -coverpkg=.,./pkg/... ./...
	cat cover.out.tmp | grep -v "mock_" > cover.out
The coverage target depends on test and hands the filtered file to go tool cover -func, so the number a maintainer reads is the one with mock files removed. That is defensible for a codebase that checks generated mocks into the tree, and it matters here because mocks/ is committed while the mocks target deletes the whole directory and regenerates it with mockery --all, even though .mockery.yaml at the root already configures the generator.
Cloud and Terraform libraries are pinned years behind the Go toolchain
module github.com/snyk/driftctl

go 1.23.0

require (
	github.com/Azure/azure-sdk-for-go/sdk/resourcemanager/compute/armcompute v0.2.0
	github.com/aws/aws-sdk-go v1.44.122
	github.com/hashicorp/terraform v0.14.0
	github.com/hashicorp/terraform-exec v0.14.0
)
The module asks for Go 1.23.0 and the Dockerfile builds on golang:1.23, yet the Terraform libraries it depends on sit at v0.14.0 and every Azure resource manager module shown here is at v0.2.0. The AWS dependency is aws-sdk-go v1.44.122, and the HCL parser is hcl/v2 v2.7.2. Those pins decide which provider API shapes and which HCL and state parsing paths driftctl can handle, and a fork inherits them before it changes a line. Terraform Cloud or Enterprise support arrives the same way, through hashicorp/go-tfe v0.20.0, and GitHub through go-git v5.4.2.
A Sentry client ships inside the scanner
The tree carries a sentry/ package and go.mod pulls getsentry/sentry-go at v0.10.0, so error reporting is compiled into a tool whose whole job is enumerating a cloud account and printing resource inventories. The README says nothing about what is sent, when it is sent, or how to switch it off, and there is no configuration section covering it. The same root directory holds .snyk, the policy configuration of the company that owns the project, and .gitleaksignore, which means at least one class of finding is deliberately kept out of secret scanning. For a binary you intend to point at production credentials, the initialization inside sentry/ is the first file worth reading.
The runtime image is one binary on alpine, running as root
FROM alpine:3.21.2

ARG OS="linux"
ARG ARCH="amd64"

WORKDIR /app
COPY --from=builder /go/src/app/bin/driftctl_${OS}_${ARCH}/driftctl /bin/driftctl
RUN chmod +x /bin/driftctl
ENTRYPOINT ["/bin/driftctl"]
The final stage copies one compiled binary and stops there. The Dockerfile installs no additional packages in the final stage. The Alpine base includes a shell, although available diagnostic tools are limited, and this stage does not add a certificate bundle. There is no USER instruction either, so the entrypoint runs as uid 0. Neither stage sets GOOS or GOARCH, which means the OS and ARCH arguments only shape the path the binary is copied from while the target selection happens in scripts/build.sh. That layout also explains make clean, which runs rm -f bin/* without a recursive flag while the binaries sit in per target directories such as bin/driftctl_linux_amd64/.
Editorial conclusion
driftctl still answers a question nothing else in that stack does: which parts of a live account never made it back into Terraform. Treat it as a fixed snapshot rather than a dependency that grows. Before pointing it at a production account, read the Sentry initialization under sentry/ and decide for yourself what leaves the machine, confirm which build your package manager actually installed, because the newest tag is v0.40.0 from December 2023 while the default branch has moved on since, and remember that the acceptance suite creates and destroys real cloud resources behind a single environment variable. Teams that need upstream review of pull requests or help with breaking changes will not get either here, and the project itself points those users at a fork.
Frequently asked questions
How does driftctl decide what counts as drift?
It scans a cloud provider and maps resources onto IaC code, then analyzes the diffs and warns about drift and unwanted unmanaged resources. Terraform is the only IaC format named, and resources can be ignored individually. Output is offered in several formats.
Where does driftctl get installed from?
No install command appears in the repository. The README links installation to docs.driftctl.com/installation and packaging status to a Repology versions page, while build steps are deferred to .github/CONTRIBUTING.md and docs/README.md. Only the Dockerfile and .goreleaser.yml describe an artifact.
Can driftctl's test suite touch my cloud account?
Yes, through the acceptance target. It sets DRIFTCTL_ACC=true, selects tests matching TestAcc_, allows five hours of runtime, and the README's security notice states that the only code allowed to access the committed Terraform resources is the acceptance run that creates and destroys them.
What is the most recent driftctl release?
v0.40.0 dated 2023-12-01, preceded by v0.39.0 on 2023-06-06 and v0.38.2 on 2023-01-09. The default branch has taken commits since, most recently on 2026-09-21, so branch builds and tagged releases have diverged.
Which providers can driftctl inspect besides AWS?
The README names AWS, GitHub, Azure and GCP, with Terraform as the IaC format. In go.mod the Azure modules are armcompute, armnetwork, armstorage and friends at v0.2.0, GCP arrives through cloud.google.com/go/asset v1.13.0, and GitHub through go-git v5.4.2 with shurcooL/github.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/snyk-driftctl)Star history chart for your README
[](https://hysenlabs.com/projects/snyk-driftctl)Was this useful?