SoftEther VPN: one server process, eight protocol front ends
Cross-platform multi-protocol VPN software. Pull requests are welcome. The stable version is available at https://github.com/SoftEtherVPN/SoftEtherVPN_Stable.
At a glance
- What is it?
- SoftEther VPN's developer repository builds a single server binary that terminates eight VPN protocols, WireGuard included. It fits a fleet split between legacy OpenVPN clients and modern handsets, and it fails an estate that depends on IKEv2 or on server-pushed routes for anything but Windows.
- Who is it for?
- Adopt the Developer Edition when your clients span old OpenVPN builds and WireGuard handsets, and when you can live with route management that reaches Windows only. Skip it for an IKEv2 estate, for XP or SoftEther VPN 1.0 clients, and for any Linux or macOS device you expect the server to route for you.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
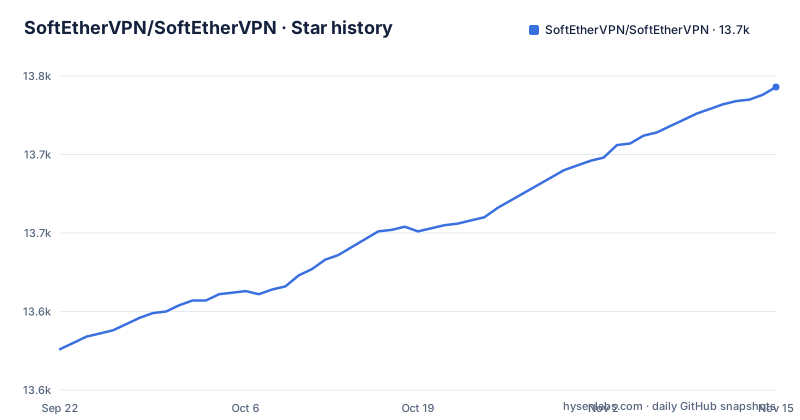
- SoftEtherVPN/SoftEtherVPN13,743 ★ · +167
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| SoftEtherVPN/SoftEtherVPN | 13.6k | 13.7k |
167 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One vpnserver process terminates eight VPN protocols
A single SoftEther VPN Server program is the whole server. The Dockerfile builds vpnserver, vpnclient and vpnbridge from one source tree, and the Dockerfile's vpnserver stage runs vpnserver execsvc, so there is no supervisor process, no per-protocol daemon and no separate management service to keep alive.
That one process terminates SSL-VPN over HTTPS, OpenVPN, IPsec, L2TP, MS-SSTP, L2TPv3 and EtherIP, and this Developer Edition adds WireGuard on top. A mixed fleet is where that pays: a site with locked-in OpenVPN clients alongside a newer WireGuard handset runs one box rather than two gateways, and the OpenVPN clone function exists for legacy OpenVPN clients. Authentication reaches the same process by password, by RADIUS or NT domain controller, or by X.509 client certificate.
One protocol is missing from both editions, and it is the only row where the comparison table marks a cross in both columns: IKEv2. If the gateway you are replacing speaks IKEv2 and nothing else, no server-side setting makes those clients connect. The change has to happen in the profile on every device instead, which is the expensive direction to move in.
The Compose file publishes 443 and 992 and leaves every other protocol commented out
docker-compose.yaml in the repository root is the shortest path to a running server, and it is worth reading before you edit it, because most of what you might want is already written down and switched off.
services:
  softether:
    image: softethervpn/vpnserver:latest
    hostname: softethervpnserver
    cap_add:
      - NET_ADMIN
    restart: always
    ports:
      #- 53:53         #DNS tunneling
      - 443:443         #Management and HTTPS tunneling
      - 992:992         #HTTPS tunneling
      #- 1194:1194/udp #OpenVPN
The image is softethervpn/vpnserver:latest, the container asks for NET_ADMIN, and restart is set to always so a crash returns without a supervisor. Only the two mappings above are active. Everything else in the ports block is commented out with its purpose in the comment: port 53 for DNS tunnelling, 1194 on UDP for OpenVPN, 5555 for HTTPS tunnelling, and 500, 4500 and 1701 on UDP for IPsec and L2TP.
That is the practical ceiling of this file. If you meant to reach the server across a network that blocks everything except DNS, the mapping exists and is disabled, so the container starts cleanly and the DNS tunnel never establishes. The same applies to an OpenVPN client you aim at 1194.
State lives in two bind mounts. ./softether_data is mounted at /var/lib/softether and ./softether_log at /var/log/softether, next to read only mounts of the host /etc/localtime and /etc/timezone so packet logs carry local timestamps. A ./adminip.txt mount is commented out as well, so that file is absent from the default deployment.
docker compose up -dThe 443 mapping is labelled management and HTTPS tunneling, which tells you the web admin console and the SSL-VPN listener share one port.
configure, make and three pinned directories build the server
The Dockerfile is a two stage build, and its builder stage is a complete description of what a source build needs.
ENV USE_MUSL=YES
ENV CMAKE_FLAGS="-DSE_PIDDIR=/run/softether -DSE_LOGDIR=/var/log/softether -DSE_DBDIR=/var/lib/softether"
RUN cd SoftEtherVPN &&\
        ./configure &&\
    make -j $(getconf _NPROCESSORS_ONLN) -C build
Those three CMake flags decide where the server keeps its pid file, its logs and its database, and they are set to match the volumes the Compose file mounts. Build dependencies are named one by one: openssl-dev, libsodium-dev, readline-dev, ncurses-dev and zlib-dev on top of build-base and cmake, with an iconv shim pulled in through LD_PRELOAD=/usr/lib/preloadable_libiconv.so. USE_MUSL=YES says the build targets Alpine's libc rather than glibc.
Reproduce those paths and the runtime image keeps only readline, openssl, libsodium, gnu-libiconv and iptables, then copies vpncmd and hamcore.se2 next to the executable along with libcedar.so and libmayaqua.so. Drop SE_DBDIR on your own machine and the server state lands wherever the default points, outside any bind mount, so a restarted container returns with an empty configuration and nothing to explain it. Each server stage runs ./vpnserver --help during the build, which means a binary that cannot start fails the image build rather than your first client connection.
AES-NI is on by default here and needs a separate library in the Stable Edition
Cryptographic acceleration is a build time difference between the two editions, not something you toggle in the console. In the Stable Edition, AES-NI requires intel_aes_lib, and that library restricts the accelerated build to x86. Here, AES-NI is enabled by default wherever the processor supports it, on x86 and on ARM. On a Raspberry Pi class host, that row alone can be the reason to build this tree rather than download the other one.
TLS server verification changes what you have to type. The Stable Edition needs the exact certificate or CA named before it will verify a server, while the Developer Edition performs standard TLS verification and uses the system CA store. Move the other way and every server you add needs its certificate spelled out by hand.
Dual-stack name resolution follows the same pattern. In the Stable Edition an IPv6 attempt happens only after IPv4 has failed, so a hostname with records in both families reaches you over IPv4 first. Here IPv6 is tried on its own terms, which changes the source address a remote access client presents and, with it, the match against any IP based access rule you wrote.
IPv6 routes are pushed to Windows clients only
Route management is the row to read twice, because both entries carry the same footnote. IPv4 route management and IPv6 route management are both Windows clients only, and IPv6 route management is also the entry the Stable Edition does not have at all.
The consequence is narrow and immediate. A server configured to push routes on connection steers traffic on Windows machines and leaves every other client alone. A Linux or macOS client takes the tunnel and then keeps whatever route table it already had, so a plan to change client egress paths from the server silently covers part of the estate and no more. You are back to per-device configuration for the other half, which is the work the central route push existed to remove.
IPv6 has a second edge in the Stable Edition: an IPv6-capable VPN tunnel is marked as supported in L2 tunnels only, so a routed IPv6 network is not covered there either. Certificate authentication has the same partial shape, supported in SSL-VPN only, and ECDSA certificates cannot be imported on that edition at all. A fleet authenticating with ECDSA client certificates cannot be served by it.
Stable Edition is the alternative, and it trades WireGuard and the system CA store for XP support
The alternative the project names itself is the Stable Edition at github.com/SoftEtherVPN/SoftEtherVPN_Stable, with source packages and binaries published at softether-download.com, and the difference is written down in two comparison tables rather than argued.
What the Stable Edition gives up: WireGuard entirely, OpenVPN AEAD mode, certificate authentication outside SSL-VPN, ECDSA certificate import, IPv6 route management, standard TLS verification against the system CA store, and dual-stack name resolution. IKEv2 is absent from both, which is the one place the choice does not matter.
What it keeps that this repository does not: running on Windows XP and earlier, and compatibility with SoftEther VPN 1.0. That is the whole decision for most sites. A network still carrying XP machines or 1.0 era clients has no alternative here, because this edition marks both as unsupported. Everywhere else the trade runs the other way, and the price of the Stable Edition is naming a certificate or CA by hand for every server you add.
Repository activity and the 5.2.5188 release
This repository is not archived, and the last push landed on 2026-10-30, so master is moving. The newest release in the list is 5.2.5188, dated 2025-07-18, and the two before it are 5.02.5187 and 5.02.5186, both from 2024-09-09. The gap between a branch that moves and a release more than a year older is what you plan around, not the branch itself.
If you need a pinned build you can audit, you are building from master yourself, which puts you on the configure and make path above instead of a downloaded package. If you want a released binary, the project points you at the Stable Edition download site, and the feature differences decide whether that is acceptable.
The licensing history sits in the tree as well. Next to LICENSE is Declaration_Switch_License_from_GPL_to_Apache.pdf, alongside DISCLAIMER.md and SECURITY.md. Vendoring this source into a product means inheriting that relicensing, so read those files before the code lands in a repository you own.
ANTIVIRUS.md is at the top level because vpnserver draws heuristic alerts
ANTIVIRUS.md sits at the root of the repository because a VPN server draws heuristic alerts from endpoint products, and it is the project's own answer to that. Read it before concluding that an alert on your own vpnserver means something got in.
The rest of the tree says what kind of build this is. Build definitions live in .ci/, .gitlab-ci.yml and .travis.yml, backing the GitLab CI, Cirrus CI and Coverity Scan badges at the top of the README, and tsan_suppressions.txt sits beside them. Windows builds get CMakeSettings.json and configure.cmd, Unix builds get configure, and vcpkg.json names the dependency set. SoftEtherVPN-iOS/ and WINDOWS_README.txt cover the two platforms that need their own instructions.
Check that list against your own estate before committing. The server runs on Windows, Linux, FreeBSD, Solaris and Mac OS X, with clients listed for Windows, Linux, Mac, Android, iPhone, iPad and Windows Phone. IKEv2 is missing on every one of them, and route management stays Windows only.
Editorial conclusion
Adopt the Developer Edition when your clients span old OpenVPN builds and WireGuard handsets, and when you can live with route management that reaches Windows only. Skip it for an IKEv2 estate, for XP or SoftEther VPN 1.0 clients, and for any Linux or macOS device you expect the server to route for you. Before deploying, settle two things: whether WireGuard and system CA store TLS verification matter more to you than XP support, which points you at the Stable Edition at SoftEtherVPN/SoftEtherVPN_Stable instead, and whether the 5.2.5188 release dated 2025-07-18 or a build from master fits your change process.
Frequently asked questions
Is SoftEther VPN safe to use?
The source is published under the Apache 2.0 license, and the repository ships ANTIVIRUS.md as its own answer to false positive detections by antivirus products. This Developer Edition also performs standard TLS verification against the system CA store, where the Stable Edition requires the exact certificate or CA to be named.
Is SoftEther free to use?
Yes, it is listed as free and open-source software. Source code packages and binary files of the Stable Edition are published at https://www.softether-download.com/.
How does SoftEther VPN work?
A single SoftEther VPN Server program terminates SSL-VPN, WireGuard, OpenVPN, IPsec, L2TP, MS-SSTP, L2TPv3 and EtherIP, so one server process serves clients speaking different protocols. Both remote-access and site-to-site tunnels can be built, with Ethernet bridging at L2 and IP routing at L3.
How to install SoftEther VPN server on Ubuntu
For a Linux server the repository ships a Dockerfile and docker-compose.yaml, which run the softethervpn/vpnserver:latest image with NET_ADMIN and publish 443 and 992. The README's installation sections cover FreeBSD, Windows, binary installers (stable channel) and building from source code.
How to use the SoftEther VPN Client Manager
The Dockerfile builds vpnclient, vpnbridge and vpnserver from a single source tree and copies vpncmd into the image, and the Dockerfile starts the server with vpnserver execsvc. The README lists configuring all settings on a GUI as an advantage.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/softethervpn-softethervpn)Star history chart for your README
[](https://hysenlabs.com/projects/softethervpn-softethervpn)Was this useful?