The image downloads its own jar at build time and strips the JDK with jlink
Official SonarQube MCP Server for code quality and security in AI agents
At a glance
- What is it?
- The SonarQube MCP Server is a Java program published as a container that most clients launch themselves. Building that image pulls two binaries from the vendor's own host, and the runtime layer installs a passwordless sudo rule for one certificate command.
- Who is it for?
- sonarqube-mcp-server suits a team that already runs SonarQube and wants an agent to read its findings and analyse snippets without a bespoke integration, and it suits both hosted and self-hosted instances because one variable switches between them. It does not suit a build pipeline that cannot reach the vendor's binary host, since the image build downloads the server itself rather than copying it in.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
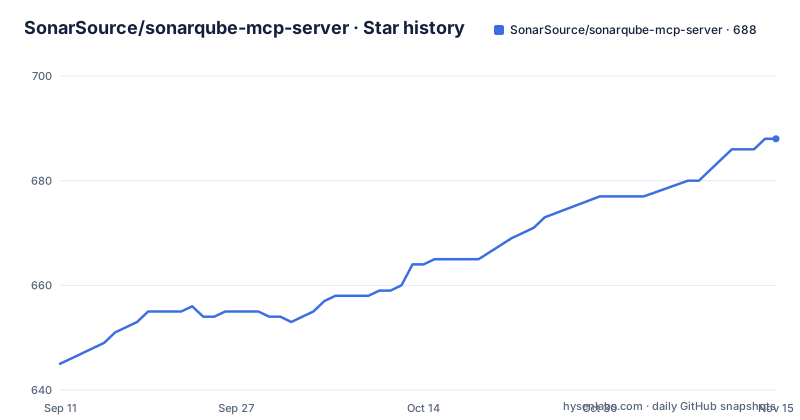
- SonarSource/sonarqube-mcp-server688 ★ · +43
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| SonarSource/sonarqube-mcp-server | 645 | 688 |
43 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The image downloads its own jar at build time
The container is not built from the source in this repository. The builder stage starts from a JDK image, installs a binutils package, and then fetches a single archive over the network, using a build argument that defaults to the current release version. The version string is four numbers long, matching the product's own scheme rather than a plain semantic version, and the default in the image matches the newest tag exactly. The readme offers a documented tension here: run the floating tag with a pull flag for automatic updates, or pin to a version tag for reproducible deployments. Both are correct, and building the image locally is a third option that pins by default, so a team can end up with a reproducible deployment of something that was fetched at build time rather than copied from a registry it controls.
A second binary is downloaded, and its version lives in two files
The build fetches a second artefact, a context-augmentation binary, and does so per architecture by mapping the build platform onto a name the download URL expects. Two architectures are accepted and anything else fails the build with an unsupported-architecture message. The version of that binary is a build argument whose default sits in the Dockerfile, and a comment immediately above it says to keep it in sync with a property of the same name in the Gradle build file. That is a version duplicated in two files with an instruction to maintain it by hand, and nothing in the build enforces it, so a release that bumps one and not the other produces an image whose augmentation tool and server disagree. Two separate downloads from one vendor host is the pattern worth naming: it is convenient and it means the build has a hard dependency on that host being reachable.
The runtime installs sudo so a non-root user can refresh certificates
The final stage is not the same base image as the builder. It is a bare Alpine release, and the builder's JDK is copied in after being reduced, so the runtime contains no compiler and no package manager leftovers beyond what it installs. That install list is short and includes a Node runtime pinned to a major version, which the visible text does not explain. It also includes the sudo tool, and then writes a sudoers entry granting the unprivileged application user passwordless permission to run exactly one command, the certificate update utility, with the file mode locked to owner-read and group-read. The user and group are created without home directories beyond what is made explicitly, and a storage directory is created and handed to them. The result is a container that runs as a normal user and has one narrowly-scoped escape hatch.
jlink reduces the runtime to the modules the server imports
The interesting build step is the one that trims the JDK. After fetching the jar, the builder runs a dependency analysis tool with the recursive and multi-release flags to compute the set of Java modules the archive actually needs, writing the result to a file, and then feeds that list into a link step that builds a custom runtime image. The link step strips debug information, man pages, and header files, and asks for level two compression. Two extra modules are added by hand, both from the cryptography provider set: the PKCS11 and elliptic-curve ones, which the analysis cannot infer from imports alone because they are reached reflectively. The net effect is a runtime containing the interpreter and exactly the modules this server loads, which is why the final image can be a bare Alpine base with no JDK package installed.
The readme has a marketing-owned section with a named escalation path
Two comment markers bracket the introduction, and between them sits a note about who may change what. It says marketing maintains that section, that wording changes require consulting a named product marketing role, and that the repository's owners review accuracy and merge the changes. That is unusual to find in a readme and useful in a specific way: it tells a contributor that a paragraph describing the product is not theirs to edit, and tells them where the request goes instead. The same markers mean a diff touching only that block is expected to come from a different queue than a diff touching the setup instructions below it, which matters when you are reading commit history to work out whether a change was a product decision or a documentation fix.
Every client example passes the token through rather than into the command
The setup section is a set of collapsed blocks, one per client, and the security guidance above them is specific. Tokens are called sensitive credentials; hardcoding them in command-line arguments is discouraged because those arguments land in shell history; environment variables are the recommended route; and for configuration files the guidance is never to commit tokens and to use variable substitution where possible. The command-line examples follow that advice, passing a variable reference into an environment flag and then handing the container only the name:
claude mcp add sonarqube
--env SONARQUBE_TOKEN=$SONAR_TOKEN
That pattern is the one worth copying. The configuration-file examples are looser, showing a literal placeholder in a JSON or TOML document, which is fine for documentation and exactly what the guidance warns against once someone fills it in for real.
Six clients, one shape, and one that has moved away
Every client block boils down to the same container invocation with the same flags: an init process so nothing is left behind, a forced pull, interactive standard input, removal on exit, and environment variables passed by name. What differs is only where the JSON or TOML lives and whether the client offers a link instead of text. One of them does. The Cursor entries are deep links that carry the whole configuration base64-encoded inside a query parameter, which is convenient for a one-click install and means your token, once filled in, travels in a URL. One entry has also left: the Gemini CLI extension is announced as having moved to a separate plugins repository, with an instruction to install it from there going forward, and this readme is the only place that is recorded. A sixth block covers an agent whose store can install the server directly and prompt for the token.
Editorial conclusion
sonarqube-mcp-server suits a team that already runs SonarQube and wants an agent to read its findings and analyse snippets without a bespoke integration, and it suits both hosted and self-hosted instances because one variable switches between them. It does not suit a build pipeline that cannot reach the vendor's binary host, since the image build downloads the server itself rather than copying it in. Before adopting it, choose between the floating tag and a pinned one deliberately, because the documented tradeoff is automatic updates against reproducibility, and read the token-handling guidance before pasting a user token into any client's configuration file.
Frequently asked questions
What is the SonarQube MCP server?
It is a Model Context Protocol server that gives an AI agent access to SonarQube Server or Cloud for code quality and security, and it can also analyse a code snippet directly inside the agent's context rather than requiring a full analysis run first.
How do I install the SonarQube MCP server?
Use the configuration generator for an agent-specific file, or run the published container image yourself. The readme suggests the floating image tag with a forced pull for automatic updates, or a version tag for reproducible deployments, and notes that any OCI-compatible runtime works.
Does the SonarQube MCP server work with a self-hosted SonarQube?
Yes. Every client has a second configuration block for SonarQube Server as well as for SonarQube Cloud, differing only in which environment variable is passed: an organisation key for the cloud, a server URL for the self-hosted case. A separate variable switches to the United States region of the cloud service.
Does the SonarQube MCP server container contain a JDK?
Not a full one. The builder stage fetches the server archive, runs a dependency analysis over it, and links a reduced runtime containing only the modules it needs, with debug information, man pages, and header files stripped. That reduced runtime is copied into a bare Alpine base for the final image.
Which agents does the SonarQube MCP server document?
Six blocks are present, including one whose extension has moved to a separate plugins repository with an instruction to install it from there. One client is configured through a link that carries the whole configuration, base64-encoded, inside a query parameter.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sonarsource-sonarqube-mcp-server)Star history chart for your README
[](https://hysenlabs.com/projects/sonarsource-sonarqube-mcp-server)Was this useful?