The DevSecOps library is a curated Markdown list with no code in it
Ultimate DevSecOps library
At a glance
- What is it?
- sottlmarek/DevSecOps collects open source security tooling into eighteen Markdown categories, from pre-commit secret checks to chaos engineering, and nothing else. It is worth an hour of reading for a team new to the field, and useless to a team that needs to pick one tool per pipeline stage.
- Who is it for?
- Read this library when you are new to DevSecOps and want the shape of the field in one sitting, and treat every row as a starting point rather than a recommendation. Do not expect it to settle a tool choice: the contribution rules forbid opinions, exclude commercial products, and require no version or license per entry.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 95 days ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
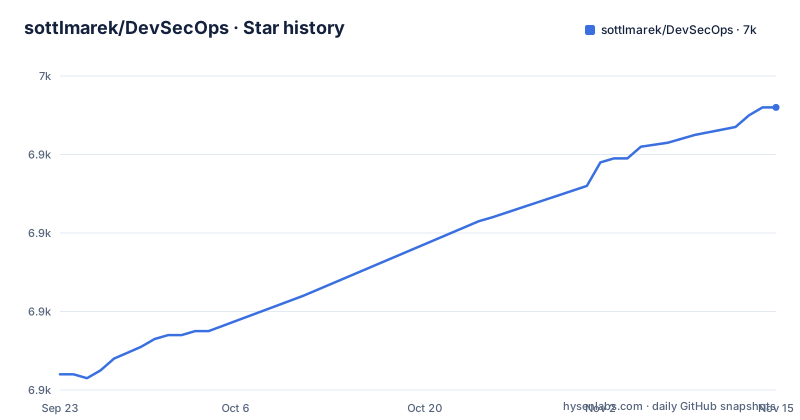
- sottlmarek/DevSecOps6,952 ★ · +68
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| sottlmarek/DevSecOps | 6.9k | 7k |
68 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One Markdown file and a LICENSE, nothing to execute
The repository holds five things at the top level: .github/, LICENSE, README.md, assets/ and devsecopsmanifesto.md. There is no package manifest, no source directory, no test suite and no build script, so there is no install step and no command to run. Its description calls it the Ultimate DevSecOps library, and the stated goal is to give engineers a guide through open source DevSecOps tooling, which is a promise about reading rather than about execution. If you want the content on disk, the only operation is a clone:
git clone https://github.com/sottlmarek/DevSecOps.gitAfter that, first use means opening README.md and jumping to a heading. There is no CLI to query, no machine readable index and no release to pin, which matters if you had hoped to feed the taxonomy into a script.
Eighteen headings decide what the list claims to cover
The table of contents is the argument. It runs through pre-commit time tools, secrets management, OSS and dependency management, supply chain specific tools, SAST, DAST, continuous deployment security, Kubernetes and containers, then gives multi-cloud three separate sections for AWS, Google cloud platform and Microsoft Azure, and finishes with policy as code, chaos engineering, infrastructure as code security, orchestration and AI. Two further sections hold methodologies, whitepapers and architecture, plus other material.
The shape of that list matters more than the count. Three headings are cloud vendor names, so the taxonomy is organised partly by supplier, while platform neutral tools sit in categories that overlap: a single scanner could sit under SAST, under supply chain or under pre-commit time tools with equal justification. The README also narrows the ambition in one sentence, saying the repository covers only cyber security in the cloud and the DevSecOps scope.
Rows carry one line of description and no version
In the pre-commit time tools section, each entry is a name, a URL and a single line of description, followed by a Meta column that stays empty on every row except the Steampipe Code Plugin, which carries a stargazers badge. No row states a version, a license, a release date or a last checked date. That is the practical limit of the format. A reader looking for inline static analysis in an editor finds DevSkim, described as a framework of IDE extensions and language analyzers providing inline security analysis, or Sonarlint, described as a Sonar linting utility for IDE, with nothing to say whether either is current.
The same section mixes secret prevention with threat modelling and gives no rule for the boundary. git-secrets from AWS labs prevents committing secrets to a repository, git-hound searches secrets in git, Yelp's detect-secrets detects secrets in a codebase, Talisman detects and prevents secrets from being checked in, and SEDATED exists to stop credentials and tokens reaching Git. Elsewhere in the same table ThreatPlaybook and threatspec are threat modelling as code, pytm is a Pythonic framework for it, Threagile is a Go framework for it, and MAL-lang is a language for building threat models in specific domains.
The contribution rules rule out paid tools and dead projects
The rules for adding an entry are the most opinionated text in the repository, and they work as a filter. A pull request must state which tool, why, its number of stars, its maturity and its topic. One tool, one topic, so no duplicates. Open source only. Active projects only. Security tools only. Fact over feelings or personal opinions. Bigger updates rather than a bare tool link. Typos as an issue rather than a pull request. A closing note calls the library an early version and asks for pull requests after the first official release.
The consequences are predictable. Commercial scanners from established vendors cannot appear at all, so a team weighing paid tooling finds nothing here. Famous but unmaintained projects are excluded by the active projects rule, which protects the list from rot and at the same time removes tools many shops still run. Stars are the one quality signal the rules ask for, and maturity is a field with no definition attached to it.
No releases and no dates, so freshness lands on the reader
The repository has no GitHub releases and no changelog file, and the last push was on 2026-08-12. Version history for the list therefore does not exist: there is no tag to diff, no dated entry telling you whether a tool was added last month or three years ago, and no record of what was removed. The README describing itself as an early version sets the expectation that sections will move between releases.
For a list whose entries are all external tools, that is the weakest point in the whole design. Nothing in the format tells you whether the project under secrets management still ships, still supports your runtime, or has been superseded by something newer. The document is cheap to read and cheap to keep, which is exactly why the verification work stays with whoever adopts a suggestion from it.
The definition section links out five times
What is DevSecOps gets a short treatment of its own: security automation, testing and enforcement during the DevOps, Release and SDLC cycles, connecting Development, Security and Operations, with security attached to every stage of the loop, named as Plan, Code, Build, Test, Release, Deploy, Operate and Monitor. After that the page stops defining and starts pointing, offering definitions by link to Red Hat, IBM, Snyk, Synopsys and Spacelift.
Handing the definition to outside sources is consistent with the rest of the project and keeps the page short. It also means the vocabulary the rest of the repository relies on is used without being pinned down. If your team disagrees about where SAST ends and supply chain analysis begins, this document will not settle the argument, because the rules forbid it from having a position.
Three gaps a reader has to close alone
The first gap is stage mapping. The categories name problem areas rather than pipeline stages, so nothing tells you which tool belongs at which point in a CI run. The second is comparison. Because opinions are excluded, two SAST tools get two rows of equal weight with no statement about overlap, so the choice is made alone. The third is money: there is no pricing or license column, and commercial products are ruled out by the contribution rules, so cost does not appear in the visible tables.
What you get in exchange is breadth and one consistent format. The categories run from the pre-commit hook to the cluster, including the three cloud vendor sections and the newer AI heading, and every row links straight to the upstream project so you can read its own documentation. The page also carries sponsorship from kvantumci and hackihub, which is worth knowing before you weigh how the curation was done.
Editorial conclusion
Read this library when you are new to DevSecOps and want the shape of the field in one sitting, and treat every row as a starting point rather than a recommendation. Do not expect it to settle a tool choice: the contribution rules forbid opinions, exclude commercial products, and require no version or license per entry. Verify each project at its own repository before adopting it, since there are no releases and no per entry dates to tell you when a listing went stale.
Frequently asked questions
What does DevSecOps mean in this library?
It is security automation, testing and enforcement across the DevOps loop, with security attached at every stage: Plan, Code, Build, Test, Release, Deploy, Operate and Monitor. The page links five outside definitions from Red Hat, IBM, Snyk, Synopsys and Spacelift instead of expanding its own.
What tools does the DevSecOps library cover?
Eighteen categories: pre-commit time tools, secrets management, OSS and dependency management, supply chain specific tools, SAST, DAST, continuous deployment security, Kubernetes, containers, multi-cloud, AWS, Google cloud platform, Microsoft Azure, policy as code, chaos engineering, infrastructure as code security, orchestration and AI.
What does the DevSecOps lifecycle look like?
The README names eight stages: Plan, Code, Build, Test, Release, Deploy, Operate and Monitor, with security applied at each one.
How does this library treat DevOps and DevSecOps differently?
It treats DevOps as the loop and DevSecOps as the same loop with security folded into each stage, connecting Development, Security and Operations during the DevOps, Release and SDLC cycles. No separate definition of plain DevOps is given.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sottlmarek-devsecops)Star history chart for your README
[](https://hysenlabs.com/projects/sottlmarek-devsecops)Was this useful?