checkup's status page cannot read from four of its seven storage backends
Distributed, lock-free, self-hosted health checks and status pages
At a glance
- What is it?
- A self-hosted health check and status page tool in Go, configured entirely from a JSON file, with seven storage backends, five checkers and a status page that supports only three of the backends. Its last release was v0.2.0 in 2017, and building it rewrites your dependency files.
- Who is it for?
- checkup suits a small operation that wants checks and a public status page without a SaaS dependency, and that is content to run the binary from a download rather than to build. It does not suit a team that needs the SQL or Azure Application Insights backends to feed the page, because the README states the page supports neither.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 11 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
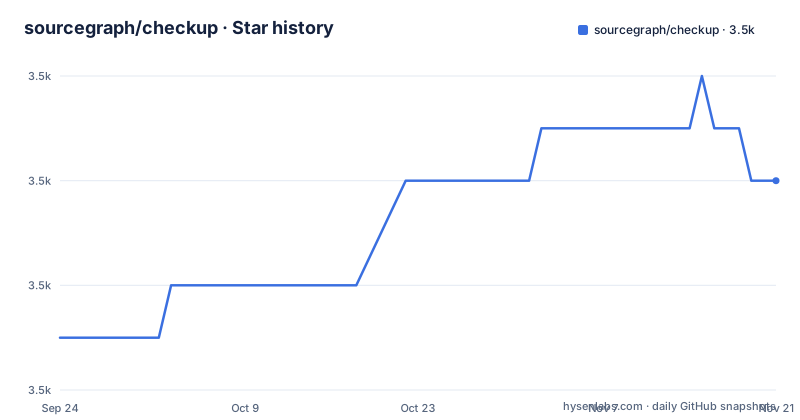
- sourcegraph/checkup3,462 ★ · +3
| Repository | 2026-09-24 | 2026-11-21 |
|---|---|---|
| sourcegraph/checkup | 3.5k | 3.5k |
3 Stars in the last 58 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The status page cannot read from four of the seven storage backends
The storage list has seven entries: Amazon S3, the local file system, GitHub, MySQL, PostgreSQL, SQLite3 and Azure Application Insights. Immediately after that list comes the caveat, and it is the most consequential line in the file: currently the status page does not support SQL or Azure Application Insights storage backends. Count them and four of the seven are ruled out for the page, leaving S3, the local file system and GitHub. So the storage backends are not interchangeable in the way the list implies. You can write results into a database, and then you cannot serve the page from them, which means a second write path or a different backend entirely. The three that do work are the three that need no database at all. That also explains the three-component model the file describes: storage holds the results, checks run against endpoints as often as you like, and the status page is hosted by you or by GitHub. For GitHub storage the page goes to a branch, with a `dir` subdirectory and a `commit_message_suffix` that defaults to `[ci skip]` so the commit does not trigger CI.
The summary names four checkers and the configuration documents five
The file announces its supported checkers in one line each: HTTP, TCP with optional TLS, DNS, and TLS. Then, further down, after those four have each been given a configuration section with a link to its documentation, there is a fifth section headed Exec Checkers. So the summary list is one short of the documented set. It is not a rounding error either, because the exec checker is the most powerful of the set and the only one that runs something. Its behaviour is specified: it can run any command, expects a zero-value exit code on success, and treats non-zero exit codes as errors. You can set `"raise":"warning"` to have a failing service counted as DEGRADED rather than as an error. Note also that TLS appears twice in the design, once as a modifier on the TCP checker and once as a checker of its own, which the summary makes clear by writing TCP with a plus-TLS note and then listing TLS separately. The security consequence of the exec checker is worth stating plainly: the command comes from the same `checkup.json` that holds your storage credentials, so whoever can write that file chooses what the checker executes.
Four checkers use endpoint_name and the exec checker uses name
Compare the five configuration samples and the field naming is inconsistent in a way that costs you a debugging session. The HTTP sample has `type`, `endpoint_name` and `endpoint_url`. The TCP sample has `type`, `endpoint_name` and `endpoint_url`. The DNS sample adds `hostname_fqdn` alongside those two. The TLS sample matches the TCP one. Then the exec sample uses `name` rather than `endpoint_name`, and has no `endpoint_url` at all:
{
    "type": "exec",
    "name": "Example Exec Check",
    "command": "testdata/exec.sh"
}
So a config assembled by copying the HTTP sample and then adding an exec check from its own sample ends up with two different label fields in the same file. That is not fatal, since the two live in different checker types, but the file gives no indication that the difference is intentional. The samples also share a convention worth copying: each carries only the required fields, and the file says so twice, once asking you to refer to the documentation for a full description of each checker, storage type and notifier and once saying only required fields are shown. The top-level shape is a JSON object with `checkers`, `storage` and `notifiers`, and the file name and location are fixed by convention rather than by an option, since you are told to save it as `checkup.json` in your working directory.
make build runs go mod tidy, so building rewrites your dependencies
The build target has a dependency that is easy to miss. `build` depends on `fmt`, and `fmt` does two things: it creates the output directory and then runs `go fmt ./...` followed by `go mod tidy`. So building the project is not a read-only operation. `go mod tidy` rewrites `go.mod` and `go.sum`, resolving and pruning the dependency list, which means a plain `make` can produce a diff in your dependency files even when no source changed. The default target is `all: build test`, so the ordinary invocation does both. The actual compile step is `go build -o builds/ ./cmd/...`, and there is a pattern rule for tags: `build-%` sets `TAG` from the pattern and builds with `-tags $(TAG)`. That is how `make build-sqlite3` works, and the README recommends exactly two forms, `make build` for mysql and postgresql support and `make build-sqlite3` for additional sqlite3 support. The binary lands at `builds/checkup`. Tests run with the race detector and no caching, as `go test -race -count=1 ./...`, and there is a matching `test-%` rule for tags.
Three different Go versions are stated in one repository
Line up the three places a Go version appears and no two agree. The install section says you will need Go 1.8 or newer. The module file says `go 1.13`. The container build starts from a `golang:1.14-alpine` base image. That is three floors and a builder for the same code, and it is the kind of drift that tells you the documentation and the build were last touched at different times by different people. The install instruction has the same vintage problem in a different way. It offers to install from source with `go get -u github.com/sourcegraph/checkup/cmd/checkup`, which is the pre-modules idiom for fetching and building a command; modern Go uses `go install` for that and has retired the `go get` form. The README's preferred route is actually the download: it points at the releases page for the latest build for your platform and tells you to put the binary in your `PATH`, then verify with `checkup --help`. Taking that route sidesteps both the version mismatch and the module tooling entirely.
CGO is disabled in the image, so sqlite3 storage is absent from the container
The Dockerfile is two stages and one environment variable does most of the work. The builder is `golang:1.14-alpine` with `CGO_ENABLED=0` set, the source is copied in, `make` is installed from the Alpine repositories and `make build` is run. The runtime stage is `alpine:latest`, it copies only the finished binary to `/usr/local/bin/checkup`, adds the `statuspage/` directory, switches to `USER nobody`, exposes port 3000 and runs `checkup serve` by default. The consequence of disabling cgo is not stated anywhere in the file but follows from the dependency list. `mattn/go-sqlite3` is a cgo package, so a binary built with `CGO_ENABLED=0` cannot use it. Since the plain `make build` that the Dockerfile calls carries no build tag, the container image has no sqlite3 storage support at all, even though sqlite3 appears in the storage list and `make build-sqlite3` exists precisely to add it. That is a gap between what the documentation offers and what the image contains, and it is invisible until a config asks for sqlite3. The `USER nobody` line is the opposite kind of decision: the process runs unprivileged, which matters for a tool whose exec checker can run arbitrary commands.
Compose publishes a random host port and expects an image you built
The compose file is short and has two details that will cost you an hour if you assume otherwise. The service is named `checkup`, sets `hostname: checkup`, and its image is `checkup:latest`, a bare local name with no registry host. Compose does not build it, so the file only works after you have run the project's own `docker` target, which is `docker build --no-cache . -t $(DOCKER_IMAGE)` with the image name defined once at the top of the Makefile. Second, the port mapping is `- 3000` with no host side, which tells Docker to assign a random port on the host every time you start it. So the status page URL is not fixed by the compose file and you have to read it back from `docker ps` each run. The volumes are where the configuration enters: `./checkup.json` is mounted at `/app/checkup.json`, matching the convention that the config lives in your working directory, and `./checks` is mounted at `/app/checks`, a directory the README never mentions and which is presumably where checker scripts like the exec check's `testdata/exec.sh` are expected to live. The restart policy is `always`, so a misconfigured container will restart in a loop rather than stay down.
The GitHub storage setup list stops partway through its third step
The GitHub storage section is the most fully specified backend in the file, and then its setup instructions break off. The configuration is eight fields: `type`, an access token described as needing repo scope, the repository owner and name, a committer name and email, a branch defaulting to `gh-pages`, a `dir` subdirectory, and a `commit_message_suffix` documented as appended to each commit message, defaulting to `[ci skip]` and removable by setting it to a single space. Two annotations explain the first and last of those: the directory is where inside the repository the check files are pushed, and the suffix exists so the commits do not re-trigger CI. Then the setup instructions begin. Step one is to create a repository. Step two is to copy the contents of `statuspage/` from this repository to the root of the new one. Step three begins, to update the URL in `co`, and the file ends there. So the one backend that can host the status page on GitHub Pages is documented down to the branch and the commit suffix and then stops mid-word on the step that configures the URL. Read the remaining instructions from the repository itself.
Editorial conclusion
checkup suits a small operation that wants checks and a public status page without a SaaS dependency, and that is content to run the binary from a download rather than to build. It does not suit a team that needs the SQL or Azure Application Insights backends to feed the page, because the README states the page supports neither. Before adopting, decide which backend you will actually read the page from, since that choice constrains where results can be written, and note that `make build` depends on a target that runs `go mod tidy`, so a build edits go.mod and go.sum. The README calls the tool a work-in-progress; the last release is v0.2.0 from 2017-07-28 and the last push was on 2026-09-16.
Frequently asked questions
What is sourcegraph/checkup?
A self-hosted health check and status page tool written in Go, described as distributed and lock-free, created by Matt Holt and maintained and sponsored by Sourcegraph. You configure it entirely from a JSON file named checkup.json, and it has three components: storage for results, checks run against endpoints as often as you like, and a status page that you or GitHub host.
Which checkers does checkup support?
HTTP, TCP with optional TLS, DNS and TLS, plus an exec checker that runs a command and treats a zero exit code as success. Non-zero exits count as errors unless you set `"raise":"warning"`, which marks the service DEGRADED instead. The command comes from the same checkup.json that holds your storage credentials.
Where can checkup store its results?
Amazon S3, the local file system, GitHub, MySQL, PostgreSQL, SQLite3 and Azure Application Insights. The README notes that the status page currently supports neither the SQL backends nor Azure Application Insights, which leaves three of the seven able to feed the page.
How do I build checkup?
Run `make build`, which writes the binary to builds/checkup, or `make build-sqlite3` for additional sqlite3 support. The README's install-from-source line is `go get -u github.com/sourcegraph/checkup/cmd/checkup`, and its preferred route is to download a release for your platform and put it in your PATH.
Is checkup still maintained?
The README calls it a work-in-progress and asks readers to use it with discretion and report bugs. The releases are v0.2.0 dated 2017-07-28 and an initial v0.1.0 dated 2016-08-03, while the last push to the repository was on 2026-09-16.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sourcegraph-checkup)Star history chart for your README
[](https://hysenlabs.com/projects/sourcegraph-checkup)Was this useful?