Sparrow's per-service yarn commands do not match its scripts
Your next-gen API testing and development tool.
At a glance
- What is it?
- Sparrow is a Svelte and Tauri API client that needs Node, Yarn, Rust and optionally Docker to run, with Mongo, an API server, an auth server, a proxy and a web app behind it. The install path is well documented and contains a mismatch: the individual service commands named in the README are not the scripts the manifest defines.
- Who is it for?
- Use Sparrow if you need an API client that runs as a desktop app through Tauri or in the browser, and plan on the Docker path since the alternative sends you to three separate repositories. Check four things first.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 165 days ago.
- What is it written in?
- Mainly Svelte, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
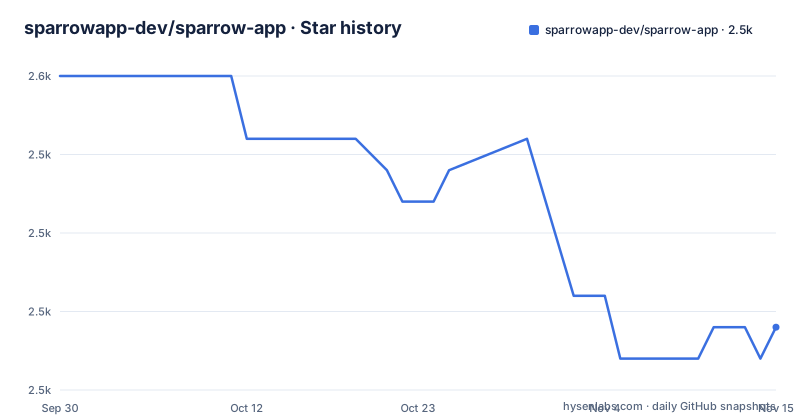
- sparrowapp-dev/sparrow-app2,542 ★ · -8
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| sparrowapp-dev/sparrow-app | 2.6k | 2.5k |
-8 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The README names four service commands that are not in the manifest
The Docker method is presented as one aggregate command plus a set of per-service commands. The aggregate is `yarn docker:up`. The per-service ones are documented as `yarn docker:<SERVICE NAME>`, then spelled out: `yarn docker:mongo`, `yarn docker:sparrow-api`, `yarn docker:sparrow-auth` and `yarn docker:sparrow-proxy`.
None of those four names is a script in `package.json`. The manifest defines this set instead:
"docker:up": "docker compose --env-file .env.docker-setup build --no-cache && docker compose --env-file .env.docker-setup up -d --force-recreate",
"docker:down": "docker compose --env-file .env.docker-setup down -v",
"docker:up:mongo": "docker compose build mongo --no-cache && docker compose up mongo -d",
"docker:up:api": "docker compose build sparrow-api --no-cache && docker compose up sparrow-api -d",
"docker:up:auth": "docker compose build sparrow-auth --no-cache && docker compose up sparrow-auth -d",
"docker:up:proxy": "docker compose build sparrow-proxy --no-cache && docker compose up sparrow-proxy -d",
So the working names are `docker:up:mongo`, `docker:up:api`, `docker:up:auth` and `docker:up:proxy`. The pattern in the scripts is `docker:up:` followed by the compose service name, not `docker:` followed by the service name.
Every image defaults to latest and every build discards its cache
Each service in the compose file takes its image tag from an environment variable with a fallback, and the fallback is `latest`:
  sparrow-api:
    image: sparrowapi/sparrow-api:${SPARROW_API_VERSION:-latest}
The same pattern applies to the auth, proxy, web and admin images. Nothing in the repository pins a default version, so a fresh checkout resolves to whatever is current for each image at the moment you build.
The scripts then compile on top of that. `docker:up` runs a build with `--no-cache` and follows it with `up -d --force-recreate`, so nothing is reused and nothing survives. The per-service scripts also pass `--no-cache`. A second difference between the two groups: the aggregate command passes `--env-file .env.docker-setup` to both compose invocations, while the per-service scripts pass no env file at all and rely on compose finding the configuration in the project directory.
That combination, floating tags plus no layer cache, means a rebuild is never guaranteed to produce the images you tested before.
The default login is printed in the README
There is a section headed Default User for Login. Sparrow creates a default user to help you get started quickly and easily, and the credentials are given in full: the email `[email protected]` and the password `12345678@`.
The intent is convenience for a local development machine, and in that context it is harmless. The problem is what happens when the same compose file is used on a machine that other people can reach. The auth service publishes host port 1421 to container port 80, the API server publishes 9000, Mongo publishes 27017, and none of those mappings is limited to a loopback address, so the stack is listening on every interface the host has by default.
The environment file is where the auth configuration is expected to come from, and it is the file to review before the stack leaves your laptop. The self-hosting guide is a separate document in `docs/`.
Nothing in the README tells you to change this account, so that step is on you.
Six services in the compose file, five named in the README
The Docker method is described as installing all services, Mongo plus API server plus auth server plus proxy server, and starting the web app on port 1422. The compose file has six services. The sixth is `sparrow-admin`, and it has a script of its own, `docker:up:admin`, alongside a port mapping of 5173 to 80.
The service list in the README therefore undercounts what the stack actually starts. Anything that reaches for the admin service will find it running, and anyone auditing the deployment from the README will not have counted it.
The port map is worth reading in full, because the compose file publishes every one of them without a host prefix: Mongo on 27017, the API server on 9000, the auth server on 1421 to container port 80, the proxy on 3000, the web app on 1422 to 80, and the admin service on 5173 to 80. All six services join a single bridge network named localnet. Mongo also stands out for having no dependency on anything, since it is the base of the chain that api, auth, web and admin all declare.
Nine workspaces, and the only desktop build produces a debug binary
The manifest is private, typed as an ES module, and declares nine Yarn workspaces: three applications, `@sparrow-web`, `@sparrow-desktop` and `@sparrow-storybook`, and six shared packages, `@sparrow-library`, `@sparrow-common`, `@sparrow-teams`, `@sparrow-workspaces`, `@sparrow-support` and `@sparrow-marketplace`. The Storybook workspace and the `Storybook.Dockerfile` at the root are the component workshop, which is why it ships as its own container.
The run scripts are thin wrappers. `desktop-start` invokes `tauri dev` in the desktop workspace and `web-start` invokes `dev` in the web workspace, so the framework, Tauri, drives the local desktop build and Vite drives the web one.
The build scripts are where the naming gets interesting. `desktop-build` runs `tauri build --debug`, and `desktop-build-intel-mac` runs the same build against the `x86_64-apple-darwin` target with `--debug` as well. There is no release build script in this part of the manifest, so anything built from these two commands is a debug artifact, and the Intel Mac variant exists because the host build is not assumed to be Intel.
The non-Docker path is three other repositories and their own READMEs
Method 2 skips containers entirely and sends you to three separate repositories to set up the backend: Sparrow API, Sparrow Auth and Sparrow Proxy, each with its own README to follow. One convenience is noted, that the Mongo DB setup is already included in the Sparrow API setup, so the database is one repository fewer.
Either way, the required steps are the same and they are short: clone the repository, move into the project root, run `yarn` to install dependencies and Husky hooks, then copy two environment templates into place.
# Copy desktop app .env.example to .env
cp apps/@sparrow-desktop/.env.example apps/@sparrow-desktop/.env

# Copy web app .env.example to .env
cp apps/@sparrow-web/.env.example apps/@sparrow-web/.env
There are two applications and therefore two environment files, and the desktop one is what Tauri reads while the web one is what the browser build reads. The variable reference lives in `docs/ENVIRONMENT_VARIABLE_GUIDE.md`, and a separate `.env.docker-setup` file at the root feeds every compose service.
One detail in the prerequisites list is easy to miss: the Tauri link points at the version 1 getting started guide, while the desktop scripts invoke the version 2 command interface.
Distribution is three Dockerfiles, an nginx directory and a snap template
The root of the repository carries three Dockerfiles, which tells you there are three deployable shapes rather than one. `Sparrow-Web.Dockerfile` builds the web app. `SelfHost-Sparrow-Web.Dockerfile` builds the self-hosted variant. `Storybook.Dockerfile` builds the component workshop. Beside them are `nginx/`, which is the web server configuration for serving the built app, and `docker-entrypoint.d/`, which holds entrypoint scripts for the images.
There is a `snapcraft.yaml.in` for the Snap packaging format. The `.in` suffix means the file is a template that something fills in at build time, so the Snap metadata is not fixed in the repository but derived during packaging. A `funding.json` declares the funding platforms, and a `.well-known/` directory sits in the root, which is where domain verification files usually live.
The tooling around that is conventional: a `.husky/` directory for the git hooks that `yarn` installs, a `.prettierignore`, a committed `yarn.lock`, a `CHANGELOG.md`, and a `.vscode/` directory with the recommended extensions being VS Code with the Svelte, Tauri and rust-analyzer extensions.
Editorial conclusion
Use Sparrow if you need an API client that runs as a desktop app through Tauri or in the browser, and plan on the Docker path since the alternative sends you to three separate repositories. Check four things first. The individual service commands in the README are named differently from the scripts that exist, so use `docker:up` and the compose file rather than the documented per-service names. The published login is a real credential pair in the README, so change it or restrict the service before anyone else can reach it. Every service image defaults to the `latest` tag and every build runs with `--no-cache`, so a rebuild is never the build you tested. And `docker:down` carries `-v`, which removes the volumes with the containers.
Frequently asked questions
How do I set up and run the Sparrow app locally?
Check that Node, Yarn and Rust are installed with node -v, yarn check and rustc --version, plus Docker if you want the container path. Then clone the repository, run yarn to install dependencies and Husky hooks, copy the desktop and web .env.example files to .env, start the services with yarn docker:up, and launch the app with yarn desktop-start or the web app with yarn web-start.
What are the default Sparrow login credentials?
Sparrow creates a default user to help you get started quickly and easily. The email is [email protected] and the password is 12345678@, both printed in the README.
Which services does the Sparrow Docker method start?
Mongo, the API server, the auth server and the proxy server as containers, plus the web app on port 1422. The compose file also defines a sparrow-admin service on port 5173 with its own docker:up:admin script, and that service is not named in the README's list.
Does yarn docker:down delete the Sparrow database?
The script runs docker compose --env-file .env.docker-setup down -v, and the -v flag removes named volumes along with the containers and the network, so anything stored in a volume goes with it.
Where are the Sparrow environment variables documented?
The README points at docs/ENVIRONMENT_VARIABLE_GUIDE.md for the variables you can customize in .env. Separately, .env.docker-setup at the repository root is the file passed to every compose service through env_file.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sparrowapp-dev-sparrow-app)Star history chart for your README
[](https://hysenlabs.com/projects/sparrowapp-dev-sparrow-app)Was this useful?