spectre-meltdown-checker: four columns of who can read whom
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD
At a glance
- What is it?
- A self-contained shell script that reports whether transient execution CVEs can reach across your userland, your kernel, and your hypervisor boundaries. Its ARM64 entries carry placeholder CVE identifiers, and the Docker route runs privileged with no network.
- Who is it for?
- Take this checker if you want a single command that tells you which transient execution issues apply to the boundaries you actually care about, rather than a list of CVEs to interpret yourself. Check three things before you trust its output as a security posture.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
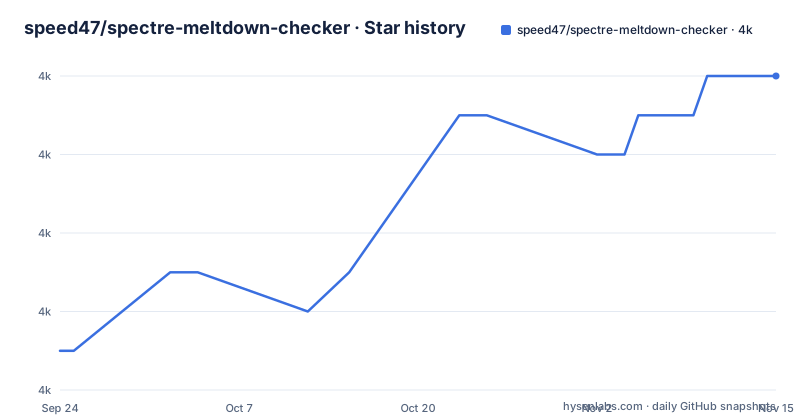
- speed47/spectre-meltdown-checker3,958 ★ · +7
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| speed47/spectre-meltdown-checker | 4k | 4k |
7 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Risk is reported per boundary, not per CVE
The table that makes this project useful is not the CVE list, it is the matrix titled as answering whether an attacker in a given position can extract data from a given target. It has four columns: userland reaching the kernel, userland reaching userland, a virtual machine reaching the host, and one virtual machine reaching another. Each cell is a marker rather than prose, with a burst for vulnerable, a check for not affected, and a skull for the cases where the answer is different again, plus numbered footnotes for the partial cases. The page also makes an important scoping point that most summaries of these bugs skip: the userland to kernel column applies inside a virtual machine too, comparing guest userland against guest kernel, because the same processor mechanisms are at play regardless of virtualization. So one row of the table answers two different questions depending on where you are, which is why the four columns rather than a single yes or no.
Mitigations are per-CVE and some have an escape hatch
The last column of the matrix is the remediation guidance, and it varies enough to be worth reading rather than skimming. The oldest entry, the bounds check bypass, is answered by recompiling everything with an instruction fence inserted, which is a build-level answer rather than a kernel one. The branch target injection row asks for a microcode and kernel update, with a retpoline alternative named in parentheses. Meltdown and the rogue system register read ask for a kernel update or a microcode update respectively, because one is a page table permission problem and the other is a cache side channel. The store buffer bypass row inverts the pattern, being safe against the kernel but not against userland, and the mitigation is microcode plus kernel update. The machine check exception on page size change row is the one whose mitigation is a hypervisor update or disabling huge pages, and the Foreshadow variant targeting virtual machines asks for a kernel update or disabling exposed page tables and simultaneous multithreading. So the guidance is genuinely per-issue rather than a single switch, which is the whole reason to run a checker instead of reading one advisory.
These are summaries of a checker table, not universal remediation instructions. Affected hardware, microcode, kernel, hypervisor and configuration determine the applicable mitigation; consult current vendor and operating-system advisories and validate the resulting status.
Three x86 issues newer than Meltdown, and one still listed as Spectre
The CVE table runs from the 2017 numbers through to the present and shows how the naming has fragmented. The originals are Bounds Check Bypass as Spectre V1, Branch Target Injection as Spectre V2, and Rogue Data Cache Load as Meltdown, followed by a variant 3a for the rogue system register read. Three 2018 entries share the L1 terminal fault description under different identifiers, one for SGX enclaves, one for the operating system and system management mode, and one for the virtual machine monitor, and they are treated as three separate rows because the mitigations differ by layer. The store buffer bypass is listed with an alias that includes its number. Then the microarchitectural data sampling family arrives in three identifiers for store buffer, load port, and fill buffer sampling, each carrying two popular names between them. The alias column is where the fragmentation is most visible, since the same bug is called several different things in different advisories, and one identifier covers both RIDL names while another covers both ZombieLoad names.
ARM64 rows have no CVE and carry placeholder identifiers
The end of the table handles a different architecture and does it differently, and this is the part of the project that will confuse a scanner. Three ARM64 silicon errata that the kernel actively works around are listed, tracked only by the processor vendor's erratum numbers, and the page says explicitly that they have no assigned CVE. What they are instead is worth reading: speculative address translation lookaside buffer corruption across several errata numbers affecting a range of Cortex cores, speculative unprivileged load on two core types, and a model-specific register feature not being self-synchronizing, which lists a long set of Cortex, X, and Neoverse cores. They are selected with a dedicated errata flag or with the associated variant mnemonic rather than by number. The identifiers in the first column are of the form where the year and sequence are literal zeroes and a one, which is a placeholder pattern rather than a real assigned identifier, so these rows cannot be cross-referenced against a CVE database and should not be treated as if they could.
The Docker route is privileged with the network switched off
The container definition is short and each line is a consequence of what the script needs to inspect. It builds from an Alpine base and installs a list of utilities the script actually calls: kernel module tools, binary utilities, grep and perl, a compression set spanning zstd, gzip, xz, bzip2 and lz4, wget, shar, unzip, sqlite, procps, and coreutils. The single script is copied to the root of the image and is the entrypoint. The supplied compose configuration sets privileged mode and disables networking. Other execution methods or reduced privileges may be possible, with some checks limited; consult the tool's documentation for the target host. Three host paths are mounted read only: the boot directory, the CPU device directory, and the loaded modules directory. Read-only mounts and network isolation reduce some exposure, but a privileged container has broad host access. Review the script and execution method before running it, especially on a production host.
One file, one screen of text
The repository is unusually small and that is the design. There is the script itself at the root, the readme, a documentation directory, the container definition and its compose file, and the automation directory. No library, no package manifest for installation as a dependency, no test suite, and no language-specific project files: the primary language recorded for the repository is shell, which is consistent with a tool whose whole value proposition is that you can read it before running it and copy it onto a machine with nothing installed. That property is also why the project works on the BSD systems named in its description, since there is nothing to build and nothing to resolve. The cost of the single-file approach is that every check and every mitigation string lives in one document, so a reader who wants to know why a particular cell says what it says has to read the script rather than a module.
Release numbers are dates, and the branch moved after the last tag
The three most recent tags are named in a way that makes the cadence obvious: a year, a week-like number, and a build counter. They are dated 2026-04-20, 2026-06-02, and 2026-09-13, so releases land every few weeks rather than on a semver schedule, which fits a tool whose content is a table that grows when a processor advisory is published. The default branch was last pushed on 2026-09-26, which is after the newest tag, so the current state of the script is ahead of the newest release in this sense. There is no separate licence statement recorded for the repository, which is worth resolving before you redistribute the script inside an image or a configuration management repository, since the rest of the page is otherwise explicit about what it checks and what to do about it.
Editorial conclusion
Take this checker if you want a single command that tells you which transient execution issues apply to the boundaries you actually care about, rather than a list of CVEs to interpret yourself. Check three things before you trust its output as a security posture. It reports the state of the running kernel and microcode, so a machine that has not rebooted after an update will still report the old state. The ARM64 rows are tracked by processor erratum numbers rather than assigned CVEs and carry placeholder identifiers, so do not paste those identifiers into a scanner expecting real ones. And the containerised route is privileged with networking disabled and three host paths mounted read-only, which is the right shape for a tool that reads hardware state, but it is still a privileged container and worth running deliberately.
Frequently asked questions
Are Spectre and Meltdown fixed?
That depends on the boundary you mean, which is why the project reports four columns rather than one answer. The original bounds check bypass row is vulnerable in every column with a recompile-with-fence mitigation, Meltdown is vulnerable only from userland to kernel and fixed by a kernel update, and the newer store and data sampling rows each name a microcode plus kernel update.
How to disable Spectre Meltdown?
The mitigation is listed per CVE rather than as one switch. The table names recompiling everything with a fence, microcode plus kernel updates, retpoline as an alternative, a hypervisor update or disabling huge pages, and disabling exposed page tables and simultaneous multithreading for the virtual machine case.
What operating systems does spectre-meltdown-checker support?
Linux and BSD. The tool is a self-contained shell script with no build step, which is why the same file works across both rather than needing per-distribution packages.
How does spectre-meltdown-checker handle ARM64 processors?
It tracks three ARM64 errata that the kernel works around, selected with an errata flag or a variant mnemonic rather than a CVE number, because they have no assigned CVE. Their identifiers in the table are placeholders and cannot be looked up in a vulnerability database.
Does the spectre-meltdown-checker Docker image need privileges?
Yes, the compose file sets privileged mode and mounts the boot directory, the processor device directory, and the loaded modules directory read only. It also sets the network mode to none, so the container cannot reach the network while it runs.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/speed47-spectre-meltdown-checker)Star history chart for your README
[](https://hysenlabs.com/projects/speed47-spectre-meltdown-checker)Was this useful?