CASL turns permissions into four parameters, inverted rules, and one shared ability
CASL is an isomorphic authorization JavaScript library which restricts what resources a given user is allowed to access
At a glance
- What is it?
- CASL is an isomorphic TypeScript authorization library. Its ability model is small: an action, a subject, conditions, and optional fields, written as regular and inverted rules and reused across UI components, API services, and database queries. The details worth checking first are the MongoDB operator syntax in conditions, the different Node.js floors across its six packages, and where questions actually get answered.
- Who is it for?
- CASL fits a TypeScript codebase that wants one set of rules reused by the interface, the API layer, and its ORM queries, and that is comfortable writing conditions with MongoDB operator syntax. It does not fit a team that wants its rules expressed in SQL style predicates, or that expects its questions answered in the issue tracker.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
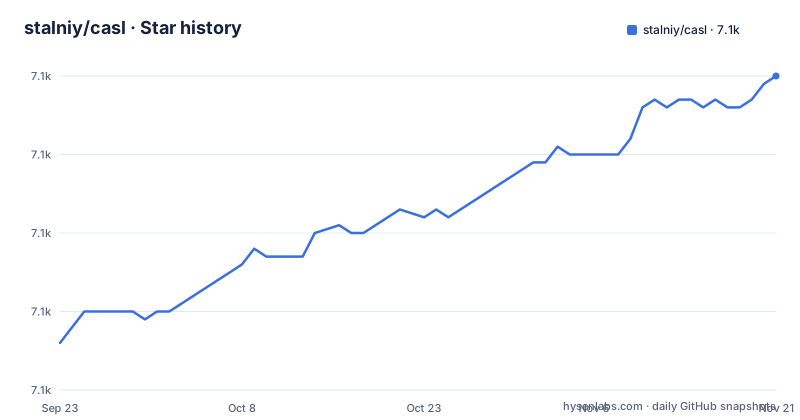
- stalniy/casl7,120 ★ · +34
| Repository | 2026-09-23 | 2026-11-21 |
|---|---|---|
| stalniy/casl | 7.1k | 7.1k |
34 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Four parameters decide every check, and three of them are optional
CASL operates at the abilities level, meaning what a user can actually do in the application, and an ability is built from four parameters. The first is the user action, a word that is usually a verb and depends on your own business logic, with prolong and read given as examples, and create, read, update, and delete named as the CRUD words that turn up often. The second is the subject, normally a business or domain entity name such as Subscription, BlogPost, or User. The third is conditions, an object or a function that restricts the action to matched subjects, which is how a user gets to update and delete their own BlogPost and not somebody else's. The fourth is fields, which narrows an action to named properties of the subject, letting a moderator update the hidden field of a BlogPost while leaving description and title alone. Only the action and subject are required. The optional three are what let the same shape carry both a blunt rule that reads everything and a narrow one that touches a single field.
manage is a wildcard, and the action words are yours to invent
The action vocabulary belongs to your domain, which is the first surprise for anyone arriving with a role list in hand. Actions are words that depend on business logic, so read and prolong are both legitimate, and nothing pushes you to stay inside CRUD. Above those sits manage, which in the blog example stands for doing anything to a subject, written as can('manage', 'BlogPost', { author: user.id }) to grant every operation on posts the user authored. Because manage already covers the widest case, conditions do the narrowing, and the same four parameters then express a blanket read, ownership scoped writes, and a single field for a single role. Rules come in two forms, regular and inverted, and the inverted form is how the blog example states the one thing a visitor must not do: delete a post created more than a day ago. Exceptions are therefore first class rather than bolted on. The subject can also be a class instead of a string, so can('read', BlogPost) works as well as can('read', 'BlogPost').
The crash course builds rules with createMongoAbility
The example defines the ability with an AbilityBuilder wrapping createMongoAbility, and the note beside it says that MongoDB operators can be used to define conditions while telling readers not to worry if they do not know MongoDB, since it is not required. The packages are published on npm under the @casl scope with @casl/ability as the core, and the documentation lives at casl.js.org. Here is the shape of the definition, taken from the crash course:
import { AbilityBuilder, createMongoAbility } from '@casl/ability'
import { User } from '../models'; // application specific interfaces

function defineAbilitiesFor(user: User) {
  const { can, cannot, build } = new AbilityBuilder(createMongoAbility);

  // can read blog posts
  can('read', 'BlogPost');
  // can manage (i.e., do anything) own posts
  can('manage', 'BlogPost', { author: user.id });
Note what conditions really are here: an object, in which the README says some MongoDB operators can be used. That is convenient for anyone already fluent in matchers, and a translation layer for everyone else, whose reflex will be SQL style predicates the library does not parse. Conditions may equally be a function, which is the escape hatch when a matcher cannot express the rule.
Six packages, and the core reaches runtimes the integrations do not
The ecosystem table is the part to read first if your runtime is pinned, because the six packages do not share a floor. @casl/ability is the core and lists Node.js 18+ with browsers IE 11+, noted as using Map and Set. @casl/mongoose lists Node.js 20 for Mongoose. @casl/prisma, @casl/angular, @casl/react, and @casl/vue each list Node.js 20+, so every integration has already moved past the core. Browser support splits as well: Angular and React keep IE 11 in their supported environments, while Vue asks for browsers with Symbol support. The consequence is concrete. A service on Node.js 18 can install the core today and cannot install the ORM or framework integrations without a runtime upgrade first, and an old browser target narrows your choice of UI package down to the two that still claim IE 11. A feature list will not tell you any of this. If you are weighing packages by what they do rather than by what they need, that table is the deciding evidence.
Declarative rules exist so they can travel between tiers
The word declarative is doing real work in the design. Rules are described as data rather than scattered checks, and the stated payoff is that you can serialize and share permissions between UI and API or microservices, with the library built to manage and share permissions across UI components, API services, and database queries. Isomorphic means the same rules run on the frontend and the backend, so a component can hide a control the user has no right to press while the API layer and the ORM query enforce that same rule where it counts. Being serializable also means an ability can travel to the client alongside a response, so the interface learns what to render instead of guessing. What that story leaves open is the lifecycle of the shared copy. Check how a stale ability sitting in a browser gets corrected after the server changes a rule.
The issue tracker takes bug reports and closes questions
If you get stuck, the repository is explicit about where not to ask. The issue list is stated to be exclusively for bug reports and feature requests, and questions posted there may be closed immediately without answers. The sanctioned routes are a support chat and a Stack Overflow tag for casl. For a user that is a real constraint on where prior answers live: the tracker holding the project's issues is deliberately closed to questions, so the searchable history sits somewhere else, and per package troubleshooting is not something you will find in an issue thread, since the people answering there are handling defects rather than usage. The same policy cuts the other way for contributors, because a question phrased as a bug report can disappear without a reply.
A pnpm monorepo whose prepare step runs a binary
The build shape is a workspace rather than a single package. The root package.json is named casl-monorepo, marked private, versioned 0.0.0, and carries two scripts only: one that builds the documentation by changing into docs-src with NODE_ENV set to production, and a prepare step that changes into packages/dx and runs bin/dx.js install. Because prepare runs on install, that command fires by itself when the repository root is installed, which is worth knowing before someone wonders why a binary executed during setup. The tree matches that layout: pnpm-workspace.yaml and pnpm-lock.yaml at the root, packages/ holding the six published packages, docs-src/ holding the documentation site, plus git-hooks/, BACKERS.md, CONTRIBUTING.md, and a pair of release-please configuration files with their manifests. Releases ship per package instead of for the repository as a whole: the newest listed are @casl/ability 5.4.6, 5.4.7 and 5.4.8, all dated 2026-10-31, the same day as the last push to master.
Editorial conclusion
CASL fits a TypeScript codebase that wants one set of rules reused by the interface, the API layer, and its ORM queries, and that is comfortable writing conditions with MongoDB operator syntax. It does not fit a team that wants its rules expressed in SQL style predicates, or that expects its questions answered in the issue tracker. Before adopting, check the Node.js floor of the integration package you want against the runtime you already run, and decide yourself how a serialized ability on the client gets corrected when the server changes.
Frequently asked questions
What does CASL stand for?
The repository gives a pronunciation rather than a backronym: CASL is pronounced like castle, written in the overview as a phonetic spelling.
What is the CASL code?
It lives in a pnpm workspace monorepo named casl-monorepo, marked private with version 0.0.0. The packages/ directory holds the six published packages, docs-src/ holds the documentation site, and the root has only a docs build script and a prepare step.
Which Node.js version does the CASL core package need?
The core @casl/ability package lists Node.js 18+ and browsers IE 11+ using Map and Set. @casl/mongoose lists Node.js 20, while @casl/prisma, @casl/angular, @casl/react, and @casl/vue each list Node.js 20+.
How do you deny a permission in CASL?
With an inverted rule through cannot in the AbilityBuilder, as in the blog example where a visitor cannot delete a BlogPost created more than a day ago. The fields parameter handles narrower denials, such as letting a moderator update the hidden field but not title or description.
Where should I ask a question about CASL?
In the support chat or on the Stack Overflow tag for casl, not in the issue list. The repository states that its issues are exclusively for bug reports and feature requests, and that questions posted there may be closed immediately without answers.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/stalniy-casl)Star history chart for your README
[](https://hysenlabs.com/projects/stalniy-casl)Was this useful?