dockprom pins seven containers to one host and two fstype edits
Docker hosts and containers monitoring with Prometheus, Grafana, cAdvisor, NodeExporter and AlertManager
At a glance
- What is it?
- dockprom assembles seven containers into one monitoring stack for a single Docker host: Prometheus, AlertManager, Grafana, NodeExporter, cAdvisor, Pushgateway and Caddy. It is opinionated down to fixed image tags and a hardcoded 200 hour retention window, and it leaves two storage panels needing a hand-edited fstype label.
- Who is it for?
- dockprom is a defensible answer for one Docker host that needs host and container metrics now, with Caddy fronting Prometheus and AlertManager and Grafana already pointed at Prometheus. It is not a multi-host answer: one compose file, one bridge network, one TSDB volume, four plain HTTP ports.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 8 months ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
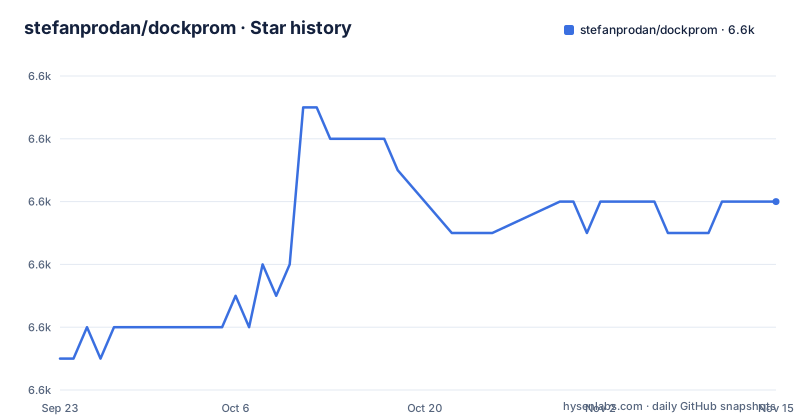
- stefanprodan/dockprom6,582 ★ · +5
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| stefanprodan/dockprom | 6.6k | 6.6k |
5 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Caddy v2 refuses a plaintext admin password
The install is one compose up carrying three variables at once:
ADMIN_USER='admin' ADMIN_PASSWORD='admin' ADMIN_PASSWORD_HASH='$2a$14$1l.IozJx7xQRVmlkEQ32OeEEfP5mRxTpbDTCTcXRqn19gXD8YK1pO' docker-compose up -dThe third variable exists because Caddy v2 does not accept plaintext passwords and must be handed a hash value instead. The hash in that shipped command corresponds to the literal password admin, so a fresh install comes up on a credential that is printed in public documentation. Setting your own means generating the hash first:
docker run --rm caddy caddy hash-password --plaintext 'ADMIN_PASSWORD'You then replace ADMIN_PASSWORD and ADMIN_PASSWORD_HASH in docker-compose.yml.
Image tags and the retention window are fixed in the command array
The compose file pins the image tags it shows:
  prometheus:
    image: prom/prometheus:v3.10.0
    container_name: prometheus
    volumes:
      - ./prometheus:/etc/prometheus
      - prometheus_data:/prometheus
    command:
      - '--config.file=/etc/prometheus/prometheus.yml'
      - '--storage.tsdb.path=/prometheus'
      - '--web.console.libraries=/etc/prometheus/console_libraries'
      - '--web.console.templates=/etc/prometheus/consoles'
      - '--storage.tsdb.retention.time=200h'
      - '--web.enable-lifecycle'
AlertManager is on prom/alertmanager:v0.31.1, NodeExporter on prom/node-exporter:v1.10.2, and cAdvisor on gcr.io/cadvisor/cadvisor:v0.55.1. Retention is the flag --storage.tsdb.retention.time=200h, roughly eight days, and it lives in the command array rather than in a Prometheus config file, so changing the window means editing compose and recreating the container. The same block sets --web.enable-lifecycle, which is the switch that makes the reload endpoint exist.
A new Grafana password does nothing while grafana_data persists
Grafana listens on http://<host-ip>:3000 and logs in as admin with password admin. Credentials can be changed in the compose file or through the ADMIN_USER and ADMIN_PASSWORD variables on compose up. A third route is an env file attached to the grafana service:
grafana:
  image: grafana/grafana:7.2.0
  env_file:
    - config
whose content is:
GF_SECURITY_ADMIN_USER=admin
GF_SECURITY_ADMIN_PASSWORD=changeme
GF_USERS_ALLOW_SIGN_UP=false
The trap is the named volume. To make a password change take effect you have to remove this entry, otherwise the change will not take effect:
- grafana_data:/var/lib/grafanaThe credentials already written inside that volume win over the environment, so a password that looks ignored is usually just a surviving database.
Two storage panels need the fstype label edited in the JSON
Three alert groups are set up in the alert.rules file: monitoring services at lines 2 to 11, the Docker host at lines 13 to 40, and containers at lines 42 to 69. One rule fires when a monitoring target disappears:
- alert: monitor_service_down
    expr: up == 0
    for: 30s
    labels:
      severity: critical
Another fires on host load:
- alert: high_cpu_load
    expr: node_load1 > 1.5
    for: 30s
    labels:
      severity: warning
The load threshold is meant to be adjusted to your CPU core count, and both rules hold for 30 seconds before firing.
Separately from alerting, the Docker Host Dashboard Free Storage graph and the Docker Containers Dashboard Storage Load graph both query filesystem metrics with an fstype matcher baked into the panel definition. The shipped value is btrfs, in grafana/provisioning/dashboards/docker_host.json at line 480:
"expr": "sum(node_filesystem_free_bytes{fstype=\"btrfs\"})",and in grafana/provisioning/dashboards/docker_containers.json at line 406. Those labels were changed from aufs to btrfs, so on ext4 or xfs the panels have nothing to match and draw nothing. You find your own value by opening http://<host-ip>:9090 and running node_filesystem_free_bytes. The awkward part is where the change has to happen: inside provisioned JSON, at line numbers that shift every time someone edits a dashboard. There is no override file for fstype.
The containers dashboard excludes the monitoring stack itself
The Docker Host Dashboard is the widest of the three. It covers server uptime, CPU idle percent, number of CPU cores, available memory, swap and storage, a system load average graph, running and blocked by IO processes, interrupts, CPU usage broken out by mode across guest, idle, iowait, irq, nice, softirq, steal, system and user, memory usage by distribution across used, free, buffers and cached, IO usage in read Bps with IO time, network usage per device for inbound and outbound Bps, and swap usage with activity.
The Docker Containers Dashboard covers total container CPU load, memory and storage usage, running containers, system load, IO usage, per-container CPU, per-container memory, cached memory usage, and inbound and outbound network usage. Its coverage has one stated hole: this dashboard does not show the containers that are part of the monitoring stack. The Monitor Services Dashboard picks up that remainder, showing Prometheus container uptime, monitoring stack total memory usage, Prometheus local storage memory chunks and series, chunks to persist, persistence urgency, chunks ops, checkpoint duration, samples ingested rate, target scrapes, scrape duration, HTTP requests, and alerts. So container visibility is deliberately split in two dashboards, and neither one is a complete picture of what runs on the host.
Every service joins one bridge network with one monitoring label
Caddy is described as the reverse proxy and basic auth provider for Prometheus and AlertManager, and for nothing else. The rest answer on their own host ports: Prometheus at http://<host-ip>:9090, Prometheus-Pushgateway at http://<host-ip>:9091, AlertManager at http://<host-ip>:9093, and Grafana at http://<host-ip>:3000. NodeExporter and cAdvisor are listed as collectors with no published host port. Every address the README lists is http, so Grafana's own admin login is served unencrypted and the Prometheus reload call travels as plain credentials. Pushgateway is described as the push acceptor for ephemeral and batch jobs.
State lives in two named volumes, prometheus_data and grafana_data, and configuration arrives as bind mounts from the repository: ./prometheus onto /etc/prometheus and ./alertmanager onto /etc/alertmanager, with AlertManager writing to /alertmanager. Everything attaches to a single network named monitor-net with driver: bridge, and the services shown in the compose file carry the label org.label-schema.group: monitoring and run with restart: unless-stopped. Grafana starts with Prometheus already registered as its default data source, named Prometheus, of type Prometheus, at http://prometheus:9090 with access set to proxy.
The collectors need host access: privileged cAdvisor, read-only rootfs
cAdvisor is declared with privileged: true and a device mapping:
  cadvisor:
    image: gcr.io/cadvisor/cadvisor:v0.55.1
    container_name: cadvisor
    privileged: true
    devices:
      - /dev/kmsg:/dev/kmsg
NodeExporter avoids privilege but reads the host instead, mounting /proc:/host/proc:ro, /sys:/host/sys:ro and /:/rootfs:ro, then pointing itself at those paths with --path.procfs, --path.rootfs and --path.sysfs. It also excludes pseudo paths from filesystem collection with --collector.filesystem.mount-points-exclude=^/(sys|proc|dev|host|etc)($$|/). The doubled dollar sign is there because compose would otherwise expand it. The trade is explicit: a privileged container and a container that can read the entire root filesystem are what buy host-level visibility.
A second compose file ships beside the one the install command uses
The repository root holds docker-compose.yml and docker-compose.exporters.yml, plus the directories alertmanager/, caddy/, grafana/, helpers/, prometheus/ and screens/, and a config file at the top level. The install command is docker-compose up -d with no file argument, so compose takes docker-compose.yml by default. The prerequisites also read from an old floor: Docker Engine >= 1.13 and Docker Compose >= 1.11, while the compose file itself uses a services-only layout with no version key and recent image tags. The repository is not archived, its last push is dated March 6, 2026, and both v9.1.0 and v9.2.0 carry that same date, with v9.0.0 from July 4, 2025 before them.
Editorial conclusion
dockprom is a defensible answer for one Docker host that needs host and container metrics now, with Caddy fronting Prometheus and AlertManager and Grafana already pointed at Prometheus. It is not a multi-host answer: one compose file, one bridge network, one TSDB volume, four plain HTTP ports. Before deploying, hash your own Caddy password, edit the fstype label in both dashboard JSON files, and decide whether a privileged cAdvisor container fits your host policy.
Frequently asked questions
What is cAdvisor used for in dockprom?
cAdvisor is the containers metrics collector in the stack, running as gcr.io/cadvisor/cadvisor:v0.55.1 with privileged: true and /dev/kmsg mapped in.
Why does the dockprom install command need a password hash?
Caddy v2 does not accept plaintext passwords and must be given a hash. Generate one with docker run --rm caddy caddy hash-password --plaintext 'ADMIN_PASSWORD' and set ADMIN_PASSWORD_HASH on compose up.
How long does dockprom keep metrics?
The Prometheus service passes --storage.tsdb.retention.time=200h in its command array, so the window is about eight days and it is edited in docker-compose.yml rather than in a config file.
Why does my Grafana password change not apply in dockprom?
The grafana_data volume holds the existing credentials, so you have to remove the entry - grafana_data:/var/lib/grafana, otherwise the change will not take effect.
How do I change the alerts in dockprom without restarting the stack?
Edit the alert groups in prometheus/alert.rules, which cover monitoring services, the Docker host, and containers, then POST to the reload endpoint: curl -X POST http://admin:admin@<host-ip>:9090/-/reload. That endpoint exists because Prometheus runs with --web.enable-lifecycle.
Which ports does dockprom open?
Prometheus on 9090, Prometheus-Pushgateway on 9091, AlertManager on 9093, and Grafana on 3000, each as http://<host-ip> followed by the port. Caddy fronts Prometheus and AlertManager only.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/stefanprodan-dockprom)Star history chart for your README
[](https://hysenlabs.com/projects/stefanprodan-dockprom)Was this useful?