Storj: patch releases are allowed to break your build
Ongoing Storj v3 development. Decentralized cloud object storage that is affordable, easy to use, private, and secure.
At a glance
- What is it?
- storj/storj is the Go repository where the Storj v3 distributed storage network is built, an S3-compatible platform that encrypts, splits and distributes files across a global network of computers. Its README is short and unusually candid about one thing above all: this repository does not follow semantic versioning, and that choice is deliberate.
- Who is it for?
- Read this repository as the network's engine room rather than as a library you depend on. It builds the distributed storage platform, it is licensed to be run as a service, and its own README says it is not meant to be consumed as a Go module, which removes the usual reason to treat it as a dependency.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
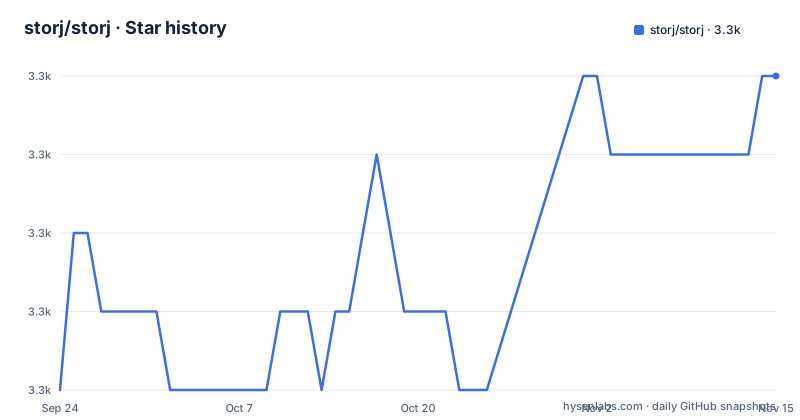
- storj/storj3,285 ★ · +4
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| storj/storj | 3.3k | 3.3k |
4 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The whole README describes one mechanism and then points at a wiki
The technical description fits in a paragraph. Storj is an S3-compatible platform and suite of distributed applications, files are encrypted, broken into little pieces and stored across a global distributed network of computers, and the network is built so that only the owner can retrieve them. The repository description calls it ongoing Storj v3 development, and a link to a white paper sits directly under the title.
Everything else in the file is a pointer. The table of contents has four entries: contributing, starting to use Storj, the license and support. Usage is delegated to the project wiki, and three tutorials are named there: using the Storj test network, using the Uplink CLI, and using the S3 gateway. Support is a community forum and a ticket system.
Two badges at the top say where the code can be read: a Go report card for the module path and a pkg.go.dev page for the same path. So this is a repository to read and build, not one whose README tells you how to install it.
Semantic versioning is followed for uplink and deliberately skipped here
The versioning note is the most consequential paragraph in the file, and it is a promise about breakage. Client libraries such as uplink do practice semantic versioning. This repository does not, and the reason given is that it is not intended to be used via Go modules. The consequence is stated plainly: backwards-incompatible changes may appear between minor and patch releases.
Read that next to the badges. A report card and a package documentation page both exist for the module path storj.io/storj, and the tree does contain a go.mod declaring that module. What the note rules out is consumption of this repository as a library through Go modules, not its existence as a module path.
For anyone tracking releases, that means the patch number carries no compatibility guarantee. The recent history shows how fast the line moves, with v1.163.6 published on 22 September 2026, then v1.164.0-rc and v1.164.1 both on 1 October 2026, the release candidate about two hours before the final build. A pin on a patch tag is a pin on a tag that may contain breaking changes.
AGPLv3 today, Apache v2 later, and a CLA that decides which
The license section is short and has a second half that is easy to skim past. The repository is licensed under AGPLv3. Then it asks contributors to sign an updated Contributor License Agreement, version 2, with the stated purpose of being able to relicense the code under Apache v2 or other licenses in the future.
So the project runs on a copyleft license while holding the paperwork to move away from it. For a user running the network that is straightforward. For a contributor it is a decision with a deadline attached to it, because code accepted under the AGPL without a signature cannot later be relicensed.
The license file itself sits at the root of the tree, and the repository also carries a MAINTAINERS.md, a CODEOWNERS file and a CODE_OF_CONDUCT.md, which is the usual shape for a project with corporate stewardship and a review process.
make with no arguments prints colored help, and the targets live in four included files
The root Makefile is a dispatcher. Its default goal is help, and help is generated by an awk one-liner that scans for targets with a comment marker and prints them with escape codes for colour. Running make alone therefore teaches you the target names instead of building anything:
.DEFAULT_GOAL := help
.PHONY: helpinclude Makefile.release.mk
include Makefile.dev.mk
include Makefile.test.mk
include Makefile.tools.mkThe four includes divide the work by purpose: releases, development, tests and tools. That naming is the closest thing to a build guide the repository has, and it sits outside the README.
The rest of the top level is the same story at larger scale. Five Jenkinsfiles exist, split into premerge, public, verify and versions variants alongside the main one. Release artefacts are built with Docker bake definitions and a separate release Dockerfile, and the tree still carries an Earthly ignore file for a builder it does not otherwise appear to use, plus a Gerrit style .gitreview file from an era of a different review system.
The go.mod names a module, pins Go 1.25.10 and ignores nine directories
The module file is where the engineering detail sits:
module storj.io/storj

go 1.25.10
A patch-level Go directive is unusually specific, so the toolchain is effectively fixed for anyone building this. Below it there is a block that lists directories the tooling should skip:
ignore (
	.build
	.claude
	.github
	.idea
	.vscode
	build
	dist
	node_modules
	release
)
Three of those are editor or assistant configuration directories and the rest are build output, which tells you this is a repository where several tools and a web frontend both write into the working tree.
The dependency list is a map of the same breadth. It pulls in Google Cloud packages for the profiler, pubsub, secret manager and storage, PostgreSQL through pgx and a SQLite driver, an embedded key value store, a Redis test double, Prometheus client libraries, an HTTP router and schema binder, a terminal UI library, a GeoIP database reader and a JWT library. That mixture is what a storage network that runs services, a satellite, storage nodes, a web front end and an installer looks like from the module file.
The source tree names the components of the network
The top-level directories are the architecture in one list. There is cmd/ for the binaries, storagenode/ for the machines that hold pieces of files, satellite/ for the coordinating service, versioncontrol/ for object metadata, certificate/ for identity material, web/ for the web front end, installer/ for the setup path, multinode/ for running several pieces together, crashcollect/ for collecting failures, and shared/, scripts/, resources/, docs/, testsuite/, private/ and experimental directories around them.
Two of those names deserve a note. crashcollect/ implies a mechanism for reporting what happened when something dies, which is the sort of component you only find in software that expects to fail on machines it does not own. private/ is a separate tree from public/, which in a repository with an AGPL core is worth knowing about before you assume the license covers everything in the directory listing.
The development documentation is split across CONTRIBUTING.md for outside contributions, DEVELOPING.md for building locally, and a Jenkinsfile.verify for checks, with the wiki carrying the tutorials that a first-time user needs.
Editorial conclusion
Read this repository as the network's engine room rather than as a library you depend on. It builds the distributed storage platform, it is licensed to be run as a service, and its own README says it is not meant to be consumed as a Go module, which removes the usual reason to treat it as a dependency. Two things follow for anyone building on it. Version numbers carry no compatibility promise here, since backwards-incompatible changes are allowed between minor and patch releases, so pin by commit and read the change history rather than trusting a tag. And the practical instructions are not in the repository at all: installation, the test network, the Uplink CLI and the S3 gateway live in the wiki, with questions going to the community forum or the support ticket system. Read the AGPL terms and the contributor licence agreement before contributing, since relicensing to Apache v2 depends on your signature.
Frequently asked questions
Does storj/storj follow semantic versioning?
Not in this repository. Semantic versioning is practiced for client libraries such as uplink, but this repository states that backwards-incompatible changes may appear between minor and patch releases, because it is not intended to be used via Go modules.
What license is storj/storj released under?
The repository is licensed under AGPLv3, and contributors are asked to sign an updated Contributor License Agreement v2 so that the code can be relicensed under Apache v2 or another license in the future.
How do I start using Storj according to this repository?
The README points to the project wiki and names three tutorials: using the Storj test network, using the Uplink CLI, and using the S3 gateway. Questions go to the community forum or to a ticket at support.storj.io.
What does the Storj repository actually build?
It is described as ongoing Storj v3 development of a distributed cloud storage network, an S3-compatible platform and suite of distributed applications whose files are encrypted, split into pieces and stored across a global network of computers.
What happens when I run make in the Storj repository?
The default goal is help, which prints a colourised usage listing generated by awk, and the real targets are included from four other makefiles covering releases, development, tests and tools.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/storj-storj)Star history chart for your README
[](https://hysenlabs.com/projects/storj-storj)Was this useful?