rage: printed passphrases, tagged SSH recipients, and a feature that needs a newer Rust
A simple, secure and modern file encryption tool (and Rust library) with small explicit keys, no config options, and UNIX-style composability.
At a glance
- What is it?
- rage is the Rust implementation of the age file encryption format: small explicit keys, no configuration file, and a command line that composes with pipes. Its own documentation is unusually candid about three costs, the autogenerated passphrase printed to your terminal, the public key tag that SSH recipients leave in a file, and a mount feature whose minimum Rust version is three releases above the crate's own.
- Who is it for?
- rage fits the case its design is aimed at, which is encrypting a file to a key you already hold with no settings to configure, and it composes well enough on standard input that shell pipelines are a natural fit. Before relying on it, pick your recipient type deliberately: SSH keys work but leave an identifying tag and are described as using more complex cryptography, and if that matters, generate a native age key instead.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 93 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 22, 2026, and from our analysis. They are not legal advice.
Star history
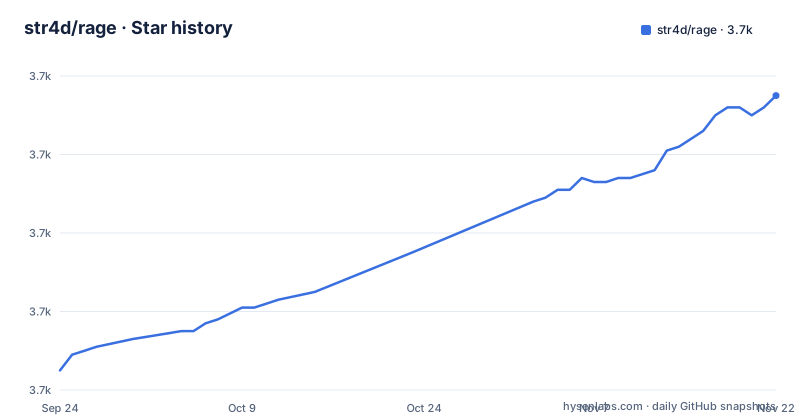
- str4d/rage3,735 ★ · +70
| Repository | 2026-09-24 | 2026-11-22 |
|---|---|---|
| str4d/rage | 3.7k | 3.7k |
70 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Dual licensed in the manifest, Apache-2.0 in the metadata
The repository metadata reports the licence as Apache-2.0. The manifest and the README both say something different and more useful: licensed under either the Apache License version 2 or the MIT licence, at your option, with `LICENSE-APACHE` and `LICENSE-MIT` at the root. The contribution clause follows the same pattern, stating that unless you say otherwise any contribution intentionally submitted for inclusion is dual licensed as above without additional terms. So the code is permissively dual licensed while the API field advertises one half of that. For anyone automating a licence check this matters, and for anyone who needs to know whether they may vendor rage into a product with a copyleft-free policy, the answer is yes on the strength of the MIT half. The project is an implementation of the age format rather than the format itself, which was designed by Benjojo and FiloSottile with a reference Go implementation kept separately.
The package is rage on most systems and rage-encryption on three
The install table has eleven rows, and the package name is not constant. It is `rage` for Cargo, Homebrew, MacPorts, Alpine's edge repository, NixOS and Scoop, and `rage-encryption` for Arch, openSUSE Tumbleweed and FreeBSD, in each case because those systems use a global namespace and `rage` collides. A note underneath spells out the policy for packagers: use `rage`, fall back to `rage-encryption` only for unavoidable name conflicts in global namespace systems, and never rename the binaries, using the package system's own conflict mechanism instead. Two more rows are worth noting. Debian and Ubuntu 22.04 or newer install from packages attached to the GitHub releases rather than from the distribution archive. Alpine is `edge` only, so a stable Alpine user has no listed route. Pre-built binaries are offered directly for Windows, Linux and macOS, and the same releases page is where the Debian and Ubuntu packages live, so those two distributions are served from the project rather than from their own archives. NixOS gets two forms, adding `pkgs.rage` to `environment.systemPackages` or running `nix-env -i rage`, and Scoop needs the bucket added before the install command will resolve. That is a lot of surface for one binary, and the policy paragraph exists because the packaging names had to be negotiated with three distributions that use a global namespace.
Recipients repeat on the command line or come from a file
Multi-party encryption is the first case the usage text handles. Repeating `-r` or `--recipient` gives every named recipient the ability to decrypt, and the same thing works through a file:
$ rage -R recipients.txt example.jpg > example.jpg.agewhere the file holds one recipient per line, and comments in the example show an `age1...` line per person. There is a small convention that pays off repeatedly: if the argument to `-R` or to `-i` is a single dash, the file is read from standard input, so recipients and identities compose with process substitution the same way the passphrase-protected key example does. The three invocation shapes are separate rather than flag combinations, encryption to recipients, encryption to a passphrase, and decryption. The help block reproduced in the README stops after `-p`, so the armour flag and several others appear only in the surrounding prose.
The autogenerated passphrase is printed as a list of words
Passphrase mode does something that is convenient and worth being deliberate about. Asked for a passphrase with `-p`, rage offers to autogenerate one, and if the prompt is left empty it generates a secure passphrase and prints it, hyphenated, in a row of words. That means the secret lands in your terminal scrollback and in anything capturing it. The prompting path has three cases. If a binary named `pinentry` is on `PATH`, that binary asks instead of rage. If `PINENTRY_PROGRAM` is set, it overrides the binary name or path. And if pinentry is missing, or `PINENTRY_PROGRAM` is set to the empty string, rage falls back to its own command line prompt. The empty-string case is the deliberate way to force the fallback rather than inheriting a pinentry that is installed but not wanted. Identity files can be protected the same way: an age file that is itself passphrase-encrypted is decrypted automatically when passed to `-i`, and the example creates one by encrypting the output of `rage-keygen`. The rationale given is that such a file is normally unnecessary, since access to the encrypted identity implies access to the whole system, but it earns its place when the identity file is stored remotely.
SSH recipients leave a tag that identifies the key
Existing SSH keys work without conversion: `ssh-rsa` and `ssh-ed25519` public keys can be used to encrypt and the matching private key file to decrypt, with `ssh-agent` explicitly not supported. The README attaches a warning to that convenience, and it is the most important sentence in the section. SSH key support employs more complex cryptography than the native key types, and it embeds a public key tag in the encrypted file, which makes it possible to track files that are encrypted to a specific public key. That is a property of the format as implemented here, not a defect in your usage: an observer holding a file can tell it was sealed to a particular key. For a tool whose selling point is small explicit keys with no configuration, that is the cost of not generating one.
The mount feature needs Rust 1.88 and the crate declares 1.85
Three Cargo feature flags are documented. `ssh` is on by default and enables the SSH key support above. `mount` enables the `rage-mount` tool, which mounts age-encrypted TAR or ZIP archives as read-only, is currently only usable on Unix systems because it relies on `libfuse`, and carries a minimum supported Rust version of 1.88. `unstable` enables in-development functionality with no stability or interoperability guarantees. The version numbers do not line up: the workspace declares `rust-version = "1.85"` and edition 2024, and the install table requires Cargo with Rust 1.85 or newer, while one optional feature needs three minor versions more. The flag syntax is `--no-default-features` with `--features` taking a comma-separated list, so turning ssh support off is a build-time decision rather than a runtime one.
Two crates on different version lines in one workspace
The workspace has four members, `age`, `age-core`, `age-plugin` and `rage`, and the two library versions are not the same: `age` is pinned at 0.12.1 and `age-core` at 0.12.0. The dependency block is annotated by standard rather than by purpose, which makes the compliance story unusually easy to audit. Base64 comes from RFC 4648, ChaCha20-Poly1305 from RFC 7539, SHA3-256 from FIPS 202, ML-KEM from FIPS 203, X25519 from RFC 7748, HKDF from RFC 5869 and HMAC from RFC 2104, HPKE from RFC 9180 and scrypt from RFC 7914, with a CSPRNG and bech32 for key encoding. The comment above the group says these are the dependencies required by the age specification. A second group is ordinary application code: a parser built on nom and cookie-factory, secret management with secrecy, subtle and zeroize, pinentry, flate2 for compression, localisation crates, and clap for the command line.
Two fuzz directories, a supply-chain directory, and a tap file
The tree carries the parts of the project that are not the tool. There are two fuzzing setups rather than one, `fuzz/` and `fuzz-afl/`, so both fuzzing engines are wired into the same repository. A `supply-chain/` directory sits alongside them, which in a Rust project of this size means dependency provenance is treated as something to check rather than something to assume. `tap_migrations.json` records taps, the test anything protocol files a test runner can consume, so a migration there is a change to how the test suite is invoked. `rust-toolchain.toml` pins the compiler for contributors independently of the declared minimum, `docs/` holds the book sources, and a `.vscode/` directory is committed. The last push to the branch was 2026-08-20, after the 0.12.1 release on 2026-07-14, and that release day also carried 0.11.4 on the previous line about sixteen minutes earlier, which is how a maintenance fix and a feature release are shipped together without renumbering either. `rust-toolchain.toml` pins the compiler for contributors independently of the declared minimum, so the version a contributor builds with and the version a user is told to need are two separate pieces of information.
Editorial conclusion
rage fits the case its design is aimed at, which is encrypting a file to a key you already hold with no settings to configure, and it composes well enough on standard input that shell pipelines are a natural fit. Before relying on it, pick your recipient type deliberately: SSH keys work but leave an identifying tag and are described as using more complex cryptography, and if that matters, generate a native age key instead. Never accept the autogenerated passphrase without moving it out of your terminal history. If you need to mount encrypted archives, check your Rust version against the 1.88 requirement for that feature rather than the 1.85 the manifest advertises. And read the MIT half of the dual licence rather than the Apache-2.0 the metadata field reports, since that is the half that answers the question people actually have.
Frequently asked questions
How do I install rage on Linux, macOS or Windows?
Eleven routes are listed. `cargo install rage` with Rust 1.85 or newer, `brew install rage`, `port install rage`, `apk add rage` on Alpine edge, `pacman -S rage-encryption` on Arch, `nix-env -i rage` or environment.systemPackages on NixOS, `zypper install rage-encryption` on openSUSE Tumbleweed, `pkg install rage-encryption` on FreeBSD, and on Windows a Scoop bucket followed by `scoop install main/rage`. Debian and Ubuntu 22.04 or newer use the packages attached to the GitHub releases.
Can rage encrypt a file to more than one person?
Yes. Repeat -r or --recipient and every named recipient can decrypt. Recipients can also be listed one per line in a file passed with -R or --recipients-file, and passing a single dash as the argument reads that file from standard input, so recipients compose with process substitution.
What happens when I use -p or --passphrase with rage?
rage offers to autogenerate a secure passphrase and, if the prompt is left empty, prints one as a hyphenated list of words. Prompting uses a pinentry binary if one is on PATH, PINENTRY_PROGRAM overrides the binary name or path, and rage falls back to its own prompt when pinentry is absent or PINENTRY_PROGRAM is set to the empty string.
Does rage work with an existing SSH key?
ssh-rsa and ssh-ed25519 public keys can encrypt and the matching private key file can decrypt, but ssh-agent is not supported. The README warns that this path uses more complex cryptography and embeds a public key tag in the encrypted file, so it is possible to tell that a given file was encrypted to a specific key.
Should I use rage as a Rust library?
No, use the age crate, which rage is built on top of. The workspace also contains age-core and age-plugin, and the manifest pins age at 0.12.1 while age-core sits at 0.12.0, so the two library lines are not released in lockstep.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/str4d-rage)Star history chart for your README
[](https://hysenlabs.com/projects/str4d-rage)Was this useful?