Stratosphere Slips: an IPS whose blocking is Linux-only
Slips, a free software behavioral Python intrusion prevention system (IDS/IPS) that uses machine learning to detect malicious behaviors in the network traffic. Stratosphere Laboratory, AIC, FEL, CVUT in Prague.
At a glance
- What is it?
- A behavioral intrusion prevention system that scores evidence from 40 plus threat feeds, machine learning models and expert heuristics, and alerts once enough of it accumulates. It runs from containers on all three major platforms, but the blocking features exist only on Linux, macOS has its own image under emulation, and a local config file with edits will stop the updater in its tracks.
- Who is it for?
- Slips fits a specific job: a research-grade behavioral detector you can point at a PCAP, a live interface, or flows from Suricata, Zeek or Argus, and read the evidence for rather than just the verdict. Two things narrow that.
- Can I use it commercially?
- Yes, with conditions. GPL-2.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
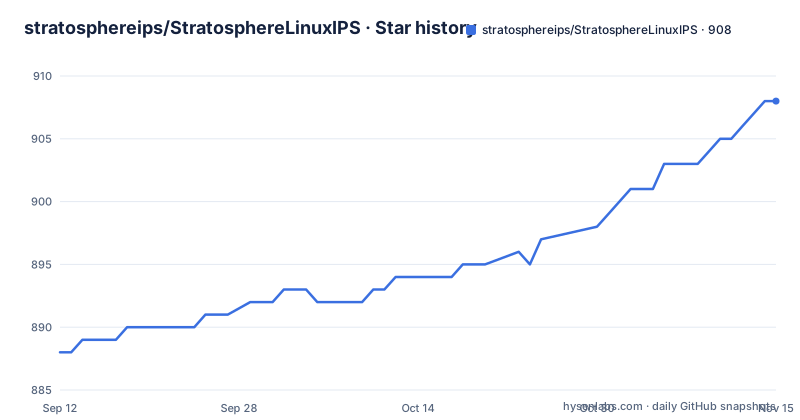
- stratosphereips/StratosphereLinuxIPS908 ★ · +20
| Repository | 2026-09-12 | 2026-11-15 |
|---|---|---|
| stratosphereips/StratosphereLinuxIPS | 888 | 908 |
20 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Detection is evidence accumulation, not a verdict
The detection model is the part to understand before anything else. Slips combines machine learning models trained to detect malicious behaviors, more than 40 threat intelligence feeds, and expert heuristics. It then gathers evidence of malicious behavior and triggers alerts when enough of it has accumulated, using thresholds the page describes as extensively trained.
That is a different shape from a signature match. There is no single rule that fires, and the alert is a summary of how much evidence a flow attracted, which is why the output artifacts matter as much as the alert itself. A PCAP goes in, and the page's own quick test reads `output_dir/alerts.log` after the run.
Inputs are equally varied. Slips works with live network traffic in real time, with PCAP files, and with network flows exported from Suricata, Zeek/Bro and Argus. The Python code relies on the Zeek network analysis framework for capturing live traffic and analyzing PCAPs, and on Redis 7.0.4 or newer for interprocess communication, which is the piece to know about if you plan to run it distributed rather than as one process.
The project dates to 2012 and is attributed to Sebastian Garcia at the Stratosphere Laboratory, part of the Faculty of Electrical Engineering at the Czech Technical University in Prague.
Three platforms run it, only one can block
The support statement is short and split in two halves. Slips is supported on Linux, macOS and Windows dockers only, and the blocking features of Slips are only supported on Linux.
That distinction is the one that matters for an intrusion prevention system as opposed to a detection system. Everywhere else you get the scoring, the evidence and the alerts, and the enforcement half is absent. The container flags reinforce the same split, since the recommended Linux run grants `NET_ADMIN`, the capability you need to touch packet filtering, and uses host networking so the tool sees real traffic rather than container traffic.
There is a fourth path, marked beta in the installation list: a Raspberry Pi. So the honest support matrix is Linux for anything that has to enforce, the other two platforms for detection, and a beta hardware target for whatever it can manage.
Python 3.12.3 and at least 4 GB of RAM are the stated requirements. Whether 4 GB is enough is the subject of the next section, because the recommended container run reserves twice that.
The requirements say 4 GB and the recommended run reserves 8 GB with no swap
The recommended invocation is a long single line, and every flag in it is a decision.
docker run --rm -it -p 55000:55000 --cpu-shares "700" --memory="8g" --memory-swap="8g" --net=host --cap-add=NET_ADMIN --name slips stratosphereips/slips:latestAgainst a stated minimum of 4 GB, this asks for 8 GB of memory, which suggests the minimum is a floor for a bare run rather than a recommendation for a normal one. Setting the memory swap equal to the memory limit is the part worth reading twice: it leaves the container no swap headroom beyond its own limit, so a memory-hungry run hits the ceiling instead of spilling.
The CPU flag is a share weight, not a cap. A value of 700 sets the container's relative weight against others on the same host, which matters if you run Slips beside something else and is easy to mistake for a percentage of a single core.
Then there are the two network decisions. Host networking on Linux means the container shares the host's stack, which is what makes live capture and blocking work. The published port 55000 exists for the web interface rather than for the analysis, since with host networking the container's own ports are already the host's.
macOS gets a different image, an emulated architecture, and no host networking
The MacOS run is a different command line, and the page explains the one that matters.
docker run --rm -it -p 55000:55000 --platform linux/amd64 --cpu-shares "700" --memory="8g" --memory-swap="8g" --cap-add=NET_ADMIN --name slips stratosphereips/slips_macos_m1:latestTwo things differ from the Linux line beyond the missing host networking. The image is a different repository tag, `stratosphereips/slips_macos_m1`, and the platform is pinned to `linux/amd64`, which on Apple Silicon means running the workload under emulation.
The missing `--net=host` is a functional change, not a stylistic one, and the page gives the reason directly: on MacOS, do not use it if you want to access the container's internal ports from the host. Host networking on Docker Desktop for Mac does not behave the way it does on Linux, so the alternative is published port mapping, and the consequence is that the container no longer sits on the host's network stack.
Everything else in the run is identical, which makes the two commands easy to read as a template with a platform-specific patch. The blocking limitation from the previous section applies here too: this is a detector on a Mac.
Editing your own configuration stops the updater
The configuration section is written as a set of prohibitions, and the last one is the consequential one.
The first rule is that you should not edit the default `config/slips.yaml` directly. Create a copy for your local changes and run Slips with `-c`, for example `./slips.py -c config/my_slips.yaml -f dataset/test7-malicious.pcap`. The same pattern applies to `config/whitelist.conf`: keep the default file unchanged, make a copy, and set `whitelists.local_whitelist_path` in your copied config to point at it.
Then the update rule, stated without elaboration: Slips aborts updating to new versions when there are changes to Slips local config files.
So the updater treats a modified local config as a reason to stop, which means a patched file becomes an upgrade blocker. That is a defensible design, since a new version can add or rename keys and a local copy would silently miss them, and it is also a mechanism by which a machine stops receiving security fixes until someone compares files by hand. The tree explains how the updater is wired, with an `update.json` at the root, a `kalipso.sh` script and an `install/` directory.
The settings themselves are ordinary: the `time_window_width` parameter for the time window, an `all` analysis direction if you want to see attacks both from and to your machine, a choice of whether to train or test the models, and toggles for popup notifications and blocking.
The documentation links point at develop, not at the default branch
Every documentation link on the page is a `develop` link.
The installation options, the parameter explanations, the web interface guide, the Raspberry Pi instructions and even the configuration file itself are all addressed to the `develop` branch, either through the ReadTheDocs `en/develop/` path or through a `blob/develop/` URL for `config/slips.yaml`. The repository's default branch is `master`.
That gap is worth knowing before you start reading. A user who clones the default branch and follows the documentation is reading about a different tree, and a key named in the docs may not exist in what they cloned, or may have moved.
The rest of the page's navigation is a mix of project infrastructure. There is a separate official site for Slips, a documentation build configured for ReadTheDocs, a blog tag and a Discord invite under the Stratosphere umbrella, a changelog, a citation file for the project, a `LICENSES/` directory alongside the main license, and a secrets baseline configuration, which is the file a scanner uses to decide which strings in the tree are expected.
The release cadence behind all of this is visible in the tags: v1.1.22 on 2026-07-04, v1.1.23 on 2026-09-01 and v1.1.24 on 2026-09-30, with the page itself headed by the current version.
The Makefile opens a shell and nothing else
The entire Makefile is two targets.
bash:
	docker run --rm -it slips /bin/bash

shell:
	docker exec -it slips /bin/bash
Neither target builds, tests, lints or installs anything, and there is no default target and no `.PHONY` declaration, so a bare `make` runs the first one. Both name the container `slips` literally, which means they only work if the container is running under that exact name, and that name comes from the `--name slips` in the documented `docker run` line rather than from anything the Makefile sets up.
The difference between the two is one word. `bash` starts a new container from the image named `slips`, which is the local image tag if you have built it, while `shell` attaches to a container that is already running.
Everything else the project uses for development sits outside the Makefile. There is a `pytest.ini` and a `conftest.py` at the root, a pre-commit configuration, a tests directory, a `zeek-scripts/` directory for the capture side, a `run/` directory, a `databases/` directory, and a `docs/` tree.
Editorial conclusion
Slips fits a specific job: a research-grade behavioral detector you can point at a PCAP, a live interface, or flows from Suricata, Zeek or Argus, and read the evidence for rather than just the verdict. Two things narrow that. If you want it to drop packets rather than describe them, Linux is the only supported host, and on the other two platforms you are running the container without host networking, which changes what the tool can see. And the configuration model is deliberately hands-off, which is good hygiene until you need to change something and find that the updater now refuses to run. Beyond that, treat the documentation as describing the `develop` branch rather than the default one, since the page's own links point there, and expect the requirement list and the recommended container flags to disagree about memory.
Frequently asked questions
What does Slips need in order to run?
Python 3.12.3 and at least 4 GB of RAM, plus the Zeek network analysis framework for capturing live traffic and analyzing PCAPs, and Redis 7.0.4 or newer for interprocess communication. Docker is the recommended way to run it, with NET_ADMIN added and, on Linux hosts, host networking.
Does Slips work on macOS?
Slips is supported on Linux, macOS and Windows through Docker, with a separate Raspberry Pi path marked beta. macOS has its own image, stratosphereips/slips_macos_m1, run with the platform pinned to linux/amd64, and the page says not to use --net=host on MacOS if you want to reach the container's ports from the host.
Can Slips block traffic, or only detect it?
Only on Linux. The page states that Slips is supported on Linux, macOS and Windows dockers, and that the blocking features of Slips are only supported on Linux. The recommended Linux container run adds NET_ADMIN and uses host networking, and the configuration exposes a blocking toggle.
How do I change Slips configuration without breaking updates?
Do not edit config/slips.yaml directly. Copy it and pass your copy with -c, for example ./slips.py -c config/my_slips.yaml -f dataset/test7-malicious.pcap. Do the same for config/whitelist.conf and point whitelists.local_whitelist_path at your copy. Slips aborts updating to new versions when Slips local config files have changes.
How do I read Slips output in a browser?
Run ./slips.py -e 1 -f dataset/test7-malicious.pcap -w and open http://localhost:55000/. The web interface is read-only, localhost-only, and fixed to that run's Redis database, SQLite flow database and output logs, showing runtime and module health, alerts, evidence, triggering flows and host context. It can also be turned on with web_interface.enabled: true in config/slips.yaml.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/stratosphereips-stratospherelinuxips)Star history chart for your README
[](https://hysenlabs.com/projects/stratosphereips-stratospherelinuxips)Was this useful?