KeyHacks: a credential check list with no authorization boundary of its own
Keyhacks is a repository which shows quick ways in which API keys leaked by a bug bounty program can be checked to see if they're valid.
At a glance
- What is it?
- One Markdown file, roughly ninety entries, and a single line stating the whole precondition: the keys are supposed to come from a bug bounty program or a pentest you are running. Everything the repository omits sits in that gap, including how to tell a live key from a dead one in most cases, and who is harmed when the answer is live.
- Who is it for?
- Do not run any of this outside a program whose written scope names the specific service and the specific credential you found. That is not a formality here: a live key found in a public repository belongs to whoever created it, and a payment, messaging or cloud credential that answers you is answering a third party who never agreed to be tested.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 100 days ago.
- What is it written in?
- GitHub does not report a main language for this repository.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
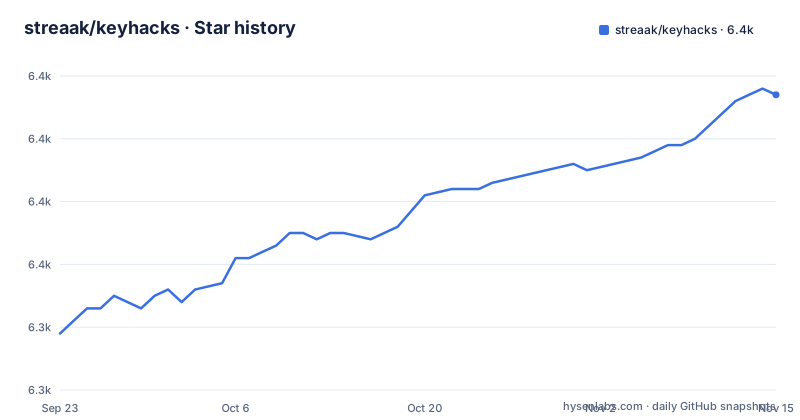
- streaak/keyhacks6,377 ★ · +38
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| streaak/keyhacks | 6.3k | 6.4k |
38 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The whole precondition is one sentence, and it is the right one
KeyHacks is a repository which shows quick ways in which API keys leaked by a bug bounty program can be checked to see if they're valid. The readme puts the same condition more plainly: it shows methods to validate different API keys found on a bug bounty program or a pentest. That is the authorization boundary, stated by the project itself, and everything below it is conditioned on it.
The condition is doing more work than it appears to. Most keys in this catalogue were never meant to be found. They sit in a client's repository, a JavaScript bundle, a mobile application, a configuration file that somebody committed by accident, or a CI log. The person who created the key did not consent to being tested, and the program that hired you did not invite them. What authorizes you is a document that names a program, a target list and a class of vulnerability, and the credential you found has to fall inside all three.
So the correct reading of this repository is narrow. It is a lookup table for a tester who already knows that a specific leaked credential is in scope for a specific target, and who needs the request shape that vendor expects rather than the vendor's documentation. It is not a hunting tool, and nothing in it establishes that any particular key may be touched. The gap between those two things is where the risk lives, and the file does not close it.
Nothing in the file checks whether a target is yours to touch
Look for a safety mechanism in a repository like this and there is none. There is no allowlist of hosts, no prompt before a request is sent, no flag that limits the run to one service, no dry run that prints what it would do, and no abort switch if a key turns out to belong to a system you were never authorized to touch.
The structure makes that absence structural rather than accidental. A key validator is by construction a program that takes an input belonging to someone else and sends it somewhere. Every entry is that program with a different vendor's URL substituted in. Adding a scope check would mean adding a per-vendor notion of whose key this is, and the catalogue has no room for such a notion: an entry is a request shape, not a record of provenance.
The blast radius differs sharply by entry, and the file does not rank them. A read-only analytics key and a payment API secret answer the same request shape and carry completely different consequences if the answer is live. That is why authorization has to come from the program's scope rather than from the list.
The linked automation runs the whole catalogue at once
The readme credits a second repository with scripting the entire process available here, pointing at a shell script kept under a pentest tools project. That script is not in this repository, so nothing here constrains what it does, and the description of it is the important part: the entire process, which means the sweep rather than one entry.
This is the scope problem in its clearest form. Authorization in a bug bounty is granted per host and per program, and the credential you are cleared to test belongs to one of them. A loop over ninety vendor checks does not know which one that is.
So the automation is where the tool stops being a lookup table and starts being a scattergun. If you use any part of this, the authorization decision has to be made before the sweep runs, per credential, not discovered by reading the responses afterwards.
Only one entry explains how to read the answer
Most entries in this file are a request and nothing else.
One entry breaks the pattern and shows what the author considered worth writing down. The Slack webhook section states that if the command returns a particular error string the URL is valid, and that any other response means it is invalid. Note what the signal is: an error message returned by the vendor's own API.
A second entry gestures at the same idea without finishing it. The GitHub token section carries a comment about checking the scope of an API token, which is the only hint in the catalogue that a key can be live and still harmless. Nothing tells you what to do with the answer, and nothing warns that a key which validates may already have been rotated, revoked, or replaced by one with narrower permissions.
The anchors in the table of contents do not match their own labels
The catalogue is a single table of contents of roughly ninety entries, and a number of its internal links point at anchors that do not correspond to their own text. These lines are copied exactly as they appear in the source:
- [Deviant Art Access Token](#Deviant-Art-Access-Token)
- [Instagram Basic Display API](#Instagram-Basic-Display-API-Access-Token)
- [Razorpay API key and secret key](#Razorpay-keys)
- [Shodan.io](#Shodan-Api-Key)
- [Twilio Account_sid and Auth token](#Twilio-Account_sid-and-Auth-token)
- [WeGlot Api Key](#weglot-api-key)
The second line is labelled one thing and points at an anchor for another entry. The third points at an anchor that names neither key nor vendor. The fourth is a search engine entry filed under an API key heading. The fifth puts an underscore into a label where every other entry uses spaces. The sixth changes case between the label and the anchor.
That last one is the harmless kind, because anchors are matched case insensitively.
One entry goes past checking, and it is the one that mints credentials
Validating a leaked key answers a narrow question: is this string still accepted? Most entries in the catalogue stay inside that question. One does not, and the difference is worth naming precisely because the file presents both in the same format.
The Facebook app secret entry says, in full, that you can generate access tokens by visiting a URL it then supplies. That is not validation. A client secret is the long lived credential a server uses to obtain tokens on behalf of an application, so an entry that turns a leaked secret into a usable access token is describing how to act as somebody else's application rather than how to detect that a secret exists. It is the one place in the file where a reader following the instructions stops probing and starts using.
The distinction is the whole ethics of this repository in miniature. Finding a key is often fair game under a disclosure policy. Using a key that belongs to another application is a different act with a different owner, a different blast radius and usually a different legal footing. Nothing in the file marks the difference, and nothing stops a reader from treating one entry the way they treated the rest.
A pinned API version from years ago, and no date on any entry
One entry builds its request with a version parameter in the query string, set to a two-part version number (v3.2). Pinning a version is defensible practice, but pinning one this old in a document with no review date tells you the entry was written once and copied forward, not that it is maintained.
There is no changelog, and no release history, which the repository genuinely does not have. The only maintenance signal available is the date of the last push to the default branch, 2026-08-07, and that applies to the whole document rather than to any entry in it.
For a catalogue of vendor request shapes, that is the central weakness. Vendors change their authentication endpoints, their error strings and their token formats, and a stale entry does not fail loudly. It fails by returning an error the reader has no way to interpret, which is the same missing-interpretation problem as before, arriving from a different direction: not only does the file rarely tell you what success looks like, it also does not tell you when its own instructions went stale.
One Markdown file, no license, and an empty header block
The repository root contains exactly one entry: README.md. There is no source code, no test suite, no build configuration, no continuous integration, no manifest of any kind. The primary language is not recorded, the license field is empty, and there is no homepage. The default branch is `master`, and the project publishes no releases.
An empty license field matters more here than it would for most repositories. This is a document people copy command lines out of, and the terms under which that is permitted are not stated anywhere in the file. Absence of a license is not a grant.
Everything the project is consists of the heading, the one sentence of scope, the attribution to the person who scripted it elsewhere, the table of contents, and the entries. That is a reasonable thing for a reference list to be, and it is worth being clear that nothing here is a tool you install, configure or audit. There is no version to pin, no behaviour to depend on, and no way to tell whether a given entry ever worked.
Editorial conclusion
Do not run any of this outside a program whose written scope names the specific service and the specific credential you found. That is not a formality here: a live key found in a public repository belongs to whoever created it, and a payment, messaging or cloud credential that answers you is answering a third party who never agreed to be tested. Two further gaps are worth weighing before you use it even in scope. The list ships no per-target authorization check, no dry run and no abort switch, and the linked automation is described as scripting the entire process. Report what you find instead of probing it, and treat the payments and messaging entries as out of bounds unless your scope says otherwise by name. Last push was 2026-08-07, the repository has no releases, and the root contains a single README.
Frequently asked questions
What is the streaak/keyhacks repository for?
It is a single README collecting quick ways to check whether API keys found during a bug bounty program or a pentest are still valid, one entry per vendor, roughly ninety of them. The repository root holds only README.md, there is no code, and the project publishes no releases. The readme states the precondition itself: the keys are supposed to come from an authorized engagement.
Does keyhacks tell you how to tell whether a key worked?
The Slack webhook entry does, which states that a particular error string means the URL is valid and that any other response means it is not. The other entries are request shapes without an expected response. One entry carries a comment about checking the scope of a token, which is the only hint that a live key can still be harmless.
Is it safe to run the keyhacks scripts on keys you find?
The repository states the condition itself: the keys should come from a bug bounty program or a pentest. Beyond that condition there is no safety mechanism at all, no host allowlist, no dry run and no abort switch, and the linked automation by another author is described as scripting the entire process. A key that answers you belongs to whoever created it.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/streaak-keyhacks)Star history chart for your README
[](https://hysenlabs.com/projects/streaak-keyhacks)Was this useful?