Sub-Store: CORS defaults, the sub.store rewrite, and protocol gaps
Advanced Subscription Manager for QX, Loon, Surge, Stash, Egern and Shadowrocket!
At a glance
- What is it?
- Sub-Store converts proxy subscriptions between client formats for QX, Loon, Surge, Stash, Egern, and Shadowrocket. Its documentation is unusually candid about three sharp edges: a rewrite domain it does not own, a CORS allowlist that defaults to three origins, and push notifications that stopped working for two providers.
- Who is it for?
- Sub-Store is worth adopting if you juggle subscriptions across several proxy clients and want one backend that speaks each of their formats, and it is a poor fit if you need notifications over Matrix or SMTP, or if you would rather not reason about a domain the project explicitly does not own.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
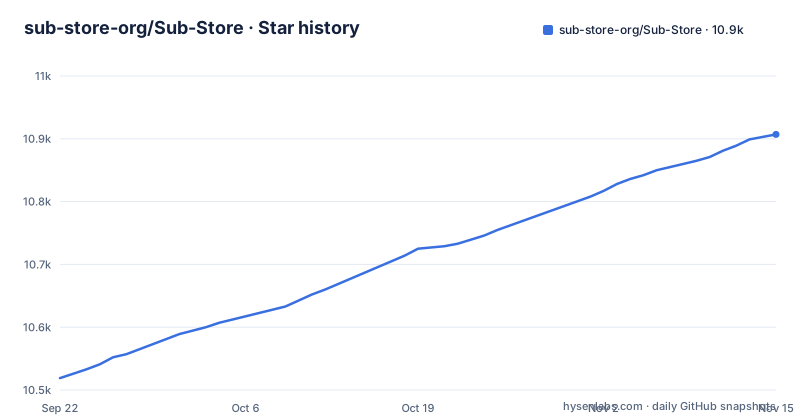
- sub-store-org/Sub-Store10,907 ★ · +388
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| sub-store-org/Sub-Store | 10.5k | 10.9k |
388 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
sub.store is a rewrite target, not a domain the project owns
The project states plainly that sub.store is only the domain used by module-script rewrite rules and is not a public domain it owns. When that rewrite does not apply, the request is not blocked: it travels to the public sub.store service instead. Two consequences are spelled out. The domain could in theory redirect users to a fake frontend, which the maintainers note is only a possibility and does not imply that the domain's owner would do this. And it could receive user data, which creates what they call a data leakage risk. The official frontend is https://sub-store.vercel.app. Their stated plan is to keep the current domain rather than move to a new one, on the grounds that a replacement needs to be related, short, and hard for anyone else to register in the short term. You can neutralize the risk locally by blocking the host:
[Host]
sub.store = 127.0.0.1
The caveat they attach to that fix is the important part: ordinary users may still send requests to the public sub.store after switching or toggling configuration modules.
The CORS allowlist has two knobs and three allowed origins by default
The backend API carries a configurable browser CORS allowlist, and setting it does not change the module rewrite domain. Node and server deployments read it from the environment variable SUB_STORE_CORS_ALLOWED_ORIGINS, while Proxy App modules take it as the cors module argument. Both default to the same three origins: https://sub-store.vercel.app, http://substore.stash, and https://substore.stash. Multiple origins are separated by commas and matched exactly by scheme, host, and port, which means http://substore.stash and https://substore.stash are two distinct entries and neither one covers a port you failed to list. Setting the value to a wildcard is possible but is advised only when you accept the risk of any website reading the local backend through browser CORS. The consequence for readers is concrete and easy to misdiagnose: host the frontend anywhere else and browser reads of the API stop working until you add that exact origin.
Matrix and SMTP push URLs fail outright after the move to shoutrrr-ts
For Node deployments, SUB_STORE_PUSH_SERVICE accepts either a Shoutrrr URL or an existing HTTP/HTTPS URL template. Shoutrrr URLs are now delivered in-process by the shoutrrr-ts library, and a separate shoutrrr executable is no longer used or required. The supported Shoutrrr families are Generic Webhook in its generic://, generic+https://, and generic+http:// forms, plus Bark, Discord, Gotify, Google Chat under its hangouts:// alias, IFTTT, Join, Mattermost, ntfy, OpsGenie, Pushover, Pushbullet, Rocket.Chat, Slack, Microsoft Teams, Telegram, and Zulip. Two are explicitly not supported: matrix:// and smtp://, and there is no fallback to the old executable. The consequence is that an existing configuration stops delivering rather than degrading gracefully, because an unsupported URL produces a notification error instead of sending anything. The maintainers ask you to check existing configurations before upgrading. They also note that upstream checks rely on local Go-compatibility fixtures rather than verified live delivery to every provider, so a passing local check is not the same as a message arriving.
The two push paths log differently, so secrets do not leak from only one of them
Push URLs may contain secrets, so SUB_STORE_PUSH_SERVICE is privileged configuration and should be treated that way. The two supported forms do not behave identically. Shoutrrr URLs are sent in-process, and diagnostics from that path do not print the configured URL, so a failing notification surfaces as an error without writing the destination into logs. The HTTP/HTTPS URL template path is unchanged, still using the existing request path and its 推送标题 and 推送内容 placeholders, and this change does not alter that path or its existing logging behavior. The consequence for readers is that the safer log behavior belongs only to the Shoutrrr branch. If your configuration uses an HTTP template, the target is still handled under the older logging rules, so treating the whole setting as secret does not by itself guarantee it stays out of your logs. Separately, the Node version the backend was tested against is recorded in the .node-version file, and current Node support should be checked against the upstream package.
Surge and mihomo accept different protocols, so a conversion can drop nodes
Input coverage is broad but uneven across clients, as the README's Supported Input Formats list shows. Surge is listed with Direct, SS, VMess, Trojan, HTTP, HTTPS, HTTP/2 CONNECT, SOCKS5, SOCKS5-TLS, AnyTLS, TrustTunnel, TUIC, Snell, Hysteria 2, MASQUE for Surge, SSH limited to password authentication, an External Proxy Program limited to macOS, and WireGuard limited to Surge to Surge. mihomo, the Clash.Meta fork, takes a different set that adds Tailscale, GOST Relay, Shadow QUIC, ZeroTier, OpenVPN, mieru, and sudoku. Loon and QX have their own lists again, with QX covering SS, SSR, VMess, Trojan, HTTP, SOCKS5, VLESS, and AnyTLS, and Loon adding SOCKS5-TLS, WireGuard, and Hysteria 2.
HTTPS is listed as a proxy scheme yet is rejected as a URI input
The proxy URI scheme list includes socks5, socks5+tls, http, and https, and https is marked as acceptable there. The documented example is socks5+tls://user:pass@ip:port#name. The broader URI list, covering AnyTLS, SOCKS, SS, SSR, VMess, VLESS, Trojan, Hysteria, Hysteria 2, TUIC v5, and WireGuard, carries a different instruction: HTTP(s) has no standard URI format, so it is not supported in that path and you should use other formats instead. That is less a contradiction than two input paths with different tolerance levels. There is also a standing warning against exporting a URI from Shadowrocket or NekoBox and importing it as input, because those exports may not be standard URIs, though several common non-standard ones such as VMess and VLESS are already supported. The practical consequence is that a link you exported from a phone client can be rejected in ways that look like a Sub-Store defect and are actually a format problem upstream of it.
The deprecated target=Clash survives on the backend but not in the frontend
Clash as a target platform is marked deprecated. The frontend no longer offers it, yet the backend still supports it, and the switch is the query parameter target=Clash on the request. The protocol list behind that legacy path is narrower than the mihomo one: SS, SSR, VMess, Trojan, HTTP, SOCKS5, Snell, VLESS, and WireGuard. The split matters for anyone with scripts or client configurations already pointing at that parameter, because those keep working straight through the deprecation while someone clicking through the interface cannot find the option at all. A second caveat sits above the feature list itself: the project notes that its feature descriptions may not be updated in real time and directs you to the actual available features for accurate information.
A backend, a config directory, and scripts, licensed under AGPL-3.0
The top level of the repository is backend/, config/, scripts/, and assets/, alongside .node-version, .gitignore, .github/, LICENSE, README.md, and a vs.code-workspace file. That layout is what any deployment has to work with: the tested Node version is pinned in .node-version, and runtime settings such as the CORS allowlist and the push service arrive through environment variables. The core feature list is deliberately short, covering conversion among formats, subscription formatting, collecting multiple subscriptions into one URL, and hosting and modifying subscriptions or files. The project is licensed AGPL-3.0, which matters to anyone who plans to modify the backend and serve the result to others. It is not archived, the last push to the master branch is 2026-11-02, and the release history is dense: 2.44.0, 2.44.1 and 2.44.2 all shipped on 2026-10-25. Documentation lives separately at sub-store-org.github.io/doc, with a wiki alongside the source.
Editorial conclusion
Sub-Store is worth adopting if you juggle subscriptions across several proxy clients and want one backend that speaks each of their formats, and it is a poor fit if you need notifications over Matrix or SMTP, or if you would rather not reason about a domain the project explicitly does not own. Before you deploy, verify three things yourself: add your own frontend origin to the CORS allowlist rather than reaching for a wildcard, audit any existing SUB_STORE_PUSH_SERVICE values for matrix:// or smtp:// now that those produce a notification error instead of sending, and decide whether the target client you convert into accepts the protocols you actually use.
Frequently asked questions
What does "sub store" mean?
Sub-Store describes itself as an advanced subscription manager for QX, Loon, Surge, Stash, Egern, and Shadowrocket. Its core functions are converting between formats, formatting subscriptions, collecting several subscriptions into one URL, and hosting and modifying subscriptions or files.
what is sub store
It is a JavaScript project released under the AGPL-3.0 license that converts proxy subscriptions between client formats. Node and server deployments are configured through environment variables such as SUB_STORE_CORS_ALLOWED_ORIGINS and SUB_STORE_PUSH_SERVICE.
Does Sub-Store own the sub.store domain?
No. The project states that sub.store is only the domain used by module-script rewrite MitM rules and is not a public domain owned by it. If a request does not go through the rewrite, the data is sent to the public sub.store service, which the project describes as a data leakage risk.
Which push notification services work with Sub-Store on Node?
SUB_STORE_PUSH_SERVICE accepts a Shoutrrr URL or an HTTP/HTTPS URL template. Supported Shoutrrr families include Generic Webhook, Bark, Discord, Gotify, Google Chat, IFTTT, Join, Mattermost, ntfy, OpsGenie, Pushover, Pushbullet, Rocket.Chat, Slack, Microsoft Teams, Telegram, and Zulip. Matrix and SMTP are not supported and there is no fallback to the old executable.
What input formats can Sub-Store convert?
It accepts proxy URI schemes including socks5, socks5+tls, http, and https, URIs for AnyTLS, SOCKS, SS, SSR, VMess, VLESS, Trojan, Hysteria, Hysteria 2, TUIC v5, and WireGuard, Clash Proxies YAML, Clash proxy JSON/JSON5/YAML, and client-specific formats for QX, Loon, Surge, and mihomo. HTTP(s) has no standard URI format and is not supported as a URI input.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sub-store-org-sub-store)Star history chart for your README
[](https://hysenlabs.com/projects/sub-store-org-sub-store)Was this useful?