Sukka rulesets split by client syntax, and rule order decides whether DNS resolution happens
Rule Snippet & Rule Set for Surge / Mihomo (Clash.Meta) / Clash Premium (Dreamacro) / sing-box / Surfboard for Android / Stash
At a glance
- What is it?
- Sukka Ruleset is a set of rule files for Surge, Mihomo, Clash Premium, sing-box, Surfboard, and Stash, served from a Cloudflare-backed host with a mirror. The part that matters most is not the lists but the order: put an IP rule before a domain rule and the DNS protection disappears.
- Who is it for?
- This ruleset fits someone running Surge, Mihomo, sing-box, or Stash who wants maintained domain and IP lists rather than hand-built rules, and who will follow the documented ordering.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
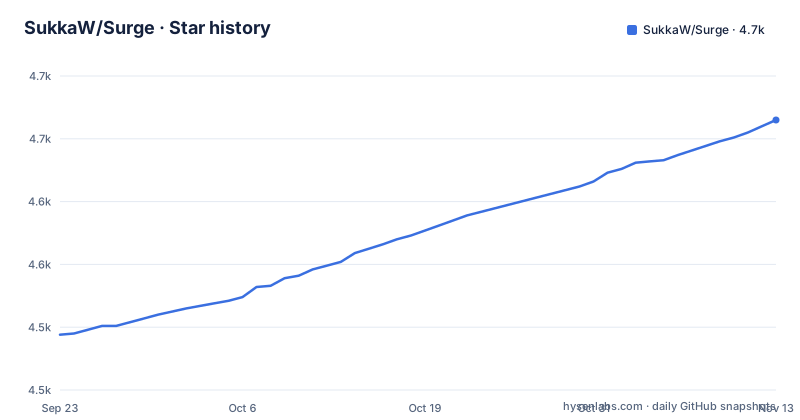
- SukkaW/Surge4,665 ★ · +171
| Repository | 2026-09-23 | 2026-11-13 |
|---|---|---|
| SukkaW/Surge | 4.5k | 4.7k |
171 Stars in the last 51 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Directory names follow each client's rule syntax
The layout mirrors the clients rather than the data. For Surge on Mac, iOS, and tvOS there are three directories: /List/domainset/ holds DOMAIN-SET groups that do not trigger DNS resolution, /List/non_ip/ holds RULE-SET groups that do not, and /List/ip/ holds RULE-SET groups that do. Mihomo has the same three-way split under /Clash/, with behaviors named precisely, domain and text for domainset, classical and text for non_ip, and classical or ipcidr with text for ip. sing-box exposes one rule format, Headless Rule, with its own three directories under /sing-box/. Stash is listed among the supported clients alongside Surge, Mihomo, Clash Premium, sing-box, and Surfboard. So the first decision when adding a list is which client you run, and the second is whether that list needs DNS resolution.
Two clients are told to reuse another client's format
The project does not build every combination, and says so rather than leaving you to guess. For Clash Premium from Dreamacro there is no separate DOMAIN-SET format under /LegacyClashPremium/domainset/, and the instruction is to use the Mihomo domainset groups under /Clash/domainset/ instead, with the note that behavior and format are the same. For Surfboard on Android there is likewise no separate /Surfboard/domainset/ DOMAIN-SET, and the instruction is to use the Surge groups under /List/domainset/. The non_ip and ip directories are provided for both clients: classical and text (or ipcidr and text for IP groups) for Clash Premium, and RULE-SET for Surfboard. Fewer files to fetch is the benefit, and the cost is that you have to know which directory belongs to which client before you start.
Order is what decides whether DNS resolution runs
The most heavily emphasised requirement in the documentation is an ordering rule. Rule groups must be added following domainset, non_ip, and ip, and every domainset or non_ip group, along with your own DOMAIN, DOMAIN-SUFFIX, and DOMAIN-KEYWORD rules, must be placed before all ip groups and your own IP-CIDR, IP-CIDR6, IP-ASN, and GEOIP rules, with no exceptions. The stated reason is mechanical. Surge, Clash, Mihomo, and Surfboard match rules from top to bottom, and DNS resolution only happens when IP type rules are being matched, or at FINAL, or on the direct policy. Put an IP rule too early and the domain rules below it never get the chance to short-circuit, so the protection these lists are designed to provide is gone immediately, and the documentation says you end up exposed to DNS pollution. This is the one line worth reading twice before you edit a config.
The reject group is layered, and the extra layer needs the base
Ad blocking, privacy, malware, and phishing blocking are auto-generated, with the data sources, allowlist domains, and generation method pointed at build-reject-domainset.ts. The Surge configuration is layered rather than a single list:
# Non IP
RULE-SET,https://ruleset.skk.moe/List/non_ip/reject-drop.conf,REJECT-DROP,pre-matching
DOMAIN-SET,https://ruleset.skk.moe/List/domainset/reject.conf,REJECT,extended-matching
DOMAIN-SET,https://ruleset.skk.moe/List/domainset/reject_extra.conf,REJECT
RULE-SET,https://ruleset.skk.moe/List/ip/reject.conf,REJECT-DROP
The comments describe a base set of 120 thousand blocked domains, an extra 90 thousand that is a supplement and has to be enabled together with the base, and a phishing list of 130 thousand domains which appears commented out in the example. So phishing blocking is off unless you uncomment it, and the extra list does nothing on its own. The IP layer is separate and goes after the domain layers, as the ordering rule requires.
Surge 5 is the condition on enabling both domain layers
One comment in the example configuration carries a version condition that decides a practical question. It says that on Surge 5 for Mac, or a newer version, enabling the base and the extra reject domain sets at the same time will not cause a drop in matching performance or excessive memory use. That is stated as a property of the newer client, not of the lists, which means the same configuration on an older Surge has a different cost profile. The project also limits where these groups are recommended at all, saying they are only suggested for Surge for Mac and that mobile platforms should use dedicated tools such as ADGuard for Android or iOS for better performance. It also states plainly that the rules cannot replace a browser ad-blocking extension such as AdGuard for Browser, so this is not a full replacement for anything on the device.
Mihomo providers are plain HTTP text with a twelve hour interval
On the Clash side the same content arrives as rule providers rather than inline rules, and the shape is consistent across groups:
rule-providers:
  speedtest:
    type: http
    behavior: domain
    format: text
    interval: 43200
    url: https://ruleset.skk.moe/Clash/domainset/speedtest.txt
    path: ./sukkaw_ruleset/speedtest.txt

rules:
  - RULE-SET,speedtest,[Replace with your policy]
Every provider is fetched over http as text, cached under ./sukkaw_ruleset/, and refreshed on an interval of 43200 seconds, which is twelve hours. The policy slot is left as a placeholder for you to replace, since the lists have no opinion about which policy a group should use. The rules block then references provider names rather than URLs, and the reject example shows the order that matches the ordering requirement, with the non-IP groups listed before the IP group.
The speedtest and CDN groups exist for specific reasons
Two groups are worth reading before you add them, because each answers a problem the lists would otherwise create. The speedtest group collects speedtest.net endpoints through the Speedtest API for dozens of common regions, plus manually maintained endpoints for tools such as macOS netQuality, and its stated purpose is to pin speedtests to one network egress without affecting normal browsing through the main egress. fast.com is deliberately excluded because it shares infrastructure and domains with the Netflix CDN, which would disturb streaming routing. The CDN group holds common static resource and object storage domains, and its documented use is sending that traffic to commercial relay nodes that bill at a low multiplier; it also includes domains absent from global.conf, so it is worth adding even without such a service, assigning the same policy as global.conf.
The build is TypeScript, and the licence field disagrees with LICENSE
The repository is a private TypeScript package named ruleset.skk.moe with build, lint, and test scripts, where tests run through mocha over the Build directory, and dependencies that include an adblocker engine, a public suffix library, and a trie implementation. Licensing is where the metadata and the repository disagree, which matters if you redistribute anything. The package manifest declares ISC, while the root LICENSE and the documentation describe AGPL-3.0 for everything except the List/ip/china_ip.conf file, which is shared under CC BY-SA 2.0. The documentation also states there is no warranty of any kind, that authors and contributors give no technical support, and that they accept no liability for losses. If you are using a commercial public proxy service, the documentation adds a warning to read your provider's terms, since some treat the use of third-party rule files as giving up service levels and support.
Editorial conclusion
This ruleset fits someone running Surge, Mihomo, sing-box, or Stash who wants maintained domain and IP lists rather than hand-built rules, and who will follow the documented ordering. It may not fit a user of a commercial public proxy service whose terms treat third-party rule files as giving up SLA and technical support, which the project warns about explicitly, and it does not fit someone who expects support: the terms state that authors and contributors provide no technical support and accept no liability. Before you point a client at ruleset.skk.moe, check three things: the licence, which is AGPL-3.0 except for the china_ip list under CC BY-SA 2.0; the ordering in your own configuration, since an IP rule placed early removes the DNS resolution behaviour these lists depend on; and whether the hosted server is acceptable to you, since fetching from it means agreeing to the project's privacy policy, and the alternative is building the lists from source.
Frequently asked questions
How do I add the Sukka ruleset groups to my configuration?
Follow the order domainset, non_ip, and ip, and place every domainset or non_ip group, plus your own DOMAIN, DOMAIN-SUFFIX, and DOMAIN-KEYWORD rules, before any ip group and before your own IP-CIDR, IP-CIDR6, IP-ASN, and GEOIP rules. Clients match rules top to bottom and only resolve DNS when matching IP rules, at FINAL, or on the direct policy, so an IP rule placed early removes that protection.
Which rule group format should Clash Premium users take?
There is no separate DOMAIN-SET output under /LegacyClashPremium/domainset/. The project points those users at the Mihomo domainset groups under /Clash/domainset/, which have the same behavior and format. The non_ip and ip directories are provided for Clash Premium as classical and text, with ipcidr and text for the IP groups.
Can I block ads with these rules on Android?
The project recommends the reject groups only on Surge for Mac and suggests dedicated tools such as ADGuard for Android and iOS for mobile performance. It also states that these rules cannot replace a browser ad-blocking extension such as AdGuard for Browser.
What does the sogouinput rule group do?
It is maintained by hand and blocks the domains the Sogou input method uses to send back what you type, such as get.sogou.com/q. The project notes that this affects Sogou input method account sync, dictionary updates, and problem feedback.
Where can I get the rule files if ruleset.skk.moe is slow?
ruleset.skk.moe is powered by Cloudflare and access from mainland China is not ideal in speed or stability, so an official mirror at ruleset-mirror.skk.moe is provided. If you prefer not to use the hosted server at all, the documentation says you can get the source from GitHub and build the rule sets yourself.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sukkaw-surge)Star history chart for your README
[](https://hysenlabs.com/projects/sukkaw-surge)Was this useful?