Summernote in Detail: Bootstrap Build Targets, base64 Images, and the Code View Warning
Super Simple WYSIWYG Editor
At a glance
- What is it?
- Summernote is a jQuery WYSIWYG editor that installs with a script tag and a div, targets Bootstrap 3, 4 and 5 through separate builds, and embeds images as base64 inside your content. This walkthrough covers what the three-step install actually commits you to, and the two places where the editor hands a decision to your server.
- Who is it for?
- Summernote suits a content form or admin panel where the authors are internal users, the page already loads jQuery and Bootstrap, and a small amount of stored HTML is acceptable. It does not suit long documents with many images, because those images travel inside the content field as base64, and it does not suit a codebase that treats stored HTML as untrusted without a server-side sanitizer, since the editor will hand back whatever was typed into the code view.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 7 months ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
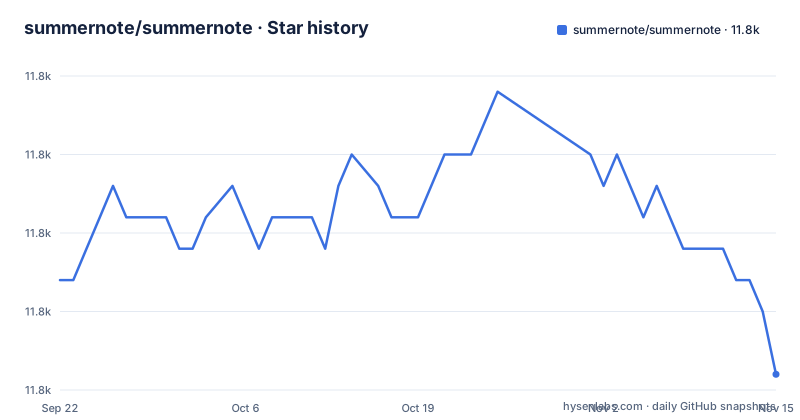
- summernote/summernote11,838 ★ · -3
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| summernote/summernote | 11.8k | 11.8k |
-3 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Bootstrap major version is encoded in the file name
The install snippet loads summernote-bs5.css and summernote-bs5.js beside Bootstrap 5.0.2, and the project also supports Bootstrap 3 and 4, with examples/summernote-bs3.html, examples/summernote-bs4.html and examples/summernote-bs5.html carrying the three variants. Initialization itself says nothing about Bootstrap:
$(document).ready(function() {
  $('#summernote').summernote();
});
The initialization call takes no Bootstrap argument, so the Bootstrap major version is decided by which asset you load; the sensible rule is that the number in the file name should match the Bootstrap major version you included.
The div you place is replaced, not upgraded in place
Step one is the script and stylesheet block, which the README says goes in the head tag:
<!-- include libraries(jQuery, bootstrap) -->
<script type="text/javascript" src="//code.jquery.com/jquery-3.6.0.min.js"></script>
<link rel="stylesheet" href="//cdn.jsdelivr.net/npm/[email protected]/dist/css/bootstrap.min.css" />
<script type="text/javascript" src="//cdn.jsdelivr.net/npm/[email protected]/dist/js/bootstrap.bundle.min.js"></script>

<!-- include summernote css/js-->
<link href="summernote-bs5.css" rel="stylesheet">
<script src="summernote-bs5.js"></script>
Step two is a single element:
<div id="summernote">Hello Summernote</div>The page states plainly that this element will be replaced with the summernote editor. Replaced, not wrapped. The node you wrote in the template is not the node users interact with afterwards. The page offers no destroy or teardown example, so returning the page to a plain editable div is left to your own code.
The code view returns raw HTML and the warning sits with your server
Reading the editor's content is a single string argument:
var html = $('#summernote').summernote('code');Whatever that returns is what you post to your backend, and the page attaches an explicit warning to it: the code view allows the user to enter script contents, so the HTML must be filtered and sanitized on the server, otherwise an attacker can inject arbitrary JavaScript into clients. The wording matters for how you design the feature. This is not a bug in the editor and not something a client-side configuration can close, because the code view is a supported feature and the injection path is the intended escape hatch for raw markup. So the responsibility lands on the write path and the read path: sanitize before storing, or you persist a payload, and sanitize again before rendering, or you execute it for whoever opens the record. Two consequences follow. Any editor instance whose users are not already trusted with script tags in content is a stored cross-site scripting risk until the server filter exists. And an audit of an existing Summernote deployment should start at the save handler.
Base64 images move the whole payload into your content field
Image handling is described as automatic: images are embedded in the content using base64 encoding, which eliminates the need for separate image management. That is a real convenience for a simple form, since there is no upload endpoint, no file table and no cleanup job to run. The cost sits in the data instead. Base64 encodes three bytes of binary as four characters, so every image inflates by about a third before it is stored, and it is stored inside the same field as the text. That field now travels on every save, and on every API read, so a document with a handful of screenshots turns into a payload large enough to dominate the request. The same inflation applies to whatever column holds the content: a schema with a varchar text column sized for prose will reject an image that looks small in the editor, and a schema with a generous text column now holds duplicated image bytes that no garbage collection reclaims when the image is deleted from the editor. The page describes only the base64 path and points elsewhere for plugins and connectors, so any upload-handler alternative is something you assemble outside the core.
Nine npm scripts, Node 17 minimum, and a Yarn-only lockfile
The package manifest pins the toolchain more tightly than the install page suggests:
"engines": {
    "node": ">=17.0.0"
},
and the script list shows how the project is built:
"scripts": {
    "dev": "vite --config vite.config.dev.js",
    "prebuild": "node ./scripts/build-fonts.js",
    "build": "vite build",
    "buildall": "yarn prebuild && node ./scripts/build-all.js",
    "lint": "eslint src public/plugin public/lang test scripts",
    "test": "vitest run",
    "test:watch": "vitest",
    "prepublishOnly": "pinst --disable",
    "postpublish": "pinst --enable"
}
Three things follow. A separate buildall target runs the prebuild step and then scripts/build-all.js. The prepublishOnly and postpublish pair disables and then re-enables install hooks around publishing. And the repository ships .yarnrc.yml, a .yarn directory and yarn.lock rather than a package-lock, so anyone reproducing a contributor build needs Yarn, not npm. Note also that "main" points at dist/summernote.js and the package is declared as an ES module, which is what you consume rather than src/.
Version 0.9.1 shipped in 2024 while main has moved since
The manifest says version 0.9.1, which matches the most recent tag, dated 2024-10-09, preceded by v0.9.0 on 2024-09-28 and v0.8.20 on 2021-10-14. That sequence is worth reading closely, because the gaps are uneven: more than two years between 0.8.20 and 0.9.0, then two more years with no tag since. The repository itself is not idle, since the last push to the main branch is dated 2026-04-15, which means work has landed that no release carries. So the version on the registry is a poor proxy for how current the code is, in either direction: a green test suite against 0.9.1 does not cover what is on main, and main is not something you can pin to. Two smaller signals point the same way. The coverage badge in the README is configured against branch=develop while the default branch is main, so the badge can describe a branch that is not what most people clone. And funding runs through OpenCollective, and the README describes the project as maintained by the community. Anyone depending on this should confirm which branch their build actually came from.
One documented API call, twenty-four example files
The API section on the page is a single line, and everything else is deferred to the documentation:
var html = $('#summernote').summernote('code');The real surface is visible in examples/, which holds twenty-two example pages besides its index, stylesheet and README: airmode.html, codemirror.html, custom-style.html, external-api.html, external-codemirror.html, hint-emoji.html, hint-math.html, hint-userdefine.html, hint-words.html, history-limit.html, jquery-custom-event.html, lang.html, link-blank.html, mode-switcher.html, ondialog.html, ondialog-multitab.html, placeholder.html, plugin-hello.html, recordEveryKeyStroke.html, plus the three Bootstrap variants. Read as a list, that is the feature set the README does not narrate: an air mode for distraction-free editing, CodeMirror as the code view, dialog behavior with and without multiple tabs, a history limit, per-keystroke recording, language packs, placeholder text, a link target default, user-defined hints alongside math and emoji hints, and a plugin entry point. None of the configuration keys behind those files appear on the page. The practical consequence is that anyone evaluating Summernote for a specific requirement, say an undo depth limit or a language pack, has to read the example file to discover whether the option exists and what it is called, since the readme answers none of it.
Editorial conclusion
Summernote suits a content form or admin panel where the authors are internal users, the page already loads jQuery and Bootstrap, and a small amount of stored HTML is acceptable. It does not suit long documents with many images, because those images travel inside the content field as base64, and it does not suit a codebase that treats stored HTML as untrusted without a server-side sanitizer, since the editor will hand back whatever was typed into the code view. Before adopting it, check three things: which Bootstrap major version your page already ships so you load the matching build, whether your content column can absorb base64 payload growth, and what version you are actually pinning, because the published package is 0.9.1 from 2024-10-09 while the last push to main is dated 2026-04-15. The project is MIT licensed, community maintained, with funding through OpenCollective.
Frequently asked questions
what is summernote
A JavaScript library for building WYSIWYG editors, built on jQuery and licensed under MIT. Installation means including its JS and CSS on an HTML page and initializing it against a div.
how to add summernote in html
Three steps: include jQuery, Bootstrap and the summernote css and js in the head, place a div such as <div id="summernote">Hello Summernote</div> in the body, then call $('#summernote').summernote() inside a document ready handler. The div is replaced with the editor when it initializes.
how to use summernote
Load the libraries, put a div in the body, and initialize it, then read the editor content with $('#summernote').summernote('code'), which returns the HTML source. The page points to the project website for more examples and to the documentation for the rest of the API.
summernote is not a function
Summernote is a jQuery plugin, so the method only exists once jQuery and the summernote script have both loaded. The example page loads jQuery 3.6.0 and summernote-bs5.js in the head and makes the call inside $(document).ready, so load order and library presence both matter.
is summernote free
Yes, it is MIT licensed, with the LICENSE file at the root of the repository. The page describes it as community maintained and funded through OpenCollective, where companies can become sponsors and individuals can become backers.
is summernote open source
The source is in the repository under src/, with public/, test/, scripts/ and examples/ alongside it, and contributions are handled through the CONTRIBUTING.md file in .github. The package version is 0.9.1 and the license field in package.json reads MIT.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/summernote-summernote)Star history chart for your README
[](https://hysenlabs.com/projects/summernote-summernote)Was this useful?