treg is a credential broker with three licence answers
OpenRouter for agent tools. Join community here: https://discord.gg/6mQYYfFMAn
At a glance
- What is it?
- A registry and proxy that injects credentials into outgoing requests so agents never hold keys, where the page names the operator's own subscriptions as the funded accounts, the three distribution manifests give three different licence answers, the base install pulls an analytics package, and request bodies can be archived to object storage.
- Who is it for?
- treg is worth understanding if you run agents that need paid third-party data, because the vocabulary is precise about what a registration contains and the precedence rule between your key and the shared one is stated plainly. Two things to settle before you use a hosted instance.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
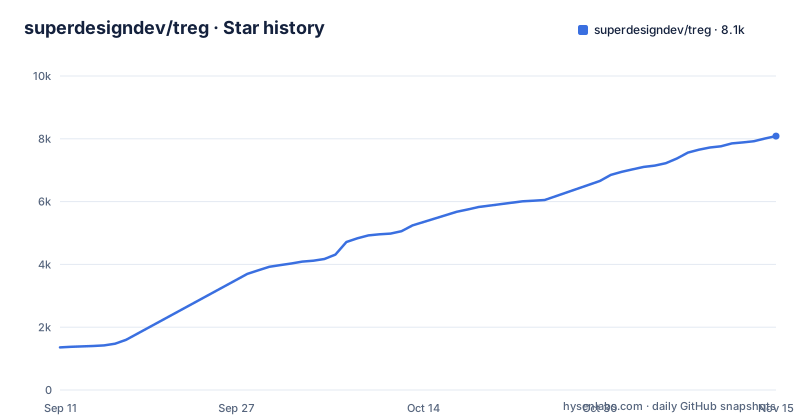
- superdesigndev/treg8,085 ★ · +6,727
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| superdesigndev/treg | 1.4k | 8.1k |
6,727 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The product is a secrets broker, and the page names whose accounts fund it
The stated rule is the whole architecture in one sentence: the proxy relays, never models, the upstream, and injects auth server-side, so it survives upstream API changes and callers never hold keys. The page is also explicit about what that means in money. The tools an agent needs for real work sit behind subscriptions nobody buys for a single run, and four are priced on the page, a search and marketing suite, a domain authority one, a company database one and a contact database one, the last per seat. treg carries those accounts and bills fractions of a cent per call. So the funded side of the catalogue is the operator's own subscriptions, and the page says so rather than implying a partnership.
Three manifests, three licence answers
The same project is published three ways and does not answer the licence question the same way in each.
"license": "Apache-2.0"That is the Node package for the plugin bundle. The Python distribution, which is the actual server and command line tool, does not name a licence in its metadata at all; it points at a file. And its classifier list contains a line reading Other/Proprietary License, which sits directly alongside the metadata's file reference. The repository's own licence field then records no recognised value either. A project whose job is holding other people's API credentials cannot afford ambiguity about its own terms, and this is the first thing to sort out before reading anything else.
The unit of registration is a credential binding
The vocabulary section is where the security model actually lives. A tool is something the registry calls for you with the organisation's credential, and it comes in two kinds. An endpoint is an upstream base URL plus credential bindings, where each binding injects one secret into the request, and a request can carry several, with the page's example being an OAuth bearer and a developer-token header together. A CLI is a vendor binary, named examples being a payment processor, a forge's client and a deployment tool, run with the credential injected. A skill or bundle is a recipe file plus its secrets plus its tools, registered as one thing. One precedence rule governs all of it: your own key always wins over the registry's, and those calls are never metered.
The base install is three packages, and one of them is analytics
The split between the command line tool and the server is deliberate and explained in a comment: the base install is meant to stay light and pure Python so the ordinary install and the Homebrew route are fast, while everything needed to run a registry lives in an optional extra.
dependencies = [
    "httpx>=0.27,<1",
    "posthog>=7.47.3",
    "questionary>=2.0",
    "toon-format==1.2.0",
]
Four packages for the client side, one of which is a product analytics service rather than something the tool needs to reach an endpoint. The server extra then adds at least ten: a web framework, an ASGI server, two SQL layers, two database drivers, a cryptography library, a migration tool, settings and YAML. So the lightweight path is genuinely light, and it also ships an analytics package.
The Python floor is duplicated in a shell script
The version constraint carries a note about its own maintenance.
requires-python = ">=3.12,<3.14" # keep in sync with PYREQ in src/treg/web/install.shSo the supported interpreter range is declared twice, once in the Python manifest and once inside a shell script served by the web tier, with a comment asking a human to keep them aligned. Nothing enforces it. The install surface is wider than that, though: a script fetched over HTTPS and piped into a shell, a marketplace plugin install for one coding agent, and an add command for the other agents.
Request and response bodies are archived to object storage by default
The example environment file describes a body archive layer. Four blank variables hold an object store endpoint, a bucket, an access key and a secret, under a comment saying to supply them privately and never commit populated values. Then come switches for where bodies are written and read: writes accept a database, both, or the object store, and reads accept the database or the object store first. A read timeout is documented as defaulting to two seconds, with the upload keeping its own. There is a per-endpoint cache ceiling, and a separate read-only replica data source whose comment says plainly that you must provision and synchronise it yourself because the URL does not replicate data. The file also says that omitting these switches retains the default db behaviour.
One of the four workflow skills modifies the agent itself
Six workflow skills are listed and most are recipes for using the catalogue. One is different. It gives a coding agent a memory, described as a modification in which a named component judges each prompt after the turn and keeps lasting preferences, installable ready-made or built from a single prompt. It is also opt-in: install.sh installs only the treg skill by default, and jev-memory is never included in --skills all.
Thousands, or exactly 2,896
The prose says a curated catalogue of thousands of endpoints across many providers. The package description says 4,000+ agent-friendly tools, which is harmless in itself but worth noting next to the other claims on the same page. The root directory is where the project's shape shows. There are seven separate agent and tooling surfaces: an agent instructions file and directory, a coding-agent instructions file, a plugin marketplace directory, a second plugin directory, a cursor plugin directory, and a general plugins directory. There is a secret scanner with both a configuration file and an ignore file, which is a reasonable pair of things to have in a product that exists to hold secrets.
Editorial conclusion
treg is worth understanding if you run agents that need paid third-party data, because the vocabulary is precise about what a registration contains and the precedence rule between your key and the shared one is stated plainly. Two things to settle before you use a hosted instance. The design assumes a server you trust holds your secrets and injects them for you, so read that instance's terms before registering a credential that matters, and find out where request and response bodies are kept. If you self-host, note that the Python version floor lives in two files that have to be kept in step by hand.
Frequently asked questions
What is treg?
A registry and credential-injecting proxy that lets one base URL and one token reach many paid third-party endpoints, covering search and backlink data, social and trend data, company and contact enrichment, ads, scraping, and image and video generation, billed per call from a cent. It also serves tools a team registers itself. The page says it was built for one team and that anyone can self-host.
Does treg need an account with the data provider?
Not for the catalogue. The page says external endpoints can be served with the registry's own key or through a verified public route that needs no provider key, so no account with the vendor is required. Calls made with your own registered key take precedence and are never metered, and new verified accounts receive a small free balance once when they create an eligible team.
Where do my API keys go?
Into the registry, as credential bindings attached to a tool, and the proxy injects them into outgoing requests server-side. The page's stated rule is that the proxy relays rather than models the upstream and that callers never hold keys. Your own key always wins over the registry's, and calls made through it are not metered.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 0 in the last 30 days; newest first.
- Treg (OpenRouter for Tools)Hacker News · Oct 6, 2026 · 46 points · 11 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/superdesigndev-treg)Star history chart for your README
[](https://hysenlabs.com/projects/superdesigndev-treg)Was this useful?