Surge binds its HTTP API to every interface unless you pass one flag, ships a Windows executable in the repo root, and versions its extension separately
SurgeDM is a Go-based terminal UI download manager with a TUI interface, background headless server mode, and automation-focused CLI controls for power users.
At a glance
- What is it?
- SurgeDM/Surge is an MIT-licensed Go download manager with a terminal interface, a headless server mode and automation commands, at v0.12.2 with the last push on 2026-10-03. The remote control section is the one to read before you start it on a network, and the repository layout has a couple of things in it that no section explains.
- Who is it for?
- Surge is worth trying if you want segmented parallel downloads with mirror failover and a queue shared across terminal tabs, and the CLI plus token model is what makes it scriptable. Two things to check before you run it anywhere shared.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 6 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
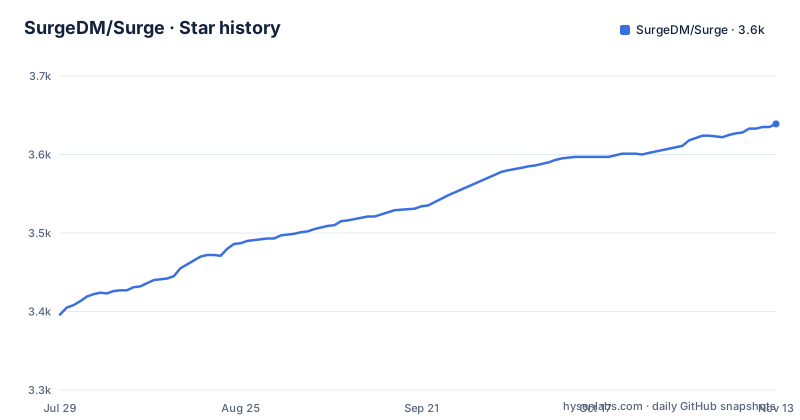
- SurgeDM/Surge3,639 ★ · +243
| Repository | 2026-07-29 | 2026-11-13 |
|---|---|---|
| SurgeDM/Surge | 3.4k | 3.6k |
243 Stars in the last 107 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Both commands listen on every interface by default
The Remote TUI section is four sentences and it is the most important one in the file for anyone deploying this.
It states that both the interactive command and the server command bind the HTTP API to all interfaces, and that this means the server is reachable on the loopback address as well as on your local network address. The API is protected by a token.
So the default posture is a network-exposed control surface whose only protection is a bearer token. That is a defensible choice for a tool that also ships a browser extension, since an extension in your browser needs to reach a local process, and loopback alone would not cover a phone on the same wifi.
It does mean the security model is entirely the token. The README does not describe token generation policy, default value, rotation, rate limiting, or what the endpoints can do beyond queueing downloads. Token management gets its own subcommand, and a second one for when the process is running as a system service, because that is a different context.
The visible file cuts off in the middle of the sentence telling you where else to find the token in the interface, so the full set of lookup locations is not visible here.
The one flag that keeps it local also disables the remote commands
There is exactly one flag that changes the exposure, and it has a cost the README states explicitly.
surge --no-serverThe description says this keeps the interface fully local and skips the embedded HTTP API. The next sentence is the important one: CLI control commands such as the add and pause commands, and browser-extension requests, will not be able to target that instance.
So the flag is not a network binding option. It removes the API, and with it everything that talks to the API. You get a local-only interface, or you get a queue you can drive from another tab, a script or an extension. There is no middle setting described in the file, such as binding to loopback while keeping the API enabled.
That matters if you have scripts. A user with a working script calling the pause command loses it by adding one flag, and a user who wants remote control has to accept the all-interfaces binding.
The daemon design is what makes remote control useful in the first place. The README describes a single background engine that many terminals can queue into, so the API is not an incidental feature but the mechanism behind the multi-tab workflow.
Paste a copied cURL command and it becomes a download
Inside the interactive interface there are two inputs beyond typing URLs.
Pressing the question mark opens a bug reporting wizard from inside the tool.
And pressing a modified A, or using your terminal's paste shortcut, automatically parses a copied browser cURL command straight into a new download.
That second one is the distinctive feature. A cURL command copied from browser developer tools carries not just the URL but the request headers, and a session cookie among them. Creating a download from it therefore carries the browser's session with it, which is what makes it possible to download something that requires being logged in.
It also means the queue now holds credentials, and the file does not say what happens to them: whether they are written to disk, held in memory, or included in any log or exported queue file.
That is the question to ask before using the feature on anything you care about. A download manager that can hold a session cookie is a different kind of program from one that only holds URLs, and the difference is not visible from the feature list.
Two release trains, one for the application and one for the browser extension
The three most recent tags are v0.12.1, v0.12.2 and ext-v2.1.3.
Two belong to the application and carry a plain version prefix. The third belongs to something else, with a prefix naming an extension component and its own independent version line.
So this repository ships two artefacts on two schedules. The application is at 0.12.x, and the browser extension is at 2.1.x, which means the extension is considerably further along its own numbering than the application is on the shared one.
That arrangement makes sense given the design. The extension is the thing that talks to the HTTP API from a browser, and browser extension review and publishing have their own cadence. But it has a practical consequence for anyone automating an upgrade: a changelog that covers the application tells you nothing about which extension you need, and there is no table in the file mapping an application version to an extension version.
The README's structure reflects the split in one place. There is a navigation entry for the extension, and the donation section explains that publishing it officially costs a store fee. The extension directory is at the repository root alongside the application source, rather than in a separate repository.
Eight install routes, three of them Windows package managers
The installation table has eight rows, and the spread is unusual for a young project.
There is a prebuilt binary from the releases page, described as the easiest method. There is a Linux AppImage, with the note that it supports delta updates, and the instructions are to make it executable and run it. There is an Arch Linux package for the AUR helper. There is a Homebrew tap, recommended for Mac and Linux users. There is a Nix route with the run command and the configuration snippet for a NixOS module. There is a Go install route that requires a recent Go toolchain.
Windows gets three rows' worth of options in one cell: a command for the Windows package manager, a command for the Scoop installer, and a command for the Chocolatey package manager.
Three competing Windows package managers for one binary is the kind of coverage that takes work to maintain and is a reasonable signal of adoption. It also means a Windows user has three sources that could be at different versions, and the file does not say which one is authoritative.
The Go install route is worth flagging separately because it pins nothing. It runs at the latest tag, so an installation from source is whatever was published most recently rather than a version you chose.
A Windows executable is committed at the repository root
The top-level listing contains a file with a Windows executable extension, sitting between a scripts directory and a themes directory.
It is the only compiled binary in the root, and no section of the README explains it. It is not referenced by the installation table, not by the development instructions, and not by the release process described in the file.
Two readings are plausible and neither is confirmed by what is visible. It could be a build artifact left in the working tree by a local run on Windows, or it could be something the build system generates and that is committed deliberately. The repository does not say.
What is worth knowing either way is that a binary of unknown provenance sits at the top level of a project whose releases are otherwise distributed as archives and packages. If you are auditing the repository before running anything from it, that is the file to look at first.
The rest of the root is more explicable. There is a release configuration for the build tool, a lint configuration, a Go entry point, a main command directory, an internal directory, and separate directories for the browser extension, for Docker, for themes and for distribution packaging.
Two indirect dependencies are pinned to commits from 2018 and this year
The module declares a recent Go language version and lists twenty-one direct dependencies. Two things in there are worth pointing at.
The first is where the interface libraries come from. The three terminal interface packages are listed under a vanity domain rather than the GitHub path their organisation normally uses, and the ansi and terminal packages from the same organisation are still listed under the GitHub path. So one family of libraries is imported two different ways in the same file, which is what a vanity import migration looks like partway through.
The second is in the indirect block. Two entries carry pseudo-versions rather than release tags. One is a commit from earlier this year belonging to an ultraviolet renderer. The other is a commit from 2018, belonging to a package that is a fork of the more commonly used resize handler, pinned to a seven-year-old revision and never moved.
There is also a goroutine leak detector listed as a direct dependency rather than a test-only one, in a module that is an application. It will not end up in the binary, but it is resolved as part of this module's graph rather than a test module's.
None of this is wrong. It is the sort of detail that tells you the build is current and that at least one dependency has been carried forward deliberately rather than refreshed.
Two students maintain it, and the donation list is three specific invoices
The support section is the most direct writing in the file. It says the maintainers are two computer science students building Surge between classes and exams, that they love working on it, and that maintaining something at that scale takes time and resources.
Then it does something most projects do not, which is list exactly what money would be spent on. Three items, each with a reason.
The first is publishing the browser extension, described as paying the store's one-off fee so people can install it officially rather than sideloading. That tells you the extension exists and is not yet in the store, which matches the release train finding.
The second is developer tooling, naming a paid licence for the release automation tool so they can automate builds.
The third is Debrid integration, described as covering subscription costs so they can test and build native support.
So the file discloses both the funding gap and its cause, and the Debrid line is the one that tells you a feature is planned rather than shipped. Debrid services are subscription-based link resolvers, and integrating one means shipping a dependency on somebody else's account model.
The section closes by saying all of this is optional, because stars, issues and contributions already matter, and the sign-off is a smiley. It is a well-judged ask: three invoices rather than a general request for support.
Editorial conclusion
Surge is worth trying if you want segmented parallel downloads with mirror failover and a queue shared across terminal tabs, and the CLI plus token model is what makes it scriptable. Two things to check before you run it anywhere shared. It listens on every network interface by default and relies on a token as the only barrier, so decide about that before it is on a network you do not control. And note the single flag that keeps it local also disables the remote commands, so the two cannot both be had.
Frequently asked questions
What is Surge download manager?
A Go-based terminal download manager for keyboard-driven use, with a terminal interface, a background headless server mode and automation commands. It opens up to 16 connections per file by default, splits the file, downloads chunks in parallel and fails over between mirrors automatically.
How do I install Surge?
Eight routes are listed: a prebuilt binary, a Linux AppImage with delta updates, the AUR, a Homebrew tap, a Nix flake, three Windows package managers, a Docker Compose setup, or a Go install which requires Go 1.25 or later.
Does the Surge API listen on my network?
Yes. Both the interactive and server commands bind the HTTP API to all interfaces by default, so it is reachable on loopback and on your local network address. The API is token-protected, and the token is retrieved with a dedicated command.
How do I keep Surge on localhost only?
Run it with the no-server flag, which skips the embedded HTTP API entirely. The README notes that CLI control commands and browser-extension requests will then not be able to target that instance.
Can Surge download something that needs a login?
The interface can parse a copied browser cURL command into a new download, which carries the request headers from the browser session. The README does not say whether those credentials are stored on disk, and it does not document the extension's own version line.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/surgedm-surge)Star history chart for your README
[](https://hysenlabs.com/projects/surgedm-surge)Was this useful?