mcp-windbg hands a model cdb.exe and kd.exe, and the redaction is a filter on the way out
Model Context Protocol for WinDbg.
At a glance
- What is it?
- mcp-windbg is a Python Model Context Protocol server that drives the Windows debuggers CDB and KD on behalf of a language model, covering crash dump triage, remote user-mode attaches and kernel sessions. It is a wrapper around two executables rather than an automatic fix, and its own manifest records the incident that shaped its dependency policy.
- Who is it for?
- Use mcp-windbg when the model is doing the reading and you are doing the deciding: it is a way to get structured debugger output into a conversation, not a way to get a fix. Four things are worth checking before you connect it.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 18 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
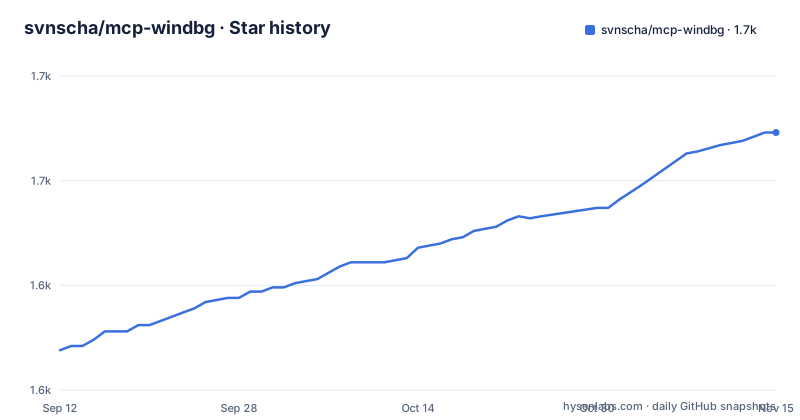
Star history
- svnscha/mcp-windbg1,673 ★ · +104
| Repository | 2026-09-12 | 2026-11-15 |
|---|---|---|
| svnscha/mcp-windbg | 1.6k | 1.7k |
104 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The tool split follows which executable the target needs, not a design choice
The server drives two Windows debuggers and does not abstract them into one. CDB handles user-mode work, which means crash dump files and `-remote` attaches, while KD handles kernel targets reached with `-k` over KDNET, a named pipe or serial. The manifest states the split plainly: user-mode targets, meaning dumps and remote sessions, run under `cdb.exe`, and kernel targets and kernel dumps run under `kd.exe`. The eleven tools are arranged along that same seam, with `open_cdb_dump`, `open_cdb_remote` and `open_kd_session`, `open_kd_dump` on the opening side and a matching `run_` and `close_` pair for each executable.
The README also rules out the reading people bring to this kind of tool. It is not a magical auto-fix, it says, and it describes itself as a Python wrapper around `cdb.exe` and `kd.exe` that lets a model run real debugger commands and reason about the output. Prerequisite is Windows with Debugging Tools for Windows or WinDbg from the Microsoft Store, which ship both executables and are auto-detected. Any MCP-compatible client works, and Python is explicitly not a prerequisite in itself, because each install route names its own.
Two install routes, and only one of them needs Python on the machine
The plugin route is two lines with nothing to configure. It adds the eleven tools with symbols preconfigured, and skills and agents stay separate:
/plugin marketplace add svnscha/mcp-windbg
/plugin install mcp-windbg-uvx@mcp-windbg
What it needs is `uv`, which supplies `uvx` and is installed with `winget install astral-sh.uv`. The plugin uses uvx to fetch the pinned server from PyPI on first use, so there is no `pip install` and no MCP configuration to edit. Symbols come from the same place the WinDbg tooling expects them, through `_NT_SYMBOL_PATH`, which the manual route has to set itself:
pip install mcp-windbg
claude mcp add mcp-windbg -s user -e _NT_SYMBOL_PATH="SRV*C:\Symbols*https://msdl.microsoft.com/download/symbols" -- python -m mcp_windbg
That route requires Python 3.10 or higher. Three plugin packages exist rather than one: `mcp-windbg-uvx` contributes the MCP tools only, `mcp-windbg-skills` adds four optional skills, and `mcp-windbg-agents` adds an optional `crash-analyst` agent, the latter two working either through the uvx plugin or your own MCP connection.
A managed client can skip the bundled plugin without telling you
The quick start opens with a note aimed at enterprise setups, and it is the failure mode worth knowing before debugging a missing server. When managed settings define `allowedMcpServers`, plugin-bundled MCP servers may be silently skipped, with the behaviour tracked as Claude Code issue 32882. Nothing errors, the tools simply are not there, and the natural conclusion is that the install failed.
The advice that follows is to register the server manually and then optionally add the skills or the agents plugin, with one condition attached: the server still has to be permitted by the organization's MCP policy. So a locked-down client has two independent gates, and clearing one does not clear the other. This is also why the manual registration command is written out in full rather than left to the plugin, since it is the path that works under policy control and the path where the symbol path becomes your responsibility.
Every open returns a session id, and sessions of all three kinds can run at once
The addressing scheme is an opaque id rather than a connection handle you manage yourself. Each `open_*` call returns a `session_id`, shaped like `cdb-1a2b3c4d`, and you pass it to the matching `run_*`, `close_*`, `send_ctrl_break` and `wait_for_break` calls. Several sessions can be open at once, covering dumps, remote user-mode servers and kernel targets at the same time, and each is addressed independently, so a kernel session does not have to be closed to open a dump.
Two of the eleven tools exist to widen that surface rather than narrow it. A dump opens with automated triage in a single call, which is `!analyze -v` together with stacks, modules and threads. And an open session accepts arbitrary commands, with `kb`, `!process 0 0`, `!heap` and `lm` given as examples of what can be run from a natural-language request. Parameters, timeouts and the built-in triage prompts are kept out of the README itself and left to a tools reference, so the exact argument list per tool is not something this page answers.
A command that outruns its timeout gets a break instruction, not a wedged session
Live debugging is where a wrapper like this usually falls apart, so the timeout behaviour is designed rather than incidental. Every call carries a timeout, and when a slow live command outruns it, the server does not wait and does not abandon the process: it sends CTRL+BREAK and resynchronizes the session. This is intended to recover the session after a timeout; check target and session state before continuing, especially when debugging a live kernel.
Two tools exist for the same problem from the other direction. `send_ctrl_break` breaks into a session that is currently running, and `wait_for_break` waits for a target you resumed with `g` to stop again, which is the shape of a workflow where you let a hang happen and then catch it. Closing has its own documented effect worth reading before you press it: `close_kd_session` resumes the target machine, so a kernel session does not end in a stopped state you can resume from.
Redaction is a filter on arguments and output, and the debugger still runs
Crash dumps are the reason this exists, and they are also the reason it can leak. A `--filter-script` can be configured to redact sensitive text from tool output, which the scenario table pairs with dumps containing secrets or PII. Its effectiveness depends on the filter's rules; test it with representative data and do not assume all sensitive information is removed. It is not a sandbox around `cdb.exe`, it does not limit which debugger commands can run, and it is not enabled unless you pass it.
Transport is the second half of the exposure surface. The server runs locally over stdio, or as a streamable-HTTP service you drive from another machine, and the second mode is what the remote scenario is built on. Under stdio the client and the debugger share your session. Under HTTP, the debugging host is reachable by whatever can reach that service, and the only thing standing between a caller and a command line is the tool surface described above. Multi-dump triage widens the same surface in a different direction, since `list_dumps` and the comparison path let one request walk a whole directory of dumps.
An unbounded mcp release broke the server at import, so all four dependencies are capped
The manifest carries a comment block explaining its own dependency policy, and the reason is a specific incident rather than a general preference. mcp 2.0.0 landed against 1.0.0 and broke it: an unbounded `mcp>=1.28.1` resolved to the new major and died at import before the server started, and the argument is that this became an install every user had to work around by hand. The stated fix is that a cap turns the same event into a Dependabot pull request that fails CI instead. The justification for capping an application rather than a library is in the same comment, namely that nothing depends on mcp-windbg, so an upper bound cannot cause a diamond conflict for anyone:
dependencies = [
    "mcp>=2.1.1,<3.0.0",
    "pydantic>=2.13.4,<3.0.0",
    "starlette>=1.6.0,<2.0.0",
    "uvicorn>=0.52.4,<1.0.0",
]
Four runtime dependencies, all bounded at the next major, and a `uv.lock` committed beside the manifest so the resolution is recorded. `requires-python` is `>=3.10`, and the classifiers claim Python 3.10 through 3.14 and a Production/Stable status on Windows only.
The default branch is develop, and two releases landed a day apart
Three tags are visible and they are close together. v1.4.0 is dated 2026-09-30, v1.3.1 is dated 2026-09-29 and v1.3.0 is dated 2026-09-09, so a patch and then a minor release landed on consecutive days, with the version in the manifest matching the newest tag. The default branch is `develop`, not `main`, and release mechanics are automated: a release-please configuration, a manifest file for it and a CHANGELOG sit at the root, so the tag names and notes come from commits rather than from a hand-written page. The last push is the same day as v1.4.0.
The repository is documentation heavy in a way that matches the audience: `mkdocs.yml` and `docs/` for the site, `requirements-docs.txt` for it, plus `CLAUDE.md`, `.claude-plugin/`, `plugins/` and `server.json`. The verification side is small and specific. `examples/` holds five C++ files named after the bug class each one produces, `divide-by-zero`, `heap-buffer-overflow`, `invalid-free`, `nullptr-dereference` and `complex-struct-nullptr`, plus a PowerShell build script, so the crash corpus is a set of reproducers to dump and re-analyze rather than a test suite with assertions.
Editorial conclusion
Use mcp-windbg when the model is doing the reading and you are doing the deciding: it is a way to get structured debugger output into a conversation, not a way to get a fix. Four things are worth checking before you connect it. Whatever your client can ask for, it can run, because arbitrary WinDbg and KD commands are a supported operation, so treat the client as debugger shell access. The `--filter-script` hook redacts arguments and output on the way out and does not restrict what the debugger itself may do. Closing a kernel session resumes the target machine, so closing is an action rather than a cleanup. And on the streamable HTTP transport, whoever reaches that endpoint is driving the debugger, which is why the stdio route is the safer default. On Windows you also need cdb.exe and kd.exe from Debugging Tools for Windows or the Store build of WinDbg, plus Python 3.10 or newer unless the uvx plugin fetches the server for you.
Frequently asked questions
What does mcp-windbg give an MCP client such as Claude Code?
It gives it eleven tools that drive CDB for user-mode dumps and `-remote` attaches, and KD for kernel targets and kernel dumps. Each open returns a session id such as `cdb-1a2b3c4d` for the matching run, close, break and wait calls, a dump opens with `!analyze -v` triage in one call, and an open session accepts arbitrary WinDbg and KD commands.
How do I install the mcp-windbg server?
With the plugin, using `/plugin marketplace add svnscha/mcp-windbg` and `/plugin install mcp-windbg-uvx@mcp-windbg`, which needs uv and fetches the pinned server from PyPI on first use. Or with pip, using `pip install mcp-windbg` followed by `claude mcp add mcp-windbg -s user`, which needs Python 3.10 or higher and sets `_NT_SYMBOL_PATH` yourself.
What does mcp-windbg require on the Windows machine?
Windows with Debugging Tools for Windows or WinDbg from the Microsoft Store, since those ship `cdb.exe` and `kd.exe`, which are auto-detected, and any MCP-compatible client. Python is not a prerequisite in itself: the plugin route uses uvx, and only the pip route needs Python 3.10 or newer.
Can mcp-windbg redact secrets and personal data from a crash dump?
Yes, through a `--filter-script` that redacts PII and secrets from tool arguments and from output before either leaves the machine. It is a text filter on the boundary traffic, not a restriction on which debugger commands run, and it only applies when you pass it.
Which mcp-windbg version is current, and are its dependencies pinned?
v1.4.0, dated 2026-09-30, after v1.3.1 on 2026-09-29 and v1.3.0 on 2026-09-09, and the manifest version matches it. All four runtime dependencies are capped at the next major, a policy added after mcp 2.0.0 resolved against an unbounded requirement and killed 1.0.0 at import, which the project tracks as issue 76.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/svnscha-mcp-windbg)Star history chart for your README
[](https://hysenlabs.com/projects/svnscha-mcp-windbg)Was this useful?