Internal All The Things is a list of payloads with no licence attached
Active Directory and Internal Pentest Cheatsheets
At a glance
- What is it?
- Internal All The Things collects Active Directory and internal pentest cheatsheets as MkDocs pages, with a GitHub Pages site as its second face. Its own share text calls it a list of payloads and bypasses for internal security assessments, its contribution model is a pull request against any page, and no licence is recorded anywhere in the repository.
- Who is it for?
- Treat this as a reference index rather than a tool, and read it inside an engagement you are authorised to run, which is the framing the project itself uses.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 91 days ago.
- What is it written in?
- Mainly HTML, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
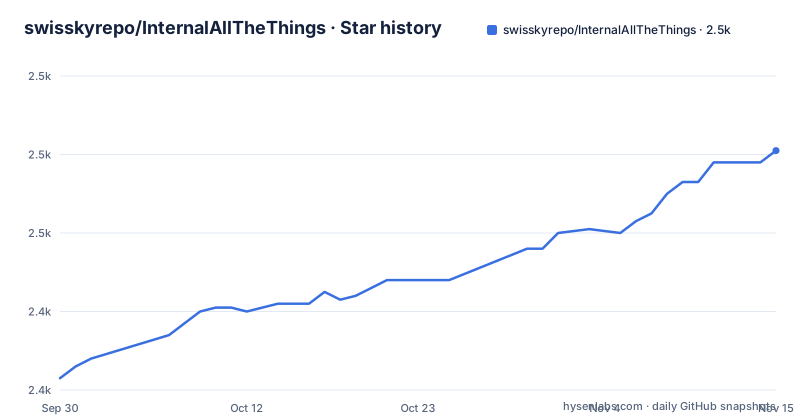
- swisskyrepo/InternalAllTheThings2,481 ★ · +58
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| swisskyrepo/InternalAllTheThings | 2.4k | 2.5k |
58 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The project's own description names payloads and bypasses
There are two self descriptions in this repository and they are worth quoting because they set expectations.
The subtitle under the title is Active Directory and Internal Pentest Cheatsheets. The share link at the bottom of the README carries longer text: a list of useful payloads and bypasses for Internal Security Assessments, attributed to the repository's author.
Both descriptions place the material on the offensive side of an assessment rather than in a defensive toolchain. That is not a criticism of the content, it is the scope the project declares for itself, and it is the frame in which the pages are meant to be used.
The disclaimer is equally direct. Content in the repository is provided as is, for learning purpose, and the author and contributors take no responsibility if you break something. That sentence is the whole of the legal framing, and it is worth reading as what it says rather than as what it might be taken to say.
So the repository does not present itself as a scanner, a framework or a toolkit. It presents itself as a written collection.
One source, two presentations
The README opens by pointing somewhere else before it says anything about itself.
An alternative display version is available at the project's GitHub Pages address, and that is presented as the alternative to reading the repository itself. So there are two ways to consume the same material: the Markdown pages in the repository, and a rendered site.
The repository layout explains why. There is a `docs/` directory holding the content, a `mkdocs.yml` configuration file at the root, an `overrides/` directory and an `assets/` directory. That is the standard shape of a static documentation site, with the theme customised rather than used as shipped, and images kept in one place.
It also explains the recorded primary language. The repository is marked as HTML, which is a strange thing for a pile of Markdown to be, and it makes sense only because the generated site is part of what the repository is for. The repository is not an application; it is a site that happens to be version controlled.
The only quality gate is a pre-commit hook
The root listing holds seven entries, and five of them are documentation related: `.github/`, `README.md`, `docs/`, `assets/`, `mkdocs.yml`, `overrides/` and `.pre-commit-config.yaml`.
That last file is the only tooling in the repository. A pre-commit configuration means hooks run before a commit is created, which for prose means formatting and lint checks on the Markdown rather than a test suite. There is no build script, no package manifest for the site, and no unit test anywhere in the listing, which is a reasonable position for a collection of written reference pages.
The `.github/` directory is where the repository's own automation would live, and it is the entry that would contain issue templates, a pull request template or a workflow if the project used one. The README asks contributors to submit pull requests that update any page, so a template that tells a contributor which pages exist would be more useful than a general contribution guide, which is not present at the root.
What is missing is any statement about how a page gets reviewed. The documentation section asks for pull requests and disclaims responsibility; it does not say who reviews them or what standard they apply.
The landing page is ninety eight words and two image slots
It is worth being blunt about what a first time visitor gets.
The README contains the title, the subtitle, one sentence offering an alternative display version, a documentation section with two bullet points, a contributions heading, a sponsorship line and a social share link. Between them sit two centred paragraph blocks that contain nothing, which in the original are image slots: one for a banner under the description and one for a contributors graphic.
So a reader arriving at the repository learns that the project exists, that there is a website, that pull requests are welcome and that the author can be sponsored. They learn nothing about coverage. Whether Active Directory enumeration, credential attacks, lateral movement or anything else is inside is not stated on the landing page, and the page titles that would answer that live inside `docs/`.
That is a design choice rather than an oversight, and the hosted site exists to compensate for it. It does mean the repository, on its own, cannot be evaluated without opening the site or the content directory.
No licence file, which is unusual for text people copy from
The repository records no licence, and no LICENSE file appears among the top level entries.
For a software project that is common enough. For a document repository whose entire value is a set of commands, queries and configuration snippets that people copy into terminals, it is the one fact that changes how you should use it.
Without a licence grant, the default position is that the text is protected and you have no permission to redistribute it, modify it or publish a derivative. That is not an accusation about the author, who invites pull requests and offers sponsorship, and it may simply mean nobody has added the file. But the practical effect on a reader is the same either way: there is nothing in the repository that tells you what you may do with a page once you have copied it out.
If your use is private reference during an authorised engagement, this is a footnote. If you intend to fork the collection, mirror it, print it into an internal handbook or quote it in a report, the absence has to be resolved with the author first.
Commits without releases, which tells you the update story
There is a maintenance signal here and it is thin.
The last push was on 2026-08-16, the repository is not archived, and it publishes no GitHub releases. So the only record of change is the commit history on the default branch, named `main`.
For a reference collection that is workable. Nobody needs a changelog for a document, and the pages change by being corrected. What it does mean is that a reader cannot tell whether a page describes a current tool version or one from two years ago, and cannot tell without opening the file history for that page. Any command in a pentest cheatsheet ages with the software it targets, and this repository provides no signal about that ageing.
The last structural detail is the contribution channel. Pull requests are the mechanism, the project asks you to update any page with your own knowledge, and the contributors graphic plus a sponsorship link are how the author acknowledges the work. There is no list of maintainers beyond the single author named in the share text, so there is one person to attribute this to when you ask about a page.
Editorial conclusion
Treat this as a reference index rather than a tool, and read it inside an engagement you are authorised to run, which is the framing the project itself uses. Two things decide whether it is useful to you: whether the pages are current for your environment, which the repository cannot tell you because it publishes no releases and its last push was on 2026-08-16, and whether you are allowed to reuse what you copy, which nothing in the repository grants because no licence file and no licence field exist. If either fails for you, treat the output as notes to rewrite rather than material to paste, and verify every command against the target platform before it runs anywhere near a domain controller.
Frequently asked questions
What is Internal All The Things?
A documentation project collecting Active Directory and internal pentest cheatsheets. Its own share text describes it as a list of useful payloads and bypasses for internal security assessments, and it presents itself as written reference material rather than as a tool.
Is there a web version of Internal All The Things?
Yes. The README links an alternative display version hosted at the project's GitHub Pages address. It is built from the repository's docs directory, with mkdocs.yml at the root, an overrides directory for the theme and an assets directory, which is why the repository's recorded primary language is HTML.
How do I contribute to Internal All The Things?
By submitting a pull request that updates any page with your own knowledge. The README states that content is provided as is for learning purposes and that the author and contributors take no responsibility if you break something, and it links a GitHub Sponsorship page.
What licence is Internal All The Things under?
None is recorded. The repository metadata carries no licence and no LICENSE file appears among the top level entries, so there is no stated grant covering reuse, redistribution or modification of the pages.
How current are the Internal All The Things pages?
The last push was on 2026-08-16 and the repository is not archived, but it publishes no GitHub releases, so there is no changelog and no version marker. Ageing has to be judged from the file history of an individual page.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/swisskyrepo-internalallthethings)Star history chart for your README
[](https://hysenlabs.com/projects/swisskyrepo-internalallthethings)Was this useful?