ssrfmap replaces one parameter with 21 payloads, and nothing in its options says which host is allowed
Automatic SSRF fuzzer and exploitation tool
At a glance
- What is it?
- A Python fuzzer that takes a captured request and a parameter name, then substitutes payloads aimed at services the target server can reach but you cannot. The module table is where the real scope question sits: two modules scan, several reach for command execution, and the option list has no allowlist and no dry run.
- Who is it for?
- SSRFmap is a well built tool for the specific job of proving that one parameter in one request can be made to reach somewhere it should not, and it is worth using when you own the target or hold written permission for it. Establish that permission before anything else, and point it at one host, because two of its modules scan rather than read a single response, and the option list offers no allowlist, no dry run and no confirmation.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 97 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
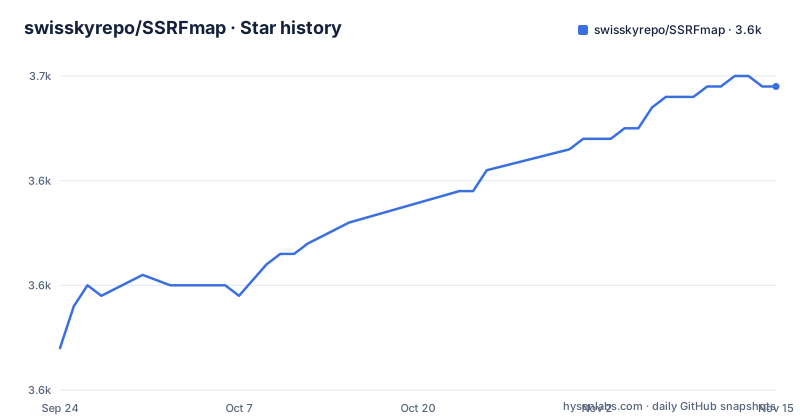
Star history
- swisskyrepo/SSRFmap3,649 ★ · +25
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| swisskyrepo/SSRFmap | 3.6k | 3.6k |
25 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Permission is the first prerequisite and the file never mentions it
SSRFmap takes a Burp request file and the name of one parameter, and replaces that parameter's value with a series of payloads aimed at services the target server can reach. The file's own definition of the flaw is that an attacker forces a server to perform requests on their behalf. Everything the tool does follows from that, and that is exactly why it belongs only in front of a host you own or are authorised to test. Nothing in the documented workflow asks for that: there is no target allowlist option, no dry run, no confirmation prompt, and no note anywhere that the payload list is pointed at third-party infrastructure the moment the target server can be made to fetch. The options line is short enough to read in full, and that absence is the first thing to notice about it.
Four cloud modules share one description, and one module carries a version ceiling
The module table has twenty one rows, and it reads like a maintenance snapshot rather than a maintained reference. Four of the rows, for Alibaba, AWS, GCE and DigitalOcean, carry the identical description: read files from the provider, for example meta-data or user-data. Whatever distinguishes them in the code, the table does not say, so the row you need is the row you have to guess at. Then there is `github`, described as GitHub Enterprise RCE in versions below 2.8.7. That ceiling is the other kind of stale entry. A row that names a vulnerability by its fixed version tells you the module stops working the day the target upgrades, and it says nothing about what the module does against a current installation.
Two of the twenty one modules scan, and the parameter is no longer the boundary
The tool's premise is narrow: one parameter, one request, observe what the server fetches. Two rows break that premise. `portscan` scans the top 8000 ports for the host, and `networkscan` is an HTTP ping sweep over the network, which means not the host but a range of addresses reachable from it. Both are selected through the same module argument as reading a file. So a test scoped to one endpoint can turn into a sweep of a subnet that belongs to somebody else, with no separate authorisation step and nothing in the output to distinguish the two cases. The rest of the option list widens the picture in the same direction: a proxy option, a user agent option, an option whose stated purpose is tweaking payloads to get past IDS and WAF, and listener options for a callback.
The image compiles curl 7.71.0 out of a tarball in the repository
The container is not a thin wrapper. It starts from `python:3.12.4-alpine`, copies the `uv` binary from a pinned `ghcr.io/astral-sh/uv:0.11.8` image, and then does something worth reading twice: it installs a compiler toolchain and builds `examples/curl-7.71.0.tar.gz` from source with `--enable-ares`, under a comment that says the goal is curl with an outdated libcurl. The tarball is committed to the repository, sitting in the same directory as the example request files, and the version it pins is from 2021. Whatever the payload delivery needs that a current Alpine curl will not do, the project has solved it by freezing an old curl and shipping the source archive in git. The locked runtime dependencies are installed afterwards, with the lint and test groups excluded.
uv manages everything, and Flask is a runtime dependency
The GitHub install path is four lines, and three of them are uv rather than pip:
git clone https://github.com/swisskyrepo/SSRFmap
cd SSRFmap/
uv sync --frozen
uv run python ssrfmap.py --help
The manifest pins five runtime dependencies with exact versions, `dnslib`, `dnspython`, `flask`, `requests` and `tldextract`, requires Python 3.12 or newer, and sets `package = false` with lint and test as the default dependency groups. Two of those deserve a second look. Flask is a runtime dependency rather than a test one, because the repository ships a small SSRF service as `examples/example.py` that the test instructions tell you to run locally, so the attacker's own machine hosts the target it fuzzes. And two DNS libraries sit side by side, with `tldextract` there for domain handling. The embedded usage text in the file stops partway through the options list, at the module argument.
Coverage is gated at 80% across two modules
The test configuration is unusually explicit. Pytest collects from `tests/`, with `--strict-config` and `--strict-markers`, and coverage is limited to two targets: `core.requester` and `core.utils`. Branch coverage is on, missing lines are reported, and the run fails below 80%. So the gate that decides whether a change lands is measured over the request plumbing and the utilities, while the repository also holds `modules/`, `handlers/` and `data/` directories that it does not measure. Lint runs ruff with a deliberately narrow selection, E9, F63, F7, F82, I, B and W605, at a line length of 100 targeting Python 3.12. One detail does not line up: the per-file ignore exempts `tests/**/*.py` from S101, a rule the selection never enables.
The examples directory holds request fixtures, a demo server and a vendored tarball
The repository root is compact: `ssrfmap.py` as the entry point, then `core/`, `modules/`, `handlers/`, `data/`, `examples/`, `tests/`, `screenshot/`, `pyproject.toml`, `uv.lock`, `Dockerfile`, `Makefile` and `.dockerignore`. The `examples/` directory does three unrelated jobs at once. It holds ten numbered request files, from `request.txt` through `request10.txt`, that are the tool's own test corpus. It holds `example.py` and `ssrf_dns.py`, the local services the tests are run against. And it holds the curl source archive the container build compiles. Two places in the file itself stop mid-command: the local test sequence ends at a bare `uv run python ssrfmap.py -`, and the last line explains that retrieved files and cloud metadata are saved under `loot` without closing the thought.
Editorial conclusion
SSRFmap is a well built tool for the specific job of proving that one parameter in one request can be made to reach somewhere it should not, and it is worth using when you own the target or hold written permission for it. Establish that permission before anything else, and point it at one host, because two of its modules scan rather than read a single response, and the option list offers no allowlist, no dry run and no confirmation. The rest of the engineering is solid and slightly unusual: dependencies are pinned exactly, the container runs unprivileged, and coverage is gated at 80%. What the gate measures is two modules, `core.requester` and `core.utils`, which is a small fraction of a tool whose value lives in its 21 modules. If you need a scoped scanner rather than a fuzzer, this is the wrong shape of tool. The project is MIT licensed, its manifest version is 0.1.0, and it publishes no GitHub releases, so pin a commit rather than a version.
Frequently asked questions
What does ssrfmap take as input?
A request file passed with `-r`, and the name of the parameter to fuzz passed with `-p`; Burp request files are said to work well with it. By default the selected parameter's complete value is replaced, unless you place the marker `*FUZZ*` where the payload belongs so the saved value around it is kept.
Which modules does ssrfmap ship?
Twenty one, selected with `-m` and combinable with commas. They include DNS zone transfers, six named at remote code execution or command execution against FastCGI, Redis, GitHub Enterprise, Zabbix, MySQL and Postgres, a scan of the top 8000 ports, a network ping sweep, file reads, cloud metadata readers for four providers, and a SOCKS4 proxy module.
What does the ssrfmap coverage gate actually check?
Two modules. The pytest options collect coverage for `core.requester` and `core.utils` with branch coverage, report missing lines, and fail under 80%. Linting runs ruff with the rule selection E9, F63, F7, F82, I, B and W605, at a line length of 100.
Why does the ssrfmap Dockerfile build curl from source?
A comment in it says the point is curl with an outdated libcurl. The image compiles `examples/curl-7.71.0.tar.gz`, which is committed to the repository, after installing build-base, cmake and c-ares-dev, and configures it with `--enable-ares`. Locked runtime dependencies come afterwards, with `uv sync --frozen --no-default-groups`.
How does the ssrfmap container handle privileges and output?
It runs unprivileged, with the entrypoint set to `uv run --no-sync python3`. A `loot` directory is created and handed to uid 1000, with a comment saying downloaded files are written there after privileges are dropped, and the uv cache is pointed at `/tmp/uv-cache` so an unprivileged user can write it.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/swisskyrepo-ssrfmap)Star history chart for your README
[](https://hysenlabs.com/projects/swisskyrepo-ssrfmap)Was this useful?