obsidian-remote ships with authentication off and a page title it forgot to change
Run Obsidian.md in a browser via a docker container.
At a glance
- What is it?
- sytone/obsidian-remote is a container image that runs the Obsidian desktop application inside a virtual desktop base image and serves it to a browser, and the repository is essentially one container file plus a root filesystem overlay. Its environment table documents placeholder basic auth credentials, says plainly that with no password there is no authentication at all, the default page title still names the upstream virtual desktop client it is built on, and the newest tagged release is from 2022 while every command in the documentation uses a floating tag.
- Who is it for?
- Use this image if you want the Obsidian desktop application, with its own plugins, reachable from a browser on a machine that has no desktop, because that is exactly what it is and nothing more. Three things to check before you point anything at it.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 36 days ago.
- What is it written in?
- Mainly Dockerfile, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
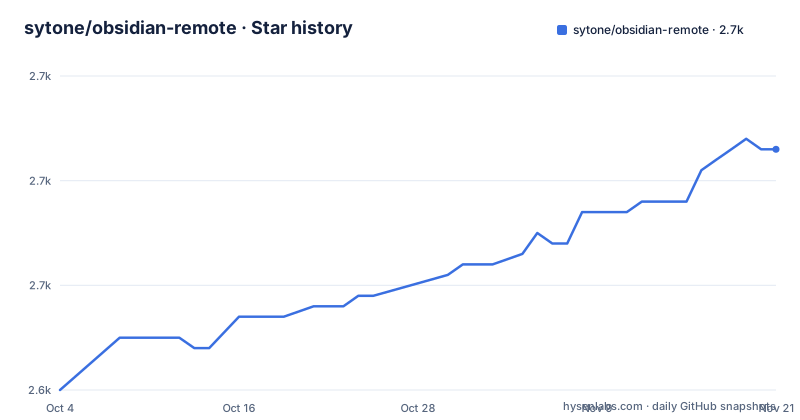
- sytone/obsidian-remote2,663 ★ · +23
| Repository | 2026-10-04 | 2026-11-21 |
|---|---|---|
| sytone/obsidian-remote | 2.6k | 2.7k |
23 Stars in the last 48 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The last numbered release is from 2022 and the docs never pin a tag
The release list has three entries and the newest is from October 2022, while the last commit to the repository is dated September 2026. So the image has been rebuilt many times over four years without a new tag, and every command in the documentation uses a floating tag rather than a version. That is the right default for something people install with a container runtime, and it is also the only choice available here, because there is nothing else to point at. The practical consequence is that a reader who wants reproducibility has nothing to pin, and a reader who wants to compare two deployments a year apart cannot tell from the tags which build each one got. The quickest way in is two volume mappings and one published port:
mkdir -p ob/{vaults,config}
docker run -d \
  -v ./ob/vaults:/vaults \
  -v ./ob/config:/config \
  -p 8080:8080 \
  ghcr.io/sytone/obsidian-remote:latest
The page does compensate in one place, naming the release page and a section on building the image locally, so the escape hatch is documented even though the versioned path is not.
The default is no authentication, with a placeholder pair documented
The environment table documents a basic auth username and a basic auth password, and gives each one's default as the same three letter placeholder. Then it says the important thing in the same row: if the password is unset there will be no auth. The container file agrees with it, setting both variables to empty strings. So a user who follows the quick start gets an application with no authentication, listening on a published port, and the page's own introduction says not to expose it to the web unless you have secured it and know what you are doing. The health check mirrors the same logic, sending credentials only when both are set. It is all consistent and all documented, which is better than most images manage, and the failure mode is still a browser reachable application with your notes in it.
The default page title still names the upstream client
The title environment variable, which is the string the browser tab shows, defaults to the name of a virtual desktop client. That is not so much a typo on this project's part as an inheritance: the container is built on a third party base image for a browser based virtual desktop, and this project keeps its configuration conventions wholesale. You can see it in the variables themselves, since the user and group identifiers default to the values that base image uses, the timezone defaults to universal UTC, the keyboard layout variable takes the layout names that base image documents, and the extension mechanism is that project's own module system with the same name and the same example. That inheritance is also where the project's real portability comes from, and also why one default in the table belongs to somebody else's product.
The whole project is one container file and a root overlay
The repository root holds a container file, a directory whose contents get copied over the image's entire filesystem, an ignore file, an editor configuration, a directory for assets, and the usual repository metadata. That is the project. Everything the image does beyond the base image is expressed as a short list of package installs, a download of the official application image at a pinned version, a handful of environment defaults, and the overlay. There is no build script for the application itself, no compiled code and no test suite, which is why the hosting service records the primary language as a container file. It is a thin and legible project, and the cost is that the interesting decisions all live in the base image's behaviour rather than in this repository.
One build argument produces an AMD or an ARM image
The container file takes the target architecture as a build argument and derives a suffix from it: for the common architecture the suffix becomes empty, and for anything else the architecture name is appended. That single line is what lets the same build produce an image that downloads the right application image, with the architecture appended to the download URL only when it is needed. The application version is a separate pinned argument, so the two axes, version and architecture, are both controlled at build time rather than at run time. That also means updating the application is a rebuild rather than a pull, which is why the documentation has a section on updating it and another on building the image yourself.
Two registries for two architectures, and an apology in both sections
The documentation covers Windows and then Linux, and in both it says the ARM image is now available, that this should be simplified later, and that the ARM image lives on the public registry rather than on the package registry hosting the main image. So there are two registries to remember and two architectures to choose between, which is exactly the friction the sentence apologises for. The two sections also disagree with each other on the tag, since the Windows example names the ARM tag explicitly while the Linux example reuses the floating default tag, which is either a mistake or a difference in what each registry publishes. Anyone copying the Linux block on an ARM machine should check the tag rather than assume the example is right.
The same warning appears twice, in two sets of typos
Both platform sections repeat the ARM note verbatim, which is fine for a page maintained by one person and is the reason the typo count doubles. Across the page the same handful of misspellings recur in the headings and in the environment table: the application name is misspelled three times in section titles and descriptions, the word for the container's group identifier is misspelled, a verb is shortened to three letters, and two other words are each misspelled twice. None of it is worth a reader's time on its own. What is worth noting is where it clusters, because the typos sit in the prose and headings while the tables of ports, volumes and variables are consistent and complete. The documentation is maintained hardest where a machine or a person would otherwise get it wrong.
Editorial conclusion
Use this image if you want the Obsidian desktop application, with its own plugins, reachable from a browser on a machine that has no desktop, because that is exactly what it is and nothing more. Three things to check before you point anything at it. Set a password, because the documented default is a placeholder pair and an unset password means no authentication at all, and the page's own warning about not exposing the port is not a formality. Decide where the vaults and the configuration live on the host, because the second of those volumes also holds the SSH data a git plugin needs. And pin the tag, since the documentation only ever shows a floating one and the last numbered release is several years old, so there is no version to go back to.
Frequently asked questions
how to use obsidian remote
Run the image with two volumes mapped, one for your vaults and one for configuration, publish a port, and open it in a browser. The page gives a PowerShell form and a bash form, each for an interactive run and for a background one.
Does obsidian-remote need authentication?
Not by default. The page documents placeholder values for the basic auth user and password and states that with the password unset there is no authentication, and it warns in the introduction not to expose the port unless you have secured it.
Which ports and volumes does obsidian-remote use?
Two ports, one for plain HTTP and one for HTTPS. Two volumes: one for your vaults, and one that stores the application's configuration together with the SSH data used by a git plugin.
What is obsidian-remote built on?
A third party base image for a browser based virtual desktop, which is where its user identifier, timezone, keyboard layout and extension mechanism come from, with the vendor's official application image downloaded and extracted at build time at a pinned version.
How do I update Obsidian inside obsidian-remote?
The page has a section on updating the application and a separate section on building the image locally. The version it downloads is a build argument pinned in the container file, so updating means rebuilding.
is obsidian remote vault free
The repository is MIT licensed and the image packages the vendor's own published release of the application. The page does not discuss the licensing of the application it ships, so that part is answered by the vendor rather than here.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sytone-obsidian-remote)Star history chart for your README
[](https://hysenlabs.com/projects/sytone-obsidian-remote)Was this useful?