terraform-aws-vpc decides your NAT gateway count with max() across four subnet lists
Terraform module to create AWS VPC resources 🇺🇦
At a glance
- What is it?
- The terraform-aws-modules VPC module is a widely used Terraform building block whose defaults are data dependent rather than explicit: NAT gateways are sized from the longest of four private subnet lists, two NAT flags can be set at once with one silently winning, and the flow log is implemented twice until v7.0.0.
- Who is it for?
- terraform-aws-vpc is a reasonable choice when you want one reviewed module to own subnets, routing, gateways and ACLs instead of writing them by hand, and its NAT topology options cover the three arrangements most teams end up with. Two behaviours deserve a look before you adopt it.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 58 days ago.
- What is it written in?
- Mainly HCL, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
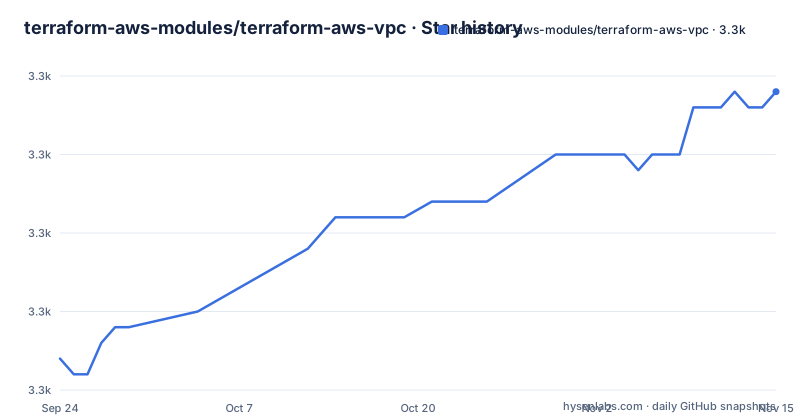
Star history
- terraform-aws-modules/terraform-aws-vpc3,284 ★ · +17
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| terraform-aws-modules/terraform-aws-vpc | 3.3k | 3.3k |
17 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The gateway count is the max of four subnet lists
There is no variable that says how many NAT gateways to build. By default the module takes the max() of the lengths of database_subnets, elasticache_subnets, private_subnets and redshift_subnets, so the longest list wins and the others are ignored for sizing. The README's own example makes the arithmetic visible: two database subnets, two elasticache subnets, five private subnets, two redshift subnets and three intra subnets produce five gateways, because five private subnet CIDR blocks were given. intra_subnets is deliberately excluded from the calculation, because those subnets are designed to have no Internet access through a gateway. Two consequences follow that are not stated anywhere. Adding a subnet to a shorter list changes nothing, while adding one to the longest list creates another gateway and another Elastic IP with no change to any flag. And because the count comes from data, the same module block produces a different infrastructure after an edit that looks cosmetic.
Set both NAT flags and one of them wins
Three topologies are supported, each spelled as a triple of flags. One gateway per subnet is the default: enable_nat_gateway true, single_nat_gateway false, one_nat_gateway_per_az false. A single gateway is enable_nat_gateway true with single_nat_gateway true. One per availability zone is enable_nat_gateway true, single_nat_gateway false, one_nat_gateway_per_az true. The module does not reject the combination of single_nat_gateway and one_nat_gateway_per_az both being true: single_nat_gateway takes precedence, quietly, with no warning. Placement is also decided for you. The single gateway goes into the first entry of your public_subnets list, which means the ordering of that list is load bearing. The per availability zone mode has two stated requirements: var.azs must be specified, and the number of public subnet CIDR blocks must be greater than or equal to the number of availability zones, so that each gateway has a dedicated public subnet. Exceed the AZ count on public subnets and the extra gateways still follow var.azs.
Reusing Elastic IPs means counting them yourself
By default the module provisions new Elastic IPs for the NAT gateways, and when the VPC is destroyed those addresses are released with it. If you want the same addresses to survive a destroy and recreate, you allocate them yourself and hand them in. The README shows an aws_eip resource with count = 3 declared outside the module, then two variables on the module call:
resource "aws_eip" "nat" {
  count = 3

  vpc = true
}
`reuse_nat_ips = true` skips creating addresses, and `external_nat_ip_ids` receives the ids. The count is not derived: it is whatever you typed. Three matches three gateways, which is what single_nat_gateway false with three subnets produces, and with single_nat_gateway true the same resource would only need one. Nothing reconciles the two, so adding an availability zone without raising the count breaks the plan at apply time rather than at review time. The example also uses the older splat interpolation form, "${aws_eip.nat.*.id}", rather than the bracketed list form used in the rest of the module's examples.
The flow log is implemented twice until v7.0.0
A deprecation warning sits directly under the usage example. Version 6.x still supports creating a VPC Flow Log inside the root module, but that behaviour is deprecated and will be removed in v7.0.0, and the recommendation is to use the standalone flow-log module instead. The repository reflects both states at once: there is a vpc-flow-logs.tf file at the root and a modules directory that holds the flow-log module alongside the others. That means the same log can be produced two ways during the deprecation window, and a configuration written against the root resource has a migration waiting for it. The upgrade boundary is stated in the README as v7.0.0 rather than as an open-ended plan, which is the useful part, but nothing in the visible text tells you which arguments move to the submodule or whether the resource address changes.
Intra subnets exist for ENI capacity, not for secrecy
The distinction between private and intra subnets is about how many network interfaces AWS hands out. Private subnets, by default, are given routes for Internet traffic that point at whichever NAT gateways the options above produced. intra_subnets get no Internet routing at all, in the sense of RFC1918 Category 1 space, and the README names the use case: AWS Lambda functions running inside a VPC that only need to reach internal resources or VPC endpoints. The reason to size those subnets generously is stated next: Lambda allocates Elastic Network Interfaces in proportion to the traffic it receives, so a workload with a large address allocation can exhaust a small subnet long before it exhausts a large one. Read that way, intra is not a more private tier of private, it is a place to put functions that should not have a route out. The module does not restrict which subnet variable you use for it, and the NAT calculation ignores intra_subnets entirely, so adding them never changes gateway count.
create_vpc is a leftover from before count was allowed
Conditional creation is documented as a legacy path. Prior to Terraform 0.13 you could not specify count in a module block, so a module whose resources you wanted to skip needed a boolean that its own code honoured, and that boolean is create_vpc. Setting it to false leaves the module call in place with nothing created, which the example shows in three lines. Anyone on Terraform 0.13 or later does not need it, and anyone still on an older release is running a Terraform version old enough that this module's other requirements deserve a second look. Around that, the repository is a plain module with main.tf, variables.tf, outputs.tf, versions.tf and the deprecated vpc-flow-logs.tf at the root, plus a modules directory, docs, wrappers and examples. Releases go through .releaserc.json and land in CHANGELOG.md, and a .pre-commit-config.yaml is present for commit-time checks.
The RDS public access recipe is labelled not for production
One section documents how to give RDS instances public access, and it says in the same sentence that it is not recommended for production. The recipe is five arguments rather than one switch: create_database_subnet_group, create_database_subnet_route_table and create_database_internet_gateway_route for the routing, then enable_dns_hostnames and enable_dns_support. Reading them together, the module is not opening a database to the internet by accident when you enable one of them. It needs the subnet group to exist, a route table for the database subnets, and an internet gateway route on top of that, and DNS support has to be on for the instance to be reachable by name at all. The honest framing is that this is a staging convenience, and the caution is placed before the code rather than after it.
AWS creates the default network ACL after the VPC
The network ACL section explains the ordering constraint rather than the syntax. Once the VPC is created, AWS creates the default network ACL, and that resource is what manage_default_network_acl = true controls, which means the module adopts something AWS made rather than creating it. Each subnet type can also get its own ACL with custom rules, and public subnets get a dedicated one when public_dedicated_network_acl is true, with the rules themselves supplied through public_inbound_acl_rules and public_outbound_acl_rules. That paragraph then breaks off partway through the sentence describing those rule values, so the shape of the rule objects is not shown here. What is clear is the division of labour: one flag for the VPC-wide default that AWS generated, one flag per subnet tier for dedicated ACLs, and two rule inputs for the public tier. The same pattern of managing an AWS-created default is why manage_default_network_acl is a flag rather than an unconditional resource.
Editorial conclusion
terraform-aws-vpc is a reasonable choice when you want one reviewed module to own subnets, routing, gateways and ACLs instead of writing them by hand, and its NAT topology options cover the three arrangements most teams end up with. Two behaviours deserve a look before you adopt it. The gateway count is derived, not configured, so it is the longest of database, elasticache, private and redshift subnets that decides how many you get, and editing the wrong list changes your infrastructure quietly. And the flow log exists in two implementations during the v6 to v7 window, so pick the standalone module now rather than at the upgrade. If you need predictable per-AZ egress cost, or you want to keep Elastic IPs across a destroy and recreate, you have to set those flags yourself: reuse_nat_ips with external_nat_ip_ids, and one_nat_gateway_per_az with var.azs and enough public subnets to match. Check the examples directory before writing your first configuration, because it holds fourteen ready-made ones.
Frequently asked questions
Where can I find a terraform aws vpc example?
The repository ships an examples directory with fourteen named configurations: simple, complete, ipv6-dualstack, ipv6-only, network-acls, secondary-cidr-blocks, separate-route-tables, manage-default-vpc, block-public-access, ipam, outpost, flow-log and issues, each with its own README. The usage snippet in the main README is a third option, a minimal module block with source set to terraform-aws-modules/vpc/aws.
How many NAT gateways does terraform-aws-vpc create by default?
It creates the max() of the lengths of database_subnets, elasticache_subnets, private_subnets and redshift_subnets, so the longest of those four lists decides. intra_subnets are excluded because they are meant to have no Internet access. With single_nat_gateway = true you get exactly one, placed in the first entry of public_subnets.
What is the difference between private and intra subnets in terraform-aws-vpc?
Private subnets get routes for Internet traffic pointing at the NAT gateways, while intra_subnets get no Internet routing, which suits AWS Lambda functions in a VPC that only reach internal resources or VPC endpoints. The README notes Lambda allocates Elastic Network Interfaces in proportion to traffic received, so intra subnets are sized to absorb them.
Can terraform-aws-vpc keep the same Elastic IPs for its NAT gateways?
Yes, if you allocate them yourself and pass them in. Declare aws_eip resources outside the module, then set reuse_nat_ips = true and external_nat_ip_ids to their ids, and the module skips creating addresses. Left at the default, it provisions new Elastic IPs and releases them when the VPC is destroyed.
Is public RDS access possible through terraform-aws-vpc, and is it advised?
It can be enabled with create_database_subnet_group, create_database_subnet_route_table and create_database_internet_gateway_route, together with enable_dns_hostnames and enable_dns_support. The README states plainly that public access to RDS instances is not recommended for production.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 1 in the last 30 days; newest first.
- modules.tf now reviews Terraform module pull requestsdev.to · Nov 4, 2026 · 2 points · 0 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/terraform-aws-modules-terraform-aws-vpc)Star history chart for your README
[](https://hysenlabs.com/projects/terraform-aws-modules-terraform-aws-vpc)Was this useful?