open_oura found that the readiness scores are computed on your phone, not in the vendor's cloud
A Rust toolkit for the Oura Ring (Gen 3/4/5): reverse-engineered BLE protocol, event decoders, and reimplemented data-processing algorithms. Sync, store, and analyze your data locally.
At a glance
- What is it?
- A reverse-engineered protocol and a local client for a health ring you already own, with a claim that changes what the device is: the scores the app shows you are calculated on the handset by a native engine and small neural models, and uploaded, which is why they can be reproduced offline.
- Who is it for?
- The interesting finding here is architectural, not technical. Hardware vendors describe their cloud as the brain; this project read the protocol and the app binary and found the computation on the handset, with the cloud doing storage and sync.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 45 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
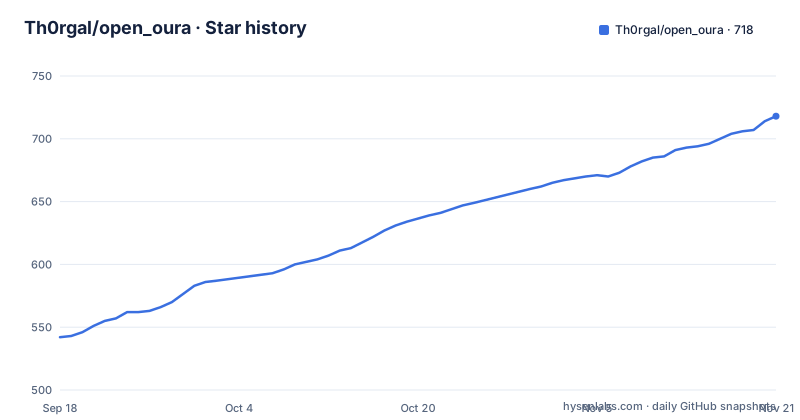
Star history
- Th0rgal/open_oura718 ★ · +176
| Repository | 2026-09-18 | 2026-11-21 |
|---|---|---|
| Th0rgal/open_oura | 542 | 718 |
176 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
It was tested against two real rings, on two hardware generations
The first paragraph of substance is a testing claim, and it is the kind that should be checked before anything else in a project like this. Pairing, authentication and event synchronisation were confirmed live on a Ring 3 in one finish and a Ring 5, and the project is designed for three generations that share the same low-level layout.
Sharing a protocol across hardware generations is not guaranteed and is not the vendor's stated goal, which is presumably why it is called out. A reverse-engineered client that works on one model of a device is a curiosity. One that works across three because the layout happens to be identical is a tool.
The scope is stated as a toolkit rather than an app: reusable libraries plus a small independent client that reads your data straight from the device. Critically, it works with no vendor account at all. If you have ever tried to get your own data out of a consumer health device and hit a login wall, that sentence is the entire pitch.
The companion application and web dashboard built on the same libraries live in a separate repository, which is a sensible split. This one is the protocol and the primitives; the other is a product.
What comes off the device, and what does not
The recovery section is specific about both halves, and the split is what makes this project credible rather than a fishing expedition.
Straight from the device with no account: identifying information, battery, live heart rate converted from inter-beat intervals into beats per minute, the most recent heart rate and blood oxygen readings, and the full history event stream. That stream is where the value is, because it carries the raw photoplethysmography, inter-beat interval, temperature, motion and blood oxygen samples, plus two things you cannot reconstruct from raw samples: the sleep stages the device classifies on its own hardware, activity intensity in metabolic-equivalent levels, and heart rate variability.
What the device does not emit is the set of scores the app displays. Readiness, sleep, activity and stress, all on a zero to hundred scale. And here is the finding: those are not computed in the vendor's cloud either. They are computed on the phone, by a native engine and a set of small neural models, and the cloud only stores the results and hands them back on the next sync.
That is a much more consequential claim than it first reads. If the scores were computed server-side, an offline reproduction would be impossible in principle and any project claiming otherwise would be wrong. If they are computed on the handset, they are reproducible, and this project says they are.
There is exactly one genuine cloud dependency, and it is named rather than glossed: automatic workout classification, which is the one operation that goes to the vendor's servers. Everything else is local. A separate document maps exactly which is which.
The models are excluded on purpose, and the repository says so twice
Here is where the project's self-imposed limit matters, and it is stated in a highlighted note rather than buried in a contributing file.
The neural models that compute the scores are the vendor's proprietary intellectual property and they are not included. They are excluded from version control. The runners in this repository reference them by path, and you are expected to extract and supply your own locally.
That is a line worth respecting. It means the project can show you the pipeline and let you run your own models, without shipping someone else's property or teaching anyone how to obtain it. It also means the reproduction of the scores depends on a file you have to provide, which is the honest trade for not redistributing.
The note ends by saying nothing model-related is committed or pushed, which is the kind of statement that only needs to be made once and only needs to be made at all when the author has thought about it.
The intellectual property boundary here is well drawn and worth naming as a design principle: reimplement the protocol and the engine, reference the proprietary artefacts by path, and do not ship them. A project that had taken the other route would be more convenient for its users and would not survive contact with the vendor's lawyers.
Five crates, one workspace, and a build that strips itself
The repository map is the fastest way to understand the structure. A crates directory holds the Rust client split into five members by concern: protocol decoding, transport, analysis, storage, and the command-line front end.
Splitting decode from fetch is the right seam. A decoder can be tested against a recorded capture with no radio involved, which is how you verify that a byte layout is correct without re-pairing a device every time. Fetch is where the Bluetooth lives. Analysis is where the derived numbers are. Storage is a local database. The command-line binary is a thin layer over the other four.
The workspace file is six lines of substance beyond the member list: a version, an edition, a licence, a repository URL, and a release profile with link-time optimisation on and symbols stripped. The release profile is the only detail that says anything, and it is the correct one for a binary you are going to run next to a wearable.
The Python research bench is separate and deliberately separate in a different way: it exists for protocol exploration rather than for daily use, and its dependency list is two packages, a Bluetooth stack and a cryptography library. Two dependencies for a research tool is a strong signal about what it is for.
Destructive operations are gated three different ways
Any project that can talk to hardware over Bluetooth has a safety problem, and this one addresses it in the documentation rather than leaving it to the reader.
The stated preference is passive, read-only requests. Beyond that, everything that changes the device's state is behind an explicit flag, and the guidance is not to send those during normal use. The reset, the firmware update, the factory reset and the flight mode are all named as gated.
The command-line client requires a second confirmation for the destructive one, a factory reset, which is the pattern that does not get fat-fingered. The Python research bench goes further and hides state-changing and destructive operations entirely unless you pass two separate flags, one to reveal state-changing commands and one to reveal destructive ones. That is a three-stage gate on the most dangerous command, and it is the right design for a tool whose commands can be read off a list.
There is a second layer, in the documentation rather than in the code. A dedicated document describes two verified ways to reset a ring, including one that involves the dock hardware rather than a command, and explains what a reset erases and how to re-pair the device afterwards without handing it back to the vendor's application. That document is the one to read if you own a ring and want it back.
Fourteen documents, and one of them explains how the byte layouts were recovered
The documentation index is longer than the readme, which is the correct ratio for this kind of project, and several entries are worth singling out because they show the method rather than just the result.
There is a protocol cheatsheet for one ring generation covering requests, responses, authentication and features. There is a document on reversing the mobile application itself, covering internal constants, the authentication operations, key generation and nonce encryption. There is a document on how each data channel is fetched and when, plus a minimal recipe for a client that only wants the essentials.
The one that makes this a research project rather than a code drop is the native decoder document, which explains how the event-body decoders were ported from a native library inside the application, including how the byte layouts were recovered with a disassembler. Read that document if you want to know whether the decoders are guesses or derivations. They are derivations, and the document shows the derivation.
Two documents document negative results, which is rarer and more valuable. One covers the firmware update path and states plainly why the firmware signing key is unreachable, because it is resident on the device and not brute-forceable. The other is a set of security observations with an explicit scope note: findings only, the what and not the how, no keys, no endpoints and no procedures.
That last scope note is the right editorial decision. Publishing a finding without a procedure leaves the vendor able to fix it without telling everyone who read the disclosure exactly how to exploit it first, and it is the difference between a security disclosure and a tutorial.
Using it, and the permission you will be asked for
The quick start for the Rust client is three commands: build in release mode, scan for nearby devices, then read device information with a key file.
cargo build --release
./target/release/oura scan
./target/release/oura --key-file key.hex info
The longer command list is in the crates documentation and includes pairing, synchronisation, live heart rate, accelerometer data, feature inspection, raw data, the event stream, a re-decode path for reprocessing stored events, a sleep analysis command, and a subscription mode with a matching status command.
The re-decode command is a good sign about the architecture. If decoding is separated from fetching, then a stored raw capture can be run through a decoder you improved later, without going near the device again. In a project where the protocol will inevitably change, that is the difference between a growing dataset and a pile of binaries.
The research bench path is a virtual environment and one script that lists available operations:
python3 -m venv .venv && .venv/bin/pip install -r requirements.txt
.venv/bin/python tools/oura_protocol.py --list
The note about it is the practical one people hit immediately: on a laptop with a desktop operating system, you have to grant Bluetooth permission to your terminal, and until you do nothing works with no obvious error.
Two operational details come out of the secret-handling section. Operations the vendor's application gates require the device's authentication key, which is re-sent on every connection, so it is not a one-time credential. And captures and keys are both excluded from version control, with the instruction never to commit a key. For a project where a leaked key is a leaked device identity, that line is load-bearing rather than decorative.
The final touch is a link to another project's protocol notes for a different ring generation, credited as prior art. Reverse-engineering communities are small, overlapping and depend entirely on people publishing what they find, and a repository that credits its sources is a repository you can trust to be worth reading.
Editorial conclusion
The interesting finding here is architectural, not technical. Hardware vendors describe their cloud as the brain; this project read the protocol and the app binary and found the computation on the handset, with the cloud doing storage and sync. That is why almost everything is reproducible locally, and it is also why the scores cannot be reproduced without the vendor's models, which are proprietary and deliberately not included. Read it as a research result plus a working client, not as a free replacement for the app. And note the honesty of the negative result: the firmware key is device-resident and described as not brute-forceable, which is a more useful sentence than a vague promise that they will get it eventually.
Frequently asked questions
What is open_oura?
A Rust toolkit for a smart ring across three hardware generations: a reverse-engineered Bluetooth protocol, event decoders, reimplemented data-processing algorithms, and a small client that reads your data directly from the device with no vendor account. An accompanying mobile app and web dashboard built on the same libraries live in a separate repository.
Can I get my ring's scores without the vendor's cloud?
Almost. The readiness, sleep, activity and stress scores are not computed in the cloud at all, they are computed on the phone by a native engine and small models, which is why they are reproducible offline. The one genuine cloud dependency is automatic workout classification. Reproducing the scores requires supplying the vendor's model files yourself, which are not included.
Is this safe to run against my ring?
The project's guidance is to prefer passive, read-only requests. State-changing operations are gated behind explicit flags, the factory reset requires a second confirmation in the command-line client, and the Python research bench hides state-changing and destructive operations entirely unless you pass two separate flags. Authentication keys and captured data are excluded from version control.
What data can I read directly from the device?
Device information, battery, live heart rate derived from inter-beat intervals, the most recent heart and blood oxygen readings, and the full history event stream. That stream carries raw photoplethysmography, inter-beat interval, temperature, motion and blood oxygen samples, plus the device's own sleep stage classifications, activity intensity levels, and heart rate variability.
How were the packet formats figured out?
From the mobile application. A document in the repository covers reversing the app, its internal constants, the authentication operations, key generation and nonce encryption, and another explains how the event-body decoders were ported from a native library inside the app, including how the byte layouts were recovered with a disassembler.
Can I reset a ring and keep it out of the vendor's app?
Yes, and the documentation covers it in detail. There is a document describing two verified reset methods, including one using the dock hardware rather than a command, along with what a reset erases and how to re-pair the device afterwards without handing it back to the vendor's application.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/th0rgal-open-oura)Star history chart for your README
[](https://hysenlabs.com/projects/th0rgal-open-oura)Was this useful?