SUDO_KILLER catalogues sudo misconfigurations, never exploits them, and takes your password as an argument
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific misconfiguration or flaw in sudo to gain elevated privileges on the system, essentially allowing a regular user to execute commands as the root user.
At a glance
- What is it?
- A shell audit script for pentesters, system administrators and CTF players that inspects sudo rules, sudo versions, dangerous binaries and environment variables on the machine it runs on, then prints a catalogue and stops. The interesting details are in its flags, its lab environment and the parts of its own documentation that contradict each other.
- Who is it for?
- SUDO_KILLER belongs on a machine you are authorised to audit, and its refusal to exploit automatically is the property that makes it defensible in that setting. Before running it on a real host, understand what it writes: the sudoers export and the report both land in a directory you name, and the documented example puts them in /tmp, so treat the output path as sensitive.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 8 months ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
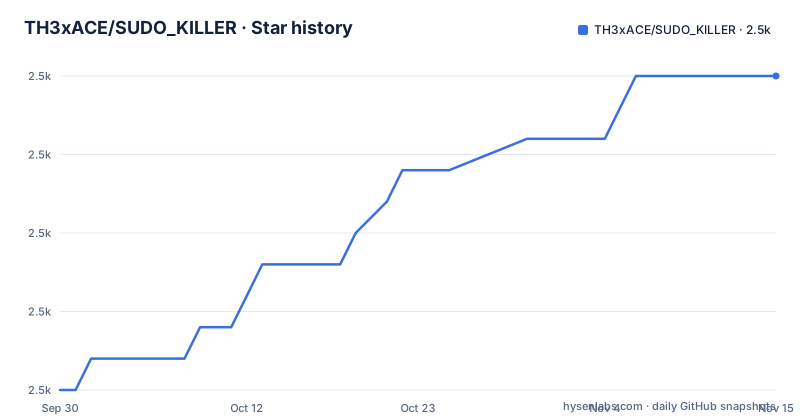
- TH3xACE/SUDO_KILLER2,495 ★ · +10
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| TH3xACE/SUDO_KILLER | 2.5k | 2.5k |
10 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The documented command line still contains a version placeholder
The usage section gives one invocation:
./SUDO_KILLERv<version>.sh -c -a -e -r report.txt -p /tmpThe filename is not a real filename. The script in the root is `SUDO_KILLERv3.sh`, the default branch is `V3`, and the angle-bracket placeholder is left in the documentation, so the line has to be edited before it runs. Everything after the filename is the interesting half: `-c` includes CVE checks, `-a` includes CVEs related to third party apps and devices, `-i` imports in offline mode, `-e` exports the sudo rules and the sudoers file, `-r` names the report, `-p` sets where the export and the report are written, `-s` supplies a user password for sudo checks, and `-h` prints help. Seven of the eight do work; none of them limit scope.
Offline mode points at a script the root does not contain
The flag list describes `-i` as an import in offline mode from `extract.sh`. The root of the repository holds `CHANGELOG.md`, `CVE/`, `FUNDING.yml`, `LICENSE`, `README.md`, `SK-Tools/`, `SUDO_KILLERv3.sh`, `dbins/`, `notes/` and `res/`. There is no `extract.sh` at the top level.
That matters for the offline path specifically, because offline mode is the mode an auditor would want: running a script that inspects sudo rules on a machine where executing unfamiliar code is the thing you are trying to avoid. As documented, the import step depends on a file name that the visible tree does not provide, so an air-gapped or change-controlled environment has to source that script from somewhere else.
The directories around it hint at how the tool is assembled. `CVE/` holds version data, `dbins/` is the dangerous binaries catalogue behind the GTFOBINS check, and `res/` and `notes/` carry the material the script prints.
Two CVE checks, and the tool tells you which one fired
The note attached to `-c` is the most useful paragraph in the documentation. Two types of check are provided: one for which the CVE identified is solely based on the current sudo version being used, and another where the requirements are also checked. The reason for the split is stated plainly. Very often a sudo version might be vulnerable, but some pre-requisites might be needed for a successful exploitation.
So a version match is not a finding on its own, and the tool distinguishes the two cases rather than printing one verdict. `-a` widens the same idea outward, to CVEs related to third party apps and devices, which is where the interesting misconfigurations usually live.
On the state of the project: there are no GitHub releases, so version tracking is by the script name and `CHANGELOG.md`. The last commit on the default branch is dated 2026-03-11, and the current script is the v3 line.
Supplying your sudo password is a documented argument
The second note explains the failure mode. If a password is needed to run `sudo -l`, the script will not work unless you provide one with `-s`.
That makes the password an ordinary command line argument, which puts it in the process list for every user on the host and in your shell history, and it makes the audit incomplete if you omit it. A reviewer reading an audit report has to know which of the two happened, and the report format does not obviously carry that.
The same argument pattern applies to output. `-e` exports the sudo rules and the sudoers file, `-r` names the report, and `-p` decides where both are written, with the documented example using `/tmp`. Credential harvesting is one of the checks the script performs, so on a real host the output can contain exactly the kind of material that should not sit in a shared temporary directory.
Scope is whatever host you run it on, and nothing enforces it
The audit boundary here is the machine the script runs on. The documentation offers two places to be: the deliberately vulnerable Docker environment, or the system to be audited. There is no per-host authorisation check, no target list, no dry run and no abort switch among the eight documented arguments. The flags add checks or choose where output goes; none of them restrict what is inspected or who may inspect it.
The containment that does exist is behavioural rather than technical. The tool provides a catalogue of potential commands and local exploits for manual privilege elevation, and it refrains from automated exploitation, requiring the operator to carry out the elevation themselves. The intended audience is named as cyber security practitioners, which is to say pentesters, security auditors, system administrators, CTF players and Infosec students.
That means the authorisation boundary is social. A catalogue printed on a host is a catalogue you can read anywhere, and the lab exists precisely so nobody has to practise on production.
The lab scenario table numbers two of its entries twice
The vulnerable test environment switches scenarios with `switchScenario <scenario_number>`, and the documentation says available scenarios run from 0 to 10. The list that follows does not agree with itself. Two entries are labelled Scenario 2, one for excessive permissions and one for excessive permissions with authentication required. Two more are labelled Scenario 4, one for a change of owner and one for a wildcard. The last entry shown is Scenario 9, so a number that the range promises is not in the list.
The classes themselves are the useful part, because they are the shapes a sudo rule takes when it is wrong: rules, excessive permissions with and without authentication, user impersonation, changing the owner of a file, wildcards, missing scripts referenced by sudo rules, dangerous environment variables, dangerous binaries, recursive impersonation, and environment handling. Scenario 0 carries its own warning that a conflict might occur.
The lab is the right place to run any of this. It exists as purpose built containers, including one dedicated to a single sudo CVE from 2019, plus a third party exploit repository credited in the documentation for a later one.
The sudo -l explanation is the part to read first
One section explains the behaviour the whole tool depends on. By default, if the NOPASSWD tag is applied to any of the entries for a user on a host, you can run `sudo -l` without a password. That behaviour may be overridden through the verifypw and listpw options.
Two consequences follow directly. Those rules only affect the current user, so if user impersonation is possible using su, sudo -l has to be launched from that user as well. And sometimes `/etc/sudoers` can be read even when sudo -l is not accessible without a password, which is why the export flag exists at all.
The check list the script works through follows from that framing: misconfigurations, dangerous binaries, vulnerable sudo versions, sudo problems tied to third party apps, dangerous environment variables, credential harvesting, writable directories where scripts reside, binaries that might be replaced, and missing scripts. The list closes with a warning that it is not exhaustive, which is the correct thing for a catalogue to say about itself.
Editorial conclusion
SUDO_KILLER belongs on a machine you are authorised to audit, and its refusal to exploit automatically is the property that makes it defensible in that setting. Before running it on a real host, understand what it writes: the sudoers export and the report both land in a directory you name, and the documented example puts them in /tmp, so treat the output path as sensitive. Pass the password through a controlled channel rather than the command line if you use that argument at all. And if you intend to practise rather than audit, use the deliberately vulnerable containers, whose scenario numbering in the documentation contains two duplicated entries you will hit when you try to switch between them.
Frequently asked questions
What does SUDO_KILLER do when I run it?
It provides a catalogue of potential commands and local exploits for manual privilege elevation, and it refrains from automated exploitation, so the operator performs the elevation. The stated audience is pentesters, security auditors, system admins, CTF players and Infosec students.
Do I have to give SUDO_KILLER my sudo password?
Only when the sudo rules are not accessible without it. The -s argument supplies the user password for sudo checks, and if a password is needed to run sudo -l the script will not work without it.
How does SUDO_KILLER decide whether a sudo version is vulnerable?
With -c it performs two kinds of check: one based solely on the current sudo version, and one that also verifies the requirements, because a vulnerable version often still needs prerequisites. The -a argument adds CVEs related to third party apps and devices.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/th3xace-sudo-killer)Star history chart for your README
[](https://hysenlabs.com/projects/th3xace-sudo-killer)Was this useful?