Simple HTTP Server speaks HTTP/1.1 only, and its own help warns about passing a token on the command line
Simple http server in Rust (Windows/Mac/Linux)
At a glance
- What is it?
- An MIT-licensed Rust static file server built on axum and tokio, with directory listing, upload, basic auth, range requests, compression, CORS, an SPA fallback and optional PKCS#12 HTTPS. The option list in the readme stops after four flags, TLS is off by default and vendored on Windows, the manifest is one patch ahead of the newest tag, and the passphrases in the documented examples travel on the command line.
- Who is it for?
- Simple HTTP Server is a sensible choice when you want one binary to serve a directory over HTTP without a language runtime, because the feature list covers the parts people end up hand-writing, cache headers with modification times and entity tags, single-range requests so seeking in a video works, compression, and the cross-origin isolation headers a browser needs for a threaded runtime. Three things to know.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 87 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
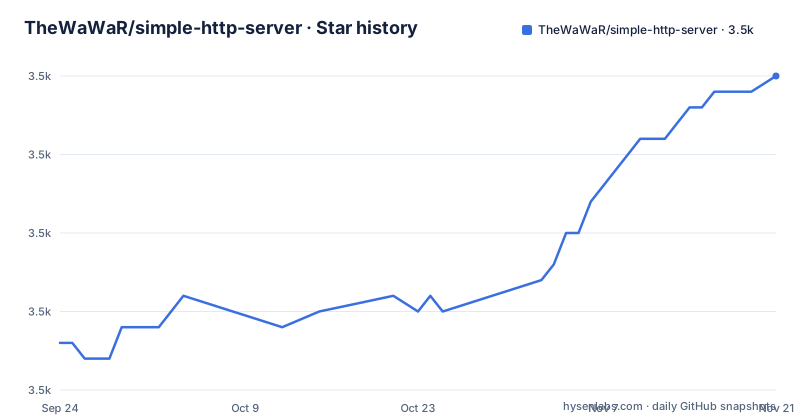
- TheWaWaR/simple-http-server3,475 ★ · +17
| Repository | 2026-09-24 | 2026-11-21 |
|---|---|---|
| TheWaWaR/simple-http-server | 3.5k | 3.5k |
17 Stars in the last 58 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The option list stops after four flags
The usage block in the readme is the reference, and it is cut off partway through the fourth option. You get the positional root directory, the flag that enables automatic index rendering for two filenames, the flag that enables uploads with a CSRF token required, the flag that sets a custom CSRF token, and the flag that redirects to a URL with a permanent redirect status. Then the text ends mid-word on a flag that disables sorting. Everything else, and there is a lot: the address and port flags, the upload size limit, the certificate and passphrase flags, the base path flag, the fallback file flag, the authentication flags, all of it, appears only in the examples further down. The examples are good and specific, so the information exists, but a reader looking up a flag finds a truncated table rather than a reference.
The project warns you about its own CSRF token flag
The help text for the custom token flag reads that using it is dangerous, because the token is passed on the command line and may be visible in process listings. That warning is in the project's own interface, not in a documentation page, which is where a warning about this belongs. The release that added the flag is titled to say the same thing, describing it as allowing a CSRF token to be passed and marking it as not recommended. What it is protecting against is specific and real: any other process on the machine can read the argument list of a running command, so a token that guards uploads should not live there. Upload support is off unless you ask for it, and when it is on a token is required, so the shape is right. The gap is only that the safe way to supply a token is not documented anywhere visible.
The documented HTTPS example puts the passphrase in the argument list
The certificate walkthrough is unusually complete: it generates a self-signed key and certificate with an explicit key size, a digest, a validity window of seven days and a subject alternative name for localhost, converts the pair into a PKCS#12 file with a passphrase, starts the server bound to the loopback address on a non-standard port, and then verifies it two ways, once strictly against the certificate file and once as a smoke test that skips verification. The certificate format is constrained too, since the flag expects a PKCS#12 file and PEM files are not accepted directly. The flaw is the one the project warns about elsewhere: the passphrase is passed as an argument, so it is readable from process listings for the lifetime of the server. For a demonstration on loopback that is harmless. Copied into a deployment it is the same mistake the CSRF flag warns about.
TLS is a compile-time feature and it is off by default
The feature list in the package manifest has an empty default set and one feature, which pulls in a TLS library and its async wrapper. The readme explains the reason plainly: TLS is behind the feature and disabled by default so the default binary stays smaller. The install section has two commands, one plain and one that asks for the feature, so the choice is explicit and visible at the point of installation:
cargo install simple-http-server
cargo install simple-http-server --features tls
What the choice costs is also visible in the dependency declaration, and it differs by platform. On Windows the TLS library is pulled in with a vendored feature, which means the library is compiled from source as part of the build; on every other platform the build links whatever the system provides. A Windows build from source therefore takes substantially longer than a Linux one, for the same optional feature.
The framework is configured for HTTP/1.1 only
Both framework dependencies are declared with their default features switched off and an explicit list instead. The web framework is enabled for HTTP version one, the async runtime, multipart handling and query parsing, and the argument parser is reduced to standard library support, help, usage, error context, suggestions and colour. Turning off defaults is how a small server stays small, and the effect on the protocol is the concrete part: this binary negotiates HTTP/1.1 and does not do HTTP/2. For serving files to browsers that is not a limitation you will notice. For anything expecting a modern protocol, such as a deployment fronted by an HTTP/2-only gateway or a server push scenario, it settles the question before you start rather than after.
The manifest is a patch ahead of the newest tag
The manifest declares version 0.8.1 while the newest published release is 0.8.0. The release titles tell you what happened in between releases rather than only numbering them: the 0.8.0 entry is named after a rewrite of the implementation onto a different web framework, and the 0.6.14 entry names a feature while marking it as not recommended. So the 0.8 line is not a small increment on 0.6, it is a different server underneath, published under a version number that has not reached one. If you are pinning, pin the tag and read its title, because a 0.7 does not appear in the visible history between the two 0.6 releases and the rewrite. The repository is not marked as archived and the default branch was last pushed on 2026-08-27.
CI fails if the checks modify the lockfile
The build file is four targets and the interesting one is the aggregate. Formatting checks the whole tree, the linter runs over all targets, all tests and all features with warnings promoted to errors, and the test target additionally sets a full backtrace and promotes warnings for the compiler itself. Then the aggregate runs all three and finishes with a single command that fails if the lockfile differs from what is committed. That is a gate nobody puts in by accident: it means a dependency that resolves differently, or a build step that quietly rewrites the lockfile, breaks continuous integration rather than passing quietly. One consequence is worth knowing: because the linter and the tests both request all features, the optional TLS path is compiled on every run even though it is off in the default build.
The screenshot section is empty and the toolchain pin has no extension
Two small things in the tree. The readme has a screenshot heading with nothing under it, while the image itself sits at the repository root, so the documentation and the repository disagree about where the picture is. And the Rust toolchain is pinned by a file with no extension, where the conventional name for that file carries one, so tooling that looks for the conventional name will not find the pin. There is also an analysis document at the root next to the readme and the contributing guide, which is an unusual place for one. Two continuous integration directories exist, one under a dot-prefixed name and one under the forge's own, and there is a directory of Docker material and a committed lockfile.
Editorial conclusion
Simple HTTP Server is a sensible choice when you want one binary to serve a directory over HTTP without a language runtime, because the feature list covers the parts people end up hand-writing, cache headers with modification times and entity tags, single-range requests so seeking in a video works, compression, and the cross-origin isolation headers a browser needs for a threaded runtime. Three things to know. The dependency set is pinned so that the framework is HTTP/1.1 only, which is fine for a file server and will matter if you expected HTTP/2. TLS is a compile-time feature that is off by default, so the binary you get from a plain install has no HTTPS at all. And the readme's own examples put both a certificate passphrase and, in the other feature, a CSRF token on the command line, which the project warns about in its help text; treat those examples as demonstrations rather than as a deployment recipe.
Frequently asked questions
what is simple http server
A static file server written in Rust, built on the axum web framework and the tokio runtime, distributed through the cargo installer as the simple-http-server package. It does directory listings, uploads, basic auth, range requests, compression, cross-origin headers, an SPA fallback and optional HTTPS.
how to set up simple http server
Install it with cargo, optionally adding the tls feature for HTTPS, then run it against a directory. Flags enable an index page for two filenames, uploads with a size limit, a fallback file for single-page applications, and a base path for running behind a reverse proxy.
Does simple-http-server support HTTPS out of the box?
No. TLS is a compile-time feature that is empty by default so the standard binary stays smaller. Install with the feature enabled and supply a PKCS#12 certificate file, since PEM files are not accepted directly.
Does simple-http-server speak HTTP/2?
No. The web framework is declared with only HTTP version one enabled and its default features turned off, so the server negotiates HTTP/1.1.
Why does simple-http-server warn about its own CSRF token flag?
Because the token is passed on the command line and may be visible to other processes through process listings. The release that added the flag also describes it as not recommended, and upload support is off unless requested.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/thewawar-simple-http-server)Star history chart for your README
[](https://hysenlabs.com/projects/thewawar-simple-http-server)Was this useful?