cap: a self-hosted CAPTCHA whose proof-of-work runs in the visitor's browser
Free, open-source and self-hosted CAPTCHA alternative to reCAPTCHA. Privacy-first and powered by proof-of-work and instrumentation challenges.
At a glance
- What is it?
- cap is a privacy-first, self-hosted alternative to reCAPTCHA that replaces the traffic-light puzzle with small background challenges, including GPU-resistant proof-of-work. It ships as four separate packages, its three most recent releases are all scoped to the standalone one, has no dependencies by default, and its only quantitative claim is being 200 times smaller than hCaptcha.
- Who is it for?
- Adopt cap when you need to stop automated abuse of a form and you do not want a third party watching your visitors, because the absence of tracking and third parties is the reason the project exists and it names two production users. Do not adopt it expecting it to behave like a puzzle, because the challenge runs silently in the background and a reader will not know a check happened.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
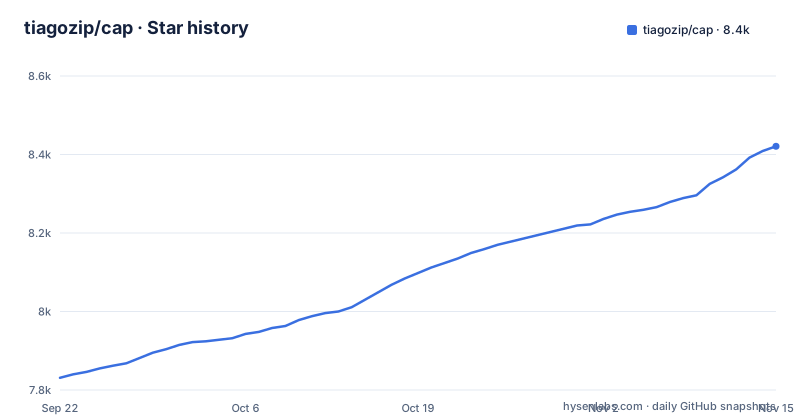
- tiagozip/cap8,421 ★ · +590
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| tiagozip/cap | 7.8k | 8.4k |
590 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The check happens, but the visitor never sees it
The framing of the project is a rejection of the puzzle rather than a cheaper version of it.
It is a self-hosted and privacy-first captcha alternative that does not force your users to click on traffic lights. There are no puzzles, no tracking, and no third parties watching your visitors.
So the usual interaction is absent by design. What replaces it is described as the user's browser quietly solving a few small challenges in the background, and the two named challenge types are gpu-resistant proof-of-work and instrumentation.
The direction of that matters. The work is done by the visitor's own browser, on the visitor's own CPU, in order to establish that a human is present. That is the same principle as a proof-of-work coin mint, applied to the question of whether a request came from a person.
The consequence is for the user experience. There is no moment where someone pauses and solves something, so there is nothing to train a user on and nothing for a user to fail at. The trade is that the cost moves to the client, invisibly, and a site owner is accepting that cost on their visitors' behalf.
Four packages, and the release tag names only one of them
The repository is not a single package. The top level holds four directories that read as separate deliverables.
`core/` is the shared logic. `standalone/` is a server you run yourself. `wasm/` is a WebAssembly build, and `widget/` is the client-side piece that a page embeds.
The recent release record covers only one of them. All three most recent tags are prefixed with the package name, `[email protected]`, `[email protected]` and `[email protected]`.
That is a scoped-release convention rather than a single version line for the repository. It tells you the maintainer versions and ships the standalone component on its own, and the recent list shows no tag for the other three.
Two of those three are twenty-four minutes apart on the same afternoon, which says patch releases here are cheap to cut and likely to be cut for a specific fix rather than on a schedule.
The consequence is that there is no repository-wide version to pin. If you deploy the widget and the standalone server together, you are picking two artefacts whose versions are coordinated by whatever the maintainer chose, not by a single number, and a tag tells you which of the four moved.
GPU-resistant is the claim that needs measuring
Of everything in this README, one phrase carries the most technical weight and the least evidence.
The challenges include gpu-resistant proof-of-work.
A proof-of-work scheme's cost is measured in the work a device performs, and graphics processors are good at exactly the kind of parallel hashing that proof of work asks for. So a scheme that is resistant to GPU advantage is doing something specific: it is making the cost harder to amortise across a device that can run thousands of operations in parallel.
There is also a second challenge type named, instrumentation, and the README says the challenges can be configured to stop autonomous AI agents from using up your resources.
That second clause is the one to read carefully. It is the same mechanism serving two purposes: distinguishing a human from a bot, and limiting what an automated agent can consume. Those overlap but are not identical, and the configuration knob appears to be shared between them.
The consequence is that no number is given. There is no difficulty setting, no expected solve time, no device target, and no comparison. So if you deploy this, the questions worth answering are empirical: how long does the challenge take on the slowest phone your visitors actually use, and what does it cost in battery.
The one number in the README is a size comparison
The whole README is short, and it contains a single quantified claim.
It has no dependencies by default, is 200x smaller than hCaptcha, and you can run it with docker, on workers or on railway.
Three things in one sentence, and they are the three facts that distinguish the project: it pulls nothing in, it is dramatically smaller than the alternative it names, and it deploys in three different ways.
The 200x figure is a size comparison against hCaptcha specifically, and no artefact is named or sized. It is not a claim about solve rate, false positive rate, or how many requests per second it can gate, and it is not a claim about how much of a request stream a motivated attacker can still push through.
The dependency claim is the more useful of the two for an adopter. A CAPTCHA that runs partly in the visitor's browser has to ship something to that browser, and a project that says it has no dependencies by default is telling you the shipped piece is small and self-contained.
The consequence is that this README argues its case on size, cost and privacy, and it does not offer any accuracy or throughput evidence at all. If you are choosing on detection quality, this document will not answer that.
Three deployment targets are named, and none is a SaaS
The deployment options are stated in the same sentence as the size claim, and they are worth separating by what they imply.
Docker, workers, and Railway.
Docker is the self-hosted answer and the one the self-hosting framing leads to. Railway is a platform as a service, which is a concession to people who want the property without running it. Workers is the edge-compute model, where the check runs close to the user rather than in one region.
That third option is the one that follows from the architecture. If the challenge is computed in the visitor's browser, then the component that verifies the result wants to be somewhere with low latency and low cost, and an edge runtime is where a small stateless verification would sit.
So the deployment list is not three interchangeable options; it is a description of where the work happens.
The consequence is that the choice of runtime changes the latency profile of your form submission for users far from your primary region, and the README does not tell you which runtime the verification logic was tuned for.
The demo uses Bun while the registry package is npm
The badge in the README points at an npm package under a scoped name, `@cap.js/wasm`, served through a public CDN. That is the artefact a consuming site would load.
The demo directory tells a different story about how the project is developed. Its four files are a lockfile, an HTML file, a JavaScript file and a package manifest, and the lockfile is named for Bun rather than npm or yarn.
So the shipped component is an npm package under the `@cap.js` scope, while the example that demonstrates it is developed against the Bun runtime.
That is not a contradiction, it is just two different toolchains for two different jobs, and it is the kind of detail that saves you an afternoon when a demo behaves differently from the published package.
The other repository-level files fit the same picture. There is a formatter and linter configuration for the JavaScript, a file for custom domain configuration used by the documentation site, a contributing guide, and a security policy whose filename uses a capitalised extension while the rest of the repository uses lower case.
What cap cannot do, and what it leaves you owning
Five limits, and the first is the design rather than a gap.
It cannot give you a puzzle. There is nothing for a user to see or solve, so a site owner cannot rely on a human being aware that a check ran, and cannot ask them to do anything if it fails.
It cannot tell you how effective it is. The README contains no false positive rate, no detection rate, no throughput figure, no solve-time measurement, and no comparison against any other CAPTCHA on anything except file size. The two named production users are evidence of use, not evidence of accuracy.
It cannot hide its cost from the visitor. The work happens on the user's device, so your form's users pay for it in CPU and battery without being told. That is a deliberate privacy trade and it is also a real cost on old hardware.
It does not remove the need for rate limiting or authentication. Nothing in this repository describes account-level controls, and a CAPTCHA is one signal rather than a whole defence.
And it does not give you a single version to pin. Four packages ship from one repository and the three most recent release tags all name the standalone component, so deploying the widget alongside the server means choosing versions per component.
Editorial conclusion
Adopt cap when you need to stop automated abuse of a form and you do not want a third party watching your visitors, because the absence of tracking and third parties is the reason the project exists and it names two production users. Do not adopt it expecting it to behave like a puzzle, because the challenge runs silently in the background and a reader will not know a check happened. Before you deploy it, check three things. The proof-of-work is described as GPU-resistant but no figure is given, so measure it on the devices your actual visitors use rather than on your own hardware. The challenge runs in the visitor's browser, so it costs your users CPU and battery, which is a real cost on a low-end phone. And the package you install from the registry is one of four, with the release tag scoped to the standalone component, so check which part you are deploying before you pin a version.
Frequently asked questions
What is cap, the CAPTCHA alternative?
A free, open-source and self-hosted CAPTCHA alternative to reCAPTCHA. It replaces the puzzle with small challenges solved quietly in the visitor's browser, including GPU-resistant proof-of-work, with no tracking and no third party watching visitors.
Is there a free CAPTCHA service available?
Self-hosting is the free option this project offers. The README states cap has no dependencies by default and can be run with Docker, on Workers, or on Railway, and names bunny.net and adguard as production users.
Can AI outsmart CAPTCHA?
The README does not claim immunity from AI. It says the browser quietly solves challenges such as GPU-resistant proof-of-work and instrumentation, and that these can be configured to stop autonomous AI agents from using up your resources. No detection rate or comparison is given.
How does cap compare with hCaptcha?
On size, the README makes one claim: that cap is 200x smaller than hCaptcha. It gives no named artefact or size, and makes no comparison on accuracy, throughput or solve rate.
How do I install cap?
The README does not give an install command. It names three ways to run it, Docker, Workers and Railway, and points at the documentation at trycap.dev plus a hosted demo. The published client component is an npm package under the @cap.js scope.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tiagozip-cap)Star history chart for your README
[](https://hysenlabs.com/projects/tiagozip-cap)Was this useful?