Fort Firewall: an own-driver design that asks you to turn off memory integrity
Fort Firewall for Windows
At a glance
- What is it?
- Fort is a Windows host firewall written in C++ and distributed as a single installer, with rules keyed on application paths, parent processes and service names. The costs are stated as prerequisites rather than trade-offs: disable HVCI on Windows 10 and later, pick between two installer rows that share one link, and read the wiki for everything the two hundred word README leaves out.
- Who is it for?
- Fort suits a single machine where you want rules the built-in Windows firewall does not express, and it costs you a kernel driver, a Visual C++ redistributable and memory integrity switched off on Windows 10 and later.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly C++, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
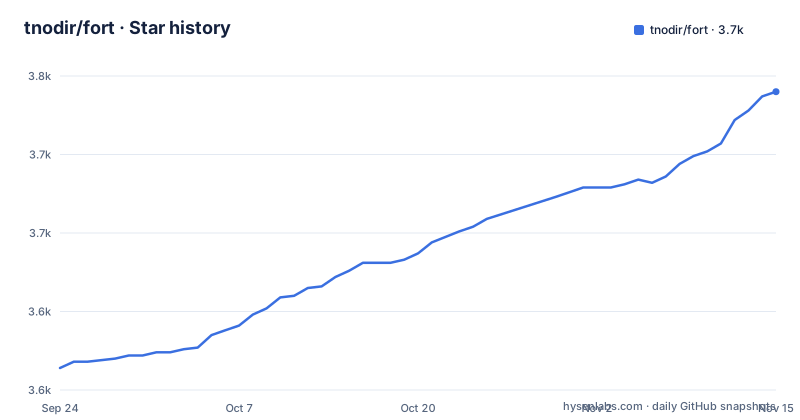
- tnodir/fort3,740 ★ · +176
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| tnodir/fort | 3.6k | 3.7k |
176 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two installer rows, both pointing at the same page
The section titled "Which installer should I download?" is a two row table. The first row reads "Windows 10 1809 or newer", the second reads "Windows 7 or newer", and both cells point at the same URL, the repository's latest release page. The choice the heading asks for is therefore not expressed anywhere in the file. The row markup does not help either: the first row ends with a stray pipe after the link and the second does not, so the pipe is not a real column boundary and the two rows have different shapes. What the table does establish is that both eras are still supported by a version released in October 2026, which is unusual for a component that installs its own kernel driver. Anyone following the heading has to open the release page and read the asset names to work out which file is theirs.
HVCI has to be off before the driver can load
Fort is described as a standalone firewall with its own driver, and the system requirements list follows from that. Two items are asked for: the latest Visual C++ redistributable packages, with separate x64, x86 and ARM64 downloads, and disabling HVCI, listed as Core Isolation: Memory Integrity, on Windows 10 and later. Memory integrity is a platform setting that decides which drivers may load, so a product that depends on loading its own is asking you to relax exactly that decision. The cost of the architecture is stated as a prerequisite rather than discussed as a trade: nothing in the README explains what re-enabling HVCI after installing Fort would break, and the wiki's HVCI page is the only place that could answer it. A host firewall you cannot run under memory integrity is a different product from one you can.
Rules key on paths, parent processes and service names
The rule model is more specific than a port list. Rules can be written per application or globally, keyed on addresses, ports and protocols. Application paths accept wildcards, so a rule can cover a family of executables rather than one path. Rules can be conditioned on the parent process, which separates a launcher from the program it starts. And requests arriving inside `SvcHost.exe` can be filtered by service name, which is the Windows specific case: several services share one host process, so a rule has to name the service rather than the executable. Groups of applications can carry a speed limit. Nothing in the README states the precedence order when a global rule and a per application rule disagree, or whether a wildcard path is matched case insensitively; both questions are pushed to the wiki's Rules page.
Zones are the blocklist feature and nothing more is said
Blocklists exist under the name "Zones". That is the entire description: the feature line reads "Blocklists via \"Zones\"" and stops. No list is named, no source is given, no update interval appears, and no format for a custom zone is described in the README. A Crowdin badge sits in the header, which tells you the interface is translated, and says nothing about who curates a zone list or how a user would supply their own. Adjacent features are equally terse: application groups can have speed limits applied, traffic statistics are saved, and bandwidth is shown graphically. Between them these cover throttling, measurement and blocking, which is most of a firewall's daily surface, and each is one line long. If a zone is the part you plan to depend on, the Rules and FAQ wiki pages are the only source available before you install.
The wiki holds the documentation and the build steps
Five wiki pages are linked and none of them is in the repository: User Guide, Functionality overview, Rules, Frequently Asked Questions and Building. The Building page matters most, because the top level of the tree holds no build manifest. The entries are `.github/`, `.gitignore`, `CLAUDE.md`, `ChangeLog`, `LICENSE`, `README.md`, `deploy/` and `src/`, so whatever defines the compile lives inside `src/` or `deploy/`, and the instructions for invoking it live on a wiki page that is not versioned with the source. `ChangeLog` is in the repository, which means release history exists in two places, one of them fixed and one of them editable by anyone with wiki access. The README itself is about two hundred words, and every descriptive sentence in it points outward.
A year between 3.19.9 and 3.20.0
The release list has an obvious gap. `v3.19.8` was published on 2025-10-01 and `v3.19.9` on 2025-10-11, ten days apart, then the next entry is `v3.20.0` on 2026-10-04. The last push to the repository is recorded at 12:42 UTC on 2026-10-04 and the release was published at 12:46 UTC the same day, so the tag for the version bump followed the final commit by about four minutes. A minor version bump on a firewall with a kernel driver, arriving after a year of silence and immediately after the last commit, is the shape of a release cut rather than a slow drip of fixes, and the release names themselves say nothing about what changed inside it. The version number in the file name is the only description the project gives for this jump.
Static analysis is advertised, testing is not mentioned
The header carries four badges pointing at the latest release, at Crowdin for translations, at CodeScene, and at a SonarCloud summary scoped to new code. A separate SAST section names PVS-Studio as the static analyzer for C, C++, C# and Java. So three hosted analysis services and one commercial analyzer are part of the project's public front door, and no test command, no coverage number and no build badge appear. That asymmetry is the reason the Building wiki page carries more weight than usual: for a C++ project of this size the interesting question is not whether the analysis services run, but how a contributor compiles a kernel driver, and the repository does not answer it. Attribution goes to the FatCow Free Icons set for the artwork, and the project is by a single named author.
Editorial conclusion
Fort suits a single machine where you want rules the built-in Windows firewall does not express, and it costs you a kernel driver, a Visual C++ redistributable and memory integrity switched off on Windows 10 and later. Before installing, read the wiki's HVCI and Building pages, because the README states both as prerequisites and neither is explained in the repository, and read the Rules page before trusting a zone, since Zones is one line long with no list named and no update interval given. Anyone putting this on a shared or production machine should first check what re-enabling memory integrity does to the running firewall, which is exactly the question the project leaves to its wiki. Track the ChangeLog in the repository rather than the wiki, since only one of the two is versioned with the source.
Frequently asked questions
What kinds of rules can Fort Firewall write?
Rules can be per application or global, keyed on addresses, ports and protocols. Application path names accept wildcards, rules can be conditioned on the parent process, and requests arriving inside SvcHost.exe can be filtered by service name. Groups of applications can also carry a speed limit.
What has to change in Windows before Fort Firewall will run?
Two things from the system requirements list: install the latest Visual C++ redistributable packages for x64, x86 or ARM64, and disable HVCI, called Core Isolation: Memory Integrity, on Windows 10 and later. Fort is a standalone firewall with its own driver, so the driver is what needs the memory integrity setting relaxed.
Which Fort Firewall installer should a Windows 7 user take?
The table under which installer should I download lists a row for Windows 10 1809 or newer and a row for Windows 7 or newer, and both cells point at the same releases/latest page, so the choice is not actually expressed there. The Windows 7 row is still present in version 3.20.0.
Where is the Fort Firewall documentation kept?
In the GitHub wiki rather than the repository. Five pages are linked: User Guide, Functionality overview, Rules, FAQ and Building. The repository itself has no documentation directory; its top level holds .github/, .gitignore, CLAUDE.md, ChangeLog, LICENSE, README.md, deploy/ and src/.
When was the most recent Fort Firewall release?
v3.20.0, published 2026-10-04, with the last push to the repository on the same day a few minutes earlier. Before it came v3.19.9 on 2025-10-11 and v3.19.8 on 2025-10-01, so about a year separates those patch releases from the version bump.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tnodir-fort)Star history chart for your README
[](https://hysenlabs.com/projects/tnodir-fort)Was this useful?