Tock isolates applications with MPUs and keeps the kernel and drivers in Rust
A secure embedded operating system for microcontrollers
At a glance
- What is it?
- Tock is an embedded operating system for running mutually distrustful applications on Cortex-M and RISC-V platforms, and its whole safety argument rests on two named mechanisms: Rust for the kernel and the drivers, memory protection units for the applications. The build is a per board make, which is where most of the friction lives.
- Who is it for?
- Choose Tock when your Cortex-M or RISC-V device runs code you did not write and mutual isolation between applications matters more than a small ecosystem. Pass when you need a single vendor toolchain and a stable tag, since the last release is 2.3.0 from October 2026 while the tree keeps moving.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
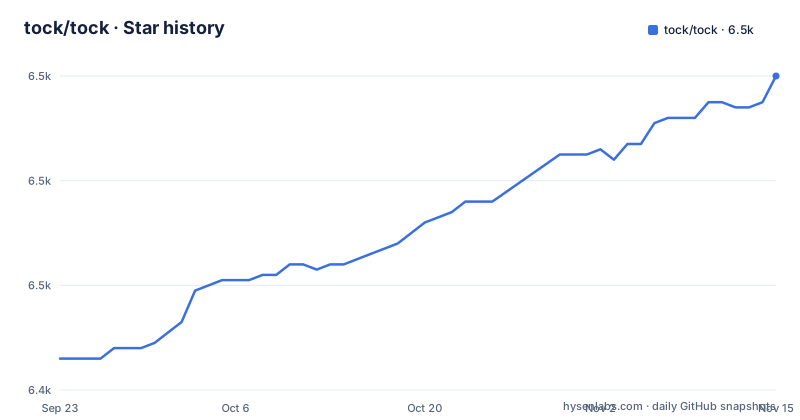
Star history
- tock/tock6,500 ★ · +54
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| tock/tock | 6.4k | 6.5k |
54 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two mechanisms, and they protect different things
Tock is built to run several applications at once on a microcontroller where those applications do not trust each other. The design claims protection from two directions, from potentially malicious applications and from device drivers, and it uses a different mechanism for each. The kernel and the device drivers are written in Rust, which gives compile-time memory safety and type safety. That choice protects the kernel, meaning the scheduler and the hardware abstraction layer, from platform specific drivers, and it isolates the drivers from each other. The second mechanism is the one that protects you from the applications: memory protection units isolate applications from each other and from the kernel. Rust alone would not do that job, since type safety says nothing about what a process may address at runtime. Neither mechanism alone would give you the property the project is selling, which is why both appear in the same paragraph.
Build flow is make inside a board directory, then make install
There is no global install step, and the starting point is a document rather than a command. The Makefile usage output points at doc/Getting_Started and warns that you need to install a few requirements before going further. After that the flow is per board. You change into the board's directory, run make to build Tock for that board, then run make install to load the result onto hardware:
make
make install
The board folder has its own README with the specifics, which matters because board support is not uniform. Two details in the Makefile explain why the flow is shaped this way. The supported platform list is not written down anywhere in the file, it is generated by running a script:
./tools/build/list_boards.shand the shell is pinned because some systems have unusual defaults:
SHELL := bashSo the list of boards you can build for comes from the tree, not from a table in the documentation.
The board list is a Cargo workspace member list
The platforms are enumerated in Cargo.toml as workspace members, which means the build graph is the inventory. Architectures come first, one directory per core family:
arch/cortex-m
arch/cortex-m33
arch/riscv
arch/x86
Then the boards, and there are a lot of them, each its own member:
boards/raspberry_pi_pico
boards/nano_rp2040_connect
boards/opentitan/earlgrey-cw310
boards/microbit_v2
Two entries in that list are worth noticing because they change what you can test. The OpenTitan entry is a security focused target rather than a hobby board, and the list also carries qemu_arm_mps2 emulator targets alongside real silicon. Being a workspace member rather than a board definition file also means a board directory is a full crate, so the same tree holds the kernel, the libraries and the board support together, with chips/ holding the hardware definitions underneath. rust-toolchain.toml at the root pins the compiler, and clippy.toml and rustfmt.toml sit beside it, so lint and formatting rules are part of the checkout rather than a matter of taste.
Binary size is a build target, measured with cargo-bloat
A microcontroller kernel lives or dies by how many bytes it costs, and the build system treats that as a first class output. The Makefile lists a per board target called cargobloat, which runs the cargo-bloat tool for attributing binary size, next to a stack-analysis target. What the pair signals is that size is something you measure after every build rather than something you discover when the image no longer fits.
The rest of the tooling follows the same pattern of making the environment reproducible. There is a shell.nix for a pinned shell and a vagrant/ directory for a virtual machine, alongside the tools/ tree that holds the board listing script. The tree also keeps SECURITY.md, which is where a vulnerability report belongs, and doc/CodeReview.md, which the Makefile header points at for how the make system and the continuous integration setup fit together.
What an application keeps after the MPU is configured is not spelled out
The protection claim is precise about the mechanisms and silent about the residue. Rust covers the kernel and the drivers, the memory protection units cover isolation between applications, and the visible README sections do not enumerate what an isolated application retains: which device registers it may still reach, how much of its own memory it may touch, or what a fault costs its neighbours. For a system whose selling point is mutual distrust, that gap is the part a security review will ask about first. The README does say where the argument lives: the threat model documentation is named as the source of truth for the current model, with the EuroSec paper on tiered trust described as a snapshot of the reasoning behind it rather than as the current position.
Rust's own limits for embedded work are documented as unresolved
A project built on a language is candid about the language's gaps, and this README is. It points at two shorter papers looking at potential limitations of the Rust language for embedded software development, and it splits them by what they offer: the earlier PLOS paper lays out the challenges and the later APSys paper lays out potential solutions. Both exist because the choice of Rust is a real constraint, not a free upgrade. The kernel paper presented at APSys'17 argues the case for writing a kernel in Rust, which is the same question asked from the other side.
The README is also explicit about citation practice. Most work should cite the SOSP'17 paper, the one presenting multiprogramming a 64kB computer safely and efficiently, and it says the language and type theory papers are worth reading for people working in that area rather than as the general reference. A ten year retrospective appeared at SOSP'25 under the title Tock: From Research To Securing 10 Million Computers, so the deployment scale is now stated outright rather than implied.
Licensed Apache-2.0 OR MIT, while the metadata asserts nothing
The licence is the first thing in every source file. The Cargo.toml header reads, licensed under the Apache License, Version 2.0 or the MIT License, with the SPDX identifier Apache-2.0 OR MIT and a copyright line for Tock Contributors 2022, and the Makefile repeats the same three lines. A dual licence means you pick one and comply with it, which is the arrangement most embedded vendors prefer, but it is a choice someone has to make on your behalf. The repository root carries COPYRIGHT, LICENSE-APACHE and LICENSE-MIT as separate files, so both texts are present rather than referenced.
What is missing is any assertion in the repository metadata, which records no licence identifier at all. If your compliance process reads the licence off the repository rather than off the source files, it will come back empty here, and the answer has to be taken from the headers and the three licence files.
Version 2.2 is from January 2025 while the tree keeps taking commits
Tock announces itself as being on its second major release, with the changelog at CHANGELOG.md named as the place to read what changed. The recorded releases are release-2.2-rc1 on 2024-12-18, release-2.2 on 2025-01-06 and release-2.3.0 on 2026-10-08, so a release candidate preceded the final 2.2 by about three weeks. The last push to master landed on 2026-11-02, after release 2.3.0. A tag gives you a dated, reproducible tree, and master gives you the current state of a project whose components change together.
For a project with this many workspace members, the distinction is not academic. Pin a tag if you are shipping, and expect to read the changelog between tags rather than between commits.
Editorial conclusion
Choose Tock when your Cortex-M or RISC-V device runs code you did not write and mutual isolation between applications matters more than a small ecosystem. Pass when you need a single vendor toolchain and a stable tag, since the last release is 2.3.0 from October 2026 while the tree keeps moving. Before you build, settle three things: the board directory you will run make in, the dual licence in the Cargo.toml header (Apache-2.0 OR MIT) against whatever your organisation requires, and what your application still gets to do after the memory protection unit is configured, which the visible README sections do not enumerate.
Frequently asked questions
What is Tock used for?
Tock is an embedded operating system designed for running multiple concurrent, mutually distrustful applications on Cortex-M and RISC-V based embedded platforms. Its design centres on protection, both from potentially malicious applications and from device drivers.
How do I build Tock for a board?
Start with doc/Getting_Started, install the requirements it lists, then run make inside the board's directory and make install to load the result onto hardware. The board folder has its own README, and the Makefile usage target prints the platforms currently supported.
Does Tock use memory protection units?
Yes, and that is one of two mechanisms it names. Memory protection units isolate applications from each other and from the kernel, while the kernel and the device drivers are written in Rust for compile-time memory safety and type safety.
What licence is Tock released under?
The header of Cargo.toml states the project is licensed under the Apache License, Version 2.0 or the MIT License, with the SPDX identifier Apache-2.0 OR MIT. The root of the repository also carries COPYRIGHT, LICENSE-APACHE and LICENSE-MIT as separate files.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tock-tock)Star history chart for your README
[](https://hysenlabs.com/projects/tock-tock)Was this useful?