innernet: WireGuard networks where CIDRs, associations and one-time invitations are the access policy
A private network system that uses WireGuard under the hood.
At a glance
- What is it?
- innernet is a Rust private network system from tonari that runs on WireGuard and uses CIDR membership as its access control model. This analysis walks through the server and client workflow, the rules that surprise operators, and the security caveats the project states itself.
- Who is it for?
- innernet suits a team that wants a self-hosted WireGuard mesh where CIDR membership defines who can reach whom, and is comfortable running its own coordination server. It is a poor fit if you need peer deletion, an audited codebase, or a hosted service.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 11 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
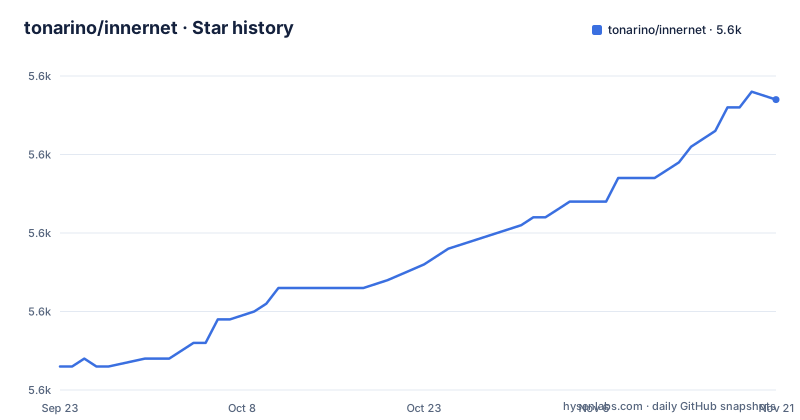
Star history
- tonarino/innernet5,587 ★ · +34
| Repository | 2026-09-23 | 2026-11-21 |
|---|---|---|
| tonarino/innernet | 5.6k | 5.6k |
34 Stars in the last 59 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Access control is CIDR membership plus explicit associations
innernet states its goal plainly: take existing networking concepts like CIDRs and the security properties of WireGuard, and turn your computer's basic IP networking into access control primitives. The README compares its goals to Slack's nebula and to Tailscale, and says it takes a different approach.
The model has three moving parts. Every peer lives in a CIDR. Server initialisation creates a special infra CIDR that holds the innernet server itself and is reachable from all CIDRs on the network. A new CIDR, such as humans, can contact only peers in the same CIDR plus the infra CIDR by default.
To let one CIDR reach another, you create an association between the two. The README's example lets humans reach a ci-servers CIDR. One detail to watch: the example gives ci-servers the block 10.60.64.0/24, the same block used for humans earlier, and says that for the example it can be anything. In a real network, pick non-overlapping blocks inside your root CIDR, which the README illustrates as 10.60.0.0/16.
A coordination server is mandatory, and invitations are single use
Every innernet network needs a coordination server to manage peers and provide endpoint information so that peers can connect directly to each other. You create one with an init wizard:
sudo innernet-server newThe wizard asks about your network and offers defaults. Run the server afterwards with innernet-server serve followed by the interface name, or on Linux enable it under systemd with systemctl enable --now innernet-server@ and the interface name.
Adding a peer produces an invitation file. It holds just enough information for the new peer to contact the server and redeem the invitation, and it can only be used once. You should transfer it securely, since it includes a private key. When the peer runs the install command, innernet connects over WireGuard, generates a new key pair and registers it with the server, after which the private key in the invitation file can no longer be used:
sudo innernet install /path/to/invitation.tomlThe practical consequence is that the server is a single point of coordination. Peers talk directly to each other, but joining, endpoint information and CIDR changes all go through it.
The first admin peer is created on the server, then everything moves to the client
The typical bootstrap path is to create an admin peer from the innernet-server CLI, then keep working through that admin peer using the innernet client CLI to add further peers and CIDRs.
On the server you add the humans CIDR and the first peer:
sudo innernet-server add-cidr <interface>sudo innernet-server add-peer <interface>When you add the peer, you select the humans CIDR, the CLI suggests the next available IP address, any name is fine, and you answer yes when asked whether the peer should be an admin. After the invitation is redeemed, the same operations are available from the client without logging into the server, for instance innernet add-cidr and innernet add-association. To check your work, sudo innernet list shows the network and every CIDR visible to the peer, and the --tree flag changes the layout to a tree view.
Because a peer only sees CIDRs it is allowed to see, the list output is a view from that peer, not a complete inventory.
Peers can be disabled but never deleted, because IP addresses are not reused
For security reasons, IP addresses cannot be re-used by new peers, and therefore peers cannot be deleted. They can be disabled instead. A disabled peer will not show up in the list of peers when the config for an interface is fetched.
The commands are:
sudo innernet disable-peer <interface>sudo innernet enable-peer <interface>The consequence for capacity planning is real. Every peer you ever add consumes an address in its CIDR permanently. The README's humans example uses 10.60.64.0/24 and admits it is not a great example unless you only want to support 256 humans. If you expect many short-lived machines, such as CI runners, give that CIDR a large block from the start.
Associations behave differently and can be removed. sudo innernet list-associations shows them, and sudo innernet delete-associations removes one, both taking the interface name.
Endpoint discovery can guess wrong, and the listen port is adjustable
The server tries to use the internet endpoint it sees from a peer so that other peers can connect to that peer too. The README says this does not always work. For those cases you set an endpoint yourself:
sudo innernet override-endpoint <interface>and return to automatic discovery with:
sudo innernet override-endpoint -u <interface>The WireGuard port has a similar pair of commands. set-listen-port changes it, and the -u flag unsets it so that WireGuard picks a randomized port:
sudo innernet set-listen-port <interface>sudo innernet set-listen-port -u <interface>One more operational note applies to servers on home networks: configure port forwarding to the Listen Port you chose when creating the innernet server, or peers outside your LAN cannot reach the coordination server.
Strict reverse path filtering is not the Linux default, and innernet asks you to turn it on
If you run a service on innernet, the README lists security considerations. The first is strict Reverse Path Filtering, described in RFC 3704. Strict RPF prevents packets from other interfaces from having internal source IP addresses. The README says this is not the default on Linux, even though it is the right choice for 99.99% of situations.
Without it, a packet arriving on some other interface could carry a source address from your innernet range and be treated as if it came from a trusted peer. Because innernet's policy is expressed in IP ranges, spoofable source addresses undercut the model directly.
You enable it with a sysctl file such as /etc/sysctl.d/60-network-security.conf containing:
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1
The README adds a note about also applying the setting to interfaces that exist when the sysctl is applied. That section is cut off in the text available here, so read the full README for the remaining recommendations.
Experimental status, no audit, and an unofficial relationship to WireGuard
The project is blunt about maturity. It has not received an independent security audit and should be considered experimental software at this early point in its lifetime. It is also not an official WireGuard project, and WireGuard is a registered trademark of Jason A. Donenfeld.
On activity, the latest release is v2.0.0 from 2026-07-02, preceded by v1.7.1 on 2025-11-10 and v1.7.0 on 2025-08-13. The last push to the main branch was on 2026-10-22.
The code is a Rust workspace with crates for server, client, client-core, hostsfile, shared, publicip and netlink-request, and the repository also has a wireguard-control directory. The release profile uses fat link time optimisation, opt-level s, one codegen unit and panic abort. Netlink dependencies are pinned in the workspace table, so the Linux kernel interface is how it drives WireGuard there.
To permanently remove a network, run innernet-server uninstall with the interface name. The README adds only: use with care.
Editorial conclusion
innernet suits a team that wants a self-hosted WireGuard mesh where CIDR membership defines who can reach whom, and is comfortable running its own coordination server. It is a poor fit if you need peer deletion, an audited codebase, or a hosted service. Before rollout, decide your CIDR layout on paper and enable strict reverse path filtering on Linux hosts.
Frequently asked questions
What is innernet?
innernet is a private network system that uses WireGuard under the hood. It is written in Rust and uses CIDRs and associations between them for access control.
Is innernet security audited?
No. The project says it has not received an independent security audit and should be considered experimental software at this early point in its lifetime.
How does innernet compare with Tailscale and nebula?
The README says innernet is similar in its goals to Slack's nebula and to Tailscale but takes a different approach, building access control on CIDRs and WireGuard security properties.
Can you delete a peer in innernet?
No. IP addresses cannot be re-used by new peers for security reasons, so peers cannot be deleted. You can disable a peer with innernet disable-peer and re-enable it later.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tonarino-innernet)Star history chart for your README
[](https://hysenlabs.com/projects/tonarino-innernet)Was this useful?