My Arsenal of AWS Security Tools: a README of badges, not an install guide
List of open source tools for AWS security: defensive, offensive, auditing, DFIR, etc.
At a glance
- What is it?
- This repository is a hand-curated index of open source AWS security tools, grouped by activity rather than by product, where every row's popularity and freshness come from live badge URLs. It gives you names and one-line descriptions, and nothing about versions, prerequisites or whether an entry still works.
- Who is it for?
- The list suits a defender who already knows the cloud and wants a fast survey of which open source tools exist in each phase, then goes to each project for the real work. It does not suit anyone who needs a vetted, versioned recommendation or a decision, because nothing in it ranks, tests, or dates the entries.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 44 days ago.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
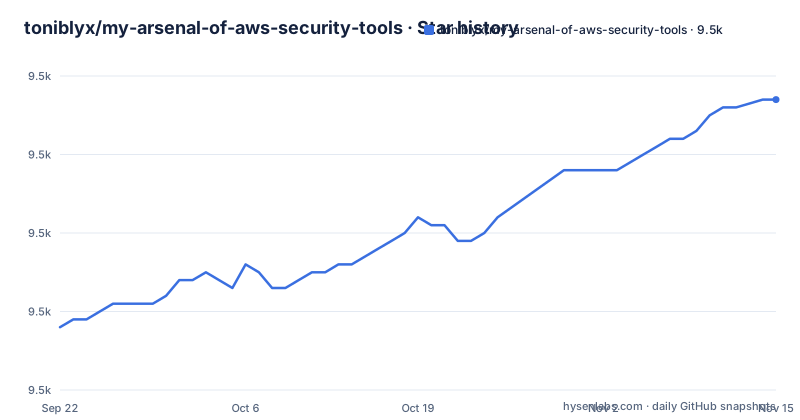
- toniblyx/my-arsenal-of-aws-security-tools9,537 ★ · +29
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| toniblyx/my-arsenal-of-aws-security-tools | 9.5k | 9.5k |
29 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The popularity column is a badge URL, so the list stores links rather than measurements
Every entry sits in a four column table: Name, Description, Popularity, Metadata. The last two columns are not data, they are image requests. The popularity cell for one row points at a stars badge and the metadata cell stacks contributors, watchers, last-commit, open-issues and closed-issues, each one a separate badgen URL:
https://badgen.net/github/stars/toniblyx/prowler
https://badgen.net/github/last-commit/toniblyx/prowler
So the repository commits no counts at all. Star totals, contributor counts and commit dates are fetched by the rendering service every time you open the page, which means the list can go stale in two directions at once. A tool that stopped shipping still shows a healthy badge, and an entry that was correct when it was added can drift years out of date with nothing in the file marking it. Read those cells as a starting signal and click through, never as a maintenance record.
Entries are grouped by attack phase, not by cloud product or job to be done
The table of contents runs Defensive: Hardening, Security Assessment and Inventory, then Offensive, Purple Teaming & Adversary Emulation, Continuous Security Auditing, Digital Forensics and Incident Response, Development Security, S3 Buckets Auditing, Training, and a closing bucket called Other interesting tools/code. That is a taxonomy of phases of an engagement rather than of products or AWS services, which makes the list easy to scan if you are working through a checklist and awkward if you are trying to answer a narrow question such as which tool covers a specific service. The same tool could reasonably sit in more than one heading.
The contribution bar is one sentence: open source and a pull request
The Contribute section asks for a pull request and says to make sure the tool is open source, linking to a general definition. That is the entire stated criteria. Nothing else is spelled out: there is no requirement that a tool still be maintained, no rule about whether an entry must be free to run, nothing about which AWS services it covers, and no stated process for removing an entry later. The repository does keep a former-list.md file at the top level, which implies removals do happen, but the README does not say what the criteria for removal are or whether the reason is recorded anywhere. If you are maintaining one of these tools and want the entry added, the fastest path is the obvious one: open a pull request.
The first row of the defensive table is a tool owned by the list's own author
Prowler heads the defensive section and carries a long description, naming CIS, NIST 800, NIST CSF, CISA, FedRAMP, PCI-DSS, GDPR, HIPAA, FFIEC, SOC2, GXP, Well-Architected Security and ENS, with a Python note at the end of the description. Its repository is toniblyx/prowler, the same account that owns this list, which also links to itself as the first row of its own table. That is not a criticism so much as a fact a reader should hold onto: the ordering at the top of the table is not an independent ranking, and the first entry is a statement by its author about their own project. The rows after it read differently. CloudMapper and CloudTracker are Python tools that analyze AWS environments and compare CloudTrail logs against current IAM policies, and ScoutSuite covers AWS, Google Cloud and Azure from Python.
Language hints live inside the description text, so you cannot filter or sort by them
There is no language column. Where the author bothered, the language appears in parentheses at the end of the description, and it is not consistent even in casing. Prowler is marked (Python), CloudMapper (Python), ScoutSuite (python), CloudSploit Scans is described as AWS security scanning checks with (NodeJS), while CloudCustodian, whose description is a rules engine with a yaml DSL for policies that query, filter and act on resources, carries no language marker at all. The practical result is that if your constraint is the language already in your toolchain, you have to read every description rather than sort a column, and you cannot tell from the table whether a missing marker means the language is mixed or simply unstated. The AWS Security Benchmarks entry, scripts and templates for the AWS CIS Foundation framework, is marked (Python).
The repository ships two directories and a shell codebase the table of contents never mentions
The top level is not just a README. Alongside LICENSE and README.md there are two directories, ami/ and kreator/, plus former-list.md, and the repository's primary language is recorded as Shell rather than Markdown. That combination suggests executable code exists in the tree, and the table of contents does not name those directories. For a list whose entire value is that you can trust the surface it shows you, that gap is worth closing before you rely on it: browse the tree, read whatever is in those directories, and decide for yourself whether it belongs in a catalogue of third party tools.
No releases, no homepage, and no command anywhere, so each tool is a separate adoption project
The repository has no GitHub releases and no project homepage, and the README is organized as tables of links rather than install or usage instructions. Everything else is a name linked to somebody else's repository, for example Prowler's, and that link is where the work actually starts:
https://github.com/toniblyx/prowlerSo evaluating any entry means adopting an unfamiliar project with its own install path, its own credential handling and its own release cadence, and the list gives you no version to ask for and no signal about what an upgrade might change. Plan for that: pick one tool per phase, read that project's own documentation, and assume you are responsible for pinning it yourself.
Freshness is per upstream project, and the file itself last changed on 2026-07-07
The last push to this repository landed on 2026-10-02, and there are no tagged releases to look back on, so the list has no version of its own to compare against. Its entries point at projects that move on their own schedules, and the only freshness signal offered is a last-commit badge embedded per row, which you have to notice and click. A separate former-list.md also sits at the top level. For a reference document, that means age is invisible from the text and you have to reconstruct it from badges, so keep your own note of when you checked a given entry rather than assuming the file position implies recency.
Editorial conclusion
The list suits a defender who already knows the cloud and wants a fast survey of which open source tools exist in each phase, then goes to each project for the real work. It does not suit anyone who needs a vetted, versioned recommendation or a decision, because nothing in it ranks, tests, or dates the entries. Treat it as a starting index: open each tool's own repository, check that it still builds and still matches the AWS services you use, and confirm the cost and permissions it needs before running it against an account that matters.
Frequently asked questions
What are the top cloud security tools listed in my-arsenal-of-aws-security-tools?
The defensive table has no ranking column, so the order is presentation rather than a top ten. Its rows begin with Prowler, CloudMapper, ScoutSuite, CloudCustodian, ICE, CloudSploit Scans, AWS Network Access Analyzer, CloudTracker and AWS Security Benchmarks, and the README splits the rest into offensive, purple teaming, continuous auditing, DFIR, development security, S3 auditing, training and other tools sections.
How does my-arsenal-of-aws-security-tools sort security categories?
By phase of work rather than by a numbered taxonomy. The headings are Defensive: Hardening, Security Assessment and Inventory, Offensive, Purple Teaming & Adversary Emulation, Continuous Security Auditing, Digital Forensics and Incident Response, Development Security, S3 Buckets Auditing, Training, and Other interesting tools/code.
Does my-arsenal-of-aws-security-tools list AWS vulnerabilities?
It lists tools rather than findings, and the README does not enumerate vulnerabilities. Two entries target specific problems: CloudTracker finds over-privileged IAM users and roles by comparing CloudTrail logs with current IAM policies, and AWS Network Access Analyzer automation identifies Internet Gateway reachability across your AWS accounts.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/toniblyx-my-arsenal-of-aws-security-tools)Star history chart for your README
[](https://hysenlabs.com/projects/toniblyx-my-arsenal-of-aws-security-tools)Was this useful?