Tracecat's AGPL has a documented exception, and its sandbox is built from a pinned commit
Open-source security automation platform for teams and AI agents
At a glance
- What is it?
- Tracecat is a security automation platform for teams and agents, published under the AGPL with an enterprise carve-out the README spells out. The engineering detail worth reading is the sandbox: the image compiles the jail from a pinned upstream commit, applies a patch from its own tree, and builds a small helper with every hardening flag the compiler offers.
- Who is it for?
- Tracecat is worth evaluating if your team wants agent-assisted case work and workflow automation on infrastructure you control, and the sandbox story is the strongest part of the engineering. Three things to check first.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
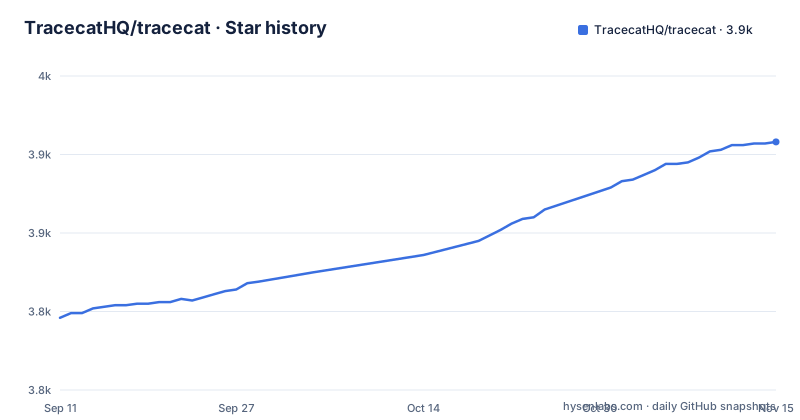
- TracecatHQ/tracecat3,908 ★ · +112
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| TracecatHQ/tracecat | 3.8k | 3.9k |
112 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The AGPL has a documented exception
The licensing section is unusually precise and the precision matters. The repository is under the AGPL version 3, except for two things: code under the enterprise package directory, and code that gates enterprise features. Both exceptions are said to fall under a paid licence, and the sentence that follows is the part to read twice, since it says code in those areas must not be redistributed, sold, used in production, or otherwise commercialised without permission. So the AGPL grant does not cover the whole repository, which is not the usual shape for an open source project and is worth knowing before you vendor it. The package metadata declares the licence plainly, with no exception recorded, so the two places a tool would read disagree in scope even though they agree on the base licence.
The sandbox is compiled from a pinned commit and a local patch
The first stage of the container image builds the sandbox jail from source rather than installing a package, and it does so reproducibly. The upstream source is cloned and checked out at one exact commit hash, pinned to a release line with a policy backend compiled in. A patch file is copied in from the image's own directory, checked with a dry run before it is applied, and the submodules are updated before the build. Then the binary is installed and the clone is deleted. Next to that, a small C++ helper is compiled with the hardening flags a careful project turns on: source fortification, the stack protector, position-independent code and position-independent executables, relro and immediate binding, and warnings promoted to errors with format checking. It is then stripped and its source removed. Two version arguments are pinned in the same file, one for a database library and one for a Node runtime, alongside three separate base images.
The compose file defaults to the previous minor version
The deployment compose file pulls a published image whose tag comes from an environment variable, and the default value of that variable is the previous minor version. The three most recent releases are all prereleases of the next minor, so a stack brought up from the repository defaults to running the older line while the tags people are reading about are the newer prereleases. Nothing is broken by that, and it is arguably the right default for a stable deployment, but it means the artefacts a new user sees in the release list and the artefacts their stack actually runs are from different lines. The rest of the file is careful in a way worth noting: the proxy trusts proxy addresses defaulting to a single loopback prefix, the application environment is pinned to production, the tracing flag defaults to off with an exporter endpoint and sampler arguments supplied, and the allowed-origins and authentication settings are all required inputs rather than defaults.
Every dependency is pinned to an exact version
The dependency list in the package metadata uses exact pins throughout, not lower bounds, across roughly fifty direct requirements. That is a deliberate choice for a platform that ships containers, and it has the usual consequence: dependency updates arrive as commits rather than as surprises. Three things in the list tell you what the agent layer is made of. There is a first-party agent SDK from one model provider at a pinned patch version, a model context protocol server library, and a multi-provider model library with its proxy feature enabled. OpenTelemetry appears three times, for the API, an OTLP exporter over HTTP, and instrumentation of the web framework, and the instrumentation package is pinned to a pre-release-looking version with a letter suffix while the other two sit on the same release. The interpreter floor is 3.12, and the build backend itself is pinned to one exact version.
Three secrets, three generation commands, and placeholders
The environment example documents three secrets, and for each one it gives the command that produces it. One encrypts and decrypts sensitive keys stored in the database, generated with a one-line Python call against a symmetric cipher library. One authenticates calls to the platform's own services, generated as thirty-two random bytes in hexadecimal. One produces private webhook URLs, generated the same way. All three are shipped as obvious placeholders made of the words your-tracecat and the secret's purpose, so the file is self-documenting and simultaneously unusable until you replace three values. Two other defaults are worth knowing: the token lifetime for executors is fifteen minutes, and the comments in the file mention tunnelling to expose webhooks to the internet, with a command that is cut off in the middle of its argument.
Four compose files, with a proxy in front
The repository ships four compose files rather than one, split by purpose: the default deployment, a development variant, a local variant and a sandbox variant. The default file puts a proxy service in front of everything, configured from a proxy configuration file mounted from the root, with the public port, the base domain and the listen address all supplied as environment variables, and a value for the address the proxy is willing to trust from. The application service sits on two networks, one for the proxy and one for the database, which is the standard way to keep the database off the public network. The same environment file defines the public and internal URLs separately, and the internal one points at the API container by name and port rather than at the public address, so a container-to-container call never leaves the network.
Two alpha releases on one day, one numbered eight point one
The release history is three tags, all on the same line: two prereleases of the next minor version, published on the same evening an hour apart, and a third that carries a fourth number in it, a patch applied to a prerelease. Nothing is wrong with that convention, and a project shipping a rapid alpha line is going to produce tags like it. The useful observation is what it implies about the version a deployment should use: the newest tag is a prerelease, the newest non-prerelease is what the compose file defaults to, and the gap between them is where surprises live. The repository root backs this up with a Python version pin, a secret-scanning configuration, a pre-commit configuration, database migration files with their configuration, two shell scripts for environment handling, a task runner file, and three separate instruction directories for coding agents alongside two instruction files.
Editorial conclusion
Tracecat is worth evaluating if your team wants agent-assisted case work and workflow automation on infrastructure you control, and the sandbox story is the strongest part of the engineering. Three things to check first. The licence is the AGPL with a written exception, and the exception covers a directory and the feature-gating code, so read the carve-out before you plan commercial use. The compose file's default image tag points at the previous minor line while the releases are prereleases of the next one. And the environment file ships placeholder secrets with the command to generate each one, which is the right shape but means an install that skips that step runs with a value everyone can read.
Frequently asked questions
What is Tracecat?
An open-source security automation platform for teams and AI agents. It provides agents and skills, case management, workflows for deterministic logic, tables for structured data, a model context protocol server and client, and more than a hundred connectors.
How do I self-host Tracecat?
With Docker, AWS Fargate or Kubernetes, and the README says it can also run fully air-gapped. Four compose files ship in the repository for the default, development, local and sandbox setups, with a proxy in front of the application.
What license is Tracecat under?
The AGPL version 3, with an exception the readme spells out: code under the enterprise package directory, and code that gates enterprise features, are excluded from the open source grant and must not be redistributed, sold or used in production without permission.
How does Tracecat run untrusted code?
In a sandbox. The README says untrusted code and agents run inside jail sandboxes or isolated runtime processes, and the container image compiles that jail from an upstream commit pinned by hash, with a patch from the repository applied before the build.
What do the Tracecat alpha releases mean for a deployment?
The three newest tags are all prereleases of the same minor version, two published on the same day, while the compose file's default image tag still points at the previous minor line. So pick a line deliberately rather than following the release list.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tracecathq-tracecat)Star history chart for your README
[](https://hysenlabs.com/projects/tracecathq-tracecat)Was this useful?