trufflehog's validation stage logs in with the credentials it finds, and its output prints them in plaintext
TruffleHog scans repositories, filesystems, and cloud services for exposed credentials, then checks whether the secrets still work.
At a glance
- What is it?
- TruffleHog is an AGPL-3.0 Go scanner that does four things: discovery across git, chats, wikis, logs, object stores and filesystems, classification of over 800 secret types, validation by attempting a login, and deeper analysis for the most common credential types. The last two stages are what separate it from a pattern matcher, and they are also where the consequences for the operator sit.
- Who is it for?
- TruffleHog suits a security team that wants to know which leaked credentials are still live rather than which strings look like keys, and that has somewhere safe to put the output. It is a poor fit for an unattended CI job on repositories you do not control, because validation sends live authentication attempts at third-party services with credentials that are not yours, and because the default output format writes raw secrets into whatever stream you redirect.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
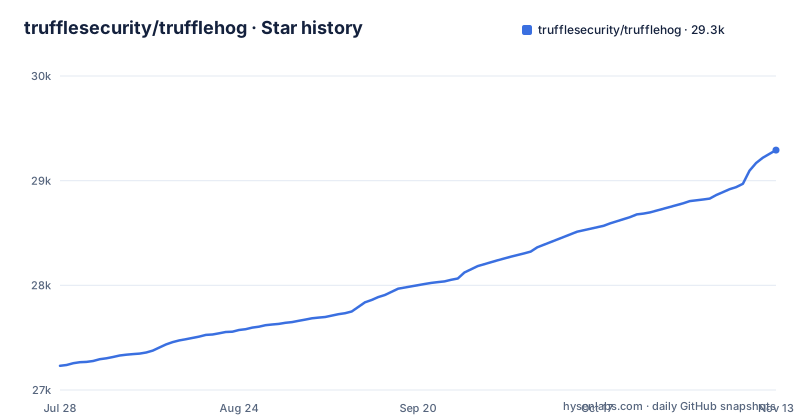
- trufflesecurity/trufflehog29,292 ★ · +2,061
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| trufflesecurity/trufflehog | 27.2k | 29.3k |
2,061 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Validation means the scanner logs in with the credential it just found
The stage that distinguishes this scanner from a pattern matcher is the third one. The README says that for every secret TruffleHog can classify, it can also log in to confirm whether that secret is live or not, and that this step is critical to know whether there is an active present danger. That is a real authentication attempt against the service the credential belongs to, using a credential the scanner did not issue. The consequence for you is concrete. A scan of a repository you do not control produces outbound login attempts at a third party, in a pattern a provider may reasonably treat as credential stuffing, and a scan of a large organisation produces a lot of them. What you learn is also partial by nature: the tool can tell you a key still works, not whether it should have been working. The wider monitoring surfaces, covering Git, Jira, Slack, Confluence, Microsoft Teams and SharePoint continuously, are the enterprise product rather than this binary.
Analysis sends many requests to map what a found key can reach
The fourth stage goes past a yes-or-no check. The README says that for around twenty of the most commonly leaked credential types, instead of sending one request to see whether the secret can log in, TruffleHog can send many requests to learn everything there is to know about it: who created it, what resources it can access, and what permissions it has on those resources. So for those twenty types the tool is not a liveness probe, it is an inventory of one identity's blast radius, gathered by exercising the API as that identity. The consequence is that the cost profile of a scan is not one request per finding. It scales with how much the discovered credential can see, which means the more privileged the leaked key, the longer and louder the enumeration. That is useful for triage and it is also the behaviour most likely to trip provider-side alerting during an unattended run.
Classification covers over 800 secret types and nothing is exempt
The second stage maps what it finds back to a specific identity, and the README is blunt about why: it classifies over 800 secret types, and sometimes it is hard to tell what you are looking at, so TruffleHog classifies everything it finds. The examples given are an AWS secret, a Stripe secret, a Cloudflare secret, a Postgres password, and an SSL private key. Two consequences follow from classifying everything. The first is volume: a repository with generated fixtures, test data, and vendored configuration will produce findings, and the number of types means the number of things you may need to triage. The second is that filtering is your job rather than the tool's. The repository carries example configuration files for exactly this, including one for generic scanning and one named for filters, so narrowing the detector set is a configuration exercise and not a code change. The detector tests also have their own build tag in the Makefile, so detectors are a separable piece of the project.
The documented output prints the raw secret, so redirected output collects live keys
The quick start shows a scan of a public repository of deliberately committed test keys, and the expected output includes a field called Raw result. The fields are Detector Type, Decoder Type, Raw result, Line, Commit, File, Email, Repository, and Timestamp:
Detector Type: AWS
Decoder Type: PLAIN
Raw result: AKIAYVP4CIPPERUVIFXG
Line: 4
Commit: fbc14303ffbf8fb1c2c1914e8dda7d0121633aca
File: keys
Email: counter <[email protected]>
Repository: https://github.com/trufflesecurity/test_keys
Timestamp: 2022-06-16 10:17:40 -0700 PDT
The consequence is that the default output is a list of working credentials, including the committer's email address. Redirect that to a file, pipe it into a ticket, or let a CI job capture it and you have copied live secrets into a system with different access controls than the scanner. The fourth quick start example scans a repository for verified secrets with JSON output instead, which is machine-readable and easier to route somewhere deliberate.
Three of the install routes pipe a remote script straight into your shell
The README offers seven installation routes and three of them are the same curl line with different flags. The plain one is:
curl -sSfL https://raw.githubusercontent.com/trufflesecurity/trufflehog/main/scripts/install.sh | sh -s -- -b /usr/local/binThe -v variant adds signature verification, and the third appends a release tag to pin a version, with v3.56.0 given as the example. Two things are worth noticing. The example tag is far behind the current line, which sits in the v3.99 range, so copying the documented example verbatim gives you a much older build than the newest one. And the -v flag does not make the pipeline safe on its own, because the README states it requires cosign to be installed prior to running the script, so the verification path has a prerequisite that has to be satisfied before the pipe starts. The other routes avoid the shell pipe entirely: Homebrew installs with `brew install trufflehog`, the Docker route is used for the demo and for the platform-specific variants, and there are binary releases and a compile-from-source option.
Artifact verification is a two-step chain and cosign is a prerequisite for it
Release signing is described in more detail than most projects bother with, and the chain has two links. The README states that checksums are applied to all artifacts and that the resulting checksum file is signed using cosign. Verifying means downloading three files from the releases page, the checksums text file, a certificate, and a signature, then checking the signature against the checksum file:
cosign verify-blob <path to trufflehog_{version}_checksums.txt> \
--certificate <path to trufflehog_{version}_checksums.txt.pem> \
--signature <path to trufflehog_{version}_checksums.txt.sig> \
--certificate-identity-regexp 'https://github\.com/trufflesecurity/trufflehog/\.github/workflows/.+' \
--certificate-oidc-issuer "https://token.actions.githubusercontent.com"
The identity regexp and the issuer pin the signature to a workflow in this repository, so the chain of custody is the CI system rather than a person. Only then do you check the artifacts themselves with `sha256sum --ignore-missing -c`, and the ignore-missing flag means files you did not download are skipped rather than treated as failures. The practical cost is that cosign is a separate install, and the whole procedure is a manual sequence for anyone not using the -v script flag.
The module file forks an archived library that it says has vulnerable dependencies
The dependency file carries two replace directives with comments, and one of those comments is the most important line in the repository for anyone assessing supply chain risk. It reads that Coinbase archived this library and it has some vulnerable dependencies so we have forked, pointing a replace at a trufflesecurity-owned fork of the Coinbase wallet-as-a-service client. A second replace redirects another library to a trufflesecurity fork without comment. The consequence is that building from source does not resolve those two dependencies to their upstream names; it resolves them to forks the project maintains itself, one of which replaces an archived upstream library that the project says has vulnerable dependencies. Separately, the build is configured with CGO disabled, which is what makes the static cross-compiled release binaries possible, but the Makefile's race-test target sets CGO to enabled, because the race detector needs it. The default make goal is help rather than build.
Editorial conclusion
TruffleHog suits a security team that wants to know which leaked credentials are still live rather than which strings look like keys, and that has somewhere safe to put the output. It is a poor fit for an unattended CI job on repositories you do not control, because validation sends live authentication attempts at third-party services with credentials that are not yours, and because the default output format writes raw secrets into whatever stream you redirect. Before you commit, decide where scan output lands, use the JSON output rather than the human format in automation, filter by detector when you only care about specific credential types, and remember that building from source resolves two dependencies to trufflesecurity-maintained forks, one replacing an archived library that go.mod says has vulnerable dependencies.
Frequently asked questions
What is TruffleHog used for?
It scans for leaked credentials, where a secret is defined as a credential a machine uses to authenticate itself to another machine, including API keys, database passwords, and private encryption keys. It covers discovery, classification, validation, and analysis across git, chats, wikis, logs, API testing platforms, object stores, and filesystems.
Is TruffleHog free?
The scanner is open source under the AGPL-3.0 license. The README also describes an enterprise product for continuously monitoring Git, Jira, Slack, Confluence, Microsoft Teams, and SharePoint, and states that revenue from it funds more open source projects.
How can I scan a git repository for secrets?
Point it at the repository and filter to findings that actually work, with `trufflehog git https://github.com/trufflesecurity/test_keys --results=verified`. For a whole organisation use the github subcommand, as in `trufflehog github --org=trufflesecurity --results=verified`, and add --exclude-archived to skip archived repositories.
how to install trufflehog on windows
There are Docker invocations written for Windows Command Prompt and for PowerShell, each with its own volume syntax, plus binary releases to download and unpack from the releases page.
what is trufflehog in cyber security
It is a secrets scanner whose distinguishing step is validation: rather than only pattern matching, it attempts to log in with each classified credential to confirm whether it is live. For roughly twenty of the most common credential types it goes further, enumerating who created the key, what it can reach, and what permissions it holds.
What are some effective open-source tools for scanning for secrets?
It describes TruffleHog as a discovery, classification, validation, and analysis tool that classifies over 800 secret types and maps each one back to the specific identity it belongs to.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 1 in the last 30 days; newest first.
- An AI Attack Framework Got Into WorkOS's Sales Tool. It Held Customers' Slack Excerptsdev.to · Nov 3, 2026 · 3 points · 0 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/trufflesecurity-trufflehog)Star history chart for your README
[](https://hysenlabs.com/projects/trufflesecurity-trufflehog)Was this useful?