Magic Unicorn is one script that emits six delivery mechanisms
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell attacks and the powershell bypass technique presented by David Kennedy (TrustedSec) and Josh Kelly at Defcon 18.
At a glance
- What is it?
- Magic Unicorn is a single Python file that takes a payload and writes the PowerShell needed to run it in memory, then hands you one of six ways to get that PowerShell onto a victim: a pasted command, a spreadsheet macro that fakes a corrupt file, an HTML application the user has to approve, a certificate file decoded with a system tool, a custom script re-encoded as a macro, or a word processor formula. The credit lines and the file tree are as interesting as the payloads.
- Who is it for?
- Magic Unicorn suits a red team operator rehearsing a document or browser delivery path against a Windows estate, and an analyst who wants to see exactly what each vector emits. It does not suit anyone looking for a maintained tool with a release history, because the repository has no published releases and its licence is not machine readable.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 18 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
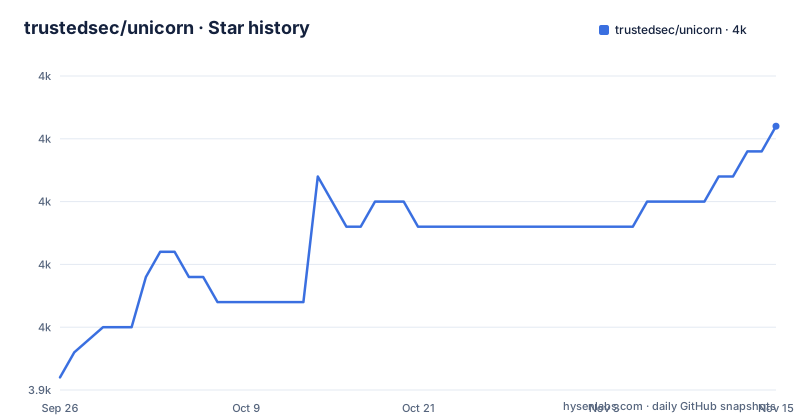
- trustedsec/unicorn3,958 ★ · +10
| Repository | 2026-09-26 | 2026-11-15 |
|---|---|---|
| trustedsec/unicorn | 3.9k | 4k |
10 Stars in the last 50 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One script, six instruction sets, and a Metasploit caveat
The repository is one Python file called unicorn.py, and the rest of the tree is small enough to enumerate: a docs directory, a templates directory holding the text that gets filled in, a tests directory, and three plain text files for the change log, the credits and the licence. The script is run with no arguments to print a banner, and with arguments to pick a payload source, which the readme names as your own shellcode, Cobalt Strike or Metasploit. The one prerequisite in the opening paragraph is that Metasploit must be installed and on the right path if you use the Metasploit payloads, which is a hint about the intended audience: this is an operator tool that assumes a listener workflow rather than a library you import. Everything the tool produces is a file on disk, and the instructions are about what to do with that file next.
The PowerShell payload lands in two files and needs a listener
The base attack writes two files. The first is a text file holding the PowerShell that performs the downgrade injection into memory, and the second is a resource file that the payload tooling uses as a listener configuration. The readme is explicit that you need somewhere that supports remote command injection of some kind, and it names the usual suspects: a spreadsheet or a word document, or the remote execution facility inside a payload framework, or a database injection point. The point of the mechanism is that nothing is written to disk on the victim as an executable, which is why it survives the kind of filtering that blocks files. Two operational notes are easy to miss. The download and execute payload method is a named argument, so the generated PowerShell fetches and runs a remote binary rather than only giving you a session. And a listener must already be enabled to capture the result, or the attack simply succeeds quietly.
The macro vector fakes a corrupt document on purpose
This is the section with the most operational detail and the most instruction about a user experience you are deliberately manufacturing. You enable the developer tab through the ribbon settings, create a macro with a specific name, paste the generated code, and the code runs when the document opens. What the victim sees is a message saying the file is corrupt, and the document closing itself, and the readme shouts in capitals that this is normal behaviour and that the trick is to make the victim believe the document is broken. There is one version specific fix: on newer Word releases the first line of the generated output has to change from the legacy macro name to the modern one, and the macro itself has to be renamed to match. There is also a copy and paste warning, because extra spaces introduced when the code is pasted will cause a syntax error at a specific variable in the generated payload.
The browser route needs the user to approve something
The HTML application vector writes three files into a dedicated output folder: a page that tells the browser to use a launcher, the launcher itself containing the injection code, and the same resource file for the listener. The listener is started with the payload console reading that resource file. What makes this vector different from the others is the interaction requirement, and the readme states it plainly: a user must click allow and accept for the injection to work. So the social engineering is a browser permission prompt rather than a broken document, and the operator has to accept that some fraction of targets will dismiss it. That is the same class of dependency as enabling macros, and it is the reason to test both vectors rather than assume one covers the other.
The certificate vector moves a binary through a file extension
This one is attributed by name in the readme to the researcher who identified it, and the mechanism is a different kind of trick from the others: a binary is converted to a text encoding, that text is placed in a file that looks like a certificate, and a system tool shipped with Windows is used on the victim to convert it back. The readme claims it should work on virtually any system, which is the argument for carrying it when a macro or a browser prompt will not do. The mechanics from the operator's side are two steps. You place an executable in the script's own directory and pass its name with a short argument to get the encoded output:
python unicorn.py <exe_name> crtThen you go to a decode output folder where a batch file performs the reverse conversion on the target machine. No listener is involved at this stage, because the payload has not run yet.
The custom script encoder has a 380 character ceiling you can raise
The custom script vector takes a PowerShell file you already have and converts it into an encoded command or into a macro, and its one real constraint is documented as a number. If you choose the macro form, a large script can exceed the number of carriage returns a spreadsheet macro language allows, because the payload has to be split across many string literals. The fix is an integer argument that sets how many characters go into each string, and the default is 380. The examples show the plain form, the macro form, and the macro form with the number raised to 500, which the readme explains produces fewer line breaks in the generated macro. So a payload that is too large is not a dead end, it is a different invocation, and anyone embedding a large script will hit that argument within a week.
The formula vector is macro free, size limited, and documented elsewhere
The last vector generates a data exchange formula for a word processor or spreadsheet and needs no macro at all, which is why it is the interesting one for a hardened environment. The readme credits the technique to a security research blog post with a link, and gives the two application programming objects it relies on, whose names are misspelled in the file, which is a small reminder that this text is written quickly. Applying it takes eight steps through the user interface: open the document, insert a field, choose a formula, expect an error message about an unexpected end of formula, toggle the field codes, paste the generated code and save. The limitation is stated in the same paragraph: the field is size limited, so the download step uses an expression evaluator rather than a direct call, and a separate download script is exported alongside the payload.
The credits file matters more here than the change log
Three plain text files at the root carry most of the project's history. The credits file names the people the techniques came from, and the readme repeats two of those names in prose: the researcher whose PowerShell work the downgrade and certificate vectors are based on, and the two presenters of the bypass technique at a conference. That attribution is not decorative in a tool whose entire purpose is to replay other people's published research, and the document vector carries a third external link to the blog post where the formula technique was written up. The change log is also plain text rather than generated, and the repository publishes no releases at all, so there is no tag to pin and no release notes to diff. The licence file exists but the repository metadata does not resolve it to an identifier, and the last push to the default branch is dated 2026-09-22 on a repository that is not archived.
Editorial conclusion
Magic Unicorn suits a red team operator rehearsing a document or browser delivery path against a Windows estate, and an analyst who wants to see exactly what each vector emits. It does not suit anyone looking for a maintained tool with a release history, because the repository has no published releases and its licence is not machine readable. Before running it, read the delivery requirements for the vector you plan to use, since several of them depend on a listener, a macro setting or a user click that is not optional.
Frequently asked questions
What does Magic Unicorn do?
It is a Python script that generates a PowerShell downgrade injection payload and writes it out as a text file, so code runs in memory rather than landing on disk as an executable. It supports your own shellcode, Cobalt Strike payloads and Metasploit payloads, with Metasploit installed and on the path when you use its methods.
How do I get a shell from a document with Magic Unicorn?
The macro vector needs the developer tab enabled, a macro created with the name the tool expects, and the generated code pasted in. When the document opens the victim sees a corrupt file message and the document closes, which the readme states is deliberate, and the shell arrives through the injection. On newer Word releases both the macro name and the first line of the output must use the newer spelling.
Can Magic Unicorn transfer a binary without macros?
Yes, two ways. The certificate vector converts a binary to a text encoding inside a file that looks like a certificate, and a system tool decodes it on the target, with the decode files written to a folder after the generation step. The formula vector instead builds a data exchange field that a word processor evaluates, and that one is size limited so the download step goes through an expression evaluator.
What does Magic Unicorn require before a test?
A listener must already be enabled to capture the result, since the readme says so explicitly. The browser route additionally needs a user to click allow on the prompt, the macro route needs the developer tab enabled in the office application, and the Metasploit methods need the payload tooling installed and on the right path.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/trustedsec-unicorn)Star history chart for your README
[](https://hysenlabs.com/projects/trustedsec-unicorn)Was this useful?