EDRChoker, a QoS throttle with no single policy undo
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
At a glance
- What is it?
- EDRChoker is a small C# utility that applies policy-based Quality of Service bandwidth caps to named processes, so an endpoint detection agent cannot get its telemetry out. The whole tool is two command lines over two source files, which is exactly where its limits are: you can add policies from a list file or remove all of them, and nothing in between.
- Who is it for?
- EDRChoker is worth knowing about as a demonstration that the telemetry path can be strangled rather than answered, and the linked write-up explains the reasoning in more depth than the README does. It is a lab tool, not a deployment tool.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 155 days ago.
- What is it written in?
- Mainly C#, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
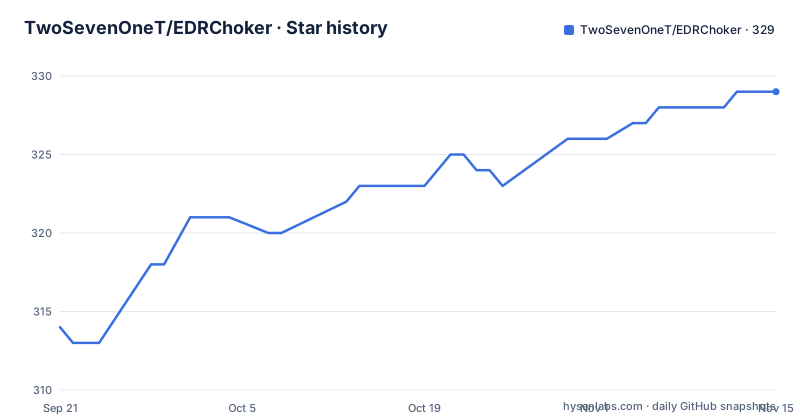
- TwoSevenOneT/EDRChoker329 ★ · +15
| Repository | 2026-09-21 | 2026-11-15 |
|---|---|---|
| TwoSevenOneT/EDRChoker | 314 | 329 |
15 Stars in the last 55 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
One list file in, all policies out
The command surface is two lines and no more. EDRChoker.exe with a path to a list file creates a QoS policy for every process name in it, one name per line. EDRChoker.exe with no arguments removes all installed QoS policies.
There is no third form. You cannot remove the policy for a single process, you cannot ask the tool which policies are currently applied, and there is no dry run. Cleanup is therefore all or nothing, which means the only way to undo one process is to undo everything and start again.
For a utility whose whole effect is on a machine you may not be able to reach physically, that asymmetry matters. If you applied caps to a list of forty agents and need one of them back for testing, there is no supported path to that state other than removing all forty and rebuilding the list.
The input format is plain text, which is the one genuinely convenient part: the list is easy to keep in version control and easy to diff between machines.
The only release is a tag named after the branch
The release history has one entry and the name is unusual.
It is a tag called main, titled Version 1.0, dated 7 June 2026. The default branch is also called main, so the published release is the branch itself rather than a version cut from it. There is no second tag to compare against and no change log beyond the README.
The last push to the repository is 13 June 2026 and it is not archived, so six days of work sit past the tagged point. For a tool this small that is not a large risk, since the code is two files and readable in a sitting.
What it does mean is that there is no version string to quote. If you note which copy you ran, you are noting a commit, not a release, and the README never tells you where to find the commit hash to note.
The repository also has no .github directory in its listing. No issue templates, no pull request template, no automated workflow, and no security policy file, which for a security-adjacent tool is a visible absence rather than a hidden one.
There is no LICENSE file and no stated terms
The source is public and the terms are not.
The root of the repository holds .gitattributes, .gitignore, App.config, EDRChoker.csproj, EDRChoker.sln, Program.cs, Properties/, README.md, and Utils.cs. There is no LICENSE file anywhere in that listing, and no licence is recorded for the project. Nothing in the README says what you may do with it.
That is a genuine gap rather than a formality, because the repository's only external pointer is a write-up hosted elsewhere which describes the tool as a way to bypass defences. A reader who wants to run this on a system they are responsible for has no statement of warranty, no grant, and no notice about misuse, only a README and a blog link.
It also means there is nothing to point an internal review at. Most organisations can clear a tool with a permissive licence attached. An unlicensed tool with a bypass article attached tends to sit in a queue.
pacer.sys does the work and the caps are described as hard
The mechanism is a Windows component rather than anything the tool implements.
EDRChoker relies on the pacer.sys driver, which is what backs policy-based Quality of Service on Windows. The tool registers a QoS policy against each named process with a hard bandwidth cap, and the effect the README describes is that EDR agents always time out, which is equivalent to blocking them for practical purposes.
Calling the caps hard is the load-bearing word. A soft throttle lets a sender exceed its allocation when the link is idle, which a healthy agent on a quiet network would never notice. A hard cap cannot be exceeded at all, so the agent's uploads stall regardless of available bandwidth. That is why the approach works on a machine with plenty of bandwidth, where a naive block would be more obvious.
Two properties follow from using the platform mechanism rather than a firewall rule or a service stop. The rules take effect immediately, with no reboot needed, and they persist after the target reboots Windows.
Two descriptions of what the tool actually does
The repository description and the README describe the same effect in two different ways.
The repository description says the tool uses the QoS Policy, Pacer.sys, to throttle Endpoint Detection and Response agents from connecting to the server. The README says it sets hard bandwidth caps on EDR agents, causing them to always time out, which effectively blocks them.
The first framing is about the connection failing. The second is about the throughput collapsing. The README is the more accurate of the two, because a QoS policy does not prevent a connection from being established; it limits what can be sent over it, and the agent burns its own retry budget discovering that.
That distinction has a practical consequence. An administrator watching connections rather than throughput can watch an agent keep dialling successfully and conclude nothing is wrong. The symptom is a healthy-looking socket list and a steadily growing queue of undelivered telemetry.
The README does not state the cap value, whether it is configurable, or what the timeout manifests as on the agent side. It also does not say which of the agent's flows the policy covers, outbound telemetry alone or management traffic too.
Seven products listed and an open invitation to test the rest
The README keeps a list of what has been tried, and it is the most useful paragraph in the file.
Named as successfully tested are Elastic Defend, Microsoft Defender for Endpoint, Tanium Threat Response Agent, Trend Micro Deep Security Agent, Hurukai from HarfangLab, and Cortex XDR. The list ends with an ellipsis and a request to be contacted if you have tested it against anything else.
That covers the major commercial and enterprise products and leaves out several that would be worth knowing about, particularly anything with its own embedded bandwidth expectations or aggressive retry behaviour. A tool that works by starving a channel will interact differently with an agent that treats starvation as a network fault and retries forever than with one that backs off, and the README gives you no way to tell which category an unlisted product falls into.
There is also no version attached to any of the products. An EDR agent version is usually the deciding factor in whether a throttling approach still works, since agent software changes its retry and batching behaviour regularly.
The demo video is a single YouTube link, which is more evidence than a claim but less than a test matrix.
A solution file and App.config date the tool
The project shape tells you what era of .NET this was written for.
There is a Visual Studio solution, EDRChoker.sln, and a project file, EDRChoker.csproj, alongside an App.config file. App.config is the configuration mechanism for .NET Framework applications, and the modern SDK-style equivalent stores settings elsewhere, so this is a project targeting the Framework rather than current .NET.
The source is two files. Program.cs holds the entry point and the command parsing, and Utils.cs holds the QoS work. Properties/ holds the assembly metadata. That is the entire application, and it means you can read the whole mechanism in one sitting, which is a genuine advantage over a compiled tool distributed without source.
The default branch is master rather than main, another marker of the same vintage, while the single release tag is called main. The two names disagree, which tells you the branch was renamed at some point and the tag was not renamed with it.
For anyone running this on a current Windows build, the practical question is whether the Framework runtime it targets is still present on the machine, and the README does not answer that.
Editorial conclusion
EDRChoker is worth knowing about as a demonstration that the telemetry path can be strangled rather than answered, and the linked write-up explains the reasoning in more depth than the README does. It is a lab tool, not a deployment tool. Before you run it, check three things. Whether you have the process names exactly as Windows reports them, since a mismatch means no policy and no visible effect. That you understand the policies survive a reboot and are removed only by running the tool with no arguments. And that you have your own plan for undoing it, because there is no command to remove one process and no inventory of what is currently installed.
Frequently asked questions
How do I install and remove EDRChoker's QoS policies?
Run EDRChoker.exe with the path to a list file to create a QoS policy for every process name in it, one name per line. Run EDRChoker.exe with no arguments to remove all installed QoS policies. There is no command to remove a single process.
What does EDRChoker need from Windows?
It relies on the pacer.sys driver, the Windows component behind policy-based Quality of Service, which is how the hard bandwidth caps are applied. The README states the rules take effect immediately and persist after the target reboots Windows.
Which EDR products has EDRChoker been tested against?
Elastic Defend, Microsoft Defender for Endpoint, the Tanium Threat Response Agent, the Trend Micro Deep Security Agent, Hurukai from HarfangLab, and Cortex XDR. The author asks to be contacted about successful tests against any other product.
Is EDRChoker open source and what licence does it use?
The source is public, with EDRChoker.sln, EDRChoker.csproj, Program.cs, Utils.cs, App.config, and Properties/ at the root, but there is no LICENSE file in the repository and no licence is stated for the project.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/twosevenonet-edrchoker)Star history chart for your README
[](https://hysenlabs.com/projects/twosevenonet-edrchoker)Was this useful?